
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Refer to the exhibit.
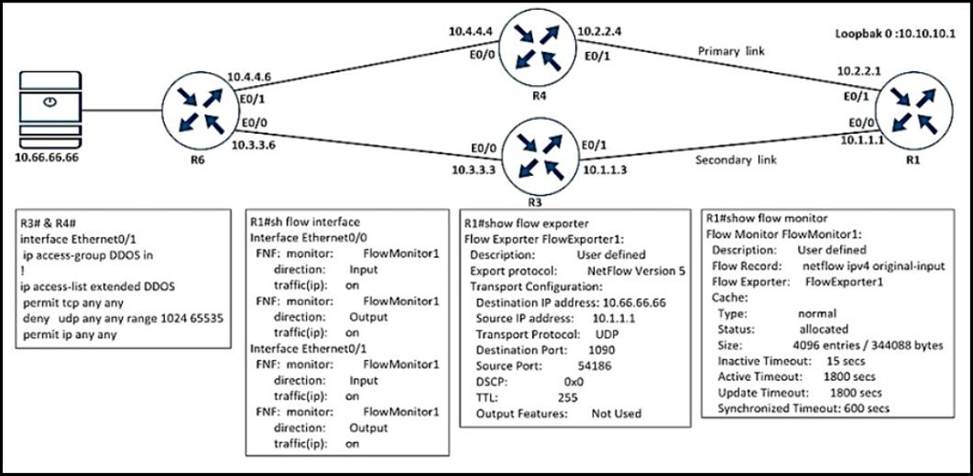
An engineer configured NetFlow but cannot receive the flows from R1.
Which two configurations resolve the issue? (Choose two)
A)

B)

C)

D)

E)

- A . Option A
- B . Option B
- C . Option C
- D . Option D
- E . Option E
Refer to the exhibit.
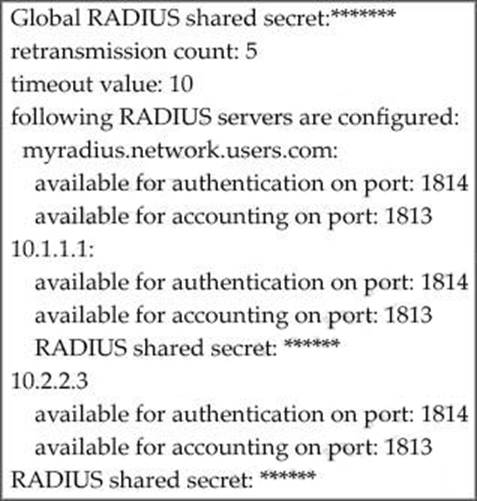
AAA server 10.1.1.1 is configured with the default authentication and accounting settings, but the switch cannot communicate with the server.
Which action resolves this issue?
- A . Match the authentication port
- B . Match the accounting port
- C . Correct the timeout value.
- D . Correct the shared secret.
A
Explanation:
Command Default
Accounting port: 1813
Authentication port: 1812
Accounting: enabled
Authentication: enabled
Retransmission count: 1
Idle-time: 0
Server monitoring: disabled
Timeout: 5 seconds
Test username: test
Test password: test
Reference: https://www.cisco.com/c/m/en_us/techdoc/dc/reference/cli/n5k/commands/radius-server-host.html
By default, RADIUS uses UDP port 1812 for authentication and port 1813 for accounting. In the exhibit above we see port 1814 is being used for authentication to AAA server at 10.1.1.1 which is not the default port so we must adjust the authentication port to the default value 1812.
Users were moved from the local DHCP server to the remote corporate DHCP server. After the move, none of the users were able to use the network.
Which two issues will prevent this setup from working properly? (Choose two)
- A . Auto-QoS is blocking DHCP traffic.
- B . The DHCP server IP address configuration is missing locally
- C . 802.1X is blocking DHCP traffic
- D . The broadcast domain is too large for proper DHCP propagation
- E . The route to the new DHCP server is missing
Refer to the exhibit.
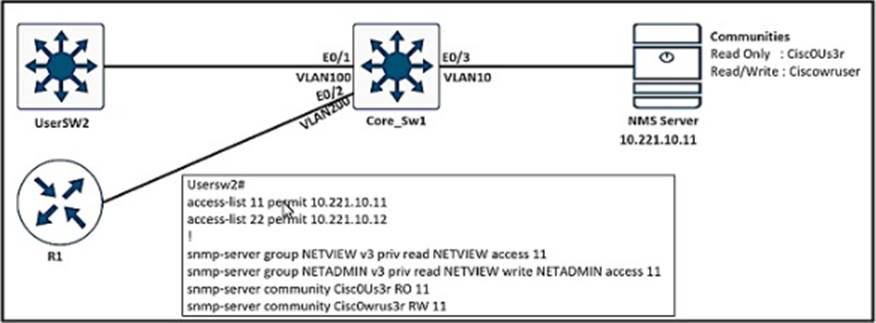
An engineer configured SNMP Commîmes on UserSW2 switch, but the SNMP server cannot upload modified configurations to the switch.
Which configuration resolves this issue?
- A . snmp-server community Ciscowruser RW 11
- B . snmp-server group NETADMIN v3 priv read NETVIEW write NETADMIN access 22
- C . snmp-server community CiscOUs3r RW 11
- D . snmp-server group NETVIEW v2c priv read NETVIEW access 11
Refer to the exhibit.
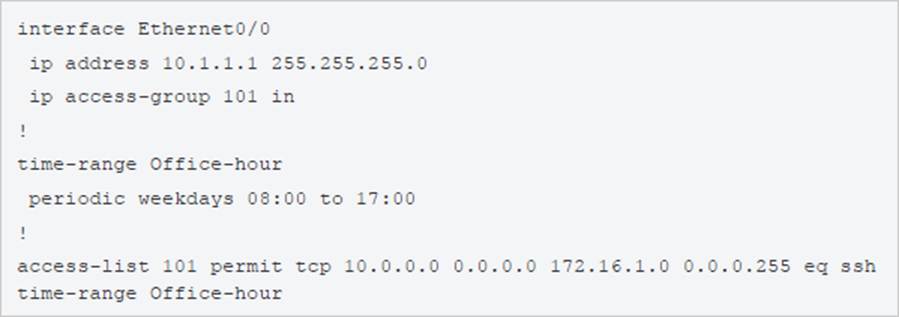
An IT staff member comes into the office during normal office hours and cannot access devices through SSH.
Which action should be taken to resolve this issue?
- A . Modify the access list to use the correct IP address.
- B . Configure the correct time range.
- C . Modify the access list to correct the subnet mask
- D . Configure the access list in the outbound direction.
A
Explanation:
To ACL should be permit tcp 101 10.1.1.1 0.0.0.0
Refer to the exhibit.
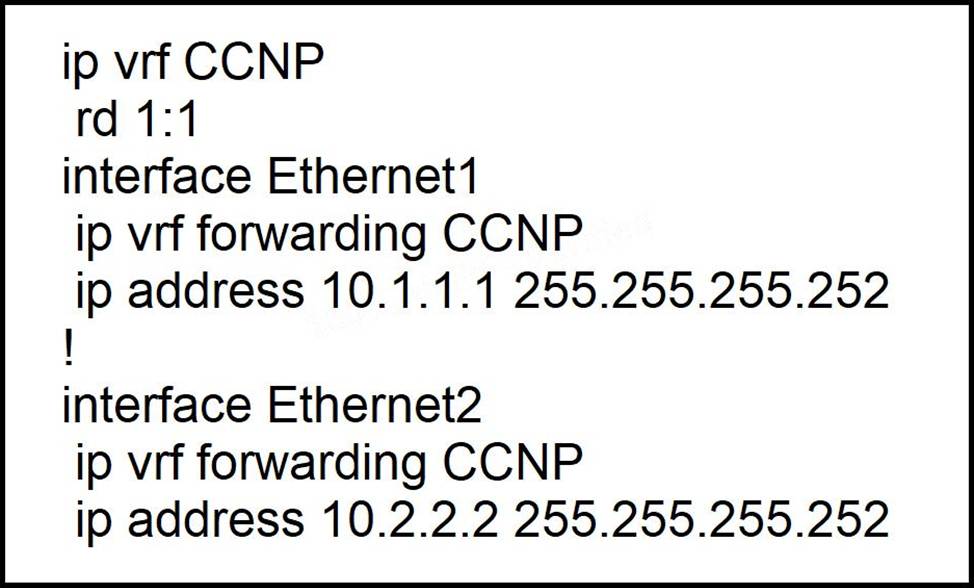
Which configuration enables OSPF for area 0 interfaces to adjacency with a neighboring router with the same VRF?
- A . router ospf 1 vrf CCNP
interface Ethernet1
ip ospf 1 area 0.0.0.0
interface Ethernet2
ip ospf 1 area 0.0.0.0 - B . router ospf 1
interface Ethernet1
ip ospf 1 area 0.0.0.0
interface Ethernet2
ip ospf 1 area 0.0.0.0 - C . router ospf 1 vrf CCNP
network 10.1.1.1 0.0.0.0 area 0
network 10.2.2.2 0.0.0.0 area 0 - D . router ospf 1 vrf CCNP
network 10.0.0.0 0.0.255.255 area 0
What are the two goals of micro BFD sessions? (Choose two.)
- A . The high bandwidth member link of a link aggregation group must run BFD
- B . Run the BFD session with 3×3 ms hello timer
- C . Continuity for each member link of a link aggregation group must be verified
- D . Eny member link on a link aggregation group must run BFD
- E . Each member link of a link aggregation group must run BFD.
C,E
Explanation:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/iproute_bfd/configuration/xe-16-8/irb-xe-16-8-book/irb-micro-bfd.html
Which two protocols work in the control plane of P routers across the MPLS cloud? (choose two)
- A . LSP
- B . RSVP
- C . ECMP
- D . LDP
- E . MPLS OAM
Refer to the exhibit.
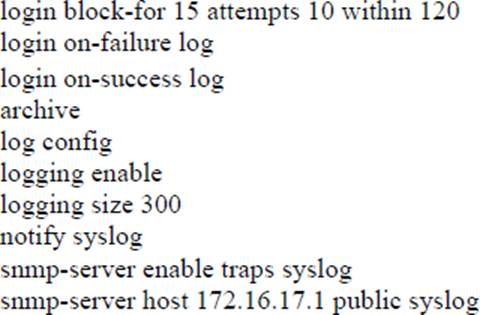
The administrator can see the traps for the failed login attempts, but cannot see the traps of successful login attempts.
What command is needed to resolve the issue?
- A . Configure logging history 2
- B . Configure logging history 3
- C . Configure logging history 4
- D . Configure logging history 5
D
Explanation:
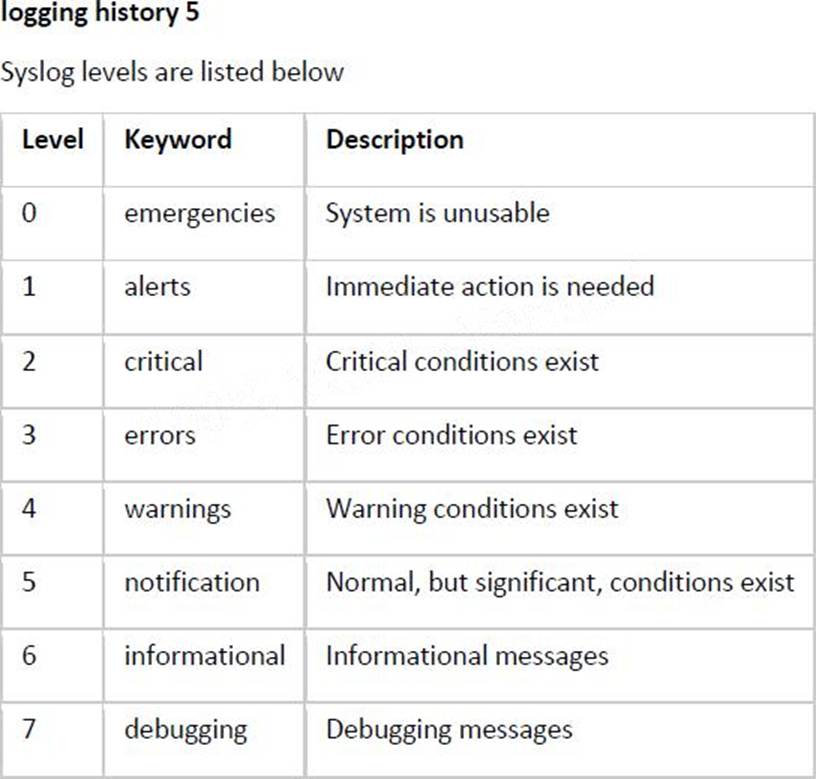
By default, the maximum severity sent as a syslog trap is warning. That is why you see syslog traps for login failures. Since a login success is severity 5 (notifications), those syslog messages will not be converted to traps.
To fix this, configure:
Note:
The syntax of login block is:
login block-for seconds attempts tries within seconds
Refer to the exhibit.
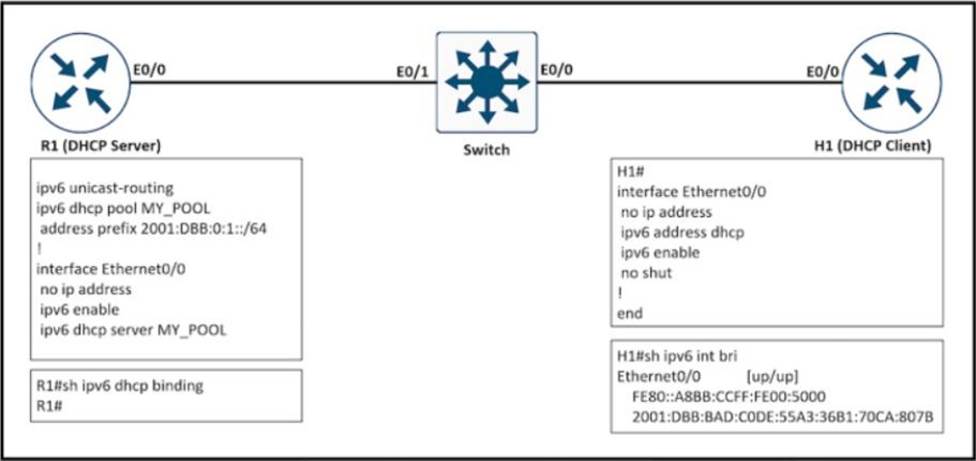
The client server but the show command does not show the IPv6 DHCP bindings on the server.
Which action resolves the issue?
- A . Extend the DHCP lease time because R1 removed the IPv6 address earlier after the lease expired.
- B . Configure H1 as the DHCP client that manually assigns the IPv6 address on interlace e0/0..
- C . Use the 2001:DBB:BAD:C0DE::/64 prefix for the DHCP pool on R1.
- D . Configure authorized DHCP servers to avoid IPv6 addresses from a rogue DHCP server.