
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
What are two functions of IPv6 Source Guard? (Choose two.)
- A . It uses the populated binding table for allowing legitimate traffic.
- B . It works independent from IPv6 neighbor discovery.
- C . It denies traffic from unknown sources or unallocated addresses.
- D . It denies traffic by inspecting neighbor discovery packets for specific pattern.
- E . It blocks certain traffic by inspecting DHCP packets for specific sources.
A,C
Explanation:


Refer to the exhibit.
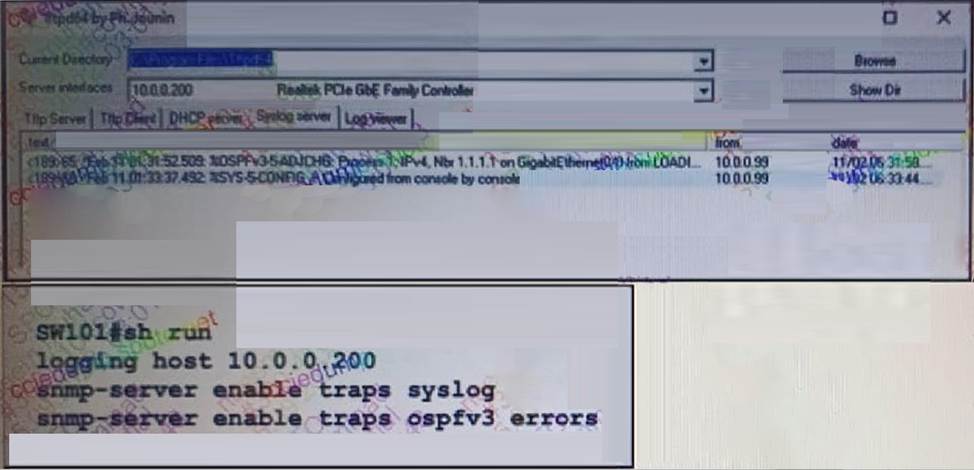
An engineer configures SW101 to send OSPFv3 interfaces state change messages to the server. However, only some OSPFv3 errors are being recorded.
Which organization resolves the ..?
- A . snmp-server enable traps ospfv3 state-change if-state-change
- B . snmp-server-enable traps ospfv3 state-change restart-status-change
- C . snmp-server-enable traps ospfv3 state-change neighbor-state-change.
- D . snmp-server-enable traps ospfv3 state-change if-state-change neighbor-state-change
Refer to the exhibit.
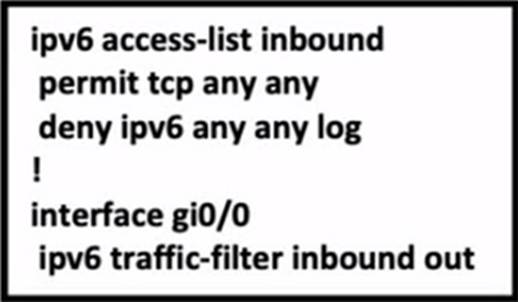
A network administrator configured an IPv6 access list to allow TCP return frame only, but it is not working as expected.
Which changes resolve this issue?
- A . ipv6 access-list inbound
permit tcp any any syn
deny ipv6 any any log
!
interface gi0/0
ipv6 traffic-filter inbound out - B . ipv6 access-list inbound
permit tcp any any syn
deny ipv6 any any log
!
interface gi0/0
ipv6 traffic-filter inbound in - C . ipv6 access-list inbound
permit tcp any any established
deny ipv6 any any log
!
interface gi0/0
ipv6 traffic-filter inbound in - D . ipv6 access-list inbound
permit tcp any any established
deny ipv6 any any log
!
interface gi0/0
ipv6 traffic-filter inbound out
C
Explanation:
https://www.cisco.com/c/en/us/td/docs/switches/lan/catalyst3750/software/release/122_55_se/configuration/guide/scg3750/swv6acl.html
Refer to the exhibit.
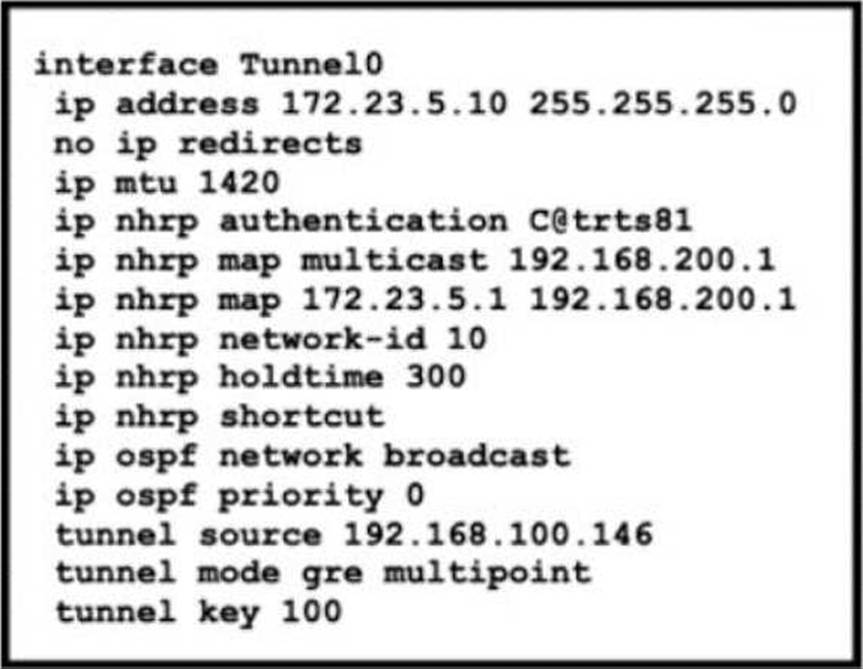
A network engineer is adding a new spoke router into an existing DMVPN Phase 3 tunnel with a hub router to provide secure communication between sites.
Which additional configuration must the engineer apply to enable the tunnel to come up?
- A . ip nhrp registration no-unique
- B . ip nhrp server-only non-caching
- C . ip nhrp responder tunnel
- D . ip nhrpnhs 172.23.5.1
Refer to the exhibit.
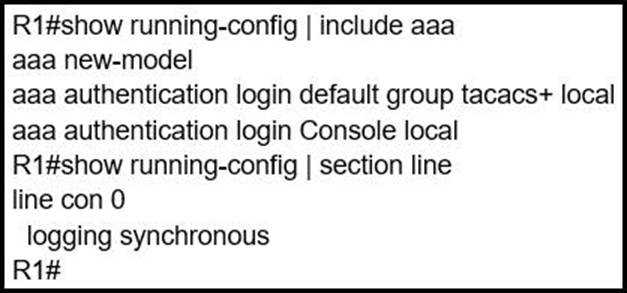
An engineer is trying to configure local authentication on the console line, but the device is trying to authenticate using TACACS+.
Which action produces the desired configuration?
- A . Add the aaa authentication login default none command to the global configuration.
- B . Replace the capital “C” with a lowercase “c” in the aaa authentication login Console local command.
- C . Add the aaa authentication login default group tacacs+ local-case command to the globalconfiguration.
- D . Add the login authentication Console command to the line configuration
D
Explanation:
Reference: https://community.cisco.com/t5/switching/how-to-define-login-local-for-console-0/td-p/2949493
Which table is used to map the packets in an MPLS LSP that exit from the same interface, via the same next hop, and have the same queuing policies?
- A . RIB
- B . FEC
- C . LDP
- D . CEF
Refer to the exhibit.
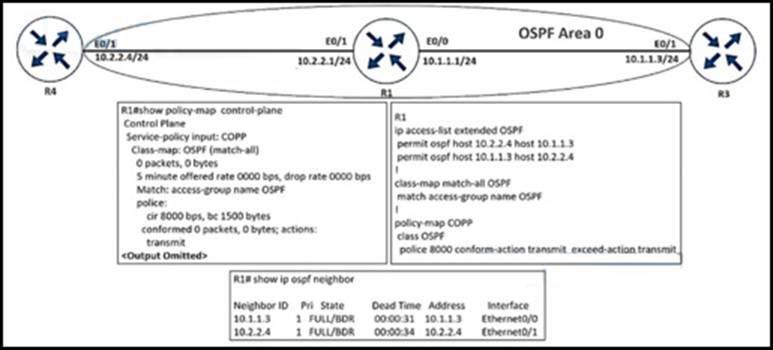
An engineer implemented CoPP but did not see OSPF traffic going through it.
Which configuration resolves the issue?
- A . ip access-list extended OSPF permit ospf any any
- B . policy-map COPP class OSFP police 8000 conform-action transmit exceed-action transmit violate-action drop
- C . control-plane service-policy input COPP
- D . class-map match-all OSFP match access-group name OSPF
Refer to the exhibit.
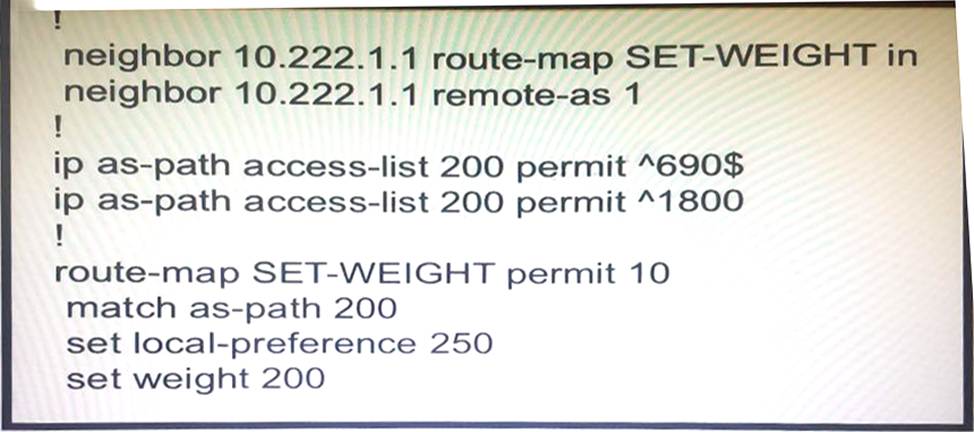
A router receiving BGP routing updates from multiple neighbors for routers in AS 690.
What is the reason that the router still sends traffic that is destined to AS 690 to a neighbor other than 10.222.1.1?
- A . The local preference value in another neighbor statement is higher than 250.
- B . The local preference value should be set to the same value as the weight in the route map.
- C . The route map is applied in the wrong direction.
- D . The weight value in another neighbor statement is higher than 200.
Refer to the exhibit.
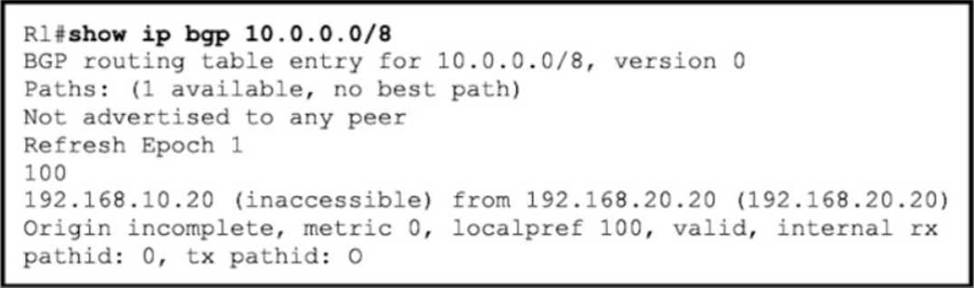
An engineer is troubleshooting a prefix advertisement issue from R3, which is not directly connected to R1.
Which configuration resolves the issue?
A)

B)
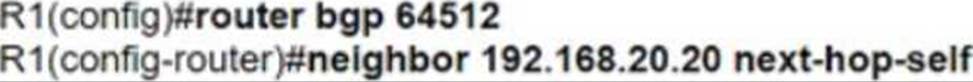
C)
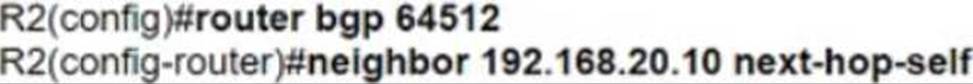
D)

- A . Option A
- B . Option B
- C . Option C
- D . Option D
Refer to Exhibit:
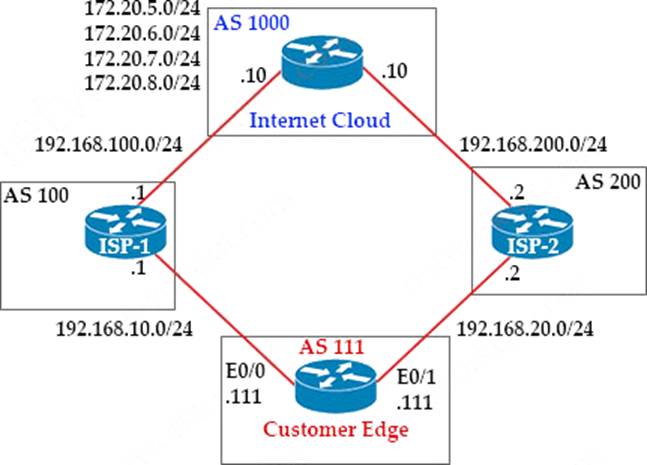
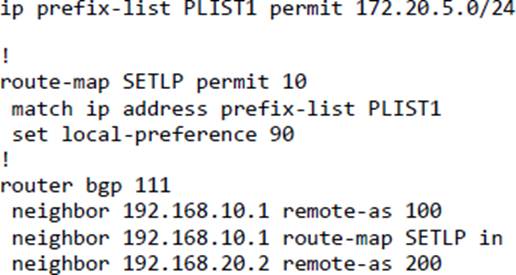
AS 111 wanted to use AS 200 as the preferred path for 172.20.5.0/24 and AS 100 as the backup. After the configuration, AS 100 is not used for any other routes.
Which configuration resolves the issue?
- A . route-mmap SETLP permit 10
match ip address prefix-list PLIST1
set local-preference 99
route-map SETLP permit 20 - B . route-map SETLP permit 10
match ip address prefix-list PLIST1
set local-preference 110
route-map SETLP permit 20 - C . router bgp 111
no neighbor 192.168.10.1 route-map SETLP in
neighbor 192.168.10.1 route-map SETLP out - D . router bap 111
no neighbor 192.168.10.1 route-map SETLP in
neighbor 192.168.20.2 route-map SE TLP in
A
Explanation:
There is an implicit deny all at the end of any route-map so all other traffic that does not match 172.20.5.0/24 would be dropped. Therefore we have to add a permit sequence at the end of the route-map to allow other traffic.
The default value of Local Preference is 100 and higher value is preferred so we have to set the local preference of AS100 lower than that of AS200.