
Cisco 200-201 Practice Exams
Last updated on Nov 16,2026- Exam Code: 200-201
- Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which metric in CVSS indicates an attack that takes a destination bank account number and replaces it with a different bank account number?
- A . integrity
- B . confidentiality
- C . availability
- D . scope
Refer to the exhibit.
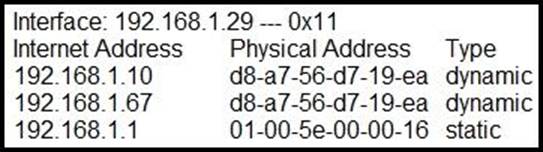
What is occurring in this network?
- A . ARP cache poisoning
- B . DNS cache poisoning
- C . MAC address table overflow
- D . MAC flooding attack
An investigator is examining a copy of an ISO file that is stored in CDFS format.
What type of evidence is this file?
- A . data from a CD copied using Mac-based system
- B . data from a CD copied using Linux system
- C . data from a DVD copied using Windows system
- D . data from a CD copied using Windows
Which security technology guarantees the integrity and authenticity of all messages transferred to and from a web application?
- A . Hypertext Transfer Protocol
- B . SSL Certificate
- C . Tunneling
- D . VPN
A user received a malicious attachment but did not run it.
Which category classifies the intrusion?
- A . weaponization
- B . reconnaissance
- C . installation
- D . delivery
One of the objectives of information security is to protect the CIA of information and systems.
What does CIA mean in this context?
- A . confidentiality, identity, and authorization
- B . confidentiality, integrity, and authorization
- C . confidentiality, identity, and availability
- D . confidentiality, integrity, and availability
Which event is user interaction?
- A . gaining root access
- B . executing remote code
- C . reading and writing file permission
- D . opening a malicious file
How does an attacker observe network traffic exchanged between two users?
- A . port scanning
- B . man-in-the-middle
- C . command injection
- D . denial of service
Which security technology allows only a set of pre-approved applications to run on a system?
- A . application-level blacklisting
- B . host-based IPS
- C . application-level whitelisting
- D . antivirus
Refer to the exhibit.
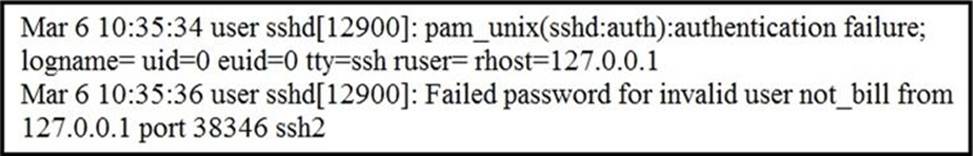
In which Linux log file is this output found?
- A . /var/log/authorization.log
- B . /var/log/dmesg
- C . var/log/var.log
- D . /var/log/auth.log