
Cisco 200-201 Practice Exams
Last updated on Nov 16,2026- Exam Code: 200-201
- Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
What makes HTTPS traffic difficult to monitor?
- A . SSL interception
- B . packet header size
- C . signature detection time
- D . encryption
A SOC analyst is investigating an incident that involves a Linux system that is identifying specific sessions.
Which identifier tracks an active program?
- A . application identification number
- B . active process identification number
- C . runtime identification number
- D . process identification number
Refer to the exhibit.

Which type of log is displayed?
- A . proxy
- B . NetFlow
- C . IDS
- D . sys
What are the two characteristics of the full packet captures? (Choose two.)
- A . Identifying network loops and collision domains.
- B . Troubleshooting the cause of security and performance issues.
- C . Reassembling fragmented traffic from raw data.
- D . Detecting common hardware faults and identify faulty assets.
- E . Providing a historical record of a network transaction.
DRAG DROP
Drag and drop the technology on the left onto the data type the technology provides on the right.
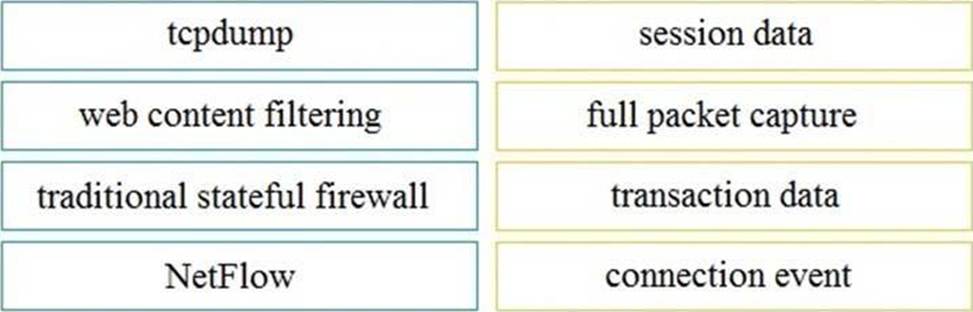
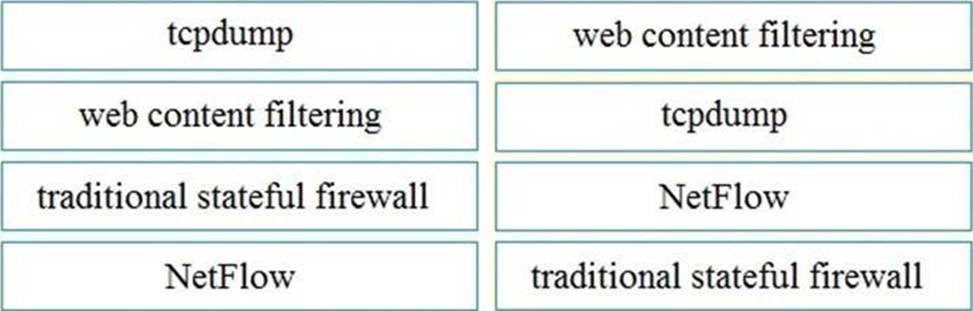
An offline audit log contains the source IP address of a session suspected to have exploited a vulnerability resulting in system compromise.
Which kind of evidence is this IP address?
- A . best evidence
- B . corroborative evidence
- C . indirect evidence
- D . forensic evidence
What is an example of social engineering attacks?
- A . receiving an unexpected email from an unknown person with an attachment from someone in the same company
- B . receiving an email from human resources requesting a visit to their secure website to update contact information
- C . sending a verbal request to an administrator who knows how to change an account password
- D . receiving an invitation to the department’s weekly WebEx meeting
Which open-sourced packet capture tool uses Linux and Mac OS X operating systems?
- A . NetScout
- B . tcpdump
- C . SolarWinds
- D . netsh
Which step in the incident response process researches an attacking host through logs in a SIEM?
- A . detection and analysis
- B . preparation
- C . eradication
- D . containment
Refer to the exhibit.
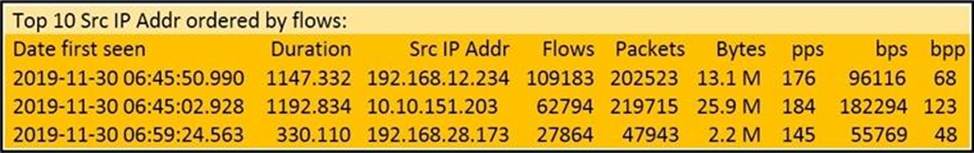
What information is depicted?
- A . IIS data
- B . NetFlow data
- C . network discovery event
- D . IPS event data