Cisco 200-201 Practice Exams
Last updated on Nov 16,2026- Exam Code: 200-201
- Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
A company receptionist received a threatening call referencing stealing assets and did not take any action assuming it was a social engineering attempt. Within 48 hours, multiple assets were breached, affecting the confidentiality of sensitive information.
What is the threat actor in this incident?
- A . company assets that are threatened
- B . customer assets that are threatened
- C . perpetrators of the attack
- D . victims of the attack
What is rule-based detection when compared to statistical detection?
- A . proof of a user’s identity
- B . proof of a user’s action
- C . likelihood of user’s action
- D . falsification of a user’s identity
Refer to the exhibit.
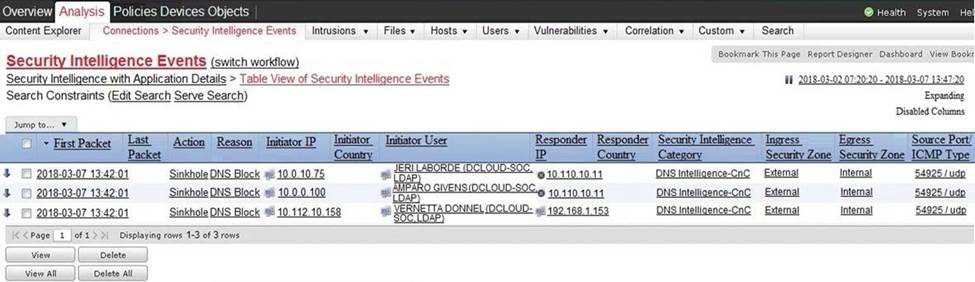
Which two elements in the table are parts of the 5-tuple? (Choose two.)
- A . First Packet
- B . Initiator User
- C . Ingress Security Zone
- D . Source Port
- E . Initiator IP
What is the difference between deep packet inspection and stateful inspection?
- A . Deep packet inspection is more secure than stateful inspection on Layer 4
- B . Stateful inspection verifies contents at Layer 4 and deep packet inspection verifies connection at Layer 7
- C . Stateful inspection is more secure than deep packet inspection on Layer 7
- D . Deep packet inspection allows visibility on Layer 7 and stateful inspection allows visibility on Layer 4
An intruder attempted malicious activity and exchanged emails with a user and received corporate information, including email distribution lists. The intruder asked the user to engage with a link in an email. When the fink launched, it infected machines and the intruder was able to access the corporate network.
Which testing method did the intruder use?
- A . social engineering
- B . eavesdropping
- C . piggybacking
- D . tailgating
How is attacking a vulnerability categorized?
- A . action on objectives
- B . delivery
- C . exploitation
- D . installation
How is NetFlow different from traffic mirroring?
- A . NetFlow collects metadata and traffic mirroring clones data.
- B . Traffic mirroring impacts switch performance and NetFlow does not.
- C . Traffic mirroring costs less to operate than NetFlow.
- D . NetFlow generates more data than traffic mirroring.
An engineer runs a suspicious file in a sandbox analysis tool to see the outcome. The analysis report shows that outbound callouts were made post infection.
Which two pieces of information from the analysis report are needed to investigate the callouts? (Choose two.)
- A . signatures
- B . host IP addresses
- C . file size
- D . dropped files
- E . domain names
Which type of data consists of connection level, application-specific records generated from network traffic?
- A . transaction data
- B . location data
- C . statistical data
- D . alert data
DRAG DROP
Drag and drop the uses on the left onto the type of security system on the right.