
Cisco 200-201 Practice Exams
Last updated on Nov 16,2026- Exam Code: 200-201
- Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
When trying to evade IDS/IPS devices, which mechanism allows the user to make the data incomprehensible without a specific key, certificate, or password?
- A . fragmentation
- B . pivoting
- C . encryption
- D . stenography
A malicious file has been identified in a sandbox analysis tool.
Which piece of information is needed to search for additional downloads of this file by other hosts?
- A . file header type
- B . file size
- C . file name
- D . file hash value
An engineer is investigating a case of the unauthorized usage of the “Tcpdump” tool. The analysis revealed that a malicious insider attempted to sniff traffic on a specific interface.
What type of information did the malicious insider attempt to obtain?
- A . tagged protocols being used on the network
- B . all firewall alerts and resulting mitigations
- C . tagged ports being used on the network
- D . all information and data within the datagram
Refer to the exhibit.
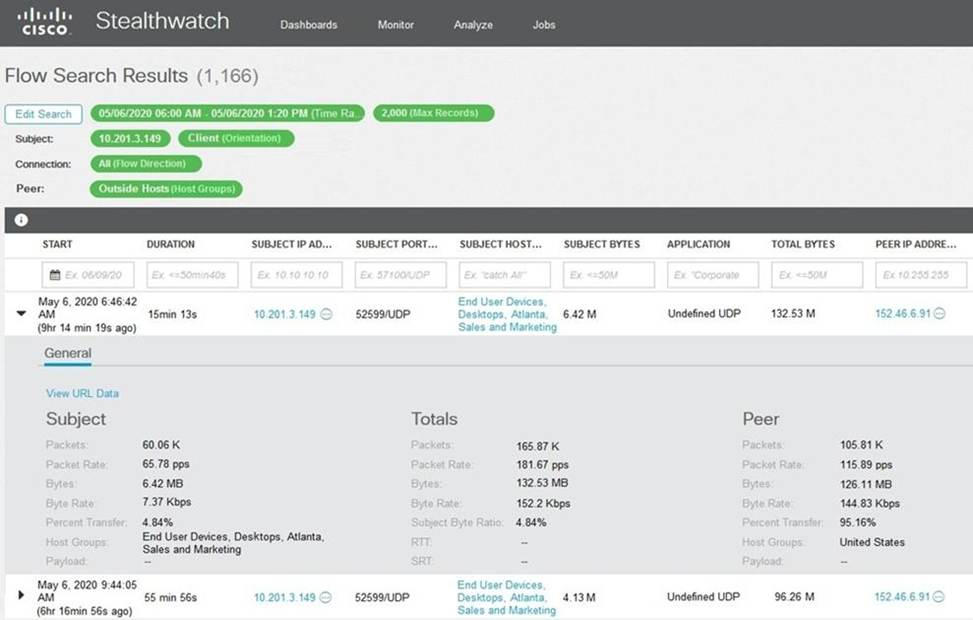
What is the potential threat identified in this Stealthwatch dashboard?
- A . Host 10.201.3.149 is sending data to 152.46.6.91 using TCP/443.
- B . Host 152.46.6.91 is being identified as a watchlist country for data transfer.
- C . Traffic to 152.46.6.149 is being denied by an Advanced Network Control policy.
- D . Host 10.201.3.149 is receiving almost 19 times more data than is being sent to host 152.46.6.91.
Which attack method intercepts traffic on a switched network?
- A . denial of service
- B . ARP cache poisoning
- C . DHCP snooping
- D . command and control
What is a purpose of a vulnerability management framework?
- A . identifies, removes, and mitigates system vulnerabilities
- B . detects and removes vulnerabilities in source code
- C . conducts vulnerability scans on the network
- D . manages a list of reported vulnerabilities
Refer to the exhibit.
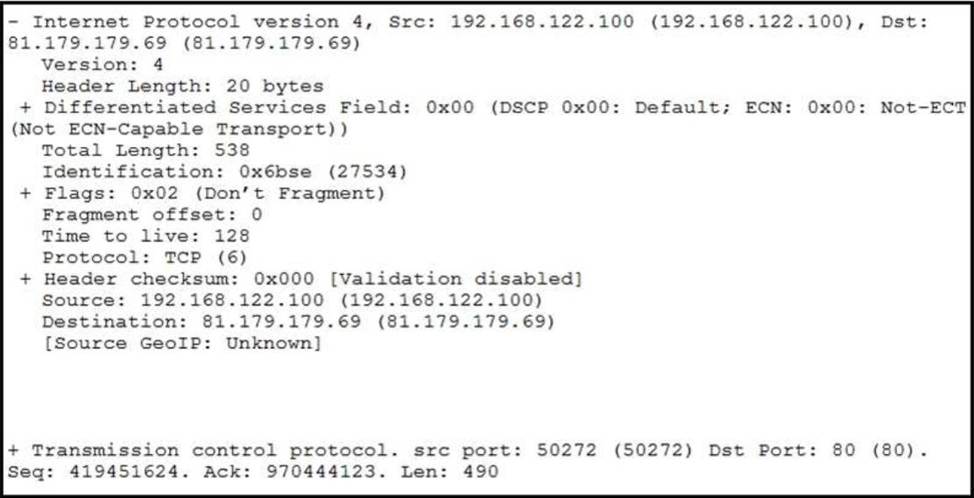
What should be interpreted from this packet capture?
- A . 81.179.179.69 is sending a packet from port 80 to port 50272 of IP address 192.168.122.100 using UDP protocol.
- B . 192.168.122.100 is sending a packet from port 50272 to port 80 of IP address 81.179.179.69 using TCP protocol.
- C . 192.168.122.100 is sending a packet from port 80 to port 50272 of IP address 81.179.179.69 using UDP protocol.
- D . 81.179.179.69 is sending a packet from port 50272 to port 80 of IP address 192.168.122.100 using TCP UDP protocol.
An employee reports that someone has logged into their system and made unapproved changes, files are out of order, and several documents have been placed in the recycle bin. The security specialist reviewed the system logs, found nothing suspicious, and was not able to determine what occurred. The software is up to date; there are no alerts from antivirus and no failed login attempts.
What is causing the lack of data visibility needed to detect the attack?
- A . The threat actor used a dictionary-based password attack to obtain credentials.
- B . The threat actor gained access to the system by known credentials.
- C . The threat actor used the teardrop technique to confuse and crash login services.
- D . The threat actor used an unknown vulnerability of the operating system that went undetected.
A security specialist notices 100 HTTP GET and POST requests for multiple pages on the web servers. The agent in the requests contains PHP code that, if executed, creates and writes to a new PHP file on the webserver.
Which event category is described?
- A . reconnaissance
- B . action on objectives
- C . installation
- D . exploitation
An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap.
Which command will accomplish this goal?
- A . nmap –top-ports 192.168.1.0/24
- B . nmap CsP 192.168.1.0/24
- C . nmap -sL 192.168.1.0/24
- D . nmap -sV 192.168.1.0/24