
Cisco 200-201 Practice Exams
Last updated on Nov 16,2026- Exam Code: 200-201
- Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which security monitoring data type requires the largest storage space?
- A . transaction data
- B . statistical data
- C . session data
- D . full packet capture
Which list identifies the information that the client sends to the server in the negotiation phase of the TLS handshake?
- A . ClientStart, ClientKeyExchange, cipher-suites it supports, and suggested compression methods
- B . ClientStart, TLS versions it supports, cipher-suites it supports, and suggested compression methods
- C . ClientHello, TLS versions it supports, cipher-suites it supports, and suggested compression methods
- D . ClientHello, ClientKeyExchange, cipher-suites it supports, and suggested compression methods
Refer to the exhibit.
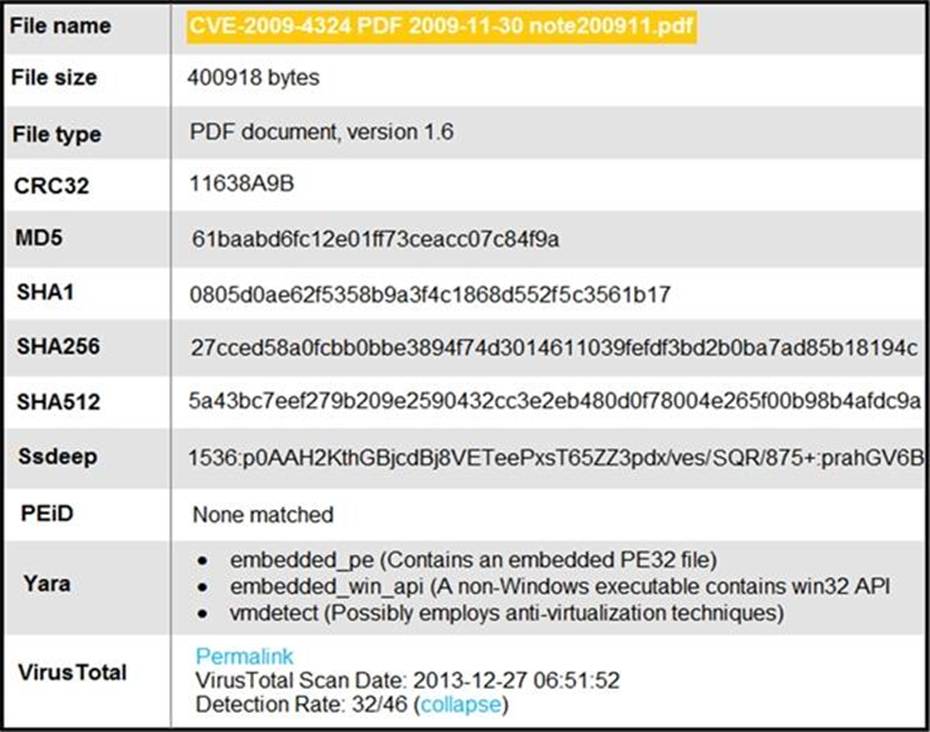
An engineer is analyzing this Cuckoo Sandbox report for a PDF file that has been downloaded from an email.
What is the state of this file?
- A . The file has an embedded executable and was matched by PEiD threat signatures for further analysis.
- B . The file has an embedded non-Windows executable but no suspicious features are identified.
- C . The file has an embedded Windows 32 executable and the Yara field lists suspicious features for further analysis.
- D . The file was matched by PEiD threat signatures but no suspicious features are identified since the signature list is up to date.
Refer to the exhibit.

Which event is occurring?
- A . A binary named "submit" is running on VM cuckoo1.
- B . A binary is being submitted to run on VM cuckoo1
- C . A binary on VM cuckoo1 is being submitted for evaluation
- D . A URL is being evaluated to see if it has a malicious binary
Refer to the exhibit.
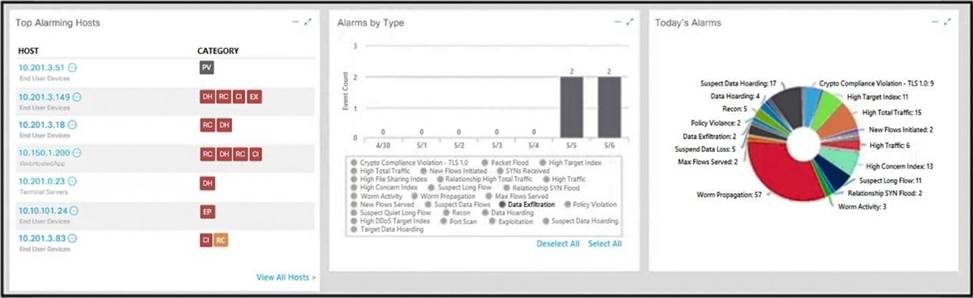
What is the potential threat identified in this Stealthwatch dashboard?
- A . A policy violation is active for host 10.10.101.24.
- B . A host on the network is sending a DDoS attack to another inside host.
- C . There are two active data exfiltration alerts.
- D . A policy violation is active for host 10.201.3.149.
Refer to the exhibit.
Which type of log is displayed?
- A . IDS
- B . proxy
- C . NetFlow
- D . sys
What is the virtual address space for a Windows process?
- A . physical location of an object in memory
- B . set of pages that reside in the physical memory
- C . system-level memory protection feature built into the operating system
- D . set of virtual memory addresses that can be used
An analyst is investigating a host in the network that appears to be communicating to a command and control server on the Internet. After collecting this packet capture, the analyst cannot determine the technique and payload used for the communication.
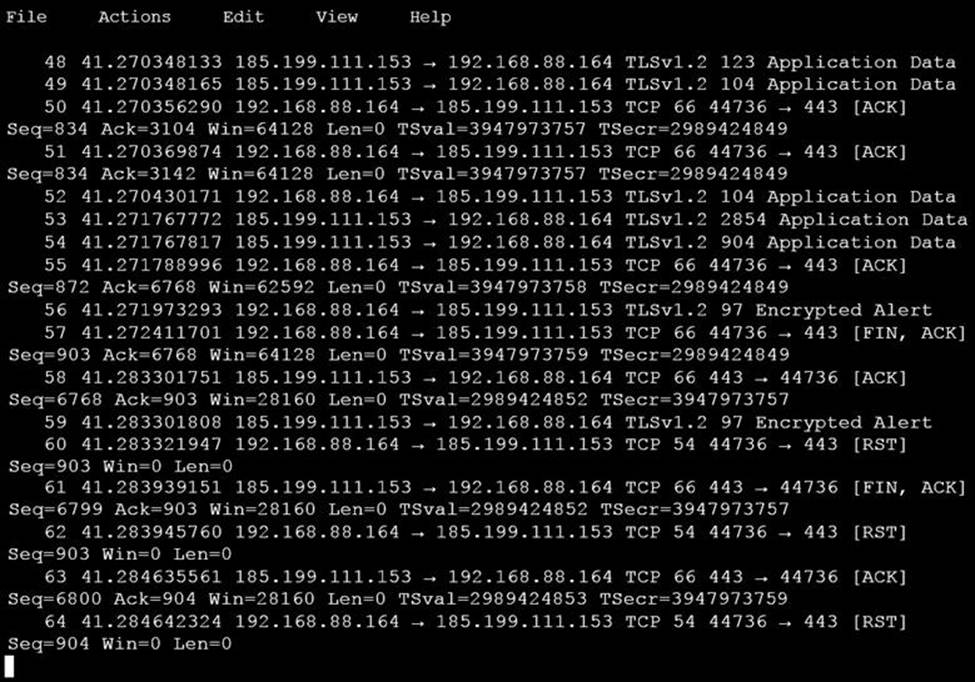
Which obfuscation technique is the attacker using?
- A . Base64 encoding
- B . TLS encryption
- C . SHA-256 hashing
- D . ROT13 encryption
Refer to the exhibit.
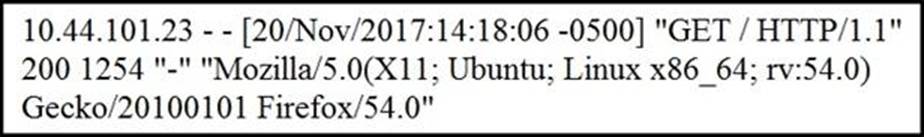
What does the message indicate?
- A . an access attempt was made from the Mosaic web browser
- B . a successful access attempt was made to retrieve the password file
- C . a successful access attempt was made to retrieve the root of the website
- D . a denied access attempt was made to retrieve the password file
What is the practice of giving employees only those permissions necessary to perform their specific role within an organization?
- A . least privilege
- B . need to know
- C . integrity validation
- D . due diligence