
Splunk SPLK-2003 Practice Exams
Last updated on Oct 07,2026- Exam Code: SPLK-2003
- Exam Name: Splunk SOAR Certified Automation Developer Exam
- Certification Provider: Splunk
- Latest update: Oct 07,2026
Which of the following can be edited or deleted in the Investigation page?
- A . Action results
- B . Comments
- C . Approval records
- D . Artifact values
B
Explanation:
On the Investigation page in Splunk SOAR, users have the ability to edit or delete comments associated with an event or a container. Comments are generally used for collaboration and to provide additional context to an investigation. While action results, approval records, and artifact values are typically not editable or deletable to maintain the integrity of the investigative data, comments are more flexible and can be managed by users to reflect the current state of the investigation.
Investigation page allows you to view and edit various information and data related to an event or a case. One of the things that you can edit or delete in the Investigation page is the comments that you or other users have added to the activity feed. Comments are a way of communicating and collaborating with other users during the investigation process. You can edit or delete your own comments by clicking on the three-dot menu icon next to the comment and selecting the appropriate option. You can also reply to other users’ comments by clicking on the reply icon. Therefore, option B is the correct answer, as it is the only option that can be edited or deleted in the Investigation page.
Option A is incorrect, because action results are the outputs of the actions or playbooks that have been run on the event or case, and they cannot be edited or deleted in the Investigation page.
Option C is incorrect, because approval records are the logs of the approval requests and responses that have been made for certain actions or playbooks, and they cannot be edited or deleted in the Investigation page.
Option D is incorrect, because artifact values are the data that has been collected or generated by the event or case, and they cannot be edited or deleted in the Investigation page.
1: Start with Investigation in Splunk SOAR (Cloud)
When configuring a Splunk asset for SOAR to connect to a Splunk Cloud instance, the user discovers that they need to be able to run two different on_poll searches.
How is this possible?
- A . Install a second Splunk app and configure the query in the second app.
- B . Configure the second query in the Splunk App for SOAR Export.
- C . Enter the two queries in the asset as comma separated values.
- D . Configure a second Splunk asset with the second query.
D
Explanation:
In Splunk SOAR, when needing to run multiple on_poll searches to a Splunk Cloud instance, the recommended approach is to configure a second Splunk asset specifically for the second query. This method allows each Splunk asset to maintain its own settings and query configurations, ensuring that each search can be managed and optimized independently. This separation also helps in troubleshooting and maintaining clarity in the configuration.
Option A, installing a second Splunk app, is not necessarily relevant as the app itself does not determine the number of queries but rather how they are managed and processed through assets.
Option B, configuring the second query in the Splunk App for SOAR Export, does not apply as this app typically handles data exportation from SOAR to Splunk, not managing multiple polling queries.
Option C, entering the two queries as comma-separated values, would not be practical or functional as Splunk SOAR’s asset configuration does not process multiple queries in this manner for polling purposes.
When configuring a Splunk asset for SOAR to connect to a Splunk Cloud instance and there is a need to run two different on_poll searches, the appropriate action is to configure a second Splunk asset with the second query. This allows each Splunk asset to have its own unique on_poll search configuration, enabling them to run independently and retrieve different sets of data as required. The other options, such as installing a second app or entering queries as comma-separated values, are not standard practices for managing multiple on_poll searches in Splunk SOAR1.
Reference: Splunk SOAR documentation on configuring search in Splunk SOAR1.
Which two playbook blocks can discern which path in the playbook to take next?
- A . Prompt and decision blocks.
- B . Decision and action blocks.
- C . Filter and decision blocks.
- D . Filter and prompt blocks.
A
Explanation:
https://docs.splunk.com/Documentation/SOAR/current/Playbook/DecisionBlock
In Splunk SOAR playbooks, the blocks that can discern which path to take next are the prompt and decision blocks. The prompt block allows the playbook to pause and wait for user input, which can then determine the subsequent path of execution based on the response provided. The decision block evaluates conditions based on data within the playbook and directs the flow to different paths accordingly11.
The decision block is used to change the flow of artifacts by performing IF, ELSE IF, or ELSE functions. When an artifact meets a True condition, it is passed downstream to the corresponding block in the playbook flow11. The prompt block, on the other hand, interacts with users to make decisions during playbook execution, which can also influence the direction of the playbook’s flow.
Reference: Splunk SOAR documentation on using decisions to send artifacts to a specific downstream action in your playbook
Which of the following is a best practice for use of the global block?
- A . Execute code at the beginning of each run of the playbook.
- B . Declare outputs which will be selectable within playbook blocks.
- C . Import packages which will be used within the playbook.
- D . Execute custom code after each run of the playbook.
C
Explanation:
The global block within a Splunk SOAR playbook is primarily used to import external packages or define global variables that will be utilized across various parts of the playbook. This block sets the stage for the playbook by ensuring that all necessary libraries, modules, or predefined variables are available for use in subsequent actions, decision blocks, or custom code segments within the playbook. This practice promotes code reuse and efficiency, enabling more sophisticated and powerful playbook designs by leveraging external functionalities.
Regarding the Splunk SOAR Automation Broker requirements, which of the following statements is not correct?
- A . The Splunk SOAR Automation Broker requires outbound/egress connectivity to the Splunk SOAR (Cloud) or Splunk SOAR (On-premises) instance.
- B . The Splunk SOAR Automation Broker must be able to connect to TCP port 443 (HTTPS) on the Splunk SOAR (Cloud) or Splunk SOAR (On-premises) instance.
- C . The Splunk SOAR Automation Broker requires both inbound/ingress and outbound/egress connectivity to the Splunk SOAR (Cloud) or Splunk SOAR (On-premises) instance.
- D . The Splunk SOAR Automation Broker requires inbound/ingress network connection from the Splunk SOAR (Cloud) or Splunk SOAR (On-premises) instance.
D
Explanation:
The Splunk SOAR Automation Broker does not require inbound/ingress network connections from the Splunk SOAR (Cloud) or (On-premises) instance. Instead, it requires only outbound/egress connectivity. The Automation Broker is responsible for securely communicating with SOAR to execute actions, retrieve data, and send results, but this communication is initiated from the Automation Broker towards SOAR, using outbound connections (typically over TCP port 443). This ensures that no inbound connections need to be established, which simplifies firewall and security configurations.
Thus, option D is the incorrect statement, making it the right answer for this question.
Reference: Splunk SOAR Documentation: Automation Broker Requirements.
Splunk SOAR Cloud and On-Premises Deployment Guide.
A new project requires event data from SOAR to be sent to an external system via REST. All events with the label notable that are in new status should be sent.
Which of the following REST Django expressions will select the correct events?
A)
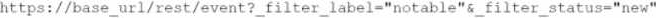
B)
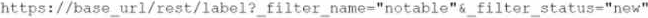
C)
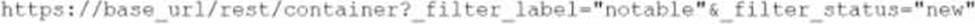
D)
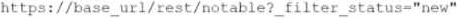
- A . Option A
- B . Option B
- C . Option C
- D . Option D
C
Explanation:
The correct REST Django expression to retrieve events with the label "notable" that are in the "new" status is using the container endpoint, as containers are used to store events and associated data in Splunk SOAR. The expression correctly filters the events by label (_filter_label="notable") and status (_filter_status="new"), ensuring only notable events that are still in the "new" status are selected.
A and D reference the wrong endpoints (event and notable respectively), which do not align with the container-based model used in Splunk SOAR for storing and filtering events.
B is incorrect due to the use of _filter_name instead of _filter_label, which is not a valid filter in this context.
Reference: Splunk SOAR Documentation: REST API Endpoints.
Splunk SOAR Developer Guide: Using Django REST for Filtering.
To limit the impact of custom code on the VPE, where should the custom code be placed?
- A . A custom container or a separate KV store.
- B . A separate code repository.
- C . A custom function block.
- D . A separate container.
C
Explanation:
To limit the impact of custom code on the Visual Playbook Editor (VPE) in Splunk SOAR, custom code should be placed within a custom function block. Custom function blocks are designed to encapsulate code within a playbook, allowing users to input their own Python code and execute it as part of the playbook run. By confining custom code to these blocks, it maintains the VPE’s performance and stability by isolating the custom code from the core functions of the playbook.
A custom function block is a way of adding custom Python code to your playbook, which can expand the functionality and processing of your playbook logic. Custom functions can also interact with the REST API in a customizable way. You can share custom functions across your team and across multiple playbooks to increase collaboration and efficiency. To create custom functions, you must have Edit Code permissions, which can be configured by an Administrator in Administration > User Management > Roles and Permissions. Therefore, option C is the correct answer, as it is the recommended way of placing custom code on the VPE, which limits the impact of custom code on the VPE performance and security.
Option A is incorrect, because a custom container or a separate KV store are not valid ways of placing custom code on the VPE, but rather ways of storing data or artifacts.
Option B is incorrect, because a separate code repository is not a way of placing custom code on the VPE, but rather a way of managing and versioning your code outside of Splunk SOAR.
Option D is incorrect, because a separate container is not a way of placing custom code on the VPE, but rather a way of creating a new event or case.
1: Add custom code to your Splunk SOAR (Cloud) playbook with the custom function block using the classic playbook editor
When is using decision blocks most useful?
- A . When selecting one (or zero) possible paths in the playbook.
- B . When processing different data in parallel.
- C . When evaluating complex, multi-value results or artifacts.
- D . When modifying downstream data hi one or more paths in the playbook.
A
Explanation:
Decision blocks are most useful when selecting one (or zero) possible paths in the playbook. Decision blocks allow the user to define one or more conditions based on action results, artifacts, or custom expressions, and execute the corresponding path if the condition is met. If none of the conditions are met, the playbook execution ends. Decision blocks are not used for processing different data in parallel, evaluating complex, multi-value results or artifacts, or modifying downstream data in one or more paths in the playbook. Decision blocks within Splunk Phantom playbooks are used to control the flow of execution based on certain criteria. They are most useful when you need to select one or potentially no paths for the playbook to follow, based on the evaluation of specified conditions. This is akin to an if-else or switch-case logic in programming where depending on the conditions met, a particular path is chosen for further actions. Decision blocks evaluate the data and direct the playbook to different paths accordingly, making them a fundamental component for creating dynamic and responsive automation workflows.
A filter block with only one condition configured which states: artifact.*.cef .sourceAddress !- , would permit which of the following data to pass forward to the next block?
- A . Null IP addresses
- B . Non-null IP addresses
- C . Non-null destinationAddresses
- D . Null values
B
Explanation:
A filter block with only one condition configured which states: artifact.*.cef .sourceAddress !- , would permit only non-null IP addresses to pass forward to the next block. The !- operator means “is not null”. The other options are not valid because they either include null values or other fields than sourceAddress. See Filter block for more details. A filter block in Splunk SOAR that is configured with the condition artifact.*.cef.sourceAddress != (assuming the intention was to use "!=" to denote ‘not equal to’) is designed to allow data that has non-null sourceAddress values to pass through to subsequent blocks. This means that any artifact data within the container that includes a sourceAddress field with a defined value (i.e., an actual IP address) will be permitted to move forward in the playbook. The filter effectively screens out any artifacts that do not have a source address specified, focusing the playbook’s actions on those artifacts that contain valid IP address information in the sourceAddress field.
Within the 12A2 design methodology, which of the following most accurately describes the last step?
- A . List of the apps used by the playbook.
- B . List of the actions of the playbook design.
- C . List of the outputs of the playbook design.
- D . List of the data needed to run the playbook.
C
Explanation:
The correct answer is C because the last step of the 12A2 design methodology is to list the outputs of the playbook design. The outputs are the expected results or outcomes of the playbook execution, such as sending an email, creating a ticket, blocking an IP, etc. The outputs should be aligned with the objectives and goals of the playbook. See Splunk SOAR Certified Automation Developer for more details.
The 12A2 design methodology in the context of Splunk SOAR (formerly Phantom) refers to a structured approach to developing playbooks. The last step in this methodology focuses on defining the outputs of the playbook design. This step is crucial as it outlines what the expected results or actions the playbook should achieve upon its completion. These outputs can vary widely, from sending notifications, creating tickets, updating statuses, to generating reports. Defining the outputs is essential for understanding the playbook’s impact on the security operation workflows and how it contributes to resolving security incidents or automating tasks.