
PECB ISO-IEC-27001 Lead Auditor Practice Exams
Last updated on Oct 22,2026- Exam Code: ISO-IEC-27001 Lead Auditor
- Exam Name: PECB Certified ISO/IEC 27001 Lead Auditor exam
- Certification Provider: PECB
- Latest update: Oct 22,2026
You are performing an ISMS audit at a residential nursing home that provides healthcare services.
The next step in your audit plan is to verify the information security incident management process.
The IT Security Manager presents the information security incident management procedure (Document reference ID: ISMS_L2_16, version 4) and explains that the process is based on ISO/IEC 27035-1:2016.
You review the document and notice a statement "any information security weakness, event, and incident should be reported to the Point of Contact (PoC) within 1 hour after identification". When interviewing staff, you found that there were differences in the understanding of the meaning of "weakness, event, and incident".
The IT Security Manager explained that an online "information security handling" training seminar was conducted 6 months ago. All of the interviewed persons participated in and passed the reporting exercise and course assessment.
You are preparing the audit findings. Select two options that are correct.
- A . There is a nonconformity (NC). The information security incident training has failed. This is not conforming with clause 7.2 and control A.6.3.
- B . There is a nonconformity (NC). The terminology of the the incident management reporting process is unclear as evidenced by staff misunderstanding of the meaning of "weakness, event and incident". This is not conforming with clause 9.1 and control A.5.24.
- C . There is an opportunity for improvement (OFI). The information security incident training effectiveness can be improved. This is relevant to clause 7.2 and control A.6.3.
- D . There is an opportunity for improvement (OFI). The information security weaknesses, events, and incidents are reported. This is relevant to clause 9.1 and control A.5.24.
- E . There is no nonconformance. The information security handling training has been effective. This conforms with clause 7.2 and control A.6.3.
- F . There is no nonconformance. The information security weaknesses, events, and incidents are reported. This conforms with clause 9.1 and control A.5.24.
BC
Explanation:
According to ISO/IEC 27001:2022 clause 7.2, the organization must ensure that the persons doing work under its control are aware of the information security policy, their contribution to the effectiveness of the ISMS, the implications of not conforming to the ISMS requirements, and the benefits of improved information security performance. The organization must also provide information security awareness education and training to its personnel and relevant interested parties. According to control A.6.3, the organization must ensure that all employees and contractors are made aware of the information security incident management procedures and their expected roles and responsibilities. Therefore, an opportunity for improvement (OFI) can be identified if the information security incident training effectiveness can be improved, as evidenced by the differences in the understanding of the meaning of “weakness, event, and incident” among the staff.
According to ISO/IEC 27001:2022 clause 9.1, the organization must monitor, measure, analyze and evaluate the information security performance and the effectiveness of the ISMS. The organization must also retain appropriate documented information as evidence of the monitoring and measurement results.
According to control A.5.24, the organization must establish and maintain an information security incident management process that includes the following activities:
• reporting information security events and weaknesses;
• assessing and deciding on information security events;
• responding to information security incidents;
• learning from information security incidents;
• collecting evidence and disclosing information.
Therefore, a nonconformity (NC) can be identified if the terminology of the incident management reporting process is unclear, as evidenced by the staff misunderstanding of the meaning of “weakness, event, and incident”. This could lead to inconsistent or inaccurate reporting, assessment, response, learning, and disclosure of information security incidents, which could affect the information security performance and the effectiveness of the ISMS.
Reference:
• ISO/IEC 27001:2022, clauses 7.2, 9.1, and Annex A controls A.5.24 and A.6.3
• [PECB Candidate Handbook ISO/IEC 27001 Lead Auditor], pages 15-16, 18-19, 22-23
• ISO/IEC 27035-1:2016, clauses 4, 5, 6, 7, and 8
• ISO 27001 C Annex A.16: Information Security Incident Management
• ISO 27001:2022 Annex A Control 5.24 – What’s New?
You are conducting an ISMS audit in the despatch department of an international logistics organisation that provides shipping services to large organisations including local hospitals and government offices. Parcels typically contain pharmaceutical products, biological samples, and documents such as passports and driving licences. You note that the company records show a very large number of returned items with causes including misaddressed labels and, in 15% of cases, two or more labels for different addresses for the one package. You are interviewing the Shipping Manager (SM).
You: Are items checked before being dispatched?
SM: Any obviously damaged items are removed by the duty staff before being dispatched, but the
small profit margin makes it uneconomic to
implement a formal checking process.
You: What action is taken when items are returned?
SM: Most of these contracts are relatively low value, therefore it has been decided that it is easier and more convenient to simply reprint the label and re-send individual parcels than it is to implement an investigation.
You raise a nonconformity. Referencing the scenario, which three of the following Annex A controls would you expect the auditee to have implemented when you conduct the follow-up audit?
- A . 5.11 Return of assets
- B . 5.13 Labelling of information
- C . 5.3 Segregation of duties
- D . 5.32 Intellectual property rights
- E . 5.34 Privacy and protection of personal identifiable information (PII)
- F . 5.6 Contact with special interest groups
- G . 6.3 Information security awareness, education, and training
- H . 6.4 Disciplinary process
BEG
Explanation:
The three Annex A controls that you would expect the auditee to have implemented when you conduct the follow-up audit are:
B. 5.13 Labelling of information
E. 5.34 Privacy and protection of personal identifiable information (PII)
G. 6.3 Information security awareness, education, and training
B. This control requires the organisation to label information assets in accordance with the information classification scheme, and to handle them accordingly12. This control is relevant for the auditee because it could help them to avoid misaddressing labels and sending parcels to wrong destinations, which could compromise the confidentiality, integrity, and availability of the information assets. By labelling the information assets correctly, the auditee could also ensure that they are delivered to the intended recipients and that they are protected from unauthorized access, use, or disclosure.
E. This control requires the organisation to protect the privacy and the rights of individuals whose personal identifiable information (PII) is processed by the organisation, and to comply with the applicable legal and contractual obligations13. This control is relevant for the auditee because it could help them to prevent the unauthorized use of residents’ personal data by a supplier, which could violate the privacy and the rights of the residents and their family members, and expose the auditee to legal and reputational risks. By protecting the PII of the residents and their family members, the auditee could also enhance their trust and satisfaction, and avoid complaints and disputes.
G. This control requires the organisation to ensure that all employees and contractors are aware of the information security policy, their roles and responsibilities, and the relevant information security procedures and controls14. This control is relevant for the auditee because it could help them to improve the information security culture and behaviour of their staff, and to reduce the human errors and negligence that could lead to information security incidents. By providing information security awareness, education, and training to their staff, the auditee could also increase their competence and performance, and ensure the effectiveness and efficiency of the information security processes and controls.
Reference: 1: ISO/IEC 27001:2022 – Information technology ― Security techniques ― Information security management systems ― Requirements, Annex A 2: ISO/IEC 27002:2022 – Information technology ― Security techniques ― Code of practice for information security controls, clause 8.2.1 3: ISO/IEC 27002:2022 – Information technology ― Security techniques ― Code of practice for information security controls, clause 18.1.4 4: ISO/IEC 27002:2022 – Information technology ― Security techniques ― Code of practice for information security controls, clause 7.2.2
DRAG DROP
Select the words that best complete the sentence below to describe audit resources:
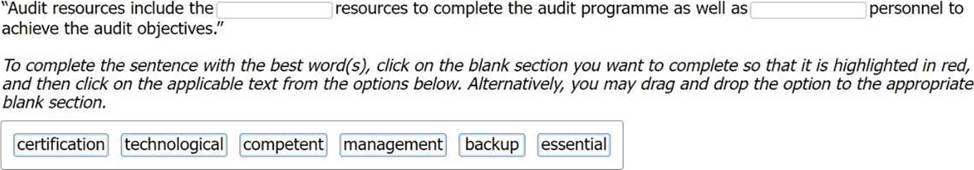
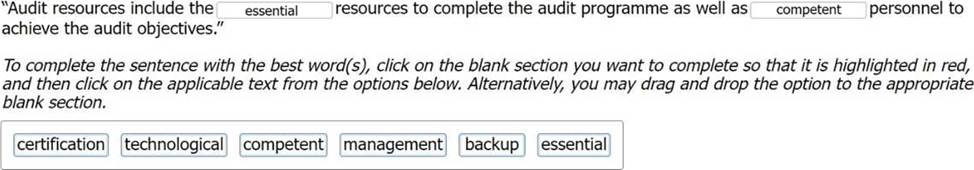
Explanation:
According to ISO 19011:2018, clause 5.3, the person responsible for managing the audit programme should determine the resources necessary for the audit programme, such as the audit team members, the budget, the time, the tools, etc. The audit resources should be sufficient and appropriate to ensure the quality and effectiveness of the audit programme and the audit results. The audit resources include the following elements12:
Essential resources: These are the resources that are required to conduct the audit programme and the individual audits, such as the audit documents, the audit methods, the audit tools, the audit schedule, the audit budget, etc. The essential resources should be identified and allocated based on the audit objectives, scope, and criteria, and the availability and cooperation of the auditee. The essential resources should also be reviewed and updated as necessary to reflect any changes or deviations in the audit programme or the individual audits.
Competent personnel: These are the audit team members who have the appropriate knowledge, skills, and experience to conduct the audit effectively and efficiently, and to provide credible and reliable audit results and recommendations. The competent personnel should include the audit team leader, the auditors, and any technical experts or observers who support the audit team. The competent personnel should be selected and appointed based on the audit objectives, scope, and criteria, and the specific competence requirements for the audit programme and the individual audits. The competent personnel should also be independent and impartial, and avoid any conflicts of interest or self-interest that may affect the audit results or the audit decisions.
Reference: ISO 19011:2018 – Guidelines for auditing management systems, clause 5.3 PECB Candidate Handbook ISO 27001 Lead Auditor, page 19
You are performing an ISMS audit at a residential nursing home called ABC that provides healthcare services. You find all nursing home residents wear an electronic wristband for monitoring their location, heartbeat, and blood pressure always. You learned that he electronic wristband automatically uploads all data to the artificial intelligence (AI) cloud server for healthcare monitoring and analysis by healthcare staff.
To verify the scope of ISMS, you interview the management system representative (MSR) who explains that the ISMS scope covers an outsourced data center.
Select four options for the clauses and/or controls of ISO/IEC 27001:2022 that are directly relevant to the verification of the scope of the ISMS.
- A . Control 5.3 Organizational roles, responsibilites and authorities
- B . Clause 4.2 Understanding the needs and expectations of interested parties
- C . Control 5.3 Legal, statutory, regulatory and contractual requirements
- D . Control 6.3 Information security awareness, education, and training
- E . Clause 5.2 Policy
- F . Clause 4.1 Understanding the organization and its context
- G . Control 7.6 Working in secure areas
- H . Clause 4.3 Determining the scope of the information security management system
BEFH
Explanation:
B. This clause requires the organisation to determine the interested parties that are relevant to the ISMS, and the requirements of these interested parties12. This clause is relevant to the verification of the scope of the ISMS because it helps the organisation to identify the stakeholders that have an influence or an interest in the information security of the organisation, such as customers, suppliers, regulators, employees, etc. The organisation should also consider the needs and expectations of these interested parties when defining the scope of the ISMS, and ensure that they are met and communicated.
E. This clause requires the organisation to establish an information security policy that provides the framework for setting the information security objectives and guiding the information security activities13. This clause is relevant to the verification of the scope of the ISMS because it helps the organisation to define the direction and principles of the ISMS, and to align them with the strategic goals and context of the organisation. The information security policy should also be consistent with the scope of the ISMS, and should be communicated and understood within the organisation and by relevant interested parties.
F. This clause requires the organisation to determine the internal and external issues that are relevant to the purpose and the context of the organisation, and that affect its ability to achieve the intended outcomes of the ISMS14. This clause is relevant to the verification of the scope of the ISMS because it helps the organisation to understand the factors and conditions that influence the information security of the organisation, such as the legal, technological, social, economic, environmental, etc. The organisation should also monitor and review these issues, and consider them when defining the scope of the ISMS.
H. This clause requires the organisation to determine the boundaries and applicability of the ISMS to establish its scope15. This clause is relevant to the verification of the scope of the ISMS because it helps the organisation to describe the information and processes that are included in the ISMS, and to document the scope in a clear and concise manner. The organisation should also consider the issues, requirements, and interfaces identified in clauses 4.1, 4.2, and 4.3 when determining the scope of the ISMS, and ensure that the scope is appropriate to the nature and scale of the organisation.
Reference: 1: PECB Candidate Handbook – ISO 27001 Lead Auditor, page 17 2: ISO/IEC 27001:2022 – Information technology ― Security techniques ― Information security management systems ― Requirements, clause 4.2 3: ISO/IEC 27001:2022 – Information technology ― Security techniques ― Information security management systems ― Requirements, clause 5.2 4: ISO/IEC 27001:2022 – Information technology ― Security techniques ― Information security management systems ― Requirements, clause 4.1 5: ISO/IEC 27001:2022 – Information technology ― Security techniques ― Information security management systems ― Requirements, clause 4.3
Scenario 5: Data Grid Inc. is a well-known company that delivers security services across the entire information technology infrastructure. It provides cybersecurity software, including endpoint security, firewalls, and antivirus software. For two decades, Data Grid Inc. has helped various companies secure their networks through advanced products and services. Having achieved reputation in the information and network security field, Data Grid Inc. decided to obtain the ISO/IEC 27001 certification to better secure its internal and customer assets and gain competitive advantage. Data Grid Inc. appointed the audit team, who agreed on the terms of the audit mandate. In addition, Data Grid Inc. defined the audit scope, specified the audit criteria, and proposed to close the audit within five days. The audit team rejected Data Grid Inc.’s proposal to conduct the audit within five days, since the company has a large number of employees and complex processes. Data Grid Inc. insisted that they have planned to complete the audit within five days, so both parties agreed upon conducting the audit within the defined duration. The audit team followed a risk-based auditing approach.
To gain an overview of the main business processes and controls, the audit team accessed process descriptions and organizational charts. They were unable to perform a deeper analysis of the IT risks and controls because their access to the IT infrastructure and applications was restricted. However, the audit team stated that the risk that a significant defect could occur to Data Grid Inc.’s ISMS was low since most of the company’s processes were automated. They therefore evaluated that the ISMS, as a whole, conforms to the standard requirements by asking the representatives of Data Grid Inc. the following questions:
• How are responsibilities for IT and IT controls defined and assigned?
• How does Data Grid Inc. assess whether the controls have achieved the desired results?
• What controls does Data Grid Inc. have in place to protect the operating environment and data from malicious software?
• Are firewall-related controls implemented?
Data Grid Inc.’s representatives provided sufficient and appropriate evidence to address all these questions.
The audit team leader drafted the audit conclusions and reported them to Data Grid Inc.’s top management. Though Data Grid Inc. was recommended for certification by the auditors, misunderstandings were raised between Data Grid Inc. and the certification body in regards to audit objectives. Data Grid Inc. stated that even though the audit objectives included the identification of areas for potential improvement, the audit team did not provide such information. Based on this scenario, answer the following question:
Data Grid Inc. is responsible for all the actions below, EXCEPT:
- A . Specifying the audit criteria
- B . Appointing the audit team
- C . Defining the audit scope
B
Explanation:
In the context of ISO/IEC 27001 audits, the audit team is appointed by the certification body, not by the organization being audited. Data Grid Inc. is responsible for specifying the audit criteria and defining the audit scope, but not for appointing the audit team.
Reference: ISO 19011:2018, Guidelines for auditing management systems
You ask the IT Manager why the organisation still uses the mobile app while personal data encryption and pseudonymization tests failed. Also, whether the Service Manager is authorized to approve the test.
The IT Manager explains the test results should be approved by him according to the software security management procedure. The reason why the encryption and pseudonymization functions failed is that these functions heavily slowed down the system and service performance. An extra 150% of resources are needed to cover this. The Service Manager agreed that access control is good enough and acceptable. That’s why the Service Manager signed the approval.
You sample one of the medical staff’s mobile and found that ABC’s healthcare mobile app, version 1.01 is installed. You found that version 1.01 has no test record.
The IT Manager explains that because of frequent ransomware attacks, the outsourced mobile app development company gave a free minor update on the tested software, performed an emergency release of the updated software, and gave a verbal guarantee that there will be no impact on any security functions. Based on his 20 years of information security experience, there is no need to re-test.
You are preparing the audit findings Select two options that are correct.
- A . There is NO nonconformity (NC). The IT Manager demonstrates he is fully competent. (Relevant to clause 7.2)
- B . There is a nonconformity (NC). The IT Manager does not comply with the software security management procedure. (Relevant to clause 8.1, control A.8.30)
- C . There is a nonconformity (NC). The organisation does not control planned changes and review the consequences of unintended changes. (Relevant to clause 8.1)
- D . There is an opportunity for improvement (OI). The organisation selects an external service provider based on the extent of free services it will provide. (Relevant to clause 8.1, control A.5.21)
- E . There is NO nonconformity (NC). The IT Manager demonstrates good leadership. (Relevant to clause 5.1, control 5.4)
- F . There is an opportunity for improvement (OI). The IT Manager should make the decision to continue the service based on appropriate testing. (Relevant to clause 8.1, control A.8.30)
BC
Explanation:
According to ISO 27001:2022 Annex A Control 8.30, the organisation shall ensure that externally provided processes, products or services that are relevant to the information security management system are controlled. This includes developing and entering into licensing agreements that cover code ownership and intellectual property rights, and implementing appropriate contractual requirements related to secure design and coding in accordance with Annex A 8.25 and 8.2912
In this case, the organisation and the developer have performed security tests that failed, which indicates that the secure design and coding requirements of Annex A 8.29 were not met. The IT Manager explains that the encryption and pseudonymization functions failed because they slowed down the system and service performance, and that an extra 150% of resources are needed to cover this. However, this does not justify the acceptance of the test results by the Service Manager, who is not authorised to approve the test according to the software security management procedure. The Service Manager should have consulted with the IT Manager, who is the owner of the process, and followed the procedure for handling nonconformities and corrective actions. The Service Manager’s decision to continue the service based on access control alone exposes the organisation to the risk of
compromising the confidentiality, integrity, and availability of personal data processed by the mobile app. Therefore, there is a nonconformity (NC) with clause 8.1, control A.8.30.
According to ISO 27001:2022 Clause 8.1, the organisation shall plan, implement and control the processes needed to meet information security requirements, and to implement the actions determined in Clause 6.1. The organisation shall also control planned changes and review the consequences of unintended changes, taking action to mitigate any adverse effects, as necessary12 In this case, the organisation has not controlled the planned change of the mobile app from version 1.0 to version 1.01, which was a minor update provided by the outsourced developer in response to frequent ransomware attacks. The IT Manager explains that the developer performed an emergency release of the updated software, and gave a verbal guarantee that there will be no impact on any security functions. However, this is not sufficient to ensure that the change is properly assessed, tested, documented, and approved before deployment. The IT Manager should have followed the change management process and procedure, and verified that the updated software meets the security requirements and does not introduce any new vulnerabilities or risks. The IT Manager’s reliance on his 20 years of information security experience and the developer’s verbal guarantee is not a valid basis for skipping the re-testing of the software. Therefore, there is a nonconformity (NC) with clause 8.1.
Reference: 1: ISO/IEC 27001:2022 Lead Auditor (Information Security Management Systems) Course by CQI and IRCA Certified Training 1 2: ISO/IEC 27001 Lead Auditor Training Course by PECB 2
OrgXY is an ISO/IEC 27001-certified software development company. A year after being certified, OrgXY’s top management informed the certification body that the company was not ready for conducting the surveillance audit.
What happens in this case?
- A . The certification is suspended
- B . The current certification is used until the next surveillance audit
- C . OrgXY transfers its registration to another certification body
A
Explanation:
If an organization like OrgXY informs the certification body that it is not ready to conduct the surveillance audit as scheduled, the certification may be suspended. This is because the surveillance audit is a critical part of the ongoing certification maintenance, required to ensure continued compliance with the standard.
Reference: PECB ISO/IEC 27001 Lead Auditor Course Material; ISO/IEC 27001:2013, general guidelines on certification and surveillance requirements
You are an experienced ISMS audit team leader. You are currently conducting a third-party surveillance audit of an international haulage organisation.
You have sampled four internal audit reports which state:
Report 1 – Auditor: Mr James.
Over the year the organisation has failed to meet its promised delivery dates on 23 occasions out of 100.
This is against a target of ‘95% of deliveries on time’.
Grading – Minor
Corrective Action due: Within 9 months.
Report 2 – Auditor: Mr James.
Between January and March, it was noted 125 complaints were received about the Service Desk Team. Clients accused them of being rude and unresponsive.
Grading – Minor
Corrective Action due: Within 12 months.
Report 3 – Auditor: Mr James.
Of the 40 customer orders received last month, 38 were correctly processed. Of the remaining 2, one was missing a signature and one was missing a date.
Grading –
Corrections due: Within 3 weeks
Report 4 – Auditor: Mr Rogers.
Of the 30 personnel records examined, 26 were found to be fully completed whilst the remaining 4 were all missing the individual’s start date.
Grading C Major
Corrections due: Within 1 week
Which four of the options demonstrate the concerns you would have about these reports?
- A . I would be concerned as to whether criteria for grading nonconformities are in existence in this organisation
- B . I would be concerned as to whether the auditors understand the difference between corrections and corrective actions
- C . I would be concerned because action taken to address a major nonconformity should always be completed sooner than action taken to address minor nonconformities
- D . I would be concerned that no grading is recorded for Report 3. This could indicate that the auditor
did not complete the report correctly or that they failed to make a determination as to severity - E . I would be concerned that the auditors focussed only on information security processes
- F . I would be concerned that timing for addressing the nonconformities is significantly different in the four reports
- G . I would have a concern that no nonconformity review was conducted
- H . I would have a concern that one auditor appeared to be conducting most of the internal audits
Scenario 9: UpNet, a networking company, has been certified against ISO/IEC 27001. It provides network security, virtualization, cloud computing, network hardware, network management software, and networking technologies.
The company’s recognition has increased drastically since gaining ISO/IEC 27001 certification. The certification confirmed the maturity of UpNefs operations and its compliance with a widely recognized and accepted standard.
But not everything ended after the certification. UpNet continually reviewed and enhanced its security controls and the overall effectiveness and efficiency of the ISMS by conducting internal audits. The top management was not willing to employ a full-time team of internal auditors, so they decided to outsource the internal audit function. This form of internal audits ensured independence, objectivity, and that they had an advisory role about the continual improvement of the ISMS.
Not long after the initial certification audit, the company created a new department specialized in data and storage products. They offered routers and switches optimized for data centers and software-based networking devices, such as network virtualization and network security appliances. This caused changes to the operations of the other departments already covered in the ISMS certification scope.
Therefore. UpNet initiated a risk assessment process and an internal audit. Following the internal audit result, the company confirmed the effectiveness and efficiency of the existing and new processes and controls.
The top management decided to include the new department in the certification scope since it complies with ISO/IEC 27001 requirements. UpNet announced that it is ISO/IEC 27001 certified and the certification scope encompasses the whole company.
One year after the initial certification audit, the certification body conducted another audit of UpNefs ISMS. This audit aimed to determine the UpNefs ISMS fulfillment of specified ISO/IEC 27001 requirements and ensure that the ISMS is being continually improved. The audit team confirmed that the certified ISMS continues to fulfill,the requirements of the standard. Nonetheless, the new department caused a significant impact on governing the management system. Moreover, the certification body was not informed about any changes. Thus, the UpNefs certification was suspended. Based on the scenario above, answer the following question:
Based on scenario 9, why was UpNefs certification suspended?
- A . Because UpNet used and applied the certification out of its scope
- B . Because UpNet outsourced the internal audit function
- C . Because UpNefs ISMS does not fulfill the requirements of the standard
A
Explanation:
UpNet’s certification was suspended because the certification body was not informed about the significant changes caused by the new department, impacting the governance of the management system. ISO/IEC 27001 requires organizations to inform the certification body of any changes that significantly impact the ISMS.