
Microsoft MD-102 Practice Exams
Last updated on Nov 16,2026- Exam Code: MD-102
- Exam Name: Endpoint Administrator
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
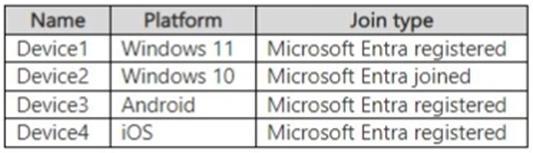
All the devices are enrolled in Microsoft Intune and have Microsoft 365 Apps for enterprise installed.
On which devices can you use the Cloud Policy service for Microsoft 365 to manage Microsoft 365 Apps for enterprise?
- A . Device2 only
- B . Device1 and Device2 only
- C . Device1, Device2, and Device3 only
- D . Device1, Device2, and Device4 only
- E . Device1, Device2, Device3, and Device4
From the Microsoft Intune admin center, create a configuration profile.
From the Microsoft Intune admin center, create a configuration profile.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has a Microsoft Entra tenant named contoso.com that contains several Windows 10 devices.
When you join new Windows 10 devices to contoso.com, users are prompted to set up a four-digit pin.
You need to ensure that the users are prompted to set up a six-digit pin when they join the Windows 10 devices to contoso.com.
Solution: From the Microsoft Entra admin center, you configure automatic mobile device management (MDM) enrollment. From the Microsoft Intune admin center, you create and assign a device restrictions profile.
Does this meet the goal?
- A . Yes
- B . No
DRAG DROP
You have a Microsoft 365 subscription that contains the devices shown in the following table.
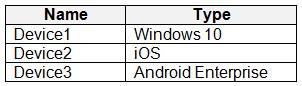
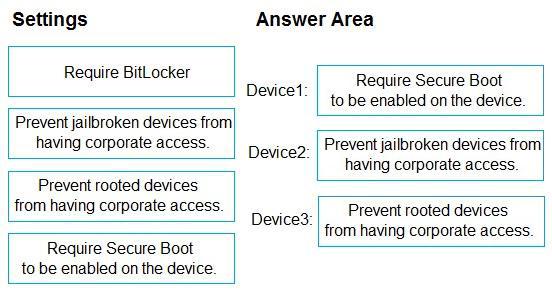
You need to ensure that only devices running trusted firmware or operating system builds can access network resources.
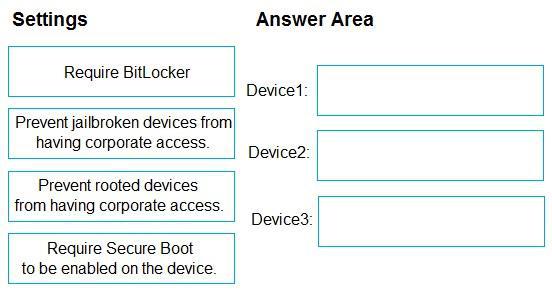
Which compliance policy setting should you configure for each device? To answer, drag the appropriate settings to the correct devices. Each setting may be used once, more than once, or not at all. You may
need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.
Select and Place:
DRAG DROP
You have a Microsoft 365 subscription that contains the devices shown in the following table.
You need to ensure that only devices running trusted firmware or operating system builds can access network resources.
Which compliance policy setting should you configure for each device? To answer, drag the appropriate settings to the correct devices. Each setting may be used once, more than once, or not at all. You may
need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.
Select and Place:
Testlet 2
Case study
Overview
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment
Network Environment
The network contains an on-premises Active Directory domain named adatum.com.
The domain contains the servers shown in the following table.
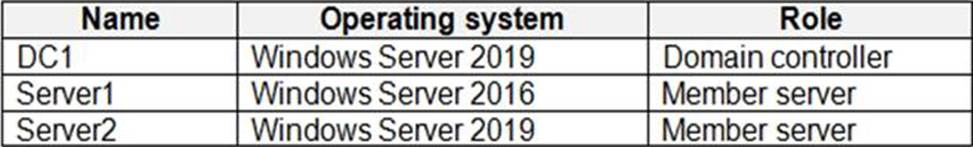
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups
The adatum.com tenant contains the users shown in the following table.
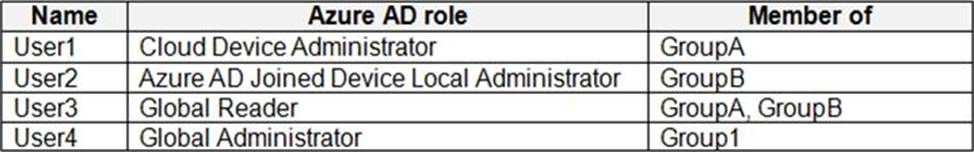
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices
ADatum has the Windows 10 devices shown in the following table.
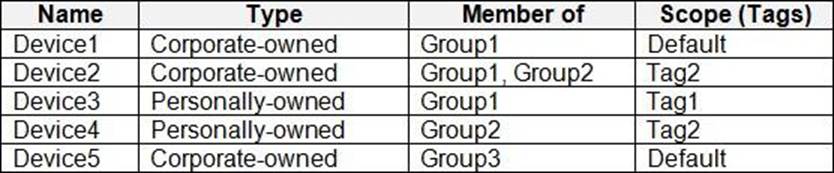
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
The Windows 10 devices are configured as shown in the following table.
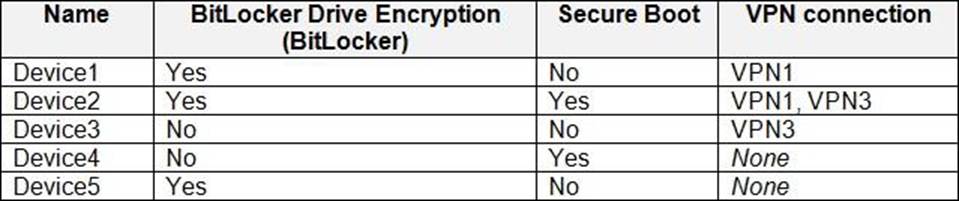
All the Azure AD joined devices have an executable file named C:AppA.exe and a folder named D: Folder1.
Microsoft Intune Configuration
Microsoft Intune has the compliance policies shown in the following table.
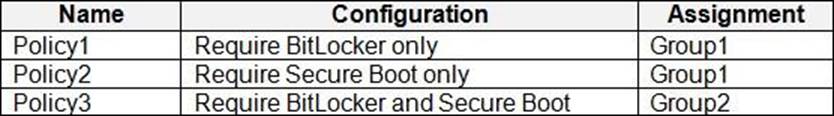
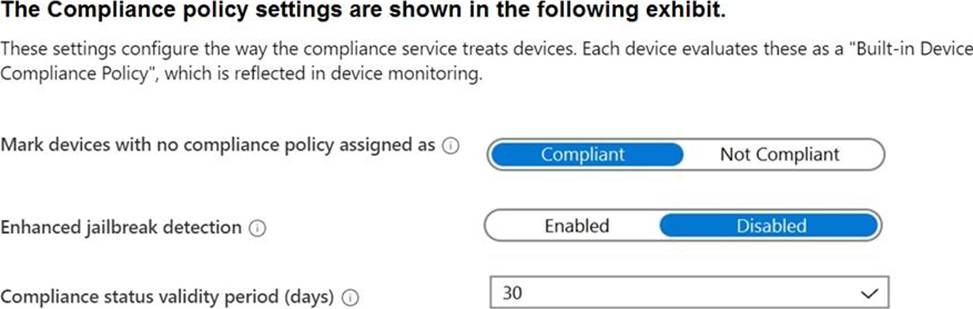
The Automatic Enrolment settings have the following configurations:
• MDM user scope GroupA
• MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
• Name: Protection1
• Folder protection: Enable
• List of apps that have access to protected folders: CVAppA.exe
• List of additional folders that need to be protected: D:Folderi1
• Assignments – Included groups: Group2, GroupB
Windows Autopilot Configuration
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
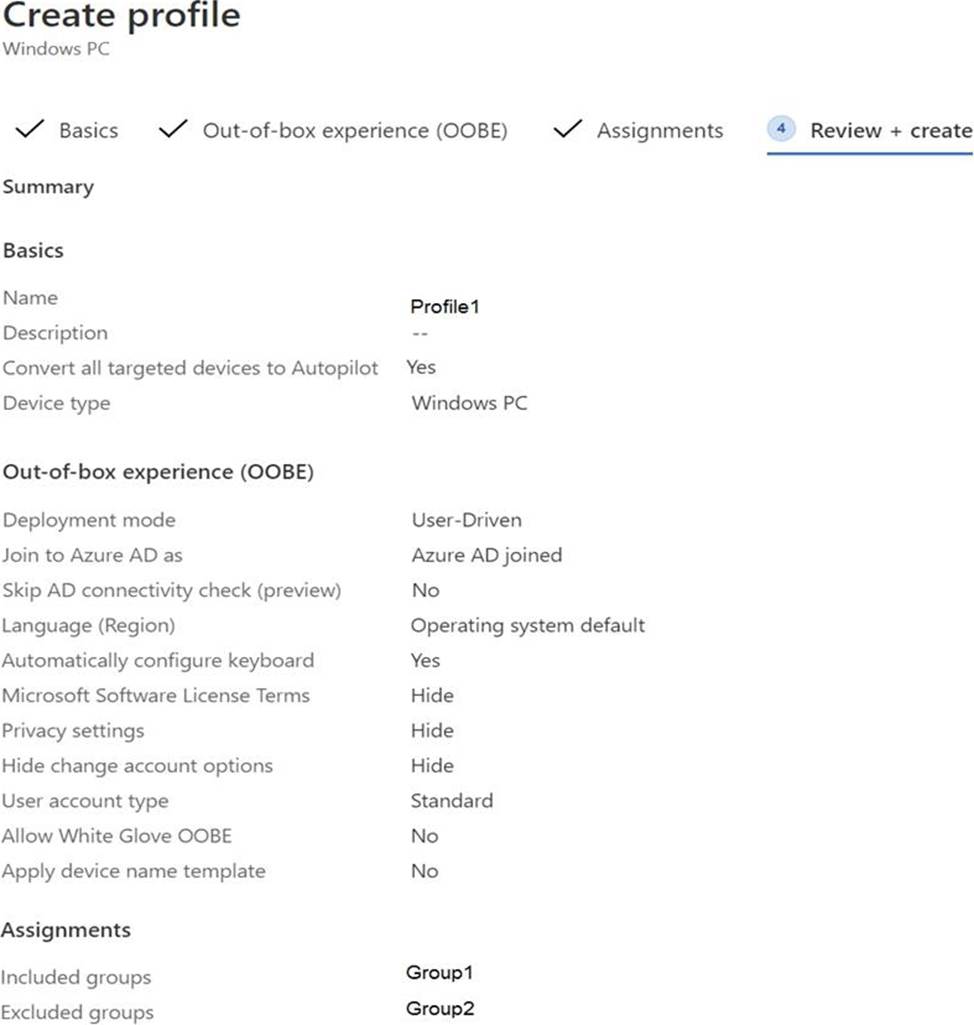
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Contoso plans to implement the following changes:
• Purchase a new Windows 10 device named Device6 and enroll the device in Intune.
• New computers will be deployed by using Windows Autopilot and will be hybrid Azure AO joined.
• Deploy a network boundary configuration profile that will have the following settings:
• Name Boundary 1
• Network boundary 192.168.1.0/24
• Scope tags: Tag 1
• Assignments;
• included groups: Group 1. Group2
• Deploy two VPN configuration profiles named Connection! and Connection that will have the following settings:
• Name: Connection 1
• Connection name: VPNI
• Connection type: L2TP
• Assignments:
• Included groups: Group1. Group2, GroupA
• Excluded groups: ―
• Name: Connection
• Connection name: VPN2
• Connection type: IKEv2 i Assignments:
• included groups: GroupA
• Excluded groups: GroupB
Technical Requirements
Contoso must meet the following technical requirements:
• Users in GroupA must be able to deploy new computers.
• Administrative effort must be minimized.
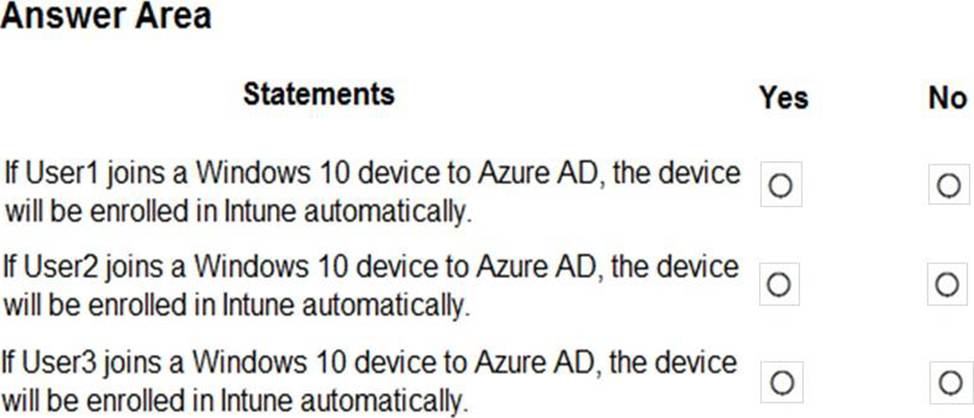
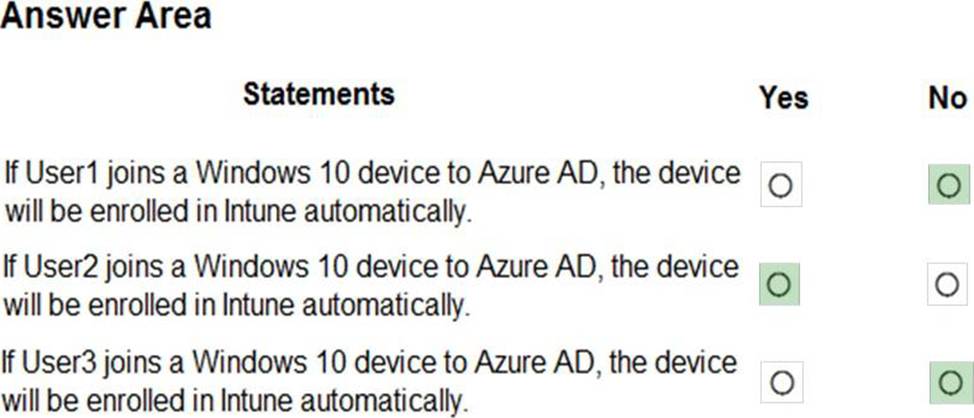
HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
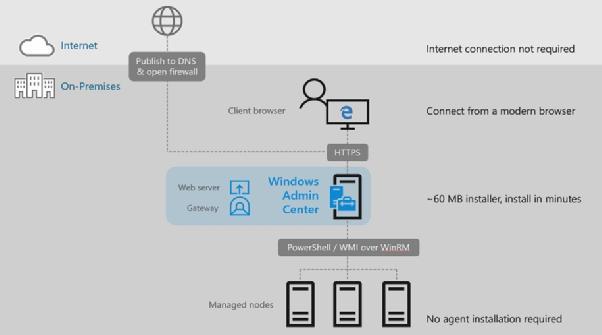
Your network contains an on-premises Active Directory domain. The domain contains two computers named Computer1 and Computer2 that run Windows 10.
You install Windows Admin Center on Computer1.
You need to manage Computer2 from Computer1 by using Windows Admin Center.
What should you do on Computer2?
- A . Update the TrustedHosts list.
- B . Run the Enable-PSRemoting cmdlet.
- C . Allow Windows Remote Management (WinRM) through the Microsoft Defender firewall.
- D . Add an inbound Microsoft Defender Firewall rule.
You have a Microsoft 365 subscription. All devices run Windows 10.
You need to prevent users from enrolling the devices in the Windows Insider Program.
What two configurations should you perform from the Microsoft Intune admin center? Each correct answer is a complete solution. NOTE: Each correct selection is worth one point.
E. a device restrictions device configuration profile
F. an app configuration policy
G. a Windows 10 and later security baseline
H. a custom device configuration profile
I. a Windows 10 and later update ring
You have a Microsoft 365 subscription. All devices run Windows 10.
You need to prevent users from enrolling the devices in the Windows Insider Program.
What two configurations should you perform from the Microsoft Intune admin center? Each correct answer is a complete solution. NOTE: Each correct selection is worth one point.
E. a device restrictions device configuration profile
F. an app configuration policy
G. a Windows 10 and later security baseline
H. a custom device configuration profile
I. a Windows 10 and later update ring