
Microsoft MD-102 Practice Exams
Last updated on Nov 16,2026- Exam Code: MD-102
- Exam Name: Endpoint Administrator
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
HOTSPOT
Your network contains an Active Directory domain. Active Directory is synced with a Microsoft Entra tenant.
There are 500 Active Directory domain-joined computers that run Windows 10 and are enrolled in Microsoft Intune.
You plan to implement Microsoft Defender Exploit Guard.
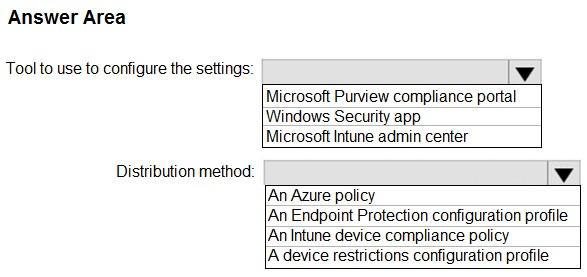
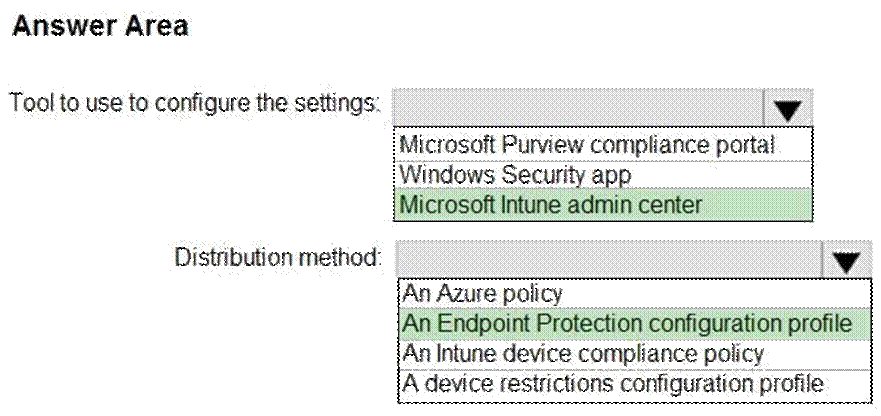
You need to create a custom Microsoft Defender Exploit Guard policy, and then distribute the policy to all the computers.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Hot Area:
HOTSPOT
Your network contains an Active Directory domain. Active Directory is synced with a Microsoft Entra tenant.
There are 500 Active Directory domain-joined computers that run Windows 10 and are enrolled in Microsoft Intune.
You plan to implement Microsoft Defender Exploit Guard.
You need to create a custom Microsoft Defender Exploit Guard policy, and then distribute the policy to all the computers.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Hot Area:
HOTSPOT
Your network contains an Active Directory domain. Active Directory is synced with a Microsoft Entra tenant.
There are 500 Active Directory domain-joined computers that run Windows 10 and are enrolled in Microsoft Intune.
You plan to implement Microsoft Defender Exploit Guard.
You need to create a custom Microsoft Defender Exploit Guard policy, and then distribute the policy to all the computers.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Hot Area:
You have a Microsoft 365 subscription.
You use Microsoft Intune to manage devices.
You plan to deploy two apps named App1 and App2 to all Windows devices. App1 must be installed before App2.
From the Intune admin center, you create and deploy two Windows app (Win32) apps.
You need to ensure that App1 is installed before App2 on every device.
What should you configure?
- A . the App1 deployment configurations
- B . a dynamic device group
- C . the App2 deployment configurations
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has a Microsoft Entra tenant named contoso.com that contains several Windows 10 devices.
When you join new Windows 10 devices to contoso.com, users are prompted to set up a four-digit pin.
You need to ensure that the users are prompted to set up a six-digit pin when they join the Windows 10 devices to contoso.com.
Solution: From the Microsoft Entra admin center, you modify the User settings and the Device settings. Does this meet the goal?
- A . Yes
- B . No
You have a Microsoft 365 tenant that uses Microsoft Intune.
You use the Company Portal app to access and install published apps to enrolled devices. From the Microsoft Intune admin center, you add a Microsoft Store app.
Which two App information types are visible in the Company Portal? NOTE: Each correct selection is worth one point.
E. Privacy URL
F. Information URL
G. Developer
H. Owner
HOTSPOT
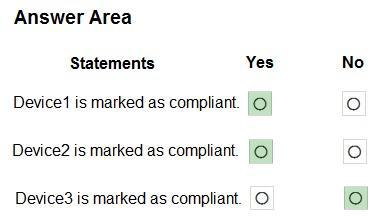
You have devices that are not rooted enrolled in Microsoft Intune as shown in the following table.
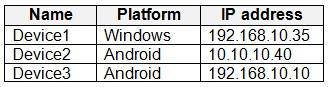
The devices are members of a group named Group1.
In Intune, you create a device compliance location that has the following configurations:
Name: Network1

IPv4 range: 192.168.0.0/16
In Intune, you create a device compliance policy for the Android platform. The policy has the following configurations:
Name: Policy1
Device health: Rooted devices: Block
Locations: Location: Network1
Mark device noncompliant: Immediately
Assigned: Group1
The Intune device compliance policy has the following configurations:
Mark devices with no compliance policy assigned as: Compliant
Enhanced jailbreak detection: Enabled
Compliance status validity period (days): 20
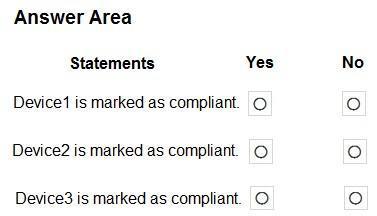
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Hot Area:
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Intune to manage devices.
You need to review details about device wipes initiated through Intune.
Which report should you review?
E. Noncompliant devices
F. Assignment status
G. Windows health attestation report
H. Device actions
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Intune to manage devices.
You need to review details about device wipes initiated through Intune.
Which report should you review?
E. Noncompliant devices
F. Assignment status
G. Windows health attestation report
H. Device actions
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Intune to manage devices.
You need to review details about device wipes initiated through Intune.
Which report should you review?
E. Noncompliant devices
F. Assignment status
G. Windows health attestation report
H. Device actions