Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
HOTSPOT
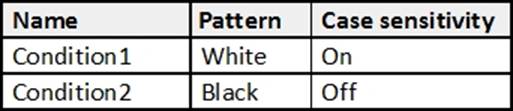
You have the Azure Information Protection conditions shown in the following table.
You have the Azure Information Protection policies as shown in the following table.
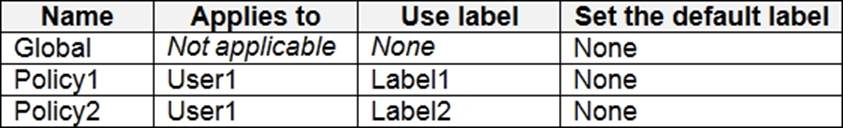
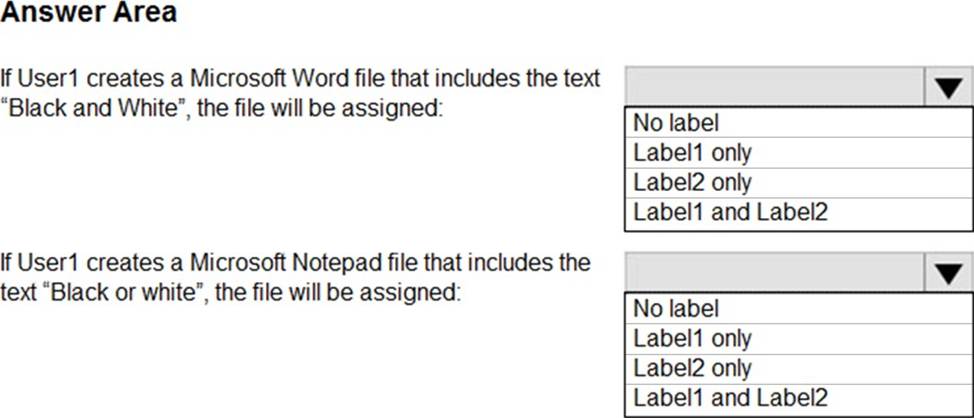
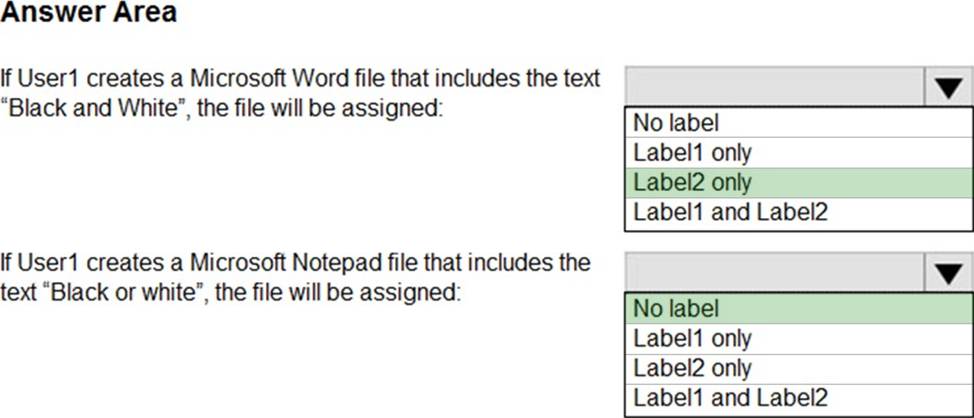
You need to identify how Azure Information Protection will label files.
What should you identify? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1.
You need to ensure that User1 can create and manage administrative units. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A . Privileged role administrator
- B . Helpdesk administrator
- C . Global administrator
- D . Security administrator
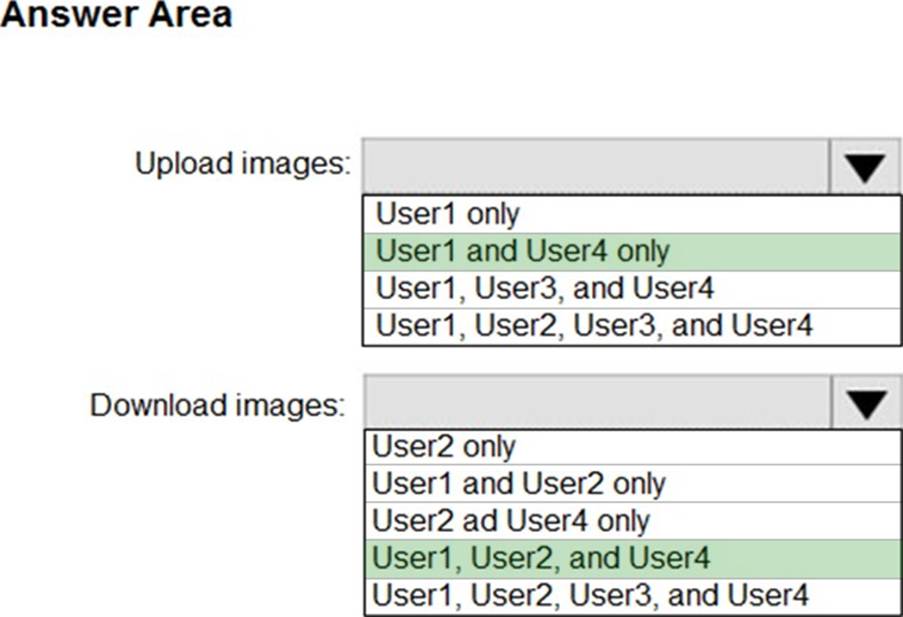
HOTSPOT
You have an Azure Container Registry named Registry1.
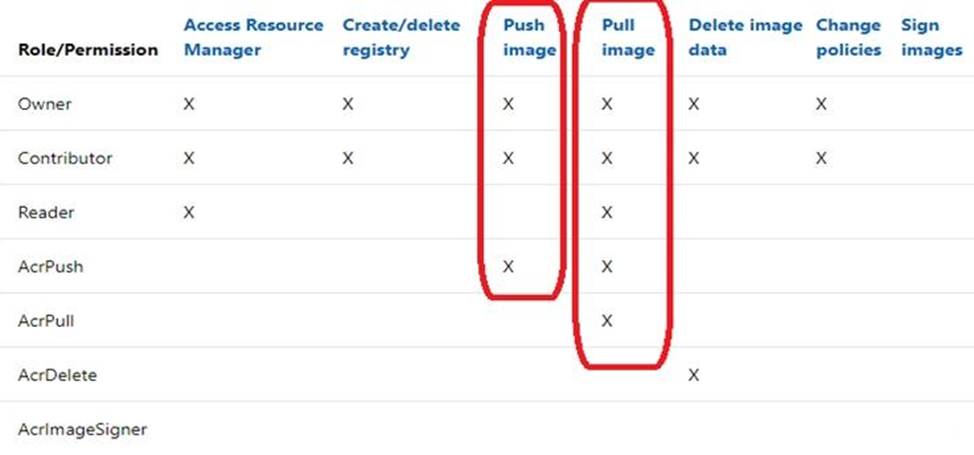
You add role assignment for Registry1 as shown in the following table.
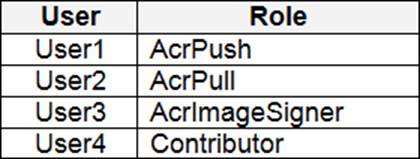
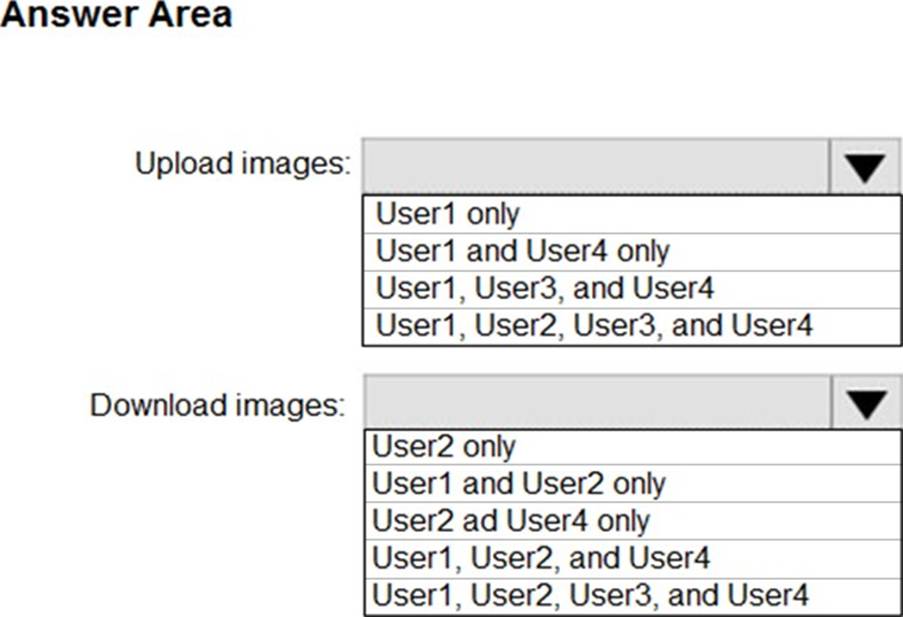
Which users can upload images to Registry1 and download images from Registry1? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
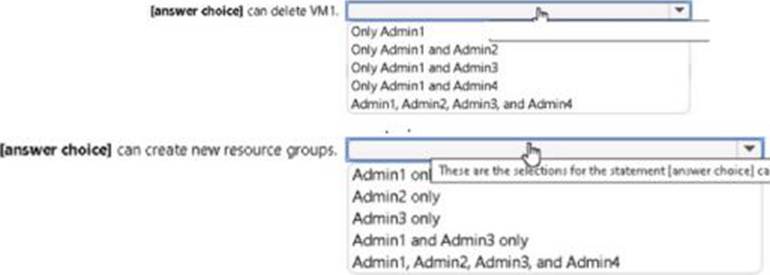
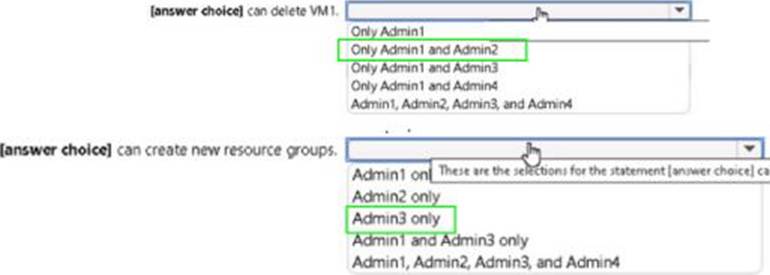
You have the role assignments shown in the following exhibit.
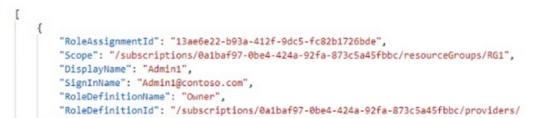
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.
You have an Azure subscription.
You plan to map an online infrastructure and perform vulnerability scanning for the following:
• ASNs
• Hostnames
• IP addresses
• SSL certificates What should you use?
- A . Microsoft Defender for Cloud
- B . Microsoft Defender for Identity
- C . Microsoft Defender for Endpoint
- D . Microsoft Defender External Attack Surface Management (Defender EASM)
DRAG DROP
You have five Azure subscriptions linked to a single Azure Active Directory (Azure AD) tenant.
You create an Azure Policy initiative named SecurityPolicyInitiative1.
You identify which standard role assignments must be configured on all new resource groups.
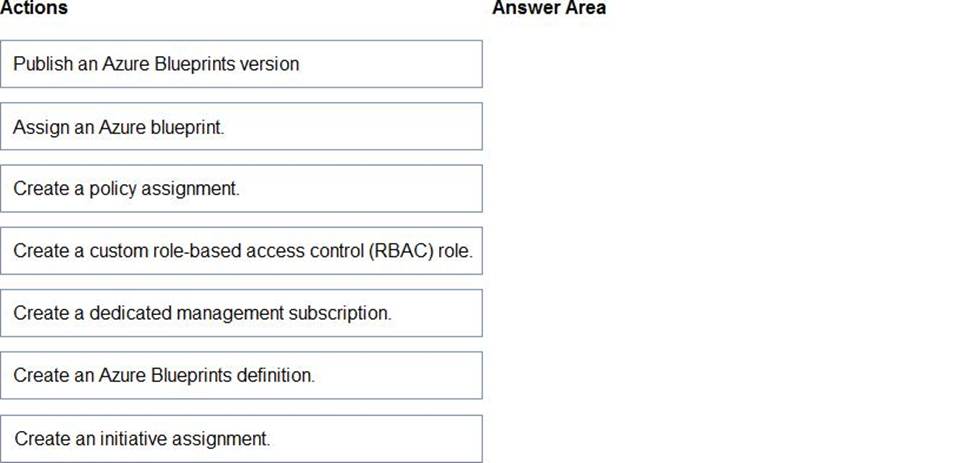
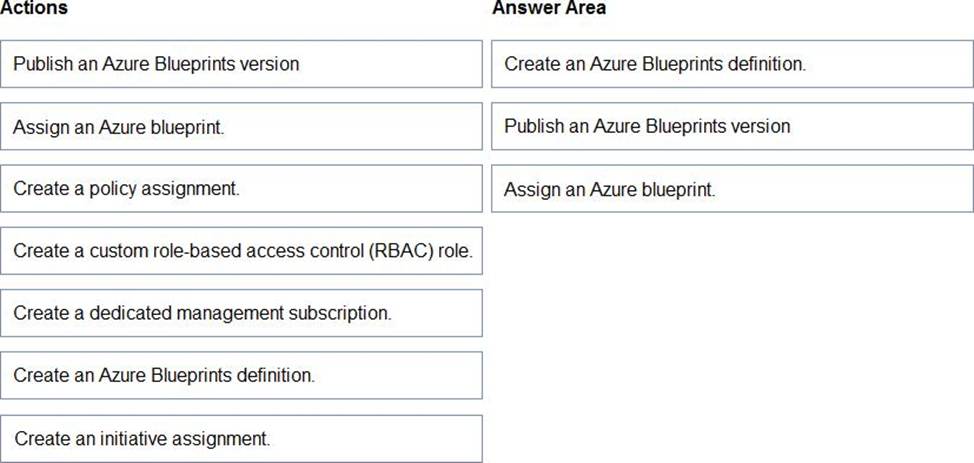
You need to enforce SecurityPolicyInitiative1 and the role assignments when a new resource group is created.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Subscription named Sub1.
You have an Azure Storage account named Sa1 in a resource group named RG1.
Users and applications access the blob service and the file service in Sa1 by using several shared access signatures (SASs) and stored access policies.
You discover that unauthorized users accessed both the file service and the blob service.
You need to revoke all access to Sa1.
Solution: You create a new stored access policy.
Does this meet the goal?
- A . Yes
- B . No
HOTSPOT
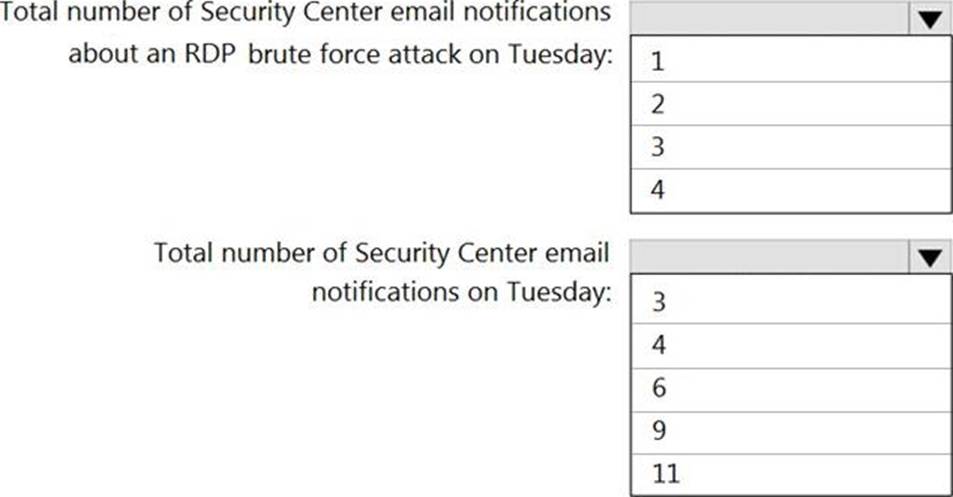
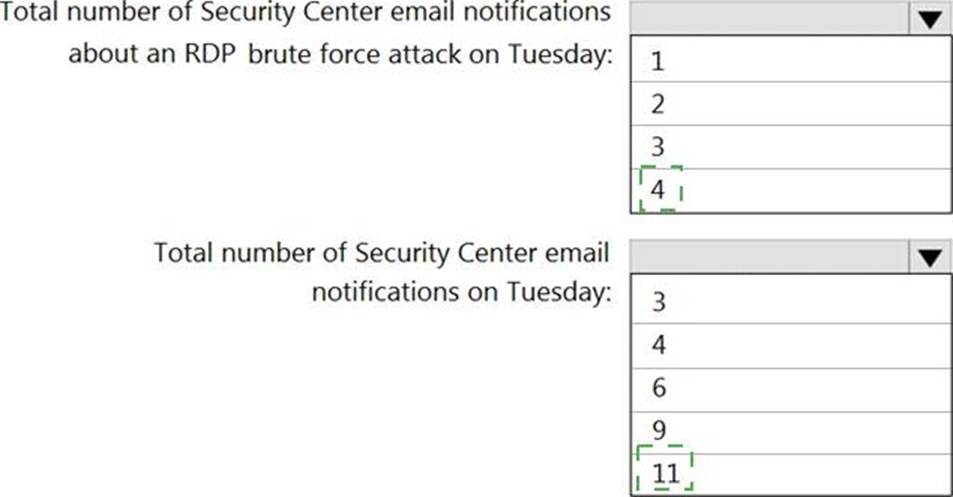
On Monday, you configure an email notification in Azure Security Center to notify user [email protected].
On Tuesday, Security Center generates the security alerts shown in the following table.
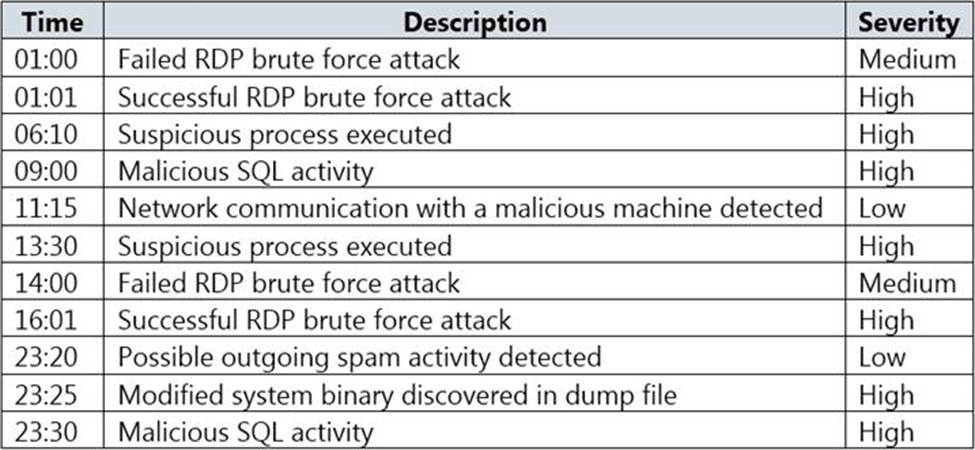
How many email notifications will [email protected] receive on Tuesday? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains a storage account and an Azure web app named App1.
App1 connects to an Azure Cosmos DB database named Cosmos1 that uses a private endpoint named Endpoint1. Endpoint1 has the default settings.
You need to validate the name resolution to Cosmos1.
Which DNS zone should you use?
- A . Endpoint1. Privatelink,blob,core,windows,net
- B . Endpoint1. Privatelink,database,azure,com
- C . Endpoint1. Privatelink,azurewebsites,net
- D . Endpoint1. Privatelink,documents,azure,com
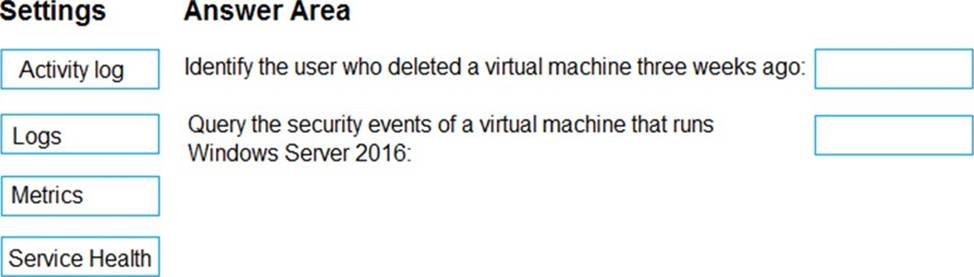
DRAG DROP
You have an Azure subscription that contains 100 virtual machines. Azure Diagnostics is enabled on all the virtual machines.
You are planning the monitoring of Azure services in the subscription.
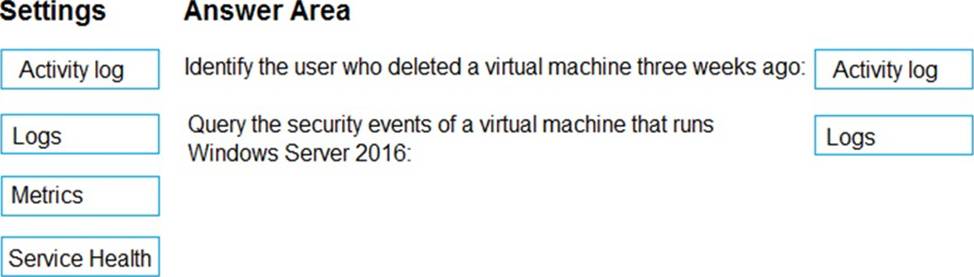
You need to retrieve the following details:
– Identify the user who deleted a virtual machine three weeks ago.
– Query the security events of a virtual machine that runs Windows Server 2016.
What should you use in Azure Monitor? To answer, drag the appropriate configuration settings to the correct details. Each configuration setting may be used once, more than once, or not at all.
You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.