
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
You have an Azure Active Directory (Azure AD) tenant.
You have the deleted objects shown in the following table.
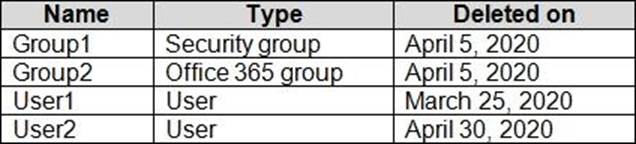
On May 4, 2020, you attempt to restore the deleted objects by using the Azure Active Directory admin center.
Which two objects can you restore? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A . Group1
- B . Group2
- C . User2
- D . User1
You have an Azure subscription named Subscription1 that contains a resource group named RG1 and the users shown in the following table.
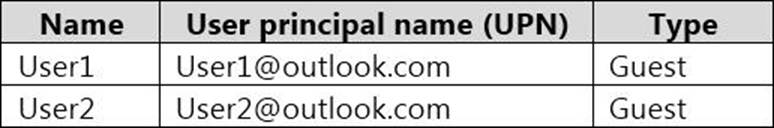
You perform the following tasks:
– Assign User1 the Network Contributor role for Subscription1.
– Assign User2 the Contributor role for RG1.
To Subscription1 and RG1, you assign the following policy definition: External accounts with write permissions should be removed from your subscription.
What is the Compliance State of the policy assignments?
- A . The Compliance State of both policy assignments is Non-compliant.
- B . The Compliance State of the policy assignment to Subscription1 is Compliant, and the Compliance State of the policy assignment to RG1 is Non-compliant.
- C . The Compliance State of the policy assignment to Subscription1 is Non-compliant, and the Compliance State of the policy assignment to RG1 is Compliant.
- D . The Compliance State of both policy assignments is Compliant.
HOTSPOT
You have an Azure subscription that contains the resources shown in the following table.
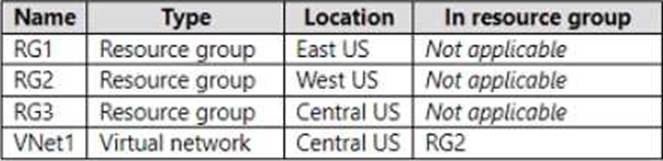
VNet1 contains the subnets shown in the following table.
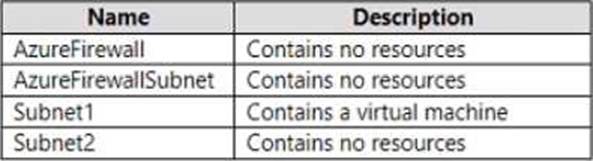
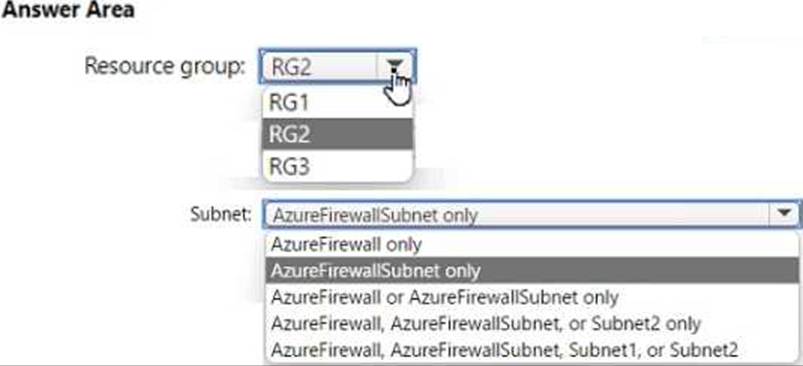
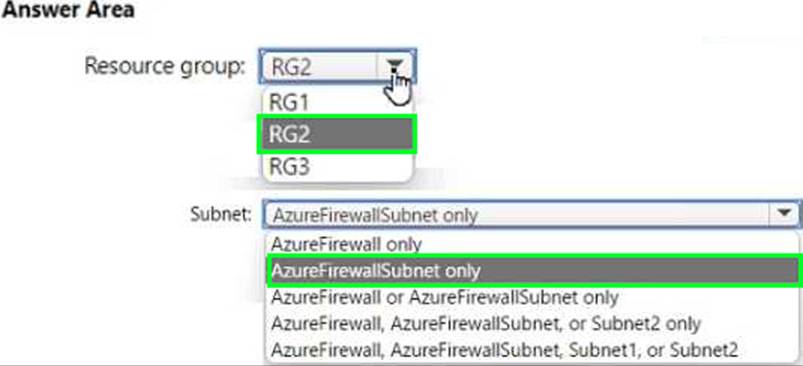
You plan to use the Azure portal to deploy an Azure firewall named AzFW1 to VNet1.
Which resource group and subnet can you use to deploy AzFW1? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains an Azure SQL database named sql1.
You plan to audit sql1.
You need to configure the audit log destination. The solution must meet the following requirements:
Support querying events by using the Kusto query language.
Minimize administrative effort.
What should you configure?
- A . an event hub
- B . a storage account
- C . a Log Analytics workspace
SIMULATION
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password
below.
Azure Username: User1 [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 8
You need to prevent HTTP connections to the rg1lod28681041n1 Azure Storage account.
SIMULATION
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password
below.
Azure Username: User1 [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 8
You need to prevent HTTP connections to the rg1lod28681041n1 Azure Storage account.
DRAG DROP
You have an Azure subscription.
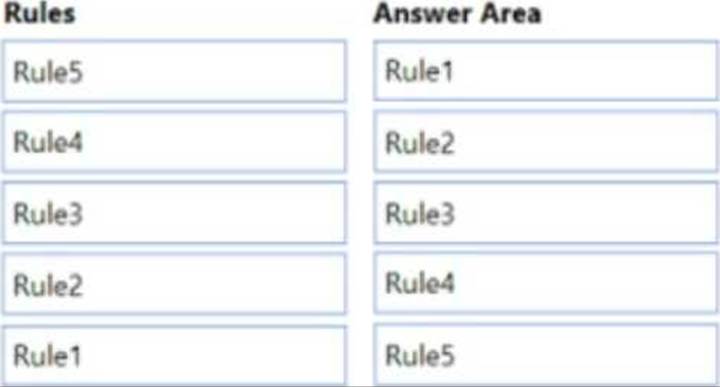
You create an Azure Firewall policy that has the rules shown in the following table:
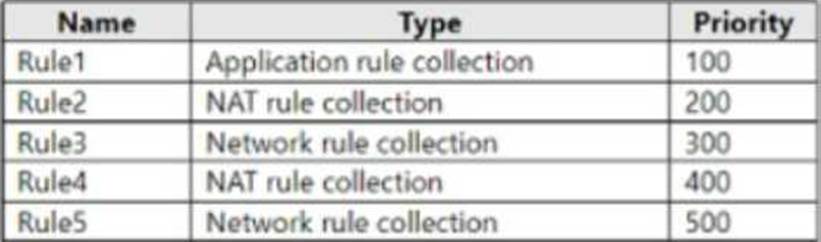
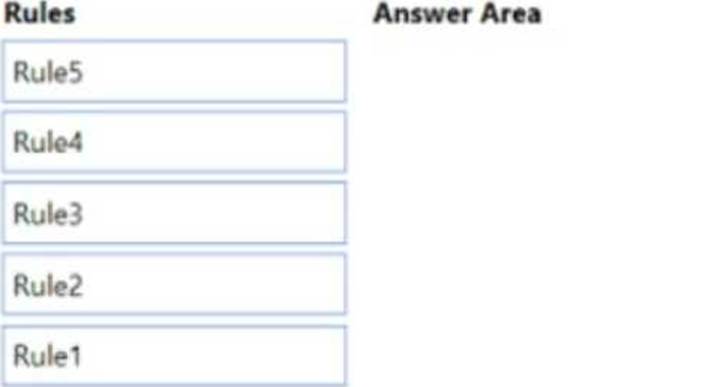
In which order should the rules be processed? To answer, move all rules from the list of rules to the answer area and arrange them in the correct order.
DRAG DROP
You have an Azure subscription that contains the following resources:
✑ A network virtual appliance (NVA) that runs non-Microsoft firewall software and routes all outbound traffic from the virtual machines to the internet
✑ An Azure function that contains a script to manage the firewall rules of the NVA
✑ Azure Security Center standard tier enabled for all virtual machines
✑ An Azure Sentinel workspace
✑ 30 virtual machines
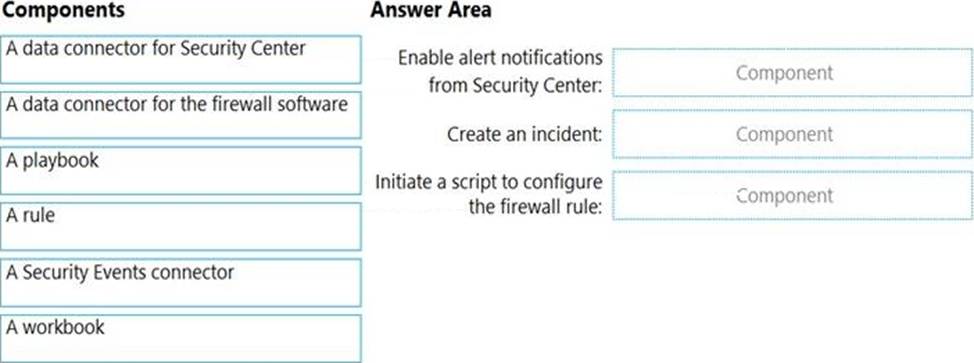
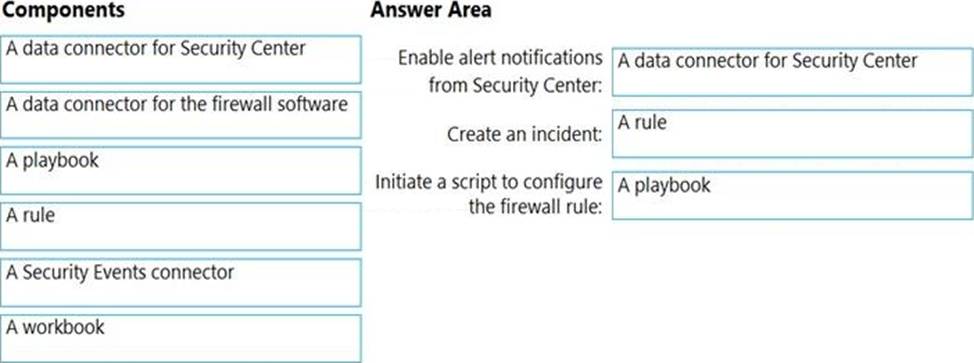
You need to ensure that when a high-priority alert is generated in Security Center for a virtual machine, an incident is created in Azure Sentinel and then a script is initiated to configure a firewall rule for the NVA.
How should you configure Azure Sentinel to meet the requirements? To answer, drag the appropriate components to the correct requirements. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.
You have an Azure AD tenant that contains 500 users and an administrative unit named AU1.
From the Azure Active Directory admin center, you plan to add the users to AU1 by using Bulk add members.
You need to create and upload a file for the bulk add.
What should you include in the file?
- A . only the display name of each user
- B . only the user principal name (UPN) of each user
- C . only the object identifier of each user
- D . only the user principal name (UPN) and object identifier of each user
- E . Only the user principal name (UPN) and display name of each user
You company has an Azure Active Directory (Azure AD) tenant named contoso.com.
You plan to create several security alerts by using Azure Monitor.
You need to prepare the Azure subscription for the alerts.
What should you create first?
- A . An Azure Storage account
- B . an Azure Log Analytics workspace
- C . an Azure event hub
- D . an Azure Automation account