
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You use Azure Security Center for the centralized policy management of three Azure subscriptions.
You use several policy definitions to manage the security of the subscriptions.
You need to deploy the policy definitions as a group to all three subscriptions.
Solution: You create an initiative and an assignment that is scoped to the Tenant Root Group management group.
Does this meet the goal?
- A . Yes
- B . No
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You use Azure Security Center for the centralized policy management of three Azure subscriptions.
You use several policy definitions to manage the security of the subscriptions.
You need to deploy the policy definitions as a group to all three subscriptions.
Solution: You create an initiative and an assignment that is scoped to the Tenant Root Group management group.
Does this meet the goal?
- A . Yes
- B . No
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription named Sub1.
You have an Azure Storage account named Sa1 in a resource group named RG1.
Users and applications access the blob service and the file service in Sa1 by using several shared access signatures (SASs) and stored access policies.
You discover that unauthorized users accessed both the file service and the blob service.
You need to revoke all access to Sa1.
Solution: You create a lock on Sa1.
Does this meet the goal?
- A . Yes
- B . No
HOTSPOT
You have an Azure Active Directory (Azure AD) tenant that contains the resources shown in the following table.
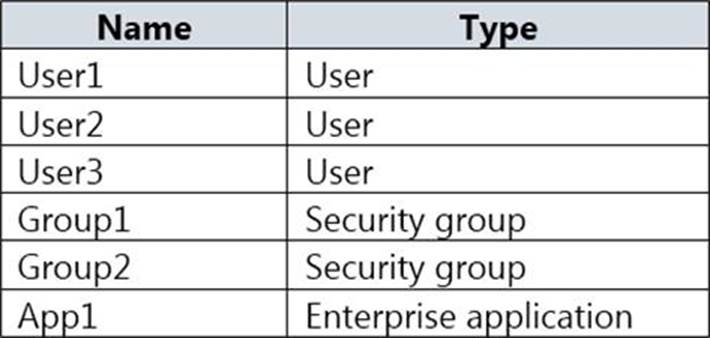
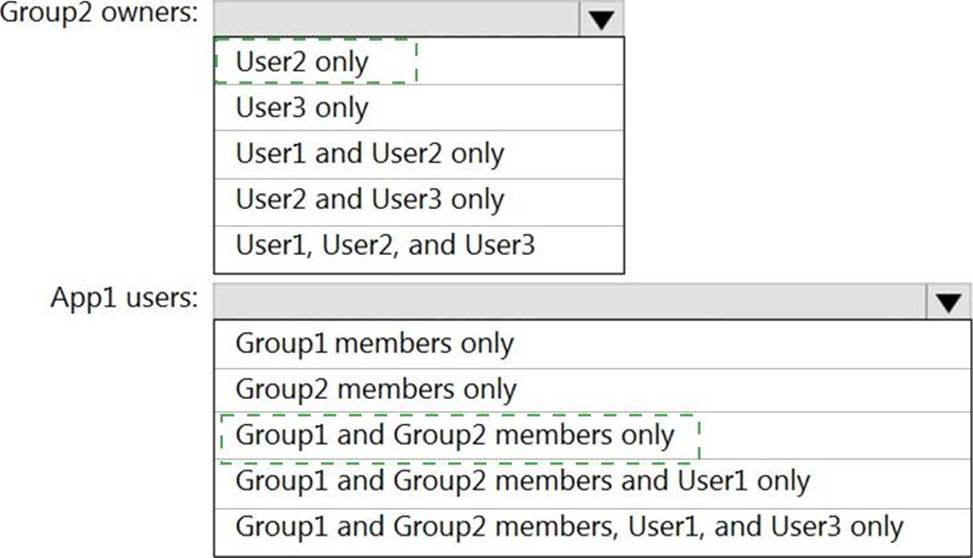
User2 is the owner of Group2.
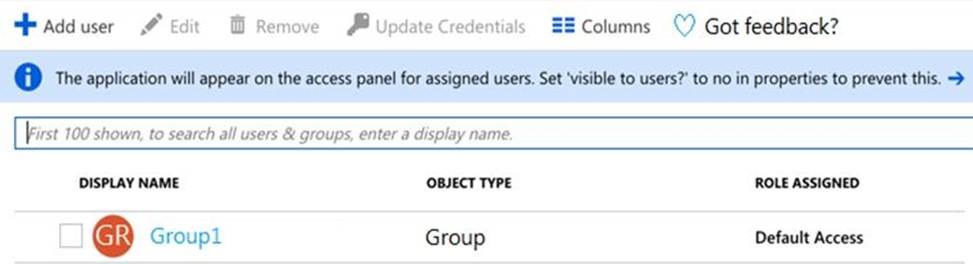
The user and group settings for App1 are configured as shown in the following exhibit.
You enable self-service application access for App1 as shown in the following exhibit.
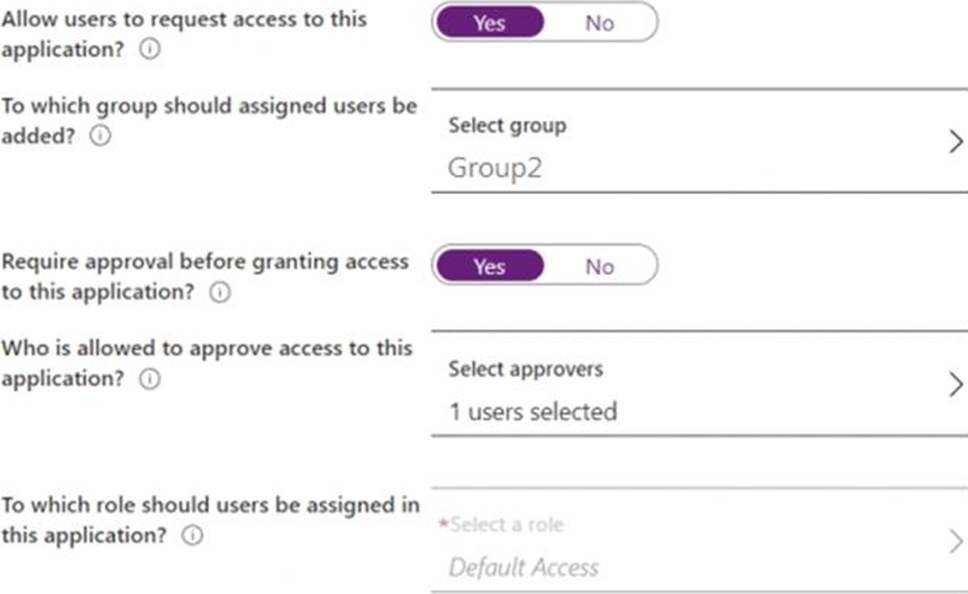
User3 is configured to approve access to Appl.
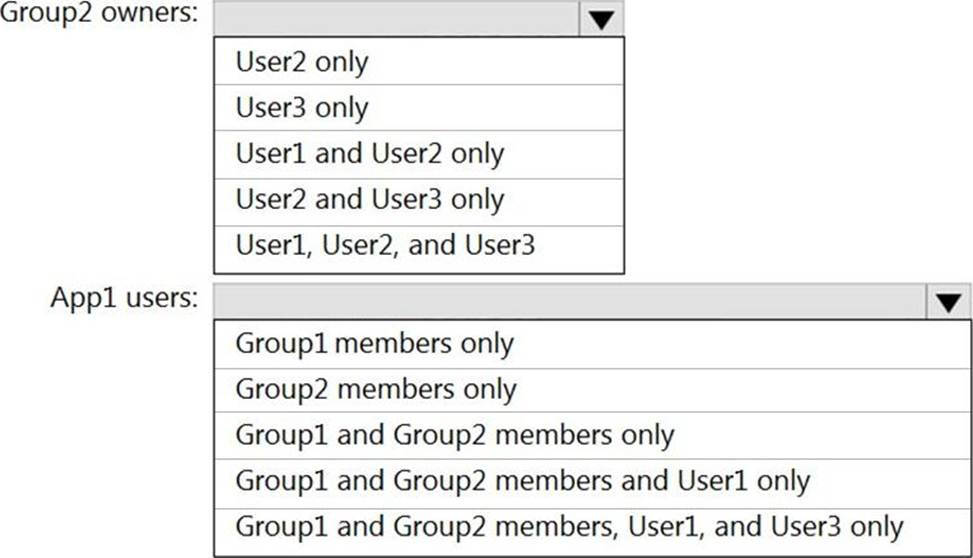
You need to identify the owners of Group2 and the users of Appl.
What should you identify? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains an Azure key vault.
You need to configure maximum number of days for Which new keys are valid. The solution must minimize administrative effort.
What should you use?
- A . Key Vault properties
- B . Azure Policy
- C . Azure Purview
- D . Azure Blueprints
You have a hybrid configuration of Azure Active Directory (Azure AD). You have an Azure SQL Database instance that is configured to support Azure AD authentication.
Database developers must connect to the database instance and authenticate by using their on-premises
Active Directory account.
You need to ensure that developers can connect to the instance by using Microsoft SQL Server Management
Studio. The solution must minimize authentication prompts.
Which authentication method should you recommend?
- A . Active Directory – Password
- B . Active Directory – Universal with MFA support
- C . SQL Server Authentication
- D . Active Directory – Integrated
Your company recently created an Azure subscription.
You have been tasked with making sure that a specified user is able to implement Azure AD Privileged Identity Management (PIM).
Which of the following is the role you should assign to the user?
- A . The Global administrator role.
- B . The Security administrator role.
- C . The Password administrator role.
- D . The Compliance administrator role.
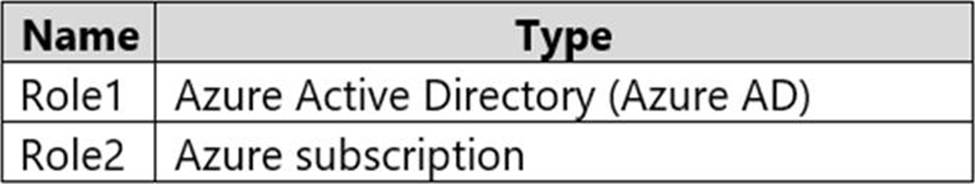
HOTSPOT
You have an Azure subscription that contains the custom roles shown in the following table.
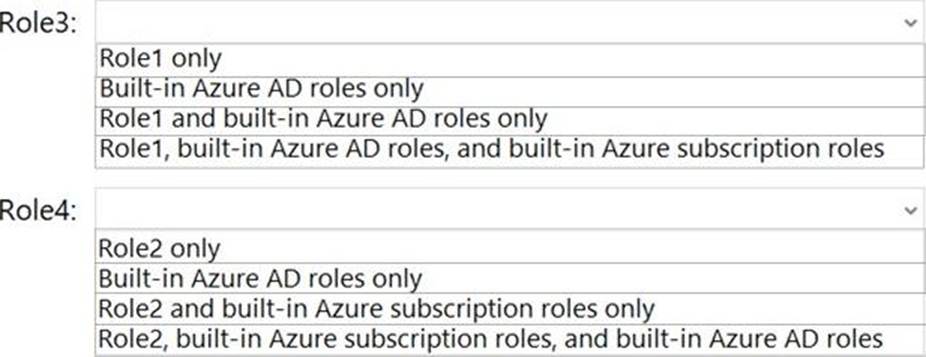
In the Azure portal, you plan to create new custom roles by cloning existing roles.
The new roles will be configured as shown in the following table.
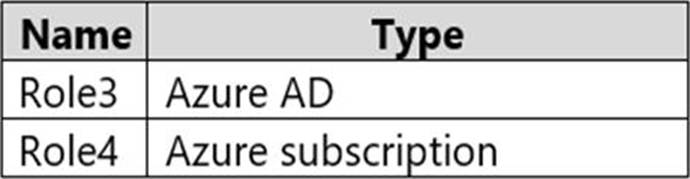
Which roles can you clone to create each new role? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains the virtual machines shown in the following table.
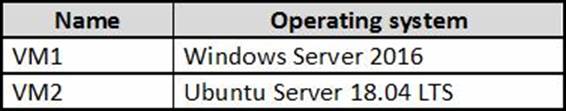
From Azure Security Center, you turn on Auto Provisioning.
You deploy the virtual machines shown in the following table.
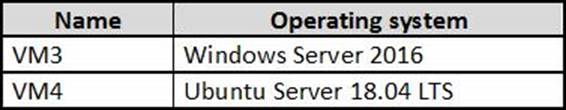
On which virtual machines is the Log Analytics agent installed?
- A . VM3 only
- B . VM1 and VM3 only
- C . VM3 and VM4 only
- D . VM1, VM2, VM3, and VM4
You have an Azure Active Directory (Azure AD) tenant. The tenant contains users that are assigned Azure AD Premium Plan 2 licenses.
You have an partner company that has a domain named The fabrikam.com domain contains a user named user’. User’ has an email address of [email protected].
You to provide User1 with to the resources in the tenant.
The solution must meet the following requirements:
– user1 must be able to sign in by using the [email protected] credentials
– You must be able to grant User1 access to the resources in the tenant
– Administrative effort must be minimized.
What should you do?
- A . Create a user account for user1.
- B . Create an invite for User1.
- C . To the tenant add fabrikamcom as a custom domain
- D . Set Enable guest self-service sign up via user flows to Yes for the tenant.