
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
HOTSPOT
You have a network security group (NSG) bound to an Azure subnet.
You run Get-AzureRmNetworkSecurityRuleConfig and receive the output shown in the following exhibit.
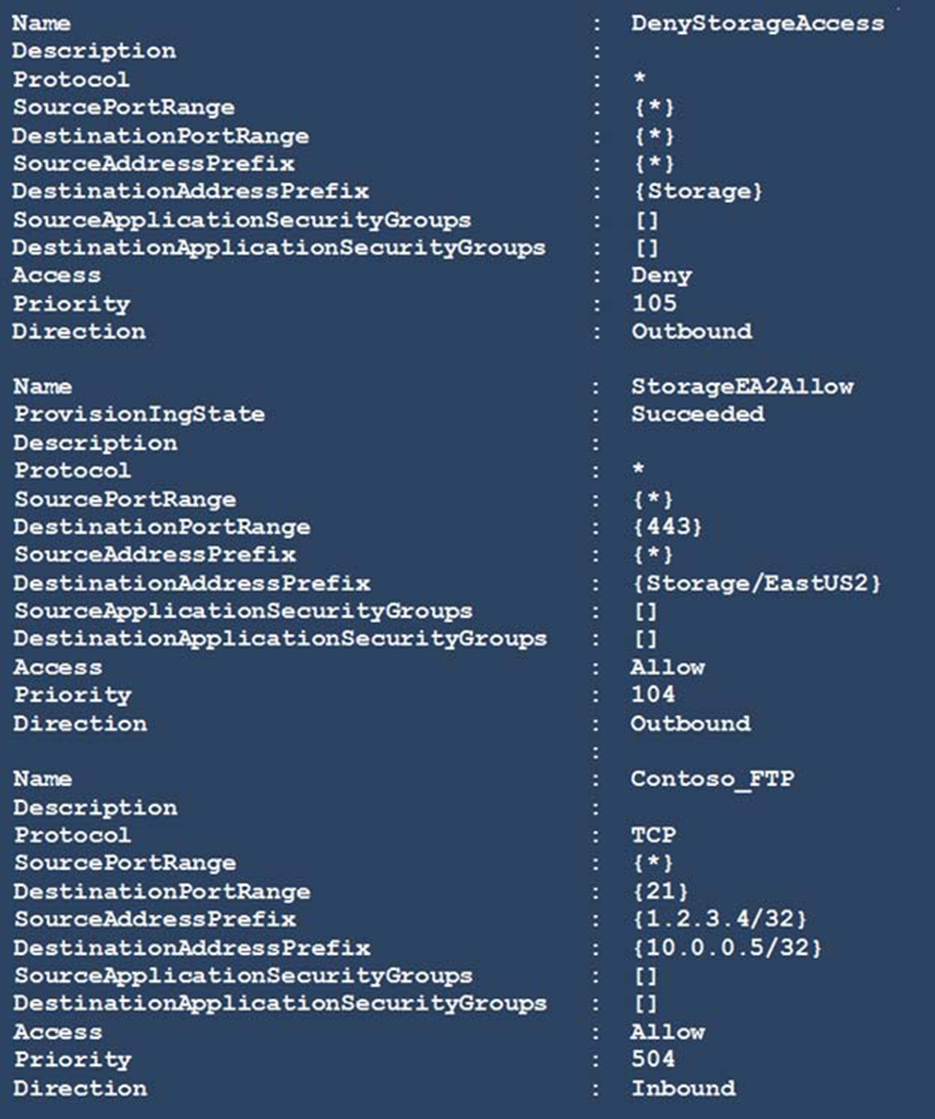
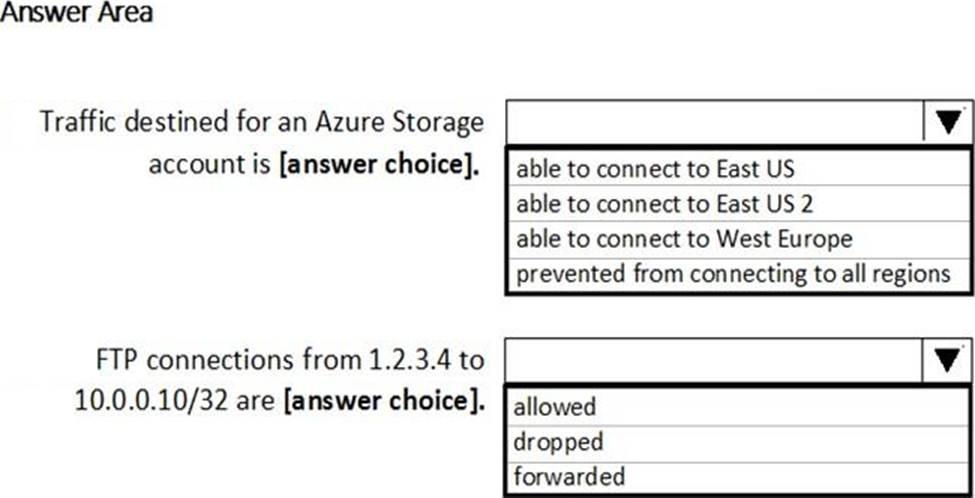
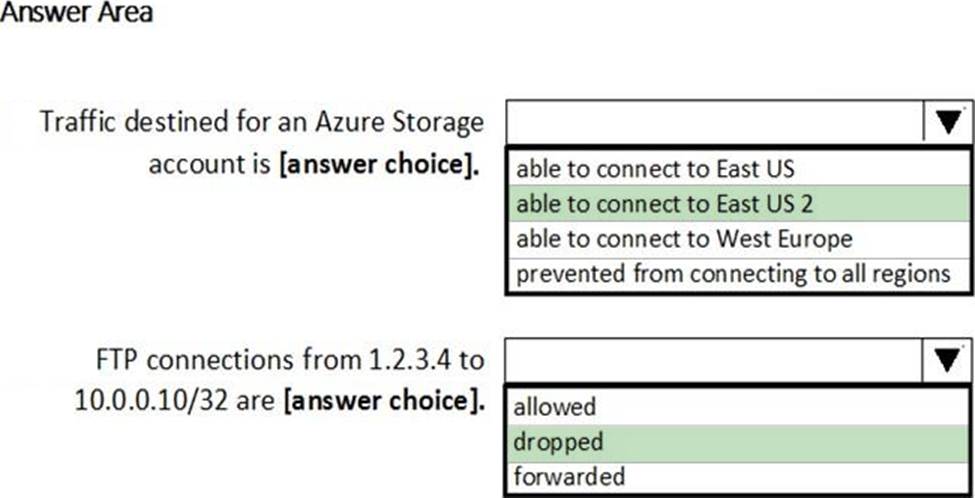
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains the resources shown in the following table.
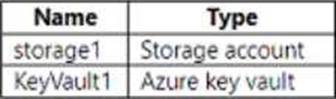
You need to configure storage1 to regenerate keys automatically every 90 days.
Which cmdlet should you run?
- A . set -A=StorageAccount
- B . Add-A:StorogcAccountmanagementPolicyAction
- C . Set-A;StorageAccountimanagementPolicy
- D . Add-AsKeyVaultmanageStorageAccount
You have Azure Resource Manager templates that you use to deploy Azure virtual machines.
You need to disable unused Windows features automatically as instances of the virtual machines are provisioned.
What should you use?
- A . security policies in Azure Security Center
- B . Azure Logic Apps
- C . an Azure Desired State Configuration (DSC) virtual machine extension
- D . Azure Advisor
HOTSPOT
You have an Azure subscription named Sub1.
Sub1 has an Azure Storage account named Storage1 that contains the resources shown in the following table.
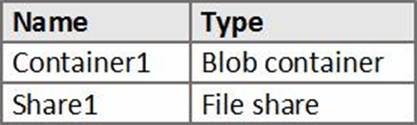
You generate a shared access signature (SAS) to connect to the blob service and the file service.
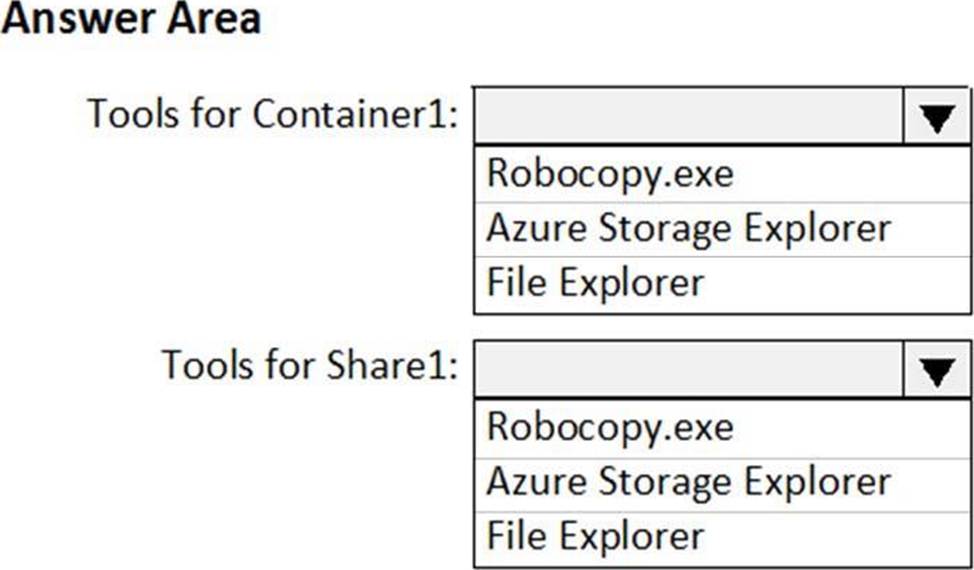
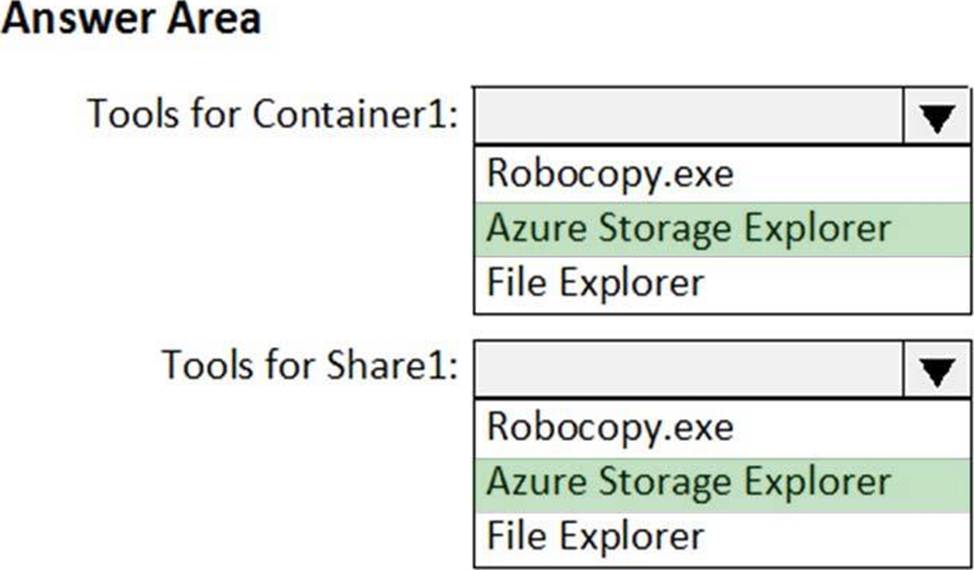
Which tool can you use to access the contents in Container1 and Share! by using the SAS? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure Kubernetes Service (AKS) cluster that will connect to an Azure Container Registry.
You need to use the automatically generated service principal for the AKS cluster to authenticate to the Azure Container Registry.
What should you create?
- A . an Azure AD user
- B . a secret in Azure Key Vault
- C . an Azure AD group
- D . a role assignment
HOTSPOT
You have an Azure subscription that contains the virtual networks shown in the following table.
The subscription contains the virtual machines shown in the following table.
You have a storage account named contoso2024 that contains the following resources:
• A container named Contained that contains a file named File1
• A file share named Share1 that contains a file named File2
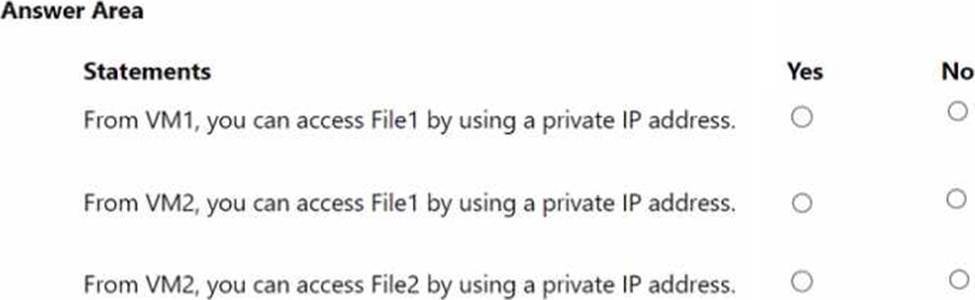
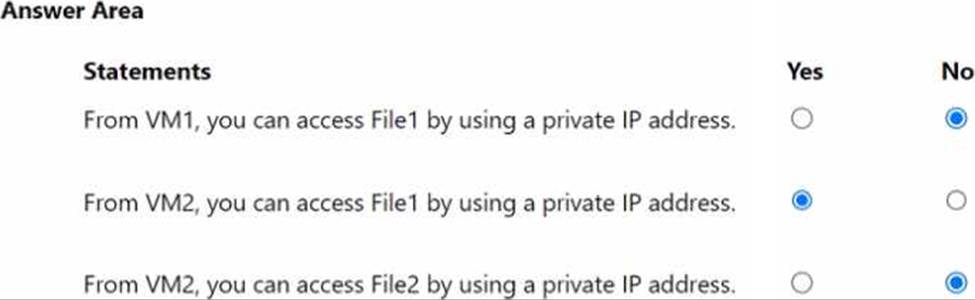
You create a private endpoint for contoso2024 as shown in the following exhibit.
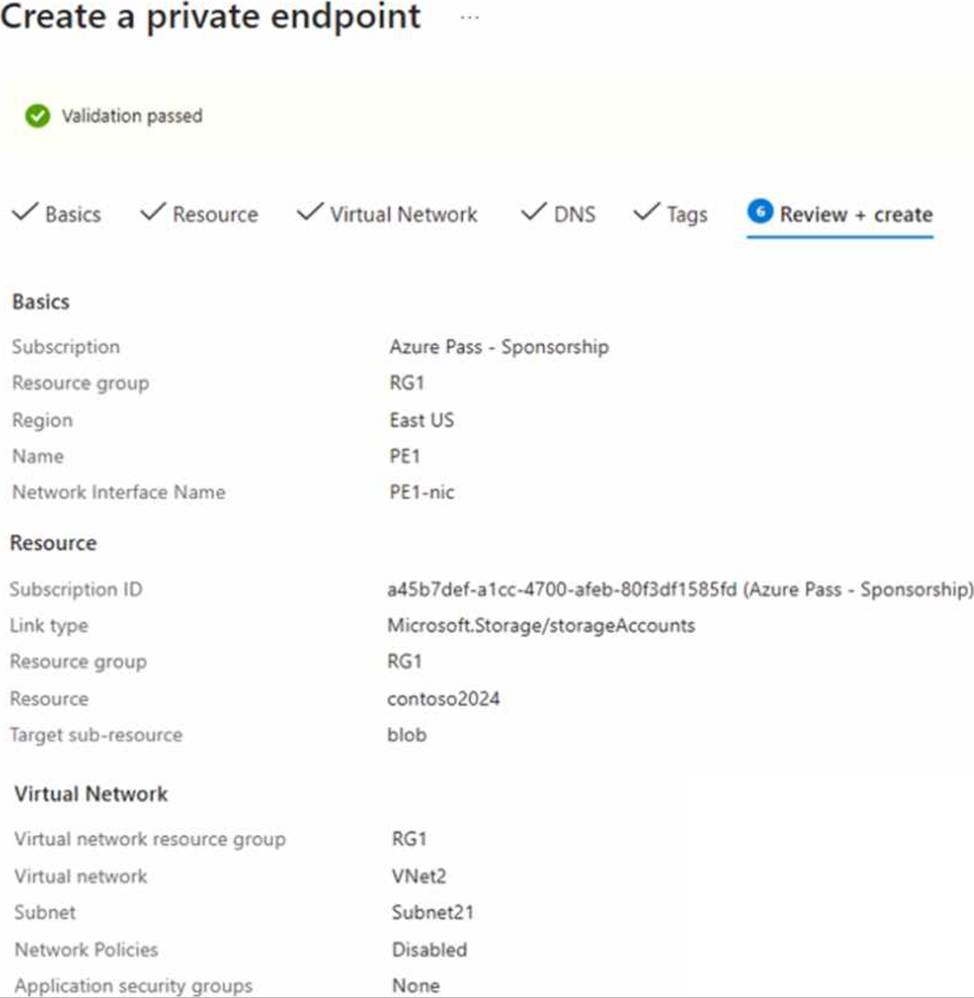
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
HOTSPOT
You have an Azure subscription that contains the virtual networks shown in the following table.
The subscription contains the virtual machines shown in the following table.
You have a storage account named contoso2024 that contains the following resources:
• A container named Contained that contains a file named File1
• A file share named Share1 that contains a file named File2
You create a private endpoint for contoso2024 as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
HOTSPOT
You have an Azure subscription that contains the virtual networks shown in the following table.
The subscription contains the virtual machines shown in the following table.
You have a storage account named contoso2024 that contains the following resources:
• A container named Contained that contains a file named File1
• A file share named Share1 that contains a file named File2
You create a private endpoint for contoso2024 as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
You have an Azure environment.
You need to identify any Azure configurations and workloads that are non-compliant with ISO 27001:2013 standards.
What should you use?
- A . Azure Active Directory (Azure AD) Identity Protection
- B . Microsoft Defender for Cloud
- C . Microsoft Defender for Identity
- D . Microsoft Sentinel
You create a new Azure subscription.
You need to ensure that you can create custom alert rules in Azure Security Center.
Which two actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . Onboard Azure Active Directory (Azure AD) Identity Protection.
- B . Create an Azure Storage account.
- C . Implement Azure Advisor recommendations.
- D . Create an Azure Log Analytics workspace.
- E . Upgrade the pricing tier of Security Center to Standard.