
Juniper JN0-231 Practice Exams
Last updated on Oct 22,2026- Exam Code: JN0-231
- Exam Name: Security - Associate (JNCIA-SEC)
- Certification Provider: Juniper
- Latest update: Oct 22,2026
Click the Exhibit button.
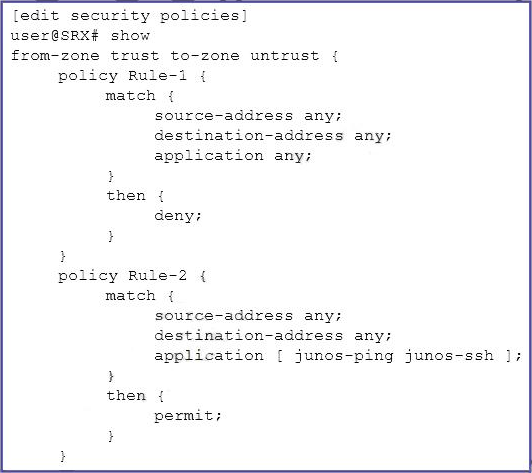
You are asked to allow only ping and SSH access to the security policies shown in the exhibit.
Which statement will accomplish this task?
- A . Rename policy Rule-2 to policy Rule-0.
- B . Insert policy Rule-2 before policy Rule-1.
- C . Replace application any with application [junos-ping junos-ssh] in policy Rule-1.
- D . Rename policy Rule-1 to policy Rule-3.
You are asked to configure your SRX Series device to block all traffic from certain countries. The solution must be automatically updated as IP prefixes become allocated to those certain countries.
Which Juniper ATP solution will accomplish this task?
- A . Geo IP
- B . unified security policies
- C . IDP
- D . C&C feed
Which Juniper ATP feed provides a dynamic list of known botnet servers and known sources of malware downloads?
- A . infected host cloud feed
- B . Geo IP feed
- C . C&C cloud feed
- D . blocklist feed
Which two services does Juniper Connected Security provide? (Choose two.)
- A . protection against zero-day threats
- B . IPsec VPNs
- C . Layer 2 VPN tunnels
- D . inline malware blocking
What is an IP addressing requirement for an IPsec VPN using main mode?
- A . One peer must have dynamic IP addressing.
- B . One peer must have static IP addressing.
- C . Both peers must have dynamic IP addresses.
- D . Both peers must have static IP addressing.
Unified threat management (UTM) inspects traffic from which three protocols? (Choose three.)
- A . FTP
- B . SMTP
- C . SNMP
- D . HTTP
- E . SSH
What information does the show chassis routing-engine command provide?
- A . chassis serial number
- B . resource utilization
- C . system version
- D . routing tables
You have an FTP server and a webserver on the inside of your network that you want to make available to users outside of the network. You are allocated a single public IP address.
In this scenario, which two NAT elements should you configure? (Choose two.)
- A . destination NAT
- B . NAT pool
- C . source NAT
- D . static NAT
Which statement is correct about packet mode processing?
- A . Packet mode enables session-based processing of incoming packets.
- B . Packet mode works with NAT, VPNs, UTM, IDP, and other advanced security services.
- C . Packet mode bypasses the flow module.
- D . Packet mode is the basis for stateful processing.
What is the default value of the dead peer detection (DPD) interval for an IPsec VPN tunnel?
- A . 20 seconds
- B . 5 seconds
- C . 10 seconds
- D . 40 seconds
B
Explanation:
The default value of the dead peer detection (DPD) interval for an IPsec VPN tunnel is 5 seconds. DPD is a mechanism that enables the IPsec device to detect if the peer is still reachable or if the IPsec VPN tunnel is still active. The DPD interval determines how often the IPsec device sends DPD packets to the peer to check the status of the VPN tunnel. A value of 5 seconds is a common default, but the specific value can vary depending on the IPsec device and its configuration.
Reference:
Juniper Networks Technical Documentation: Configuring IPsec VPNs: https://www.juniper.net/documentation/en_US/junos/topics/task/configuration/ipsec-vpn-overview-srx-series.html