
HP HPE7-A02 Practice Exams
Last updated on Oct 23,2026- Exam Code: HPE7-A02
- Exam Name: HPE Network Security Professional Exam
- Certification Provider: HP
- Latest update: Oct 23,2026
A company has HPE Aruba Networking APs running AOS-10 that connect to AOS-CX switches. The
APs will:
. Authenticate as 802.1X supplicants to HPE Aruba Networking ClearPass Policy Manager (CPPM)
. Be assigned to the "APs" role on the switches
. Have their traffic forwarded locally
What information do you need to help you determine the VLAN settings for the "APs" role?
- A . Whether the APs have static or DHCP-assigned IP addresses
- B . Whether the switches are using local user-roles (LURs) or downloadable user-roles (DURs)
- C . Whether the switches have established tunnels with an HPE Aruba Networking gateway
- D . Whether the APs bridge or tunnel traffic on their SSIDs
D
Explanation:
To determine the VLAN settings for the "APs" role on AOS-CX switches, it is crucial to know whether the APs bridge or tunnel traffic on their SSIDs. If the APs are bridging traffic, the VLAN settings on the switch need to align with the VLANs used by the SSIDs. If the APs are tunneling traffic to a controller or gateway, the VLAN settings might differ as the traffic is encapsulated and forwarded through the tunnel. Understanding this aspect ensures that the VLAN configuration on the switches correctly supports the traffic forwarding method employed by the APs.
Reference: Aruba’s AOS-10 and AOS-CX documentation provide guidance on VLAN configuration and traffic forwarding methods, highlighting the importance of aligning VLAN settings with the APs’ traffic handling mode.
A company has Aruba APs that are controlled by Central and that implement WIDS. When you check WIDS events, you see a "detect valid SSID misuse" event.
What can you interpret from this event, and what steps should you take?
- A . Clients are failing to authenticate to corporate SSIDs. You should first check for misconfigured authentication settings and then investigate a possible threat.
- B . Admins have likely misconfigured SSID security settings on some of the company’s APs. You should have them check those settings.
- C . Hackers are likely trying to pose as authorized APs. You should use the detecting radio information and immediately track down the device that triggered the event.
- D . This event might be a threat but is almost always a false positive. You should wait to see the event over several days before following up on it.
C
Explanation:
The "Detect Valid SSID Misuse" event in Aruba’s Wireless Intrusion Detection System (WIDS) indicates that a valid SSID, associated with your network, is being broadcast from an unauthorized source. This scenario often signals a potential rogue access point attempting to deceive clients into connecting to it (e.g., for credential harvesting or man-in-the-middle attacks).
Refer to the Exhibit:
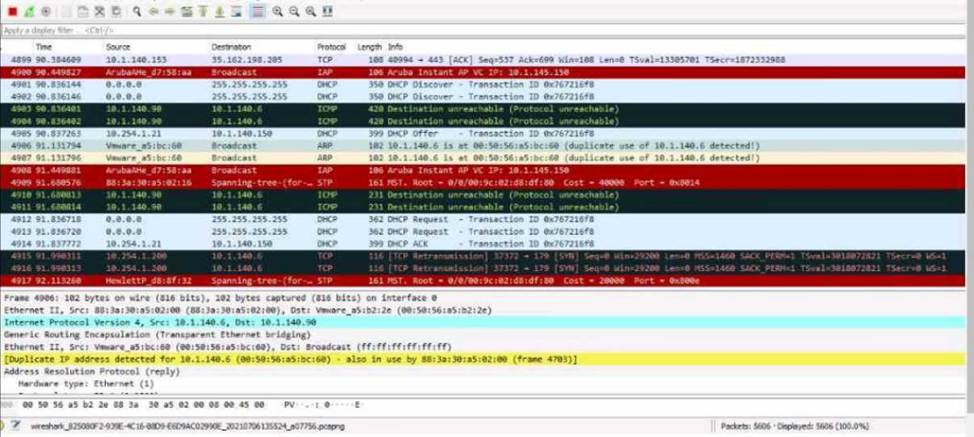
These packets have been captured from VLAN 10. which supports clients that receive their IP addresses with DHCP.
What can you interpret from the packets that you see here?
These packets have been captured from VLAN 10, which supports clients that receive their IP addresses with DHCP.
What can you interpret from the packets that you see here?
- A . Someone is possibly implementing a MAC spoofing attack to gain unauthorized access.
- B . The mirroring session that captured the packets was likely misconfigured and captured duplicate traffic.
- C . An admin has likely misconfigured two clients to use the same DHCP settings.
- D . Someone is possibly implementing an ARP poisoning and MITM attack.
A
Explanation:
The exhibit reveals duplicate IP addresses detected for 10.1.140.6, associated with two different
MAC addresses:
88:56:56:ab:c6:89
88:13:30:a3:02:00
Key observations:
Duplicate IP Address Detection:
The message "Duplicate IP address detected for 10.1.140.6" clearly indicates two devices claiming the same IP address.
This typically occurs when one device spoofs the MAC address of another device to intercept or disrupt traffic.
MAC Spoofing Context:
MAC spoofing is a tactic used to impersonate another device’s hardware address to gain unauthorized access to a network.
By spoofing a legitimate IP-MAC pairing, an attacker can bypass security mechanisms or cause denial-of-service conditions.
Why the Other Options are Incorrect:
Option B (Mirroring Misconfigured): While mirroring misconfiguration can duplicate traffic, it does not lead to a "duplicate IP detected" alert.
Option C (Misconfigured DHCP): Misconfigurations usually result in DHCP conflicts, but they do not typically involve two different MAC addresses for the same IP.
Option D (ARP Poisoning/MITM): ARP poisoning involves falsified ARP tables, but it does not directly trigger duplicate IP address detection. Instead, ARP packets flood the network.
Conclusion:
The evidence strongly suggests MAC spoofing, as two different MAC addresses are claiming the same IP address (10.1.140.6). This behavior is typical of attempts to gain unauthorized access or disrupt network operations.
Refer to the Exhibit:
These packets have been captured from VLAN 10. which supports clients that receive their IP addresses with DHCP.
What can you interpret from the packets that you see here?
These packets have been captured from VLAN 10, which supports clients that receive their IP addresses with DHCP.
What can you interpret from the packets that you see here?
- A . Someone is possibly implementing a MAC spoofing attack to gain unauthorized access.
- B . The mirroring session that captured the packets was likely misconfigured and captured duplicate traffic.
- C . An admin has likely misconfigured two clients to use the same DHCP settings.
- D . Someone is possibly implementing an ARP poisoning and MITM attack.
A
Explanation:
The exhibit reveals duplicate IP addresses detected for 10.1.140.6, associated with two different
MAC addresses:
88:56:56:ab:c6:89
88:13:30:a3:02:00
Key observations:
Duplicate IP Address Detection:
The message "Duplicate IP address detected for 10.1.140.6" clearly indicates two devices claiming the same IP address.
This typically occurs when one device spoofs the MAC address of another device to intercept or disrupt traffic.
MAC Spoofing Context:
MAC spoofing is a tactic used to impersonate another device’s hardware address to gain unauthorized access to a network.
By spoofing a legitimate IP-MAC pairing, an attacker can bypass security mechanisms or cause denial-of-service conditions.
Why the Other Options are Incorrect:
Option B (Mirroring Misconfigured): While mirroring misconfiguration can duplicate traffic, it does not lead to a "duplicate IP detected" alert.
Option C (Misconfigured DHCP): Misconfigurations usually result in DHCP conflicts, but they do not typically involve two different MAC addresses for the same IP.
Option D (ARP Poisoning/MITM): ARP poisoning involves falsified ARP tables, but it does not directly trigger duplicate IP address detection. Instead, ARP packets flood the network.
Conclusion:
The evidence strongly suggests MAC spoofing, as two different MAC addresses are claiming the same IP address (10.1.140.6). This behavior is typical of attempts to gain unauthorized access or disrupt network operations.
You are configuring the HPE Aruba Networking ClearPass Device Insight Integration settings on ClearPass Policy Manager (CPPM).
For which use case should you set the ‘Tag Updates Action" to "apply for all tag updates"?
- A . When the Device Insight integration poll interval is set to a relatively long interval but you still want CPPM to be informed quickly about devices’ new tags.
- B . When Device Insight tags are only used to identify dangerous devices, and you want to disconnect those devices without having to set up new rules in enforcement policies.
- C . When CPPM is gathering posture information for CPDI, and you want CPDI to always have access to the most up-to-date information.
- D . When you plan to have CPPM issue CoAs for clients with new tags, but do not want to have to list those specific tags in the Device Integration settings in advance.
D
Explanation:
Tag Updates Action – "Apply for All Tag Updates":
This setting ensures that all updated tags from Device Insight (CPDI) are applied dynamically.
It is particularly useful when you want to trigger Change of Authorization (CoA) without explicitly predefining the tag values.
Option D: Correct. This setting allows CPPM to issue CoAs automatically for updated tags without requiring prior configuration of specific tags.
Option A: Incorrect. The setting is not directly related to reducing the poll interval latency. Option B: Incorrect. Disconnecting devices based on dangerous tags would require predefined enforcement rules.
Option C: Incorrect. Posture information updates do not directly rely on this setting.
A company has an HPE Aruba Networking ClearPass cluster with several servers.
ClearPass Policy Manager (CPPM) is set up to:
. Update client attributes based on Syslog messages from third-party appliances
. Have the clients reauthenticate and apply new profiles to the clients based on the updates
To ensure that the correct profiles apply, what is one step you should take?
- A . Configure a CoA action for all tag updates in the ClearPass Device Insight integration settings.
- B . Tune the CoA delay on the ClearPass servers to a value of 5 seconds or greater.
- C . Set the cluster’s Endpoint Context Servers polling interval to a value of 5 seconds or less.
- D . Configure the cluster to periodically clean up (delete) unknown endpoints.
B
Explanation:
To ensure that the correct profiles apply after client attributes are updated based on Syslog messages, you should tune the Change of Authorization (CoA) delay on the ClearPass servers to a value of 5 seconds or greater. This delay allows sufficient time for the attribute updates to be processed and for the reauthentication to occur correctly, ensuring that the updated profiles are accurately applied to the clients.