
Fortinet NSE7_OTS-7.2.0 Practice Exams
Last updated on Oct 21,2026- Exam Code: NSE7_OTS-7.2.0
- Exam Name: Fortinet NSE 7 - OT Security 7.2.0
- Certification Provider: Fortinet
- Latest update: Oct 21,2026
What can be assigned using network access control policies?
- A . Layer 3 polling intervals
- B . FortiNAC device polling methods
- C . Logical networks
- D . Profiling rules
Refer to the exhibit and analyze the output.
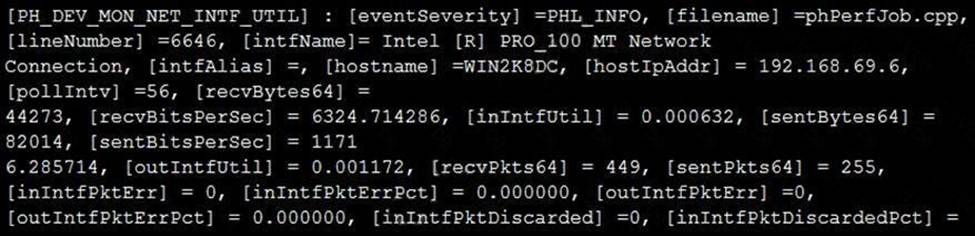
Which statement about the output is true?
- A . This is a sample of a FortiAnalyzer system interface event log.
- B . This is a sample of an SNMP temperature control event log.
- C . This is a sample of a PAM event type.
- D . This is a sample of FortiGate interface statistics.
Which statement is correct about processing matched rogue devices by FortiNAC?
- A . FortiNAC cannot revalidate matched devices.
- B . FortiNAC remembers the match ng rule of the rogue device
- C . FortiNAC disables matching rule of previously-profiled rogue devices.
- D . FortiNAC matches the rogue device with only one device profiling rule.
The OT network analyst run different level of reports to quickly explore failures that could put the network at risk. Such reports can be about device performance.
Which FortiSIEM reporting method helps to identify device failures?
- A . Business service reports
- B . Device inventory reports
- C . CMDB operational reports
- D . Active dependent rules reports
Refer to the exhibit.
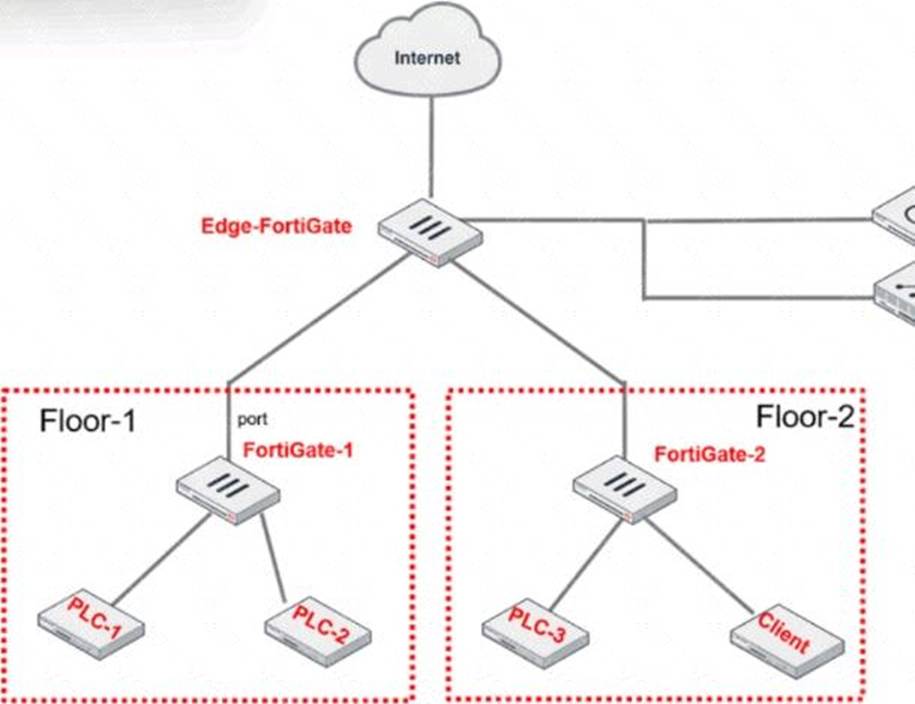
PLC-3 and CLIENT can send traffic to PLC-1 and PLC-2. FGT-2 has only one software switch (SSW-1) connecting both PLC-3 and CLIENT. PLC-3 and CLIENT can send traffic to each other at the Layer 2 level.
What must the OT admin do to prevent Layer 2-level communication between PLC-3 and CLIENT?
- A . Set a unique forward domain for each interface of the software switch.
- B . Create a VLAN for each device and replace the current FGT-2 software switch members.
- C . Enable explicit intra-switch policy to require firewall policies on FGT-2.
- D . Implement policy routes on FGT-2 to control traffic between devices.
Which two statements are true when you deploy FortiGate as an offline IDS? (Choose two.)
- A . FortiGate receives traffic from configured port mirroring.
- B . Network traffic goes through FortiGate.
- C . FortiGate acts as network sensor.
- D . Network attacks can be detected and blocked.
An OT administrator is defining an incident notification policy using FortiSIEM and would like to configure the system with a notification policy. If an incident occurs, the administrator would like to be able to intervene and block an IP address or disable a user in Active Directory from FortiSIEM.
Which step must the administrator take to achieve this task?
- A . Configure a fabric connector with a notification policy on FortiSIEM to connect with FortiGate.
- B . Create a notification policy and define a script/remediation on FortiSIEM.
- C . Define a script/remediation on FortiManager and enable a notification rule on FortiSIEM.
- D . Deploy a mitigation script on Active Directory and create a notification policy on FortiSIEM.
B
Explanation:
https://fusecommunity.fortinet.com/blogs/silviu/2022/04/12/fortisiempublishingscript
Refer to the exhibit.
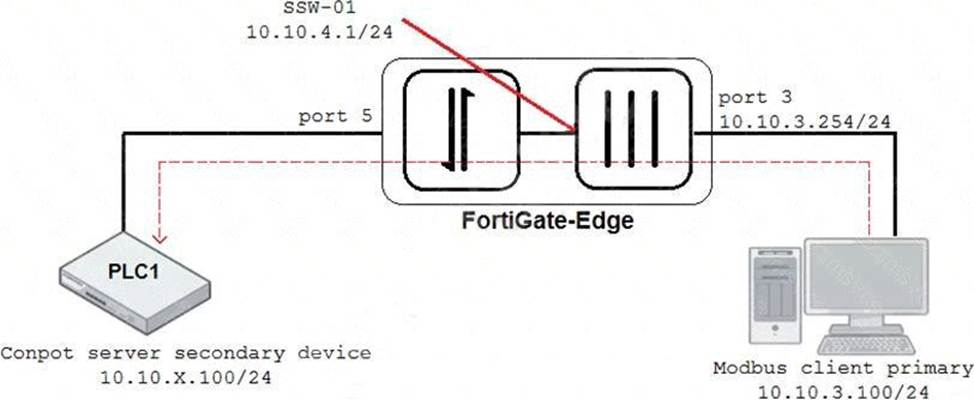
An OT architect has implemented a Modbus TCP with a simulation server Conpot to identify and control the Modus traffic in the OT network. The FortiGate-Edge device is configured with a software switch interface ssw-01.
Based on the topology shown in the exhibit, which two statements about the successful simulation of traffic between client and server are true? (Choose two.)
- A . The FortiGate-Edge device must be in NAT mode.
- B . NAT is disabled in the FortiGate firewall policy from port3 to ssw-01.
- C . The FortiGate devices is in offline IDS mode.
- D . Port5 is not a member of the software switch.
Refer to the exhibit.
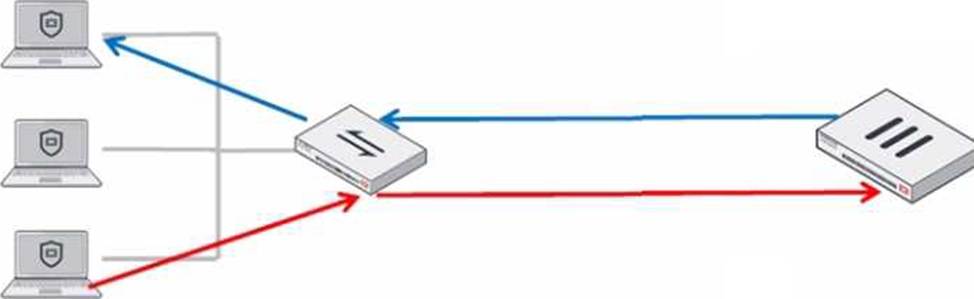
In order for a FortiGate device to act as router on a stick, what configuration must an OT network architect implement on FortiGate to achieve inter-VLAN routing?
- A . Set a unique forward domain on each interface on the network.
- B . Set FortiGate to operate in transparent mode.
- C . Set a software switch on FortiGate to handle inter-VLAN traffic.
- D . Set a FortiGate interface with the switch to operate as an 802.1 q trunk.
Refer to the exhibit.
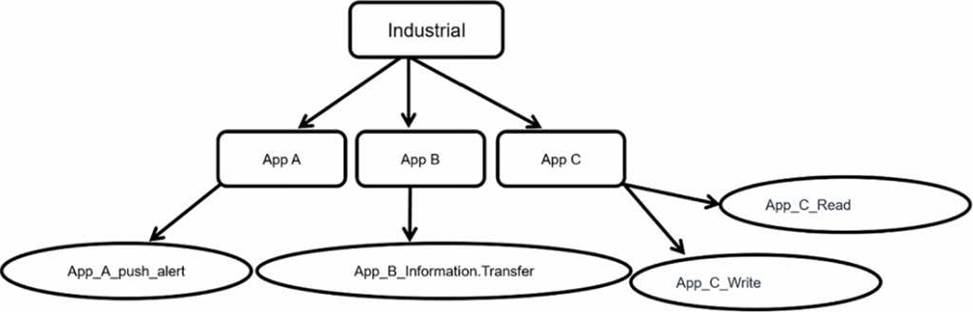
Which statement is true about application control inspection?
- A . The industrial application control inspection process is unique among application categories.
- B . Security actions cannot be applied on the lowest level of the hierarchy.
- C . You can control security actions only on the parent-level application signature
- D . The parent signature takes precedence over the child application signature.