
Fortinet NSE7_OTS-7.2.0 Practice Exams
Last updated on Oct 21,2026- Exam Code: NSE7_OTS-7.2.0
- Exam Name: Fortinet NSE 7 - OT Security 7.2.0
- Certification Provider: Fortinet
- Latest update: Oct 21,2026
FortiAnalyzer is implemented in the OT network to receive logs from responsible FortiGate devices.
The logs must be processed by FortiAnalyzer.
In this scenario, which statement is correct about the purpose of FortiAnalyzer receiving and processing multiple log messages from a given PLC or RTU?
- A . To isolate PLCs or RTUs in the event of external attacks
- B . To configure event handlers and take further action on FortiGate
- C . To determine which type of messages from the PLC or RTU causes issues in the plant
- D . To help OT administrators configure the network and prevent breaches
An OT network consists of multiple FortiGate devices. The edge FortiGate device is deployed as the secure gateway and is only allowing remote operators to access the ICS networks on site. Management hires a third-party company to conduct health and safety on site. The third-party company must have outbound access to external resources.
As the OT network administrator, what is the best scenario to provide external access to the third-party company while continuing to secure the ICS networks?
- A . Configure outbound security policies with limited active authentication users of the third-party company.
- B . Create VPN tunnels between downstream FortiGate devices and the edge FortiGate to protect ICS network traffic.
- C . Split the edge FortiGate device into multiple logical devices to allocate an independent VDOM for the third-party company.
- D . Implement an additional firewall using an additional upstream link to the internet.
An OT network architect needs to secure control area zones with a single network access policy to provision devices to any number of different networks.
On which device can this be accomplished?
- A . FortiGate
- B . FortiEDR
- C . FortiSwitch
- D . FortiNAC
A
Explanation:
An OT network architect can accomplish the goal of securing control area zones with a single network access policy to provision devices to any number of different networks on a FortiGate device.
Which three methods of communication are used by FortiNAC to gather visibility information? (Choose three.)
- A . SNMP
- B . ICMP
- C . API
- D . RADIUS
- E . TACACS
Which statemenl about the IEC 104 protocol is true?
- A . IEC 104 is used for telecontrol SCADA in electrical engineering applications.
- B . IEC 104 is IEC 101 compliant in old SCADA systems.
- C . IEC 104 protects data transmission between OT devices and services.
- D . IEC 104 uses non-TCP/IP standards.
Refer to the exhibit, which shows a non-protected OT environment.
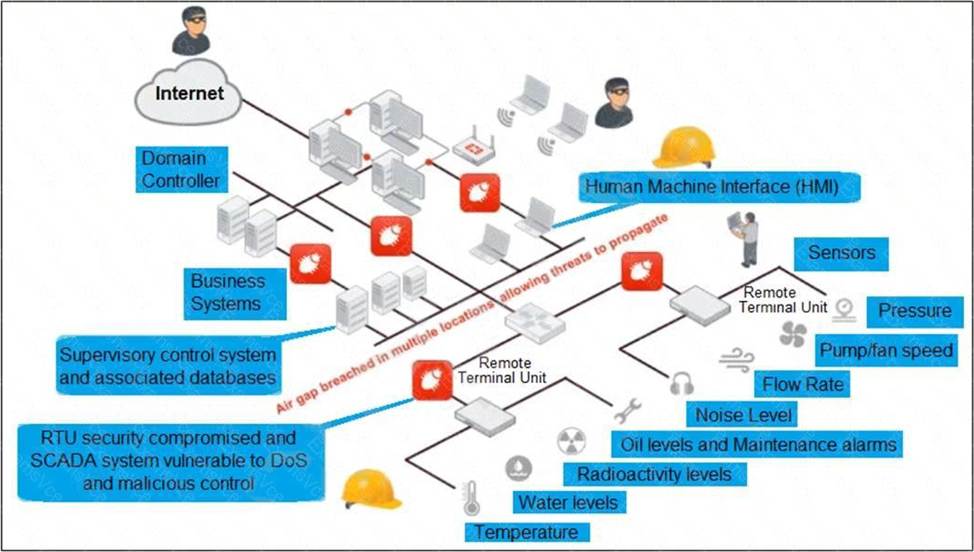
An administrator needs to implement proper protection on the OT network.
Which three steps should an administrator take to protect the OT network? (Choose three.)
- A . Deploy an edge FortiGate between the internet and an OT network as a one-arm sniffer.
- B . Deploy a FortiGate device within each ICS network.
- C . Configure firewall policies with web filter to protect the different ICS networks.
- D . Configure firewall policies with industrial protocol sensors
- E . Use segmentation
As an OT administrator, it is important to understand how industrial protocols work in an OT network.
Which communication method is used by the Modbus protocol?
- A . It uses OSI Layer 2 and the primary device sends data based on request from secondary device.
- B . It uses OSI Layer 2 and both the primary/secondary devices always send data during the communication.
- C . It uses OSI Layer 2 and both the primary/secondary devices send data based on a matching token ring.
- D . It uses OSI Layer 2 and the secondary device sends data based on request from primary device.
What are two critical tasks the OT network auditors must perform during OT network risk assessment and management? (Choose two.)
- A . Planning a threat hunting strategy
- B . Implementing strategies to automatically bring PLCs offline
- C . Creating disaster recovery plans to switch operations to a backup plant
- D . Evaluating what can go wrong before it happens
An OT supervisor has configured LDAP and FSSO for the authentication. The goal is that all the users be authenticated against passive authentication first and, if passive authentication is not successful, then users should be challenged with active authentication.
What should the OT supervisor do to achieve this on FortiGate?
- A . Configure a firewall policy with LDAP users and place it on the top of list of firewall policies.
- B . Enable two-factor authentication with FSSO.
- C . Configure a firewall policy with FSSO users and place it on the top of list of firewall policies.
- D . Under config user settings configure set auth-on-demand implicit.
C
Explanation:
The OT supervisor should configure a firewall policy with FSSO users and place it on the top of list of
firewall policies in order to achieve the goal of authenticating users against passive authentication first and, if passive authentication is not successful, then challenging them with active authentication.
In a wireless network integration, how does FortiNAC obtain connecting MAC address information?
- A . RADIUS
- B . Link traps
- C . End station traffic monitoring
- D . MAC notification traps
A
Explanation:
FortiNAC can integrate with RADIUS servers to obtain MAC address information for wireless clients that authenticate through the RADIUS server.
Reference: Fortinet NSE 7 – OT Security 6.4 Study Guide, Chapter 4: OT Security Devices, page 4-28.