
Fortinet FCSS_SASE_AD-24 Practice Exams
Last updated on Oct 22,2026- Exam Code: FCSS_SASE_AD-24
- Exam Name: FCSS - FortiSASE 24 Administrator
- Certification Provider: Fortinet
- Latest update: Oct 22,2026
Which statement describes the FortiGuard forensics analysis feature on FortiSASE?
- A . It can help troubleshoot user-to-application performance issues.
- B . It can help customers identify and mitigate potential risks to their network.
- C . It can monitor endpoint resources in real-time.
- D . It is a 24x7x365 monitoring service of your FortiSASE environment.
B
Explanation:
The FortiGuard forensics analysis feature on FortiSASE is designed to help customers identify and mitigate potential risks to their network. This feature provides detailed insights into suspicious activities, threats, and anomalies detected by FortiSASE. By analyzing logs, traffic patterns, and threat intelligence, FortiGuard forensics enables administrators to investigate incidents, understand their root causes, and take proactive measures to secure the network.
Here’s why the other options are incorrect:
Which benefits does Secure Private Access (SPA) provide within FortiSASE? (Select all that apply)
- A . Secure access to private cloud applications
- B . Simplified network topology
- C . Centralized security management
- D . Granular access control based on user roles
Which deployment case scenario effectively illustrates FortiSASE’s capability in handling high-traffic environments?
- A . A small office with limited internet usage
- B . A multinational company with global data exchanges
- C . A local retailer using a single cloud provider
- D . A home office setup with basic web filtering needs
Which endpoint functionality can you configure using FortiSASE?
- A . You can configure inline sandbox to scan zero-day malware attacks.
- B . You can enable and push web filter to FortiClient endpoints.
- C . It can be applied to both SWG and VPN deployments.
- D . Site-based FortiExtender users can perform on-demand vulnerability scans.
When viewing the daily summary report generated by FortiSASE, the administrator notices that the report contains very little data.
What is a possible explanation for this almost empty report?
- A . Log allowed traffic is set to Security Events for all policies.
- B . There are no security profile groups applied to all policies.
- C . The web filter security profile is not set to Monitor.
- D . Digital experience monitoring is not configured.
A
Explanation:
The issue of an almost empty daily summary report in FortiSASE can often be traced back to how logging is configured within the system. Specifically, if "Log Allowed Traffic" is set to "Security Events" for all policies, it means that only security-related events (such as threats or anomalies) are being logged, while normal, allowed traffic is not being recorded. Since most traffic in a typical network environment is allowed, this configuration would result in very little data being captured and subsequently reported in the daily summary.
Here’s a breakdown of why the other options are less likely to be the cause:
B. There are no security profile groups applied to all policies: While applying security profiles is important for comprehensive protection, their absence does not directly affect the volume of data in reports unless specific logging settings are also misconfigured.
C. The web filter security profile is not set to Monitor: This option pertains specifically to web filtering activities. Even if web filtering is not set to monitor mode, other types of traffic and logs should still populate the report.
D. Digital experience monitoring is not configured: Digital Experience Monitoring (DEM) focuses on user experience metrics rather than general traffic logging. Its absence would not lead to an almost empty report.
To resolve this issue, administrators should review the logging settings across all policies and ensure that "Log Allowed Traffic" is appropriately configured to capture the necessary data for reporting purposes.
Reference: Fortinet FCSS FortiSASE Documentation – Reporting and Logging Best Practices FortiSASE Administration Guide – Configuring Logging Settings
Which FortiOS command would you use to automate the bulk registration of users within FortiSASE?
- A . execute user-import bulk
- B . config user bulk-register
- C . import user-bulk registration
- D . config bulk-user import
Which logs should be prioritized for real-time monitoring in FortiSASE? (Select all that apply)
- A . Security event logs
- B . User authentication logs
- C . Bandwidth usage logs
- D . Power consumption logs
Refer to the exhibit.
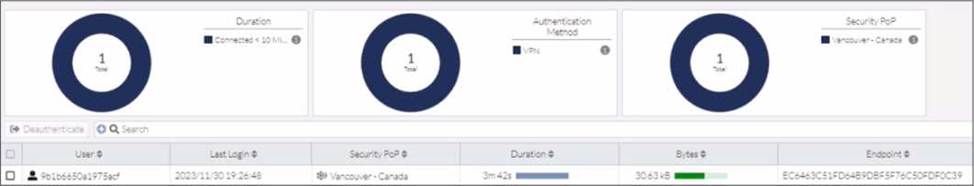
In the user connection monitor, the FortiSASE administrator notices the user name is showing random characters.
Which configuration change must the administrator make to get proper user information?
- A . Turn off log anonymization on FortiSASE.
- B . Add more endpoint licenses on FortiSASE.
- C . Configure the username using FortiSASE naming convention.
- D . Change the deployment type from SWG to VPN.
A
Explanation:
In the user connection monitor, the random characters shown for the username indicate that log anonymization is enabled. Log anonymization is a feature that hides the actual user information in the logs for privacy and security reasons. To display proper user information, you need to disable log anonymization.
Log Anonymization:
When log anonymization is turned on, the actual usernames are replaced with random characters to protect user privacy.
This feature can be beneficial in certain environments but can cause issues when detailed user monitoring is required.
Disabling Log Anonymization:
Navigate to the FortiSASE settings.
Locate the log settings section.
Disable the log anonymization feature to ensure that actual usernames are displayed in the logs and user connection monitors.
Reference: FortiSASE 23.2 Documentation: Provides detailed steps on enabling and disabling log anonymization.
Fortinet Knowledge Base: Explains the impact of log anonymization on user monitoring and logging.
Which FortiSASE component is essential for securely connecting remote users to cloud applications?
- A . Firewall as a Service (FWaaS)
- B . Firewall as a Service (FWaaS)
- C . Secure SD-WAN (SSA)
- D . Secure Private Access (SPA)
A customer wants to upgrade their legacy on-premises proxy to a could-based proxy for a hybrid network.
Which FortiSASE features would help the customer to achieve this outcome?
- A . SD-WAN and NGFW
- B . SD-WAN and inline-CASB
- C . zero trust network access (ZTNA) and next generation firewall (NGFW)
- D . secure web gateway (SWG) and inline-CASB
D
Explanation:
For a customer looking to upgrade their legacy on-premises proxy to a cloud-based proxy for a hybrid network, the combination of Secure Web Gateway (SWG) and Inline Cloud Access Security Broker (CASB) features in FortiSASE will provide the necessary capabilities. Secure Web Gateway (SWG):
SWG provides comprehensive web security by inspecting and filtering web traffic to protect against web-based threats.
It ensures that all web traffic, whether originating from on-premises or remote locations, is inspected and secured by the cloud-based proxy.
Inline Cloud Access Security Broker (CASB):
CASB enhances security by providing visibility and control over cloud applications and services.
Inline CASB integrates with SWG to enforce security policies for cloud application usage, preventing unauthorized access and data leakage.
Reference: FortiOS 7.2 Administration Guide: Details on SWG and CASB features.
FortiSASE 23.2 Documentation: Explains how SWG and inline-CASB are used in cloud-based proxy solutions.