
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
Examine the output of the ‘get router info bgp summary’ command shown in the exhibit; then answer the question below.
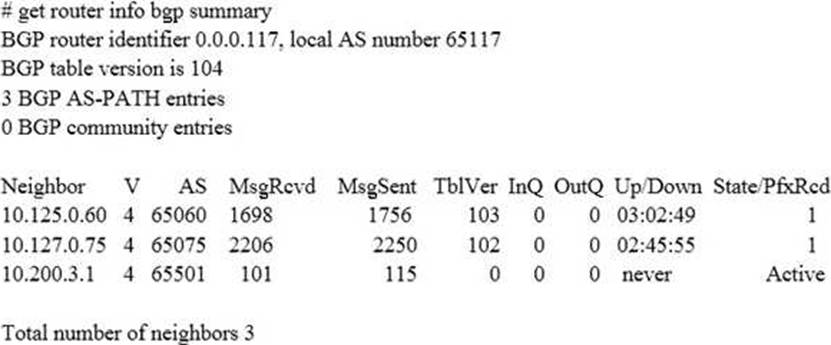
Which statements are true regarding the output in the exhibit? (Choose two.)
- A . BGP state of the peer 10.125.0.60 is Established.
- B . BGP peer 10.200.3.1 has never been down since the BGP counters were cleared.
- C . Local BGP peer has not received an OpenConfirm from 10.200.3.1.
- D . The local BGP peer has received a total of 3 BGP prefixes.
Examine the following partial outputs from two routing debug commands; then answer the question below.
# get router info kernel
tab=254 vf=0 scope=0type=1 proto=11 prio=0 0.0.0.0/0.0.0.0/0->0.0.0.0/0 pref=0.0.0.0 gwy=10.200.1.254 dev=2(port1)
tab=254 vf=0 scope=0type=1 proto=11 prio=10 0.0.0.0/0.0.0.0/0->0.0.0.0/0 pref=0.0.0.0 gwy=10.200.2.254 dev=3(port2)
tab=254 vf=0 scope=253type=1 proto=2 prio=0 0.0.0.0/0.0.0.0/.->10.0.1.0/24 pref=10.0.1.254 gwy=0.0.0.0 dev=4(port3)
# get router info routing-table all s*0.0.0.0/0 [10/0] via 10.200.1.254, portl [10/0] via 10.200.2.254, port2, [10/0] dO.0.1.0/24 is directly connected, port3 dO.200.1.0/24 is directly connected, portl d0.200.2.0/24 is directly connected, port2
Which outbound interface or interfaces will be used by this FortiGate to route web traffic from internal users to the Internet?
- A . Both portl and port2.
- B . port2.
- C . port!
- D . port3.
Refer to the exhibit, which shows a partial enterprise network.
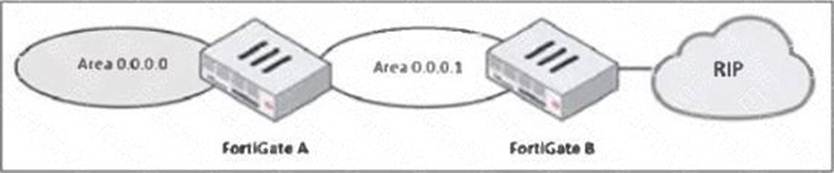
An administrator would like the area 0.0.0.0 to detect the external network.
What must the administrator configure?
- A . Enable RIP redistribution on FortiGate B.
- B . Configure a distribute-route-map-in on FortiGate B.
- C . Configure a virtual link between FortiGate A and B.
- D . Set the area 0.0.0.l type to stub on FortiGate A and B.
A
Explanation:
The diagram shows amulti-area OSPF networkwhere:
#FortiGate Ais inOSPF Area 0 (Backbone area).
#FortiGate Bis inOSPF Area 0.0.0.1and is connected to anRIP network.
To ensure thatOSPF Area 0 (0.0.0.0) learns routes from the external RIP network, FortiGate B must redistribute RIP routes into OSPF.
Steps to achieve this:
When does a RADIUS server send an Access-Challenge packet?
- A . The server does not have the user credentials yet.
- B . The server requires more information from the user, such as the token code for two-factor authentication.
- C . The user credentials are wrong.
- D . The user account is not found in the server.
View the partial crashlog output, and then answer the question below.
# diagnose debug crashlog read
2017-04-20 16:23:10 <00114> IPS enter fail open mode: engines=21 socketsize=123425682
2017-04-20 16:23:10 sessionact=pass
2017-04-20 16:24:09 <00114> IPS exit fail open mode
Which of the following statements are true regarding this FortiGate’s fail-open configuration? (Choose two.)
- A . FortiGate was dropping traffic while fail-open mode was active.
- B . Fail-open is enabled in FortiGate’s global IPS configuration.
- C . Fail-open is disabled in FortiGate’s global IPS configuration.
- D . FortiGate was passing traffic while fail-open mode was active.
An administrator wants to scale the IBGP sessions and optimize the routing table in an IBGP network.
Which parameter should the administrator configure?
- A . network-import-check
- B . ibgp-enforce-multihop
- C . neighbor-group
- D . route-reflector-client
D
Explanation:
In anIBGP (Internal BGP) network, all routers must befully meshed, meaning every router must establish a BGP session with every other router in the sameautonomous system (AS). Thisdoes not scale wellin large networks due to the exponential increase in BGP sessions.
Tooptimize and scale IBGP,Route Reflectors (RRs)are used. ARoute Reflector (RR)reduces the number ofIBGP peer connectionsby allowing acentralized router (RR)to redistribute IBGP routes to other IBGP peers (calledclients). This eliminates the need for afull mesh, significantlyreducing BGP session overhead.
By configuring theroute-reflector-clientsetting on IBGP peers, an administrator can:
#Scale IBGP sessionsby reducing the number of direct BGP peer connections.
#Optimize the routing tableby ensuring routes are efficiently propagated within the IBGP network.
#Eliminate the need for full mesh topology, making IBGP more manageable.
Which two statements about the Security Fabric are true? (Choose two.)
- A . Only the root FortiGate collects network information and forwards it to FortiAnalyzer.
- B . Branch FortiGate devices must be configured first.
- C . FortiGate uses FortiTelemetry protocol to communicate with FortiAnalyzer.
- D . All FortiGate devices in the Security Fabric must have bidirectional FortiTelemetry connectivity.
View the exhibit, which contains the output of a real-time debug, and then answer the question below.
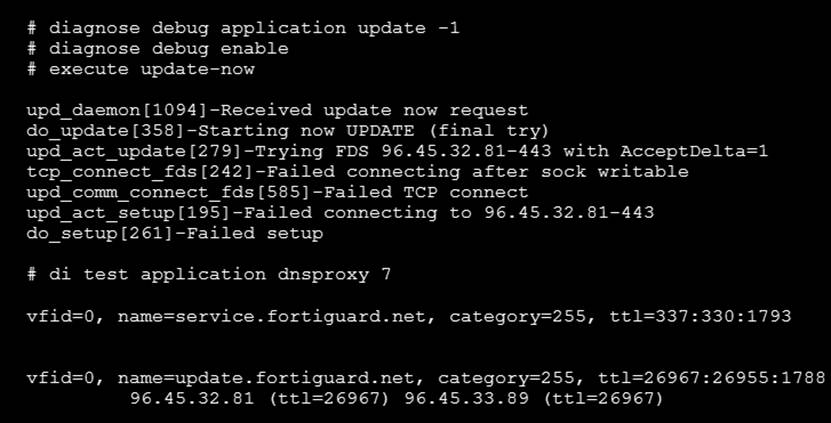
Which one of the following statements describes why the update is failing?
- A . The update should be using port 53 or port 8888, instead of port 443.
- B . FortiGate is unable to resolve the required FQDN (service.fortiguard.net) for AV and IPS updates.
- C . FortiGate is unable to establish a TCP connection with FDS.
- D . The administrator should use the execute update-wf command instead.
Examine the following partial outputs from two routing debug commands; then answer the question below:
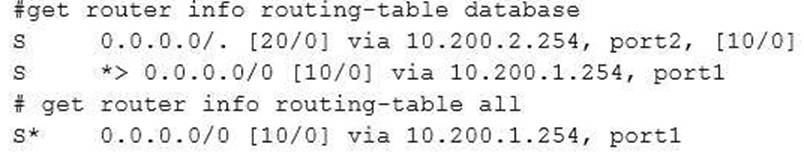
Why the default route using port2 is not displayed in the output of the second command?
- A . It has a lower priority than the default route using port1.
- B . It has a higher priority than the default route using port1.
- C . It has a higher distance than the default route using port1.
- D . It is disabled in the FortiGate configuration.
Which statement about IKE and IKE NAT-T is true?
- A . IKE is used to encapsulate ESP traffic in some situations, and IKE NAT-T is used only when the local FortiGate is using NAT on the IPsec interface.
- B . IKE is the standard implementation for IKEv1 and IKE NAT-T is an extension added in IKEv2.
- C . They both use UDP as their transport protocol and the port number is configurable.
- D . They each use their own IP protocol number.