
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
What does the command set forward-domain <domain_ID> in a transparent VDOM interface do?
- A . It configures the interface to prioritize traffic based on the domain ID, enhancing quality of service for specified VLANs.
- B . It isolates traffic within a specific VLAN by assigning a broadcast domain to an interface based on the
VLAN ID. - C . It restricts the interface to managing traffic only from the specified VLAN, effectively segregating network traffic.
- D . It assigns a unique domain ID to the interface, allowing it to operate across multiple VLANs within the same VDOM.
B
Explanation:
In atransparent mode Virtual Domain (VDOM)configuration, FortiGate operates as aLayer 2 bridgerather than performing Layer 3 routing. Theset forward-domain <domain_ID>command is used to control how traffic is forwarded between interfaces within the sametransparent VDOM.
Aforward-domainacts as abroadcast domain, meaning only interfaces with thesame forward-domain ID can exchange traffic. This setting is commonly used toseparate different VLANs or network segments within the transparent VDOM while still allowing FortiGate to apply security policies.
Refer to the exhibit, which contains the output of a web filtering diagnose command.
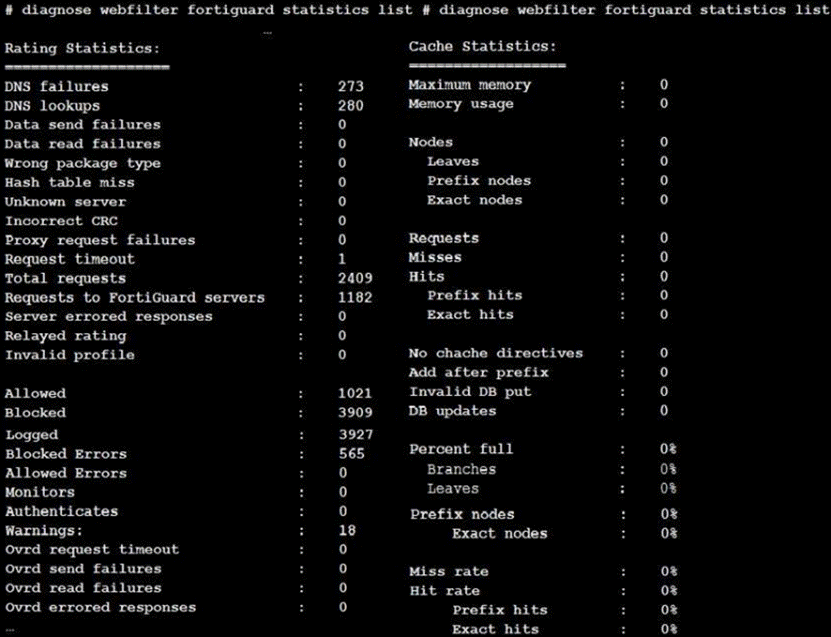
Which statement explains why the cache statistics are all zeros?
- A . The FortiGate web filter cache is disabled in the FortiGate configuration.
- B . FortiGate is using flow-based inspection which does not use the cache.
- C . The administrator has reallocated the cache memory to a separate process.
- D . There are no users making web requests.
An administrator has configured the following CLI script on FortiManager, which failed to apply any changes to the managed device after being executed
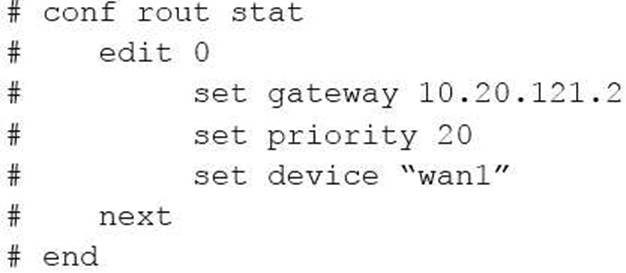
Why didn’t the script make any changes to the managed device?
- A . Commands that start with the # sign are not executed.
- B . CLI scripts will add objects only if they are referenced by policies.
- C . Incomplete commands are ignored in CLI scripts.
- D . Static routes can only be added using TCL scripts.
An administrator must enable direct communication between multiple spokes in a company’s network. Each spoke has more than one internet connection.
The requirement is for the spokes to connect directly without passing through the hub, and for the links to automatically switch to the best available connection.
How can this automatic detection and optimal link utilization between spokes be achieved?
- A . Set up OSPF routing over static VPN tunnels between spokes.
- B . Utilize ADVPN 2.0 to facilitate dynamic direct tunnels and automatic link optimization.
- C . Establish static VPN tunnels between spokes with predefined backup routes.
- D . Implement SD-WAN policies at the hub to manage spoke link quality.
B
Explanation:
ADVPN (Auto-Discovery VPN) 2.0is the optimal solution for enablingdirect spoke-to-spoke communicationwithout passing through the hub, while also allowingautomatic link selectionbased on quality metrics.
#Dynamic Direct Tunnels:
# ADVPN 2.0 allowsspokes to establish direct IPsec tunnels dynamicallybased on traffic patterns, reducing latency and improving performance.
# Unlike static VPNs, spokes do not need to pre-configure tunnels for each other.
# ADVPN 2.0monitors the qualityof multiple internet connections on each spoke.
# It automatically switches to the best available connection when the primary linkdegrades or fails.
# This is achieved by dynamically adjusting BGP-based routing or leveraging SD-WAN integration.
Which statement is true regarding File description (FD) conserve mode?
- A . IPS inspection is affected when FortiGate enters FD conserve mode.
- B . A FortiGate enters FD conserve mode when the amount of available description is less than 5%.
- C . FD conserve mode affects all daemons running on the device.
- D . Restarting the WAD process is required to leave FD conserve mode.
View the exhibit, which contains the output of a BGP debug command, and then answer the question below.
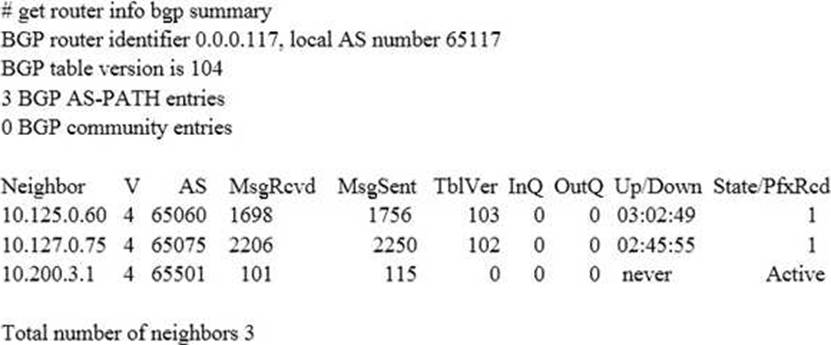
Which of the following statements about the exhibit are true? (Choose two.)
- A . For the peer 10.125.0.60, the BGP state of is Established.
- B . The local BGP peer has received a total of three BGP prefixes.
- C . Since the BGP counters were last reset, the BGP peer 10.200.3.1 has never been down.
- D . The local BGP peer has not established a TCP session to the BGP peer 10.200.3.1.
Which of the following troubleshooting steps is applicable when investigating antivirus and IPS update issues on FortiGate?
- A . Use the alternate service port 8888.
- B . Validate DNS resolution for update.fortiguard.net.
- C . Verify outbound ICMP connectivity.
- D . Use the diagnose debug rating command to check active servers.
Refer to the exhibit, which contains the partial output of the get vpn ipsec tunnel details command.
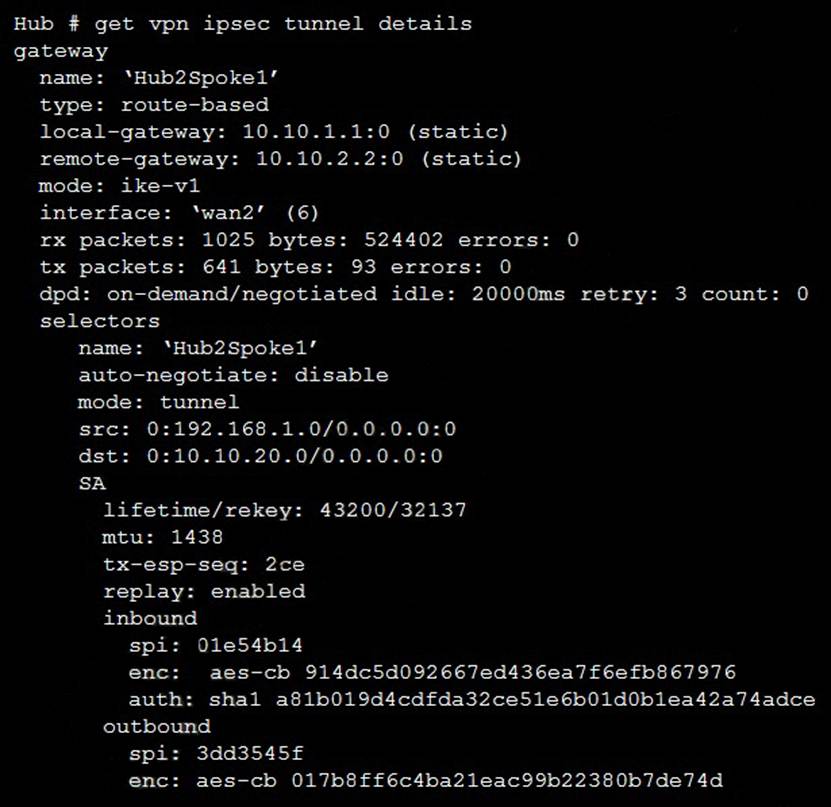
Based on the output, which two statements are correct? (Choose two.)
- A . Phase 2 authentication is set to sha1 on both sides.
- B . Hub2Spoke1 is configured on interface wan2.
- C . Anti-replay is disabled.
- D . Hub2Spoke1 is a policy-based VPN.
Refer to the exhibit, which contains a partial command output.
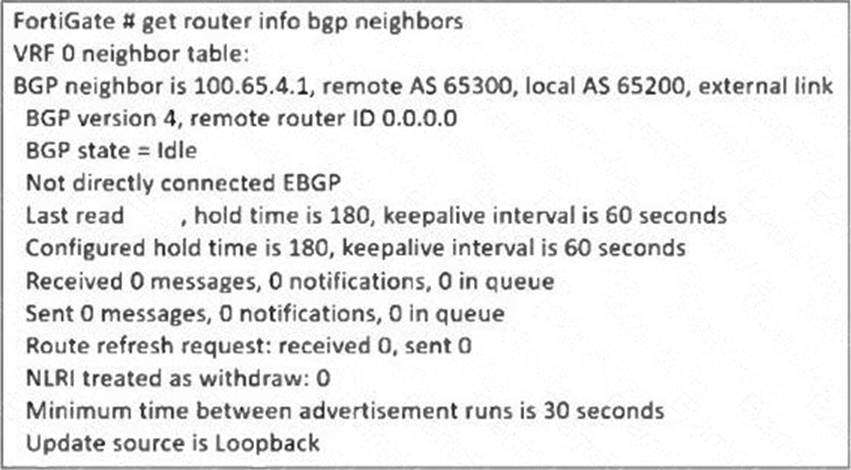
The administrator has configured BGP on FortiGate. The status of this new BGP configuration is shown in the exhibit.
What configuration must the administrator consider next?
- A . Configure a static route to 100.65.4.1.
- B . Configure the local AS to 65300.
- C . Contact the remote peer administrator to enable BGP
- D . Enable ebgp-enforce-multihop.
D
Explanation:
From theBGP neighbor status output, the key issue is thatBGP is stuck in the "Idle" state, meaning the FortiGate is unable to establish a BGP session with its peer100.65.4.1(Remote AS 65300).
The output also shows:
#"Not directly connected EBGP"# This means the BGP peer is not on the same subnet, requiring multihop BGP.
#"Update source is Loopback"# Since a loopback interface is used, FortiGate must be configured to allow BGP neighbors over multiple hops.
To resolve this issue, the administrator must enableebgp-enforce-multihop, which allows BGP sessions to be established even when the neighbors are not directly connected.
Which two statements about bulk configuration changes using FortiManager CLI scripts are correct? (Choose two.)
- A . When executed on the Policy Package, ADOM database, changes are applied directly to the managed FortiGate.
- B . When executed on the Device Database, you must use the installation wizard to apply the changes to the managed FortiGate
- C . When executed on the All FortiGate in ADOM, changes are automatically installed without creating a new revision history.
- D . When executed on the Remote FortiGate directly, administrators do not have the option to review the changes prior to installation.