
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
Examine the output of the ‘diagnose sys session list expectation’ command shown in the exhibit; then answer the question below.
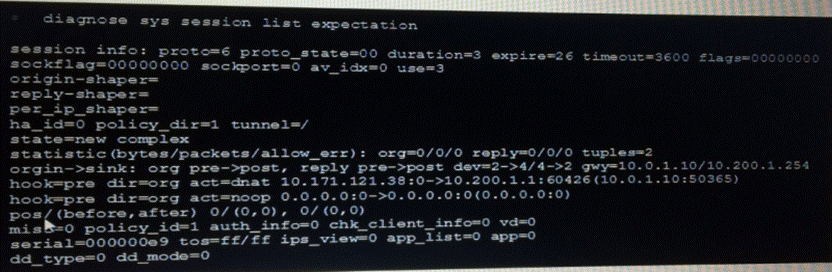
Which statement is true regarding the session in the exhibit?
- A . it was created by the FortiGate kernel to allow push updates from FortiGuard.
- B . it is for management traffic terminating at the FortiGate.
- C . it is for traffic originated from the FortiGate.
- D . it was created by a session helper or ALG.
Refer to the exhibit.
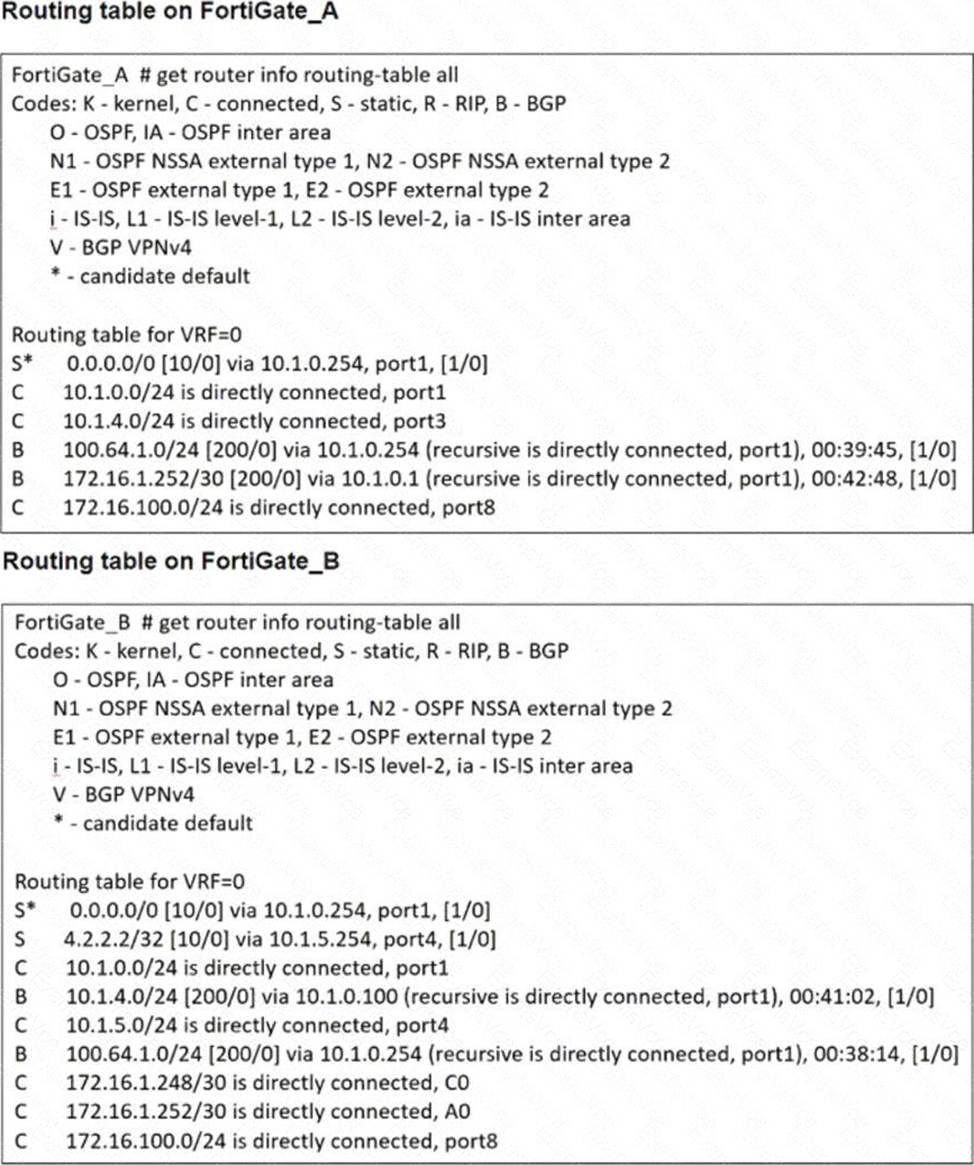
The routing tables of FortiGate_A and FortiGate_B are shown. FortiGate_A and FortiGate_B are in the same autonomous system.
The administrator wants to dynamically add only route172.16.1.248/30on FortiGate_A.
What must the administrator configure?
- A . The prefix 172.16.1.248/30 in the BGP Networks section on FortiGate_B
- B . A BGP route map out for 172.16.1.248/30 on FortiGate_B
- C . Enable Redistribute Connected in the BGP section on FortiGate_B.
- D . A BGP route map in for 172.16.1.248/30 on FortiGate_A
B
Explanation:
FortiGate_A and FortiGate_B are in thesame autonomous system (AS), andFortiGate_Adoesnot currently have route 172.16.1.248/30in its routing table. However, FortiGate_B has this routeas a connected route.
To dynamically advertiseonly172.16.1.248/30 fromFortiGate_B to FortiGate_A, the administrator must configure aBGP route map outonFortiGate_Bthat specifically permitsonlythis prefix.
A BGP route map out on FortiGate_Bcontrols which routes FortiGate_B advertises to FortiGate_A. If no filtering is applied, FortiGate_B might advertiseall BGP-learned and connected routes, which is not what the administrator wants. The route map should include aprefix-listthat explicitlyallows only172.16.1.248/30 and denies everything else.
View the exhibit, then answer the question below.
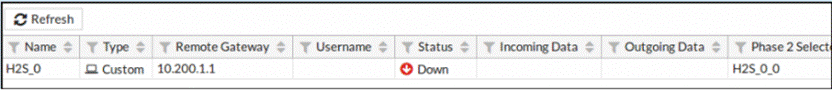
Which of the following commands will bring up the tunnel?
- A . diagnose vpn tunnel up 10.200.1.1
- B . diagnose vpn tunnel H2S_0 up
- C . diagnose vpn tunnel up H2S_0
- D . diagnose vpn tunnel up H2S_0_0
Which two configuration changes can be applied to optimize the memory usage on FortiGate? (Choose two.)
- A . Increase TCP session timers.
- B . Reduce the FortiGuard cache TTL.
- C . Use flow-based inspection.
- D . Increase the maximum file size for AV inspection.
- E . Decrease the sessions TTL.
Refer to the exhibit, which shows the output of a diagnose command.
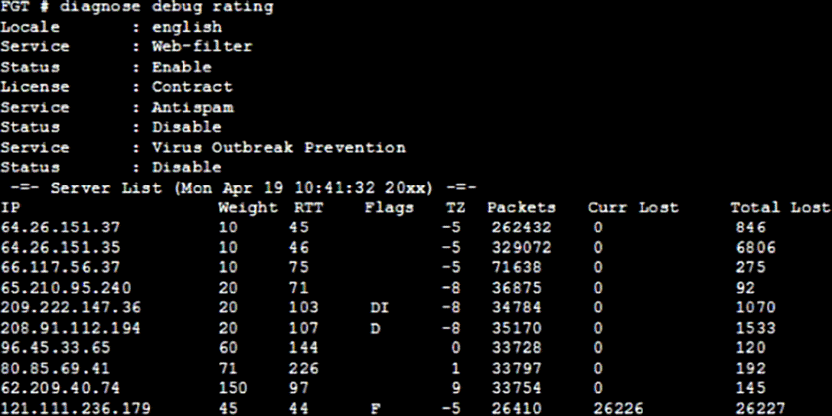
What can be concluded about the debug output in this scenario?
- A . Servers with a negative TZ value are less preferred for rating requests.
- B . There is a natural correlation between the value in the Packets field and the value in the Weight field.
- C . FortiGate used 64.26.151.37 as the initial server to validate its contract.
- D . The first server provided to FortiGate when it performed a DNS query looking for a list of rating servers, was 121.111.236.179.
An administrator added the following Ipsec VPN to a FortiGate configuration:
configvpn ipsec phasel -interface
edit "RemoteSite"
set type dynamic
set interface "portl"
set mode main
set psksecret ENC LCVkCiK2E2PhVUzZe
next
end
config vpn ipsec phase2-interface
edit "RemoteSite"
set phasel name "RemoteSite"
set proposal 3des-sha256
next
end
However, the phase 1 negotiation is failing. The administrator executed the IKF real time debug while attempting the Ipsec connection.
The output is shown in the exhibit.
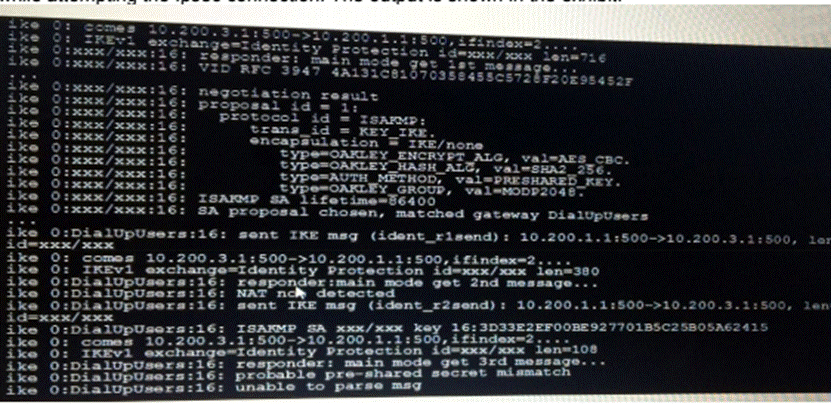
What is causing the IPsec problem in the phase 1?
- A . The incoming IPsec connection is matching the wrong VPN configuration
- B . The phrase-1 mode must be changed to aggressive
- C . The pre-shared key is wrong
- D . NAT-T settings do not match
An administrator has configured a FortiGate device with two VDOMs: root and internal.
The administrator has also created and inter-VDOM link that connects both VDOMs. The objective is to have each VDOM advertise some routes to the other VDOM via OSPF through the inter-VDOM link.
What OSPF configuration settings must match in both VDOMs to have the OSPF adjacency successfully forming? (Choose three.)
- A . Router ID.
- B . OSPF interface area.
- C . OSPF interface cost.
- D . OSPF interface MTU.
- E . Interface subnet mask.
Refer to the exhibit, which contains partial output from an IKE real-time debug.
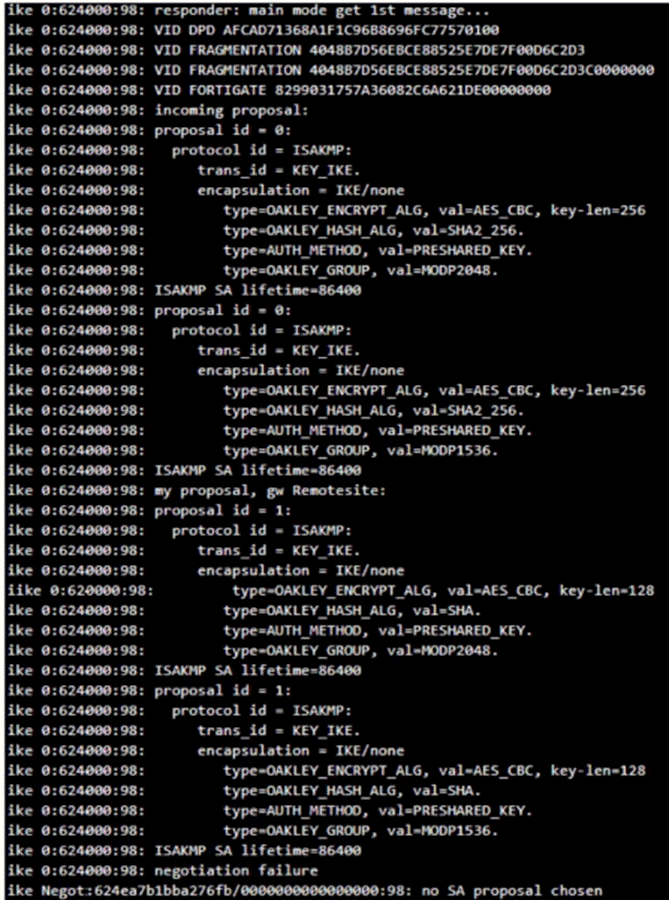
The administrator does not have access to the remote gateway.
Based on the debug output, which configuration change can the administrator make to the local gateway to resolve the phase 1 negotiation error?
- A . In the phase 1 network configuration, set the IKE version to 2.
- B . In the phase 1 proposal configuration, add AES128-SHA128 to the list of encryption algorithms.
- C . In the phase 1 proposal configuration, add AESCBC-SHA2 to the list of encryption algorithms.
- D . In the phase 1 proposal configuration, add AES256-SHA256 to the list of encryption algorithms.
Which action will FortiGate take when using the default settings for SSL certificate inspection, where the server name indication (SNI) does not match either the common name (CN) or any of the subject altemative names (SAN) in the server certificate?
- A . FortiGate uses the CN information from the Subject field in the server certificate.
- B . FortiGate uses the first entry listed in the SAN field in the server certificate.
- C . FortiGate uses the SNI from the user’s web browser.
- D . FortiGate closes the connection because this represents an invalid SSL/TLS configuration.
View the following exhibit:
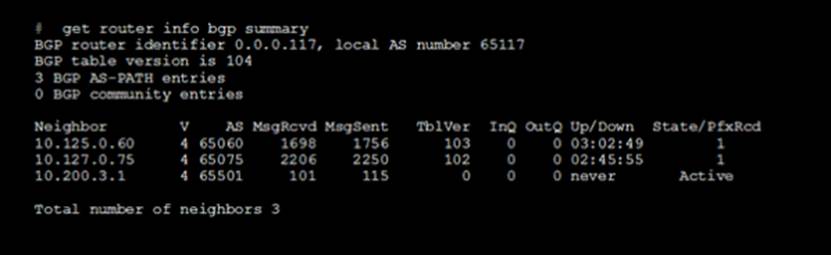
Which two statements about the BGP peer are true? (Choose two.)
- A . Since the BGP counters were last reset, the BGP peer 10.200.3.1 has never been down.
- B . For the peer 10.125.0.60, the BGP state is Established.
- C . The local BGP peer has not established a TCP session to the BGP peer 10.200.3.1.
- D . The local BGP peer has received a total of three BGP prefixes.