
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
View the exhibit, which contains the partial output of an IKE real-time debug, and then answer the question below.
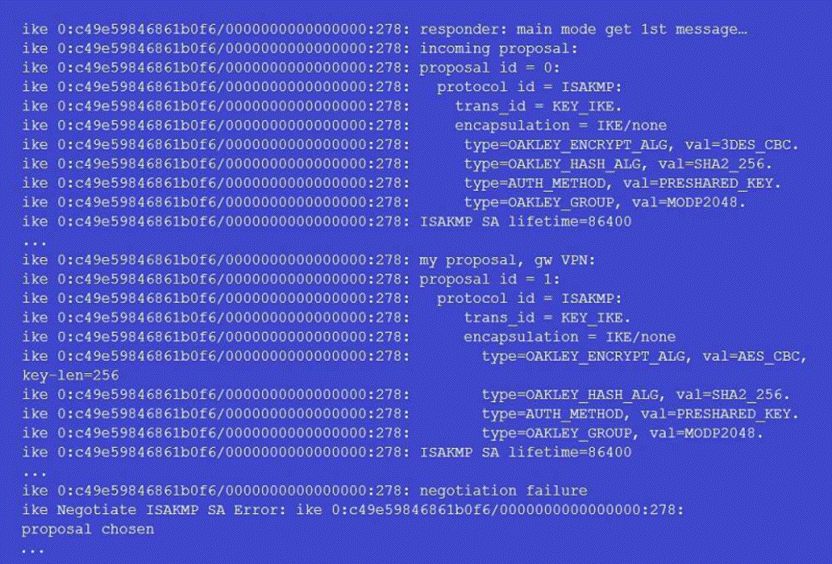
Why didn’t the tunnel come up?
- A . The pre-shared keys do not match.
- B . The remote gateway’s phase 2 configuration does not match the local gateway’s phase 2 configuration.
- C . The remote gateway’s phase 1 configuration does not match the local gateway’s phase 1 configuration.
- D . The remote gateway is using aggressive mode and the local gateway is configured to use man mode.
Which two configuration settings change the behavior for content-inspected traffic while FortiGate is in conserve mode? (Choose two.)
- A . IPS failopen
- B . mem failopen
- C . AV failopen
- D . UTM failopen
View the exhibit, which contains the output of a web diagnose command, and then answer the question below.
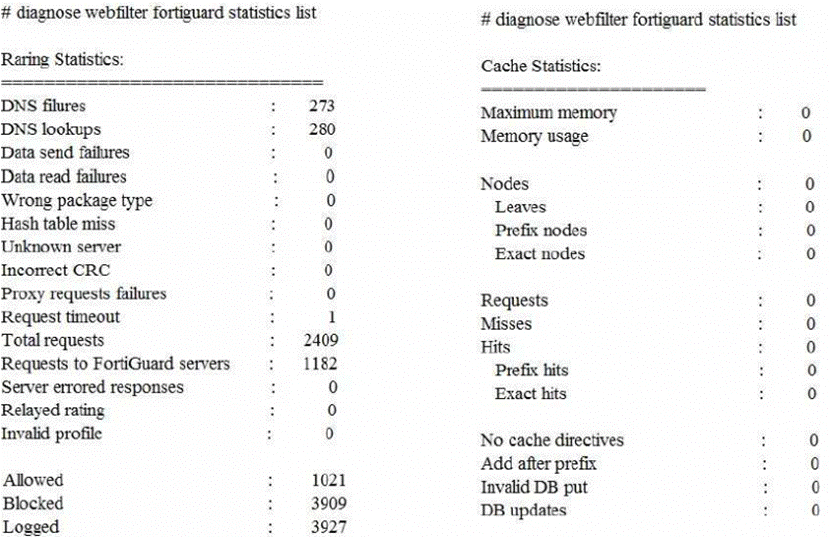
Which one of the following statements explains why the cache statistics are all zeros?
- A . The administrator has reallocated the cache memory to a separate process.
- B . There are no users making web requests.
- C . The FortiGuard web filter cache is disabled in the FortiGate’s configuration.
- D . FortiGate is using a flow-based web filter and the cache applies only to proxy-based inspection.
Which of the following statements is true regarding a FortiGate configured as an explicit web proxy?
- A . FortiGate limits the number of simultaneous sessions per explicit web proxy user. This limit CANNOT be modified by the administrator.
- B . FortiGate limits the total number of simultaneous explicit web proxy users.
- C . FortiGate limits the number of simultaneous sessions per explicit web proxy user. The limit CAN be modified by the administrator.
- D . FortiGate limits the number of workstations that authenticate using the same web proxy user credentials. This limit CANNOT be modified by the administrator.
Refer to the exhibit, which shows the output of a debug command.
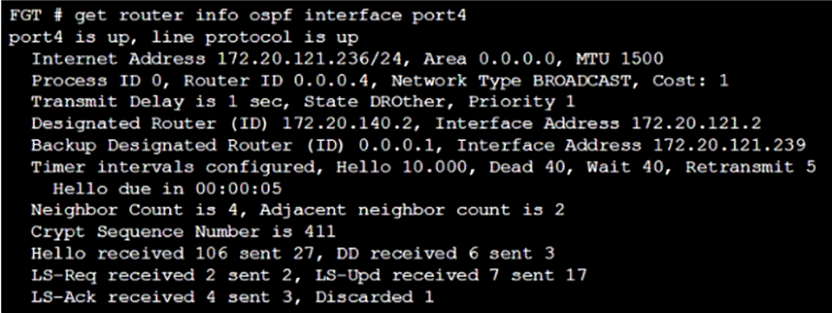
Which two statements about the output are true? (Choose two.)
- A . In the network connected to port 4, two OSPF routers are down.
- B . Based on the network type of port 4, OSPF hello packets will be sent to 224.0.0.5.
- C . Based on the network type of port 4, OSPF hello packets will be sent to 224.0.0.6.
- D . There are a total of 5 OSPF routers attached to the Port4 network segment.
What global configuration setting changes the behavior for content-inspected traffic while FortiGate is in system conserve mode?
- A . av-failopen
- B . mem-failopen
- C . utm-failopen
- D . ips-failopen
Refer to the exhibit, which contains partial output from an IKE real-time debug.
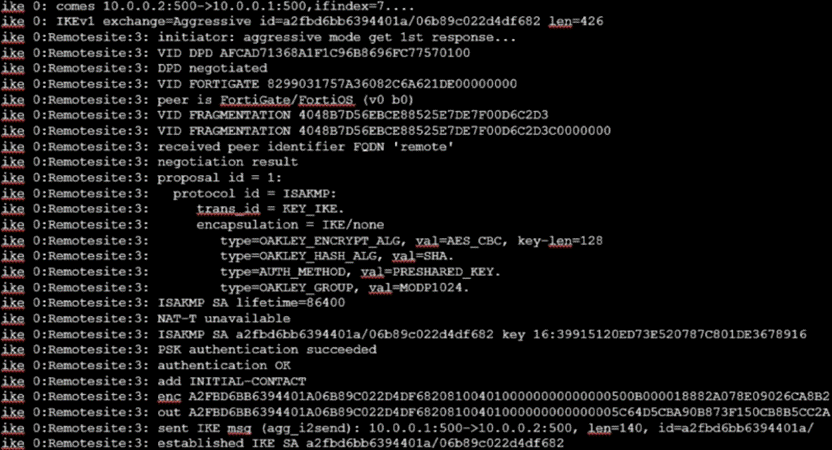
Which two statements about this debug output are correct? (Choose two.)
- A . The initiator provided remote as its IPsec peer ID.
- B . It shows a phase 2 negotiation.
- C . Perfect Forward Secrecy (PFS) is enabled in the configuration.
- D . The local gateway IP address is 10.0.0.1.
Refer to the exhibit, which contains a session table entry.
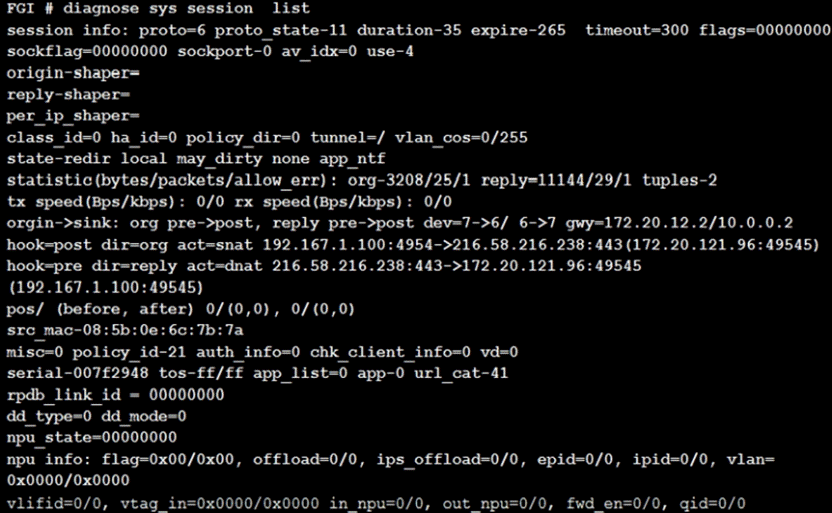
Which statement about FortiGate inspection of this session is true?
- A . FortiGate applied proxy-based inspection.
- B . FortiGate applied flow-based NGFW policy-based inspection.
- C . FortiGate applied flow-based inspection.
- D . FortiGate forwarded this session without any inspection.
An administrator must ensure that users cannot access sites containing malware and spyware, while also protecting them from phishing attempts.
What is the most resource-efficient method to block access to these sites?
- A . Enable antivirus profiles to scan all web traffic and block downloads from these malicious sites.
- B . Configure FortiGuard Web Filtering and block the categories malware, spyware, and phishing to prevent access to such sites.
- C . Create a custom IPS policy to monitor and block all outbound traffic related to malware, spyware, and phishing sites.
- D . Set up a DNS filter and block domains related to these categories to stop users from reaching malicious content.
View the exhibit, which contains the output of a debug command, and then answer the question below:
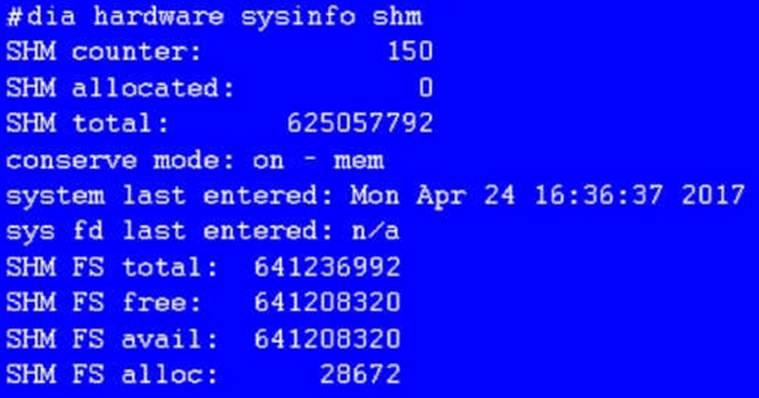
What statement is correct about this FortiGate?
- A . It is currently in system conserve mode because of high CPU usage.
- B . It is currently in FD conserve mode,
- C . It is currently in kernel conserve mode because of high memory usage
- D . It is currently in system conserve mode because of high memory usage