
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
What is the primary function of segmentation in network management?
- A . To encrypt data traffic across the network
- B . To connect multiple physical switches in a single logical interface
- C . To divide a network into smaller, isolated segments for enhanced security
- D . To enhance the decryption and encryption speeds within the network
An administrator has configured two FortiGate devices for an HA cluster. While testing HA failover, the administrator notices that some of the switches in the network continue to send traffic to the former primary device.
What can the administrator do to fix this problem?
- A . Configure remote link monitoring to detect an issue in the forwarding path.
- B . Configure set send-garp-on-failover enable under config system ha on both cluster members.
- C . Verify that the speed and duplex settings match between the FortiGate interfaces and the connected switch ports.
- D . Configure set link-failed-signal enable under config system ha on both cluster members.
Refer to the exhibit, which shows an enterprise network connected to an internet service provider.
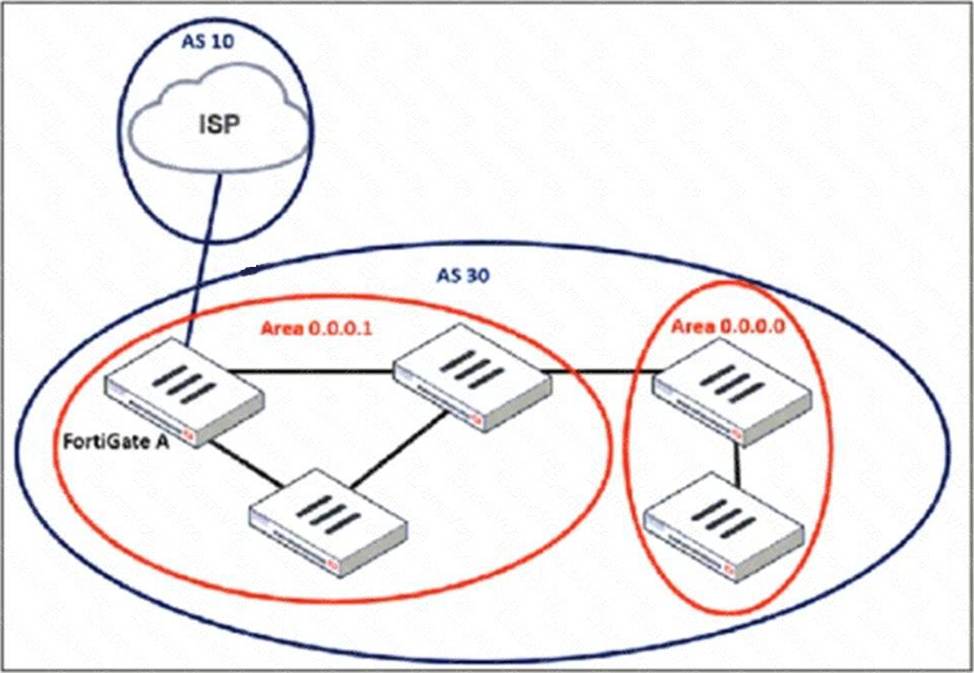
An administrator must configure a loopback as a BGP source to connect to the ISP.
Which two commands are required to establish the connection? (Choose two.)
- A . ebgp-enforce-multihop
- B . update-source
- C . ibgp-enforce-multihop
- D . recursive-next-hop
A B
Explanation:
When configuring aloopback interface as the BGP sourceforconnecting to an ISP, two important settings must be applied:
Refer to the exhibits.
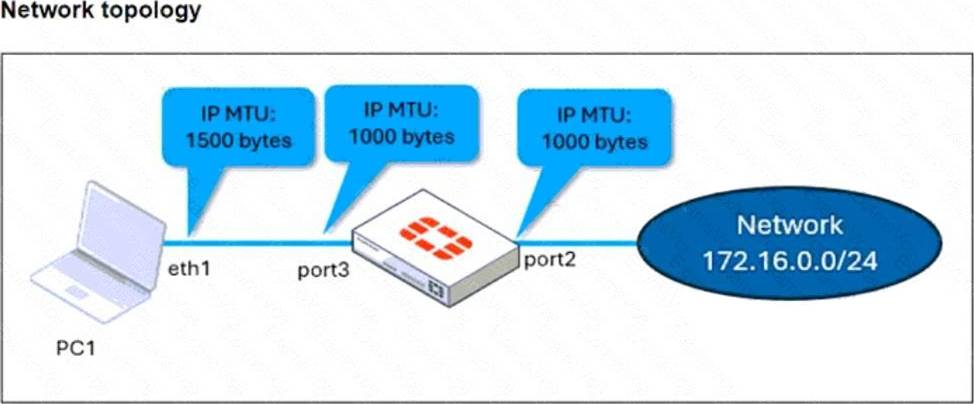
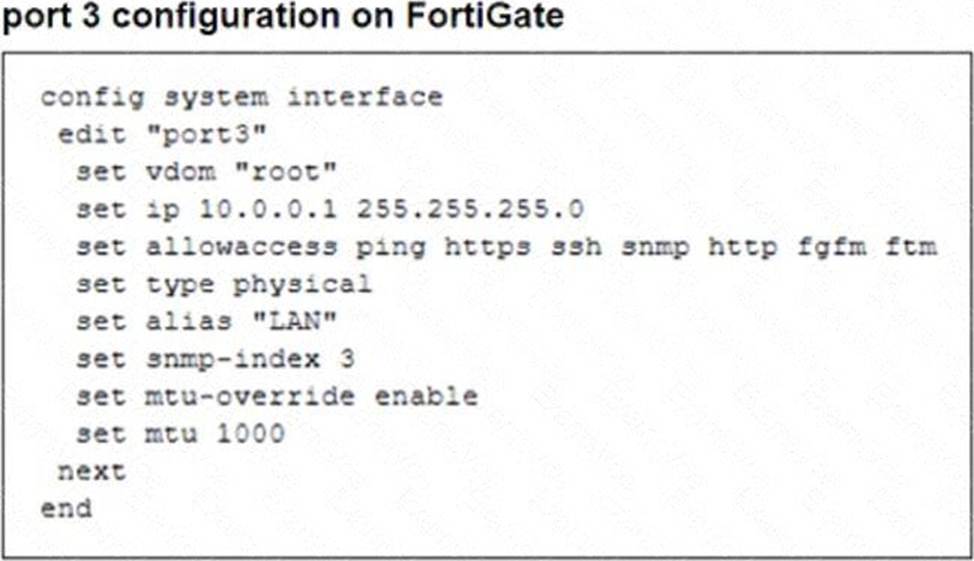
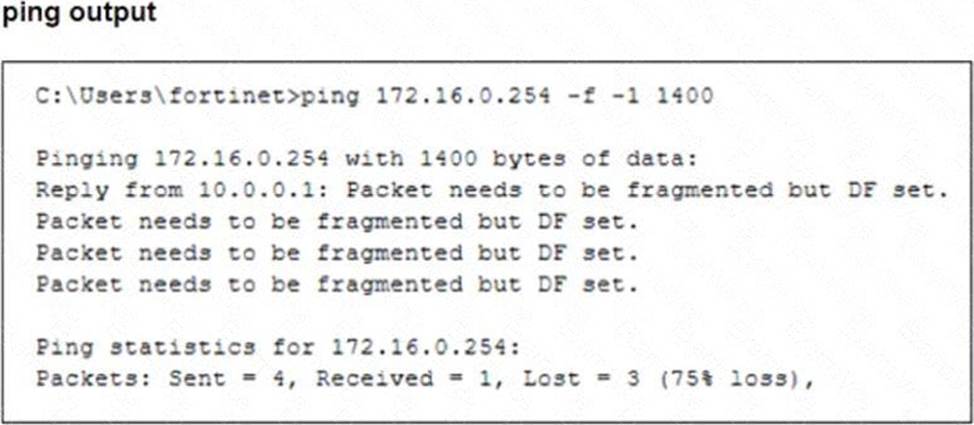
The configuration of a user’s Windows PC, which has a default MTU of 1500 bytes, along with FortiGate interfaces set to an MTU of1000bytes, and the results of PC1 pinging server172.16.0.254are shown.
Why is the user in Windows PC1 unable to ping server172.16.0.254and is seeing the message: Packet needs to be fragmented but DF set?
- A . Option ip.flags.mf must be set to enable on FortiGate. The user has to adjust the ping MTU to 1000 to succeed.
- B . Fragmented packets must be encrypted. To connect any application successfully, the user must install the Fortinet_CA certificate in the Microsoft Management Console.
- C . FortiGate honors the do not fragment bit and the packets are dropped. The user has to adjust the ping MTU to 972 to succeed.
- D . The user must trigger different traffic because path MTU discovery techniques do not recognize ICMP payloads.
C
Explanation:
The issue occurs because FortiGate enforces the "do not fragment" (DF) bit in the packet, and the packet size exceeds the MTU of the network path. When the Windows PC1 (with an MTU of 1500 bytes) attempts to send a 1400-byte packet, the FortiGate interface (with an MTU of 1000 bytes) needs to fragment it. However, since the DF bit is set, FortiGate drops the packet instead of fragmenting it.
To resolve this, the user should adjust the ping packet size to fit within the path MTU. In this case, reducing the packet size to972 bytes (1000 bytes MTU minus 28 bytes for the IP and ICMP headers) should allow successful transmission.
Refer to exhibit, which contains the output of a BGP debug command.
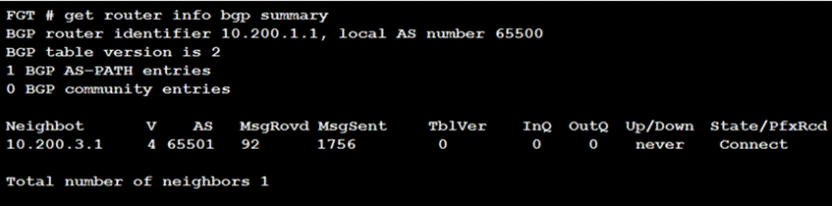
Which statement explains why the state of the 10.200.3.1 peer is Connect?
- A . The local router has received the BGP prefixes from the remote peer.
- B . The TCP session to 10.200.3.1 has not completed the three-way handshake.
- C . The local router is receiving BGP keepalives from the remote peer, but the local peer has not received the OpenConfirm yet.
- D . The local router is receiving the BGP keepalives from the peer, but it has not received a BGP prefix yet.
An administrator has configured two FortiGate devices for an HA cluster. While testing the HA failover, the administrator noticed that some of the switches in the network continue to send traffic to the former primary unit.
The administrator decides to enable the setting link-failed-signal to fix the problem.
Which statement is correct regarding this command?
- A . Forces the former primary device to shut down all its non-heartbeat interfaces for one second while the failover occurs.
- B . Sends an ARP packet to all connected devices, indicating that the HA virtual MAC address is reachable through a new master after a failover.
- C . Sends a link failed signal to all connected devices.
- D . Disables all the non-heartbeat interfaces in all the HA members for two seconds after a failover.
Which statements regarding banned words are correct? (Choose two.)
- A . Content is automatically blocked if a single instance of a banned word appears.
- B . The FortiGate updates banned words on a periodic basis.
- C . The FortiGate can scan web pages and email messages for instances of banned words.
- D . Banned words can be expressed as simple text, wildcards and regular expressions.
Refer to the exhibit, which shows partial outputs from two routing debug commands.
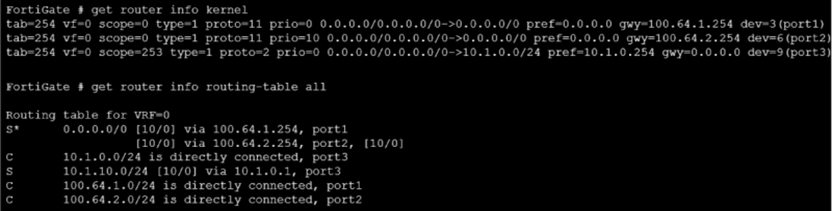
Which change must an administrator make on FortiGate to route web traffic from internal users to the internet, using ECMP?
- A . Set the priority of the static default route using port1 to 10.
- B . Set the priority of the static default route using port2 to 1.
- C . Set preserve-session-route to enable.
- D . Set snat-route-change to enable.
Refer to the exhibit, which shows partial outputs from two routing debug commands.
Which change must an administrator make on FortiGate to route web traffic from internal users to the internet, using ECMP?
- A . Set the priority of the static default route using port1 to 10.
- B . Set the priority of the static default route using port2 to 1.
- C . Set preserve-session-route to enable.
- D . Set snat-route-change to enable.
Refer to the exhibit, whi ch shows a command out put.
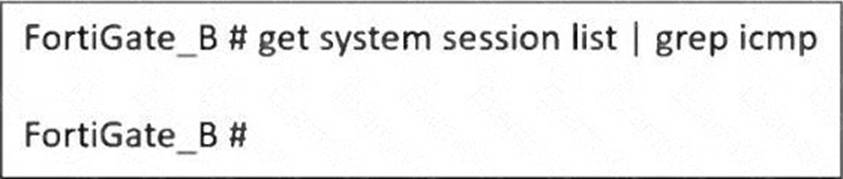
FortiGate_A and FortiGate_B are members of an FGSP cluster in an enterprise network.
While testing the cluster using the ping command, the administrator monitors packet loss and found that the session output on FortiGate_B is as shown in the exhibit.
What could be the cause of this output on FortiGate_B?
- A . The session synchronization is encrypted.
- B . session-pickup-connectionless is set to disable on FortiGate_B.
- C . FortiGate_B is configured in passive mode.
- D . FortiGate_A and FortiGate_B have the same standalone-group-id value.
B
Explanation:
TheFortinet FGSP (FortiGate Session Life Support Protocol) clusterallows session synchronization betweentwo FortiGate devicesto provide seamless failover. However,ICMP (ping) is a connectionless protocol, and by default, FortiGate does not synchronize connectionless sessions unless explicitly enabled.
In the exhibit:
# The commandget system session list | grep icmponFortiGate_Breturnsno output, meaning that ICMP sessions arenot being synchronizedfrom FortiGate_A.
# Ifsession-pickup-connectionlessis disabled,FortiGate_B will not receive ICMP sessions, causingpacket lossduring failover.