EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
A certified ethical hacker is conducting a Whois footprinting activity on a specific domain. The individual is leveraging various tools such as Batch IP Converter and Whols Analyzer Pro to retrieve vital details but is unable to gather complete Whois information from the registrar for a particular set of data. As the hacker, what might be the probable data model being utilized by the domain’s registrar for storing and looking up
Who is information?
- A . Thick Whois model with a malfunctioning server
- B . Thick Whois model working correctly
- C . Thin Whois model with a malfunctioning server
- D . Thin Whois model working correctly
jane invites her friends Alice and John over for a LAN party. Alice and John access Jane’s wireless network without a password. However. Jane has a long, complex password on her router.
What attack has likely occurred?
- A . Wireless sniffing
- B . Piggybacking
- C . Evil twin
- D . Wardriving
Gerard, a disgruntled ex-employee of Sunglass IT Solutions, targets this organization to perform sophisticated attacks and bring down its reputation in the market. To launch the attacks process, he performed DNS footprinting to gather information about ONS servers and to identify the hosts connected in the target network. He used an automated tool that can retrieve information about DNS zone data including DNS domain names, computer names. IP addresses. DNS records, and network Who is records. He further exploited this information to launch other sophisticated attacks.
What is the tool employed by Gerard in the above scenario?
- A . Knative
- B . zANTI
- C . Towelroot
- D . Bluto
Fred is the network administrator for his company. Fred is testing an internal switch.
From an external IP address, Fred wants to try and trick this switch into thinking it already has established a session with his computer.
How can Fred accomplish this?
- A . Fred can accomplish this by sending an IP packet with the RST/SIN bit and the source address of his computer.
- B . He can send an IP packet with the SYN bit and the source address of his computer.
- C . Fred can send an IP packet with the ACK bit set to zero and the source address of the switch.
- D . Fred can send an IP packet to the switch with the ACK bit and the source address of his machine.
Why would you consider sending an email to an address that you know does not exist within the company you are performing a Penetration Test for?
- A . To determine who is the holder of the root account
- B . To perform a DoS
- C . To create needless SPAM
- D . To illicit a response back that will reveal information about email servers and how they treat undeliverable mail
- E . To test for virus protection
Which type of security feature stops vehicles from crashing through the doors of a building?
- A . Bollards
- B . Receptionist
- C . Mantrap
- D . Turnstile
Which Metasploit Framework tool can help penetration tester for evading Anti-virus Systems?
- A . msfpayload
- B . msfcli
- C . msfd
- D . msfencode
which of the following Bluetooth hacking techniques refers to the theft of information from a wireless device through Bluetooth?
- A . Bluesmacking
- B . Bluebugging
- C . Bluejacking
- D . Bluesnarfing
Hackers often raise the trust level of a phishing message by modeling the email to look similar to the internal email used by the target company. This includes using logos, formatting, and names of the target company. The phishing message will often use the name of the company CEO, President, or Managers.
The time a hacker spends performing research to locate this information about a company is known as?
- A . Exploration
- B . Investigation
- C . Reconnaissance
- D . Enumeration
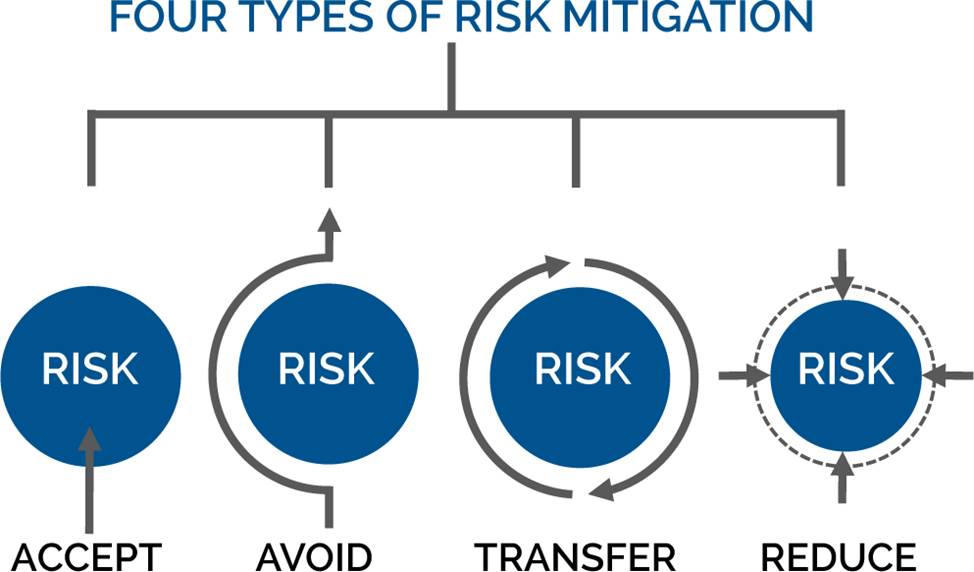
Suppose your company has just passed a security risk assessment exercise. The results display that the risk of the breach in the main company application is 50%. Security staff has taken some measures and implemented the necessary controls. After that, another security risk assessment was performed showing that risk has decreased to 10%. The risk threshold for the application is 20%.
Which of the following risk decisions will be the best for the project in terms of its successful continuation with the most business profit?
- A . Accept the risk
- B . Introduce more controls to bring risk to 0%
- C . Mitigate the risk
- D . Avoid the risk