
EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
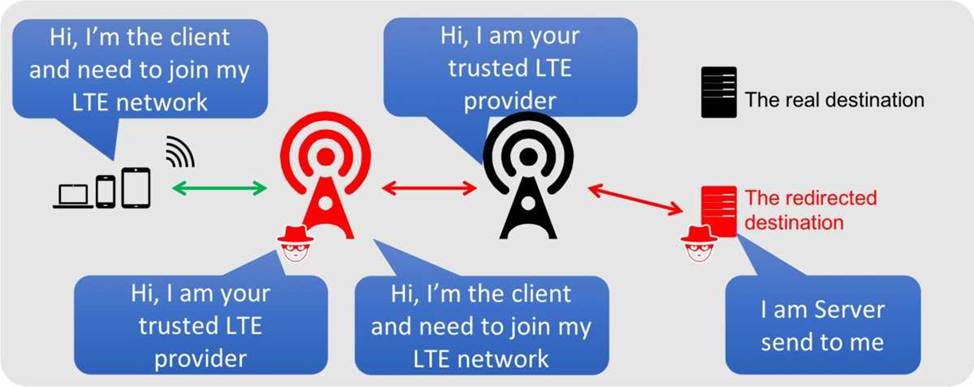
Bobby, an attacker, targeted a user and decided to hijack and intercept all their wireless communications. He installed a fake communication tower between two authentic endpoints to mislead the victim. Bobby used this virtual tower to interrupt the data transmission between the user and real tower, attempting to hijack an active session, upon receiving the users request. Bobby manipulated the traffic with the virtual tower and redirected the victim to a malicious website.
What is the attack performed by Bobby in the above scenario?
- A . Wardriving
- B . KRACK attack
- C . jamming signal attack
- D . aLTEr attack
A company’s policy requires employees to perform file transfers using protocols which encrypt traffic. You suspect some employees are still performing file transfers using unencrypted protocols because the employees do not like changes. You have positioned a network sniffer to capture traffic from the laptops used by employees in the data ingest department.
Using Wireshark to examine the captured traffic, which command can be used as display filter to find unencrypted file transfers?
- A . tcp.port = = 21
- B . tcp.port = 23
- C . tcp.port = = 21 | | tcp.port = =22
- D . tcp.port ! = 21
Which of the following commands checks for valid users on an SMTP server?
- A . RCPT
- B . CHK
- C . VRFY
- D . EXPN
What is the purpose of DNS AAAA record?
- A . Authorization, Authentication and Auditing record
- B . Address prefix record
- C . Address database record
- D . IPv6 address resolution record
If a tester is attempting to ping a target that exists but receives no response or a response that states the destination is unreachable, ICMP may be disabled and the network may be using TCP.
Which other option could the tester use to get a response from a host using TCP?
- A . Traceroute
- B . Hping
- C . TCP ping
- D . Broadcast ping
You are a penetration tester and are about to perform a scan on a specific server. The agreement that you signed with the client contains the following specific condition for the scan: “The attacker must scan every port on the server several times using a set of spoofed sources IP addresses. ” Suppose that you are using Nmap to perform this scan.
What flag will you use to satisfy this requirement?
- A . The -A flag
- B . The -g flag
- C . The -f flag
- D . The -D flag
When conducting a penetration test, it is crucial to use all means to get all available information about the target network. One of the ways to do that is by sniffing the network.
Which of the following cannot be performed by the passive network sniffing?
- A . Identifying operating systems, services, protocols and devices
- B . Modifying and replaying captured network traffic
- C . Collecting unencrypted information about usernames and passwords
- D . Capturing a network traffic for further analysis
Which of the following are well known password-cracking programs?
- A . L0phtcrack
- B . NetCat
- C . Jack the Ripper
- D . Netbus
- E . John the Ripper
Which of the following are well known password-cracking programs?
- A . L0phtcrack
- B . NetCat
- C . Jack the Ripper
- D . Netbus
- E . John the Ripper
Which of the following are well known password-cracking programs?
- A . L0phtcrack
- B . NetCat
- C . Jack the Ripper
- D . Netbus
- E . John the Ripper