
DELL EMC D-CSF-SC-01 Practice Exams
Last updated on Nov 16,2026- Exam Code: D-CSF-SC-01
- Exam Name: Dell NIST Cybersecurity Framework 2.0
- Certification Provider: DELL EMC
- Latest update: Nov 16,2026
What is the primary focus of the BIA?
- A . Prevents threats to the environment
- B . Determines criticality of assets to the business
- C . Identifies roles and responsibilities for asset recovery
- D . Maintains controls for recovery
The CSIRT team is following the existing recovery plans on non-production systems in a PRE-BREACH scenario.
This action is being executed in which function?
- A . Protect
- B . Recover
- C . Identify
- D . Respond
What defines who is accountable for contacting operational teams, managers, and others affected by a localized, safety critical event?
- A . Asset Management Plan
- B . Business Impact Analysis
- C . Business Continuity Plan
- D . Incident Response Plan
Refer to the exhibit.
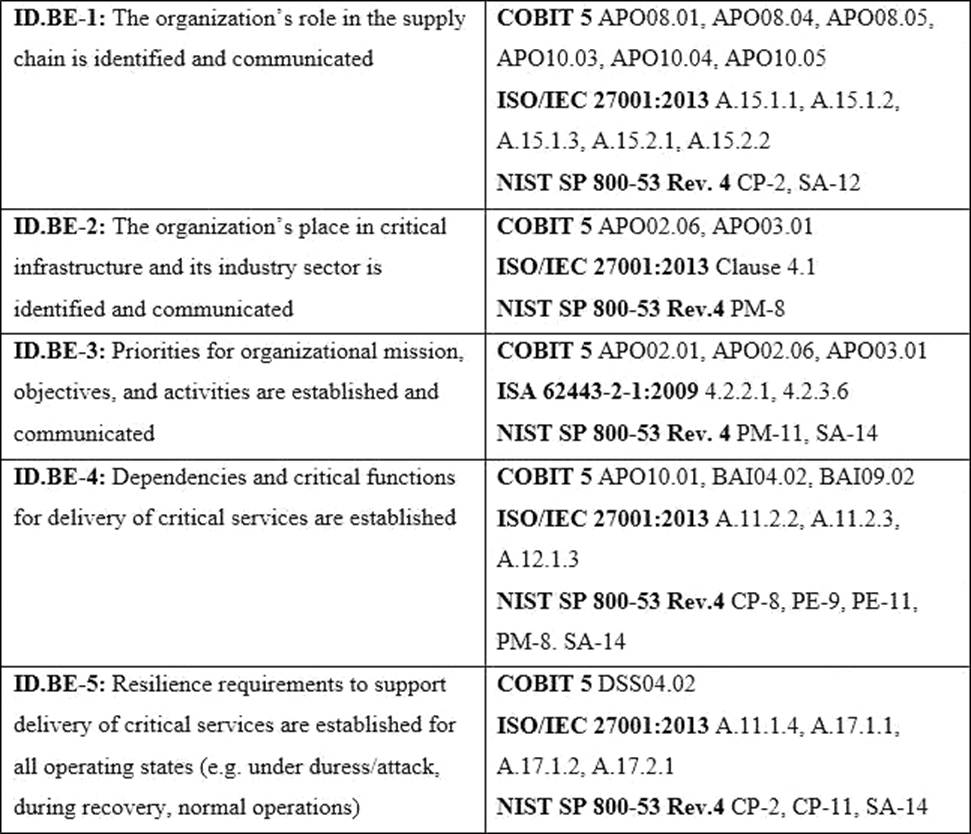
What type of item appears in the second column of the table?
- A . Subcategory
- B . Informative Reference
- C . Function
- D . Tier
An IT security engineer grants an auditor access to a conference room and provides temporary wireless access to them to conduct an analysis for the company’s annual financial report.
Which category addresses the ability to prevent access to the Internet while being able to browse a designated set of folders on the LAN?
- A . PR.AC
- B . PR.IP
- C . ID.AM
- D . RC.CO
Your organization has been breached. The attacker has sent an email demanding $100,000 in cryptocurrency in exchange for not dumping all your customer information onto the dark web. Following the RACI Matrix model outlined in your IRP, you have informed all parties, contained the breach, and eradicated the threat.
What needs to be done next?
- A . Update response strategies
- B . Performs forensics
- C . Investigate notifications from detection systems
- D . Categorize incidents consistent with Response Plan
What determines the technical controls used to restrict access to USB devices and help prevent their use within a company?
- A . Block use of the USB devices for all employees
- B . Written security policy prohibiting the use of the USB devices
- C . Acceptable use policy in the employee HR on-boarding training
- D . Detect use of the USB devices and report users
What is a result of an incomplete organizational asset identification process?
- A . Vendors will not receive payment from the organization
- B . Purchases will be delayed by the organization
- C . Risk will be introduced into the organization
- D . System disruptions will have less impact on the organization
The ___ core function in the NIST Cybersecurity Framework focuses on identifying cybersecurity events in a timely manner.
- A . Identify
- B . Detect
- C . Recover
- D . Respond
What term refers to a partially equipped, environmentally conditioned work space used to relocate operations in the event of a significant disruption?
- A . Hot site
- B . Warm site
- C . Mirror site
- D . Secondary site