
DELL EMC D-CSF-SC-01 Practice Exams
Last updated on Nov 16,2026- Exam Code: D-CSF-SC-01
- Exam Name: Dell NIST Cybersecurity Framework 2.0
- Certification Provider: DELL EMC
- Latest update: Nov 16,2026
What must be included in the CMDB?
- A . Inventory of uninstalled software
- B . Software End User Licensing Agreements
- C . Dependencies of installed components
- D . Known vulnerabilities of installed software
Rank order the relative severity of impact to an organization of each plan, where “1” signifies the most impact and “4” signifies the least impact.
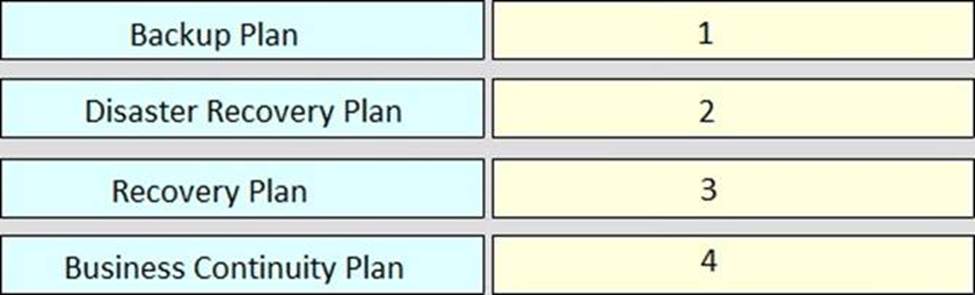
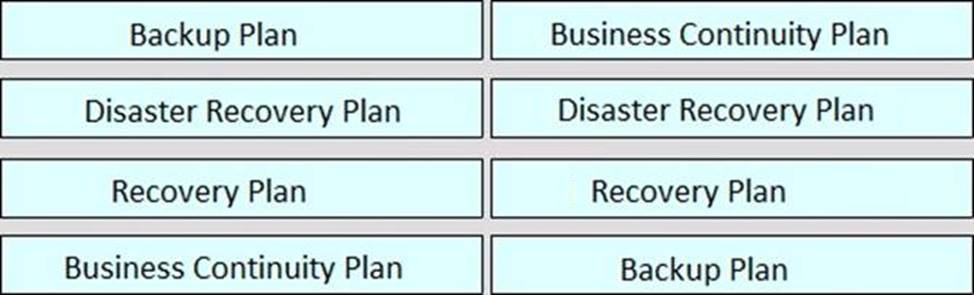
What process is used to identify an organization’s physical, digital, and human resource, as required in their Business Impact Analysis?
- A . Risk Management Strategy
- B . Risk Assessment
- C . Risk Treatment
- D . Asset Inventory
The ___ function of the NIST Cybersecurity Framework ensures timely identification of cybersecurity events.
- A . Respond
- B . Identify
- C . Detect
- D . Recover
What common process conducted by organizations when protecting digital assets is outside the scope of the NIST Cybersecurity Framework?
- A . Recover
- B . Identify
- C . Protect
- D . Investigate
What are the four tiers of integration within the NIST Cybersecurity Framework?
- A . Selective, Repeatable, Partial, and Adaptive
- B . Partial, Risk Informed, Repeatable, and Adaptive
- C . Corrective, Risk Informed, Repeatable, and Adaptive
- D . Risk Informed, Selective, Repeatable, and Partial
A security engineer is responsible for monitoring company software, firmware, system OS, and applications for known vulnerabilities.
How should they stay current on exploits and information security?
- A . Implement security awareness training
- B . Update company policies and procedures
- C . Revise vulnerability management plan
- D . Subscribe to security mailing lists
Consider the following situation:
– A complete service outage has occurred, affecting critical services
– Users are unable to perform their tasks
– Customers are unable to conduct business
– Financial impact is beyond the highest allowed threshold
What is the correct classification level for this situation?
- A . Safety critical
- B . Mission critical
- C . Business critical
- D . High impact
The COBIT 2019 framework provides guidance on establishing governance structures to ensure that ___ align with the organization’s strategic goals.
- A . Cybersecurity controls
- B . Operational procedures
- C . Financial audits
- D . Employee training programs
The ___ profile in the NIST Cybersecurity Framework represents the desired cybersecurity outcomes aligned with the organization’s risk tolerance.
- A . Current
- B . Target
- C . Risk
- D . Maturity