
CompTIA SY0-701 Practice Exams
Last updated on Nov 16,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Two companies are in the process of merging. The companies need to decide how to standardize their information security programs.
Which of the following would best align the security programs?
- A . Shared deployment of CIS baselines
- B . Joint cybersecurity best practices
- C . Both companies following the same CSF
- D . Assessment of controls in a vulnerability report
C
Explanation:
A Cybersecurity Framework (CSF) provides a structured approach to standardizing and aligning security programs across different organizations. By both companies adopting the same CSF, they can ensure that their security measures, policies, and practices are consistent, which is essential during a merger when aligning two different security programs.
Reference =
CompTIA Security+ SY0-701 Course Content: The course discusses the importance of adopting standardized cybersecurity frameworks (CSF) for aligning security programs during mergers and acquisitions.
A security analyst is reviewing the following logs:
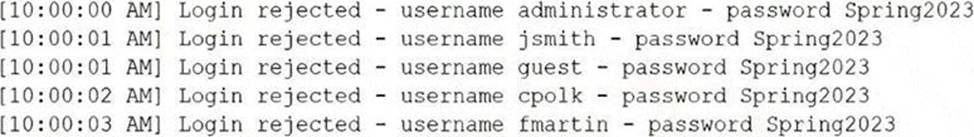
Which of the following attacks is most likely occurring?
- A . Password spraying
- B . Account forgery
- C . Pass-t he-hash
- D . Brute-force
A
Explanation:
Password spraying is a type of brute force attack that tries common passwords across several accounts to find a match. It is a mass trial-and-error approach that can bypass account lockout protocols. It can give hackers access to personal or business accounts and information. It is not a targeted attack, but a high-volume attack tactic that uses a dictionary or a list of popular or weak passwords12.
The logs show that the attacker is using the same password ("password123") to attempt to log in to different accounts ("admin", "user1", "user2", etc.) on the same web server. This is a typical pattern of password spraying, as the attacker is hoping that at least one of the accounts has a weak password that matches the one they are trying. The attacker is also using a tool called Hydra, which is one of the most popular brute force tools, often used in cracking passwords for network authentication3. Account forgery is not the correct answer, because it involves creating fake accounts or credentials to impersonate legitimate users or entities. There is no evidence of account forgery in the logs, as the attacker is not creating any new accounts or using forged credentials.
Pass-the-hash is not the correct answer, because it involves stealing a hashed user credential and using it to create a new authenticated session on the same network. Pass-the-hash does not require the attacker to know or crack the password, as they use the stored version of the password to initiate a new session4. The logs show that the attacker is using plain text passwords, not hashes, to try to log in to the web server.
Brute-force is not the correct answer, because it is a broader term that encompasses different types of attacks that involve trying different variations of symbols or words until the correct password is found. Password spraying is a specific type of brute force attack that uses a single common password against multiple accounts5. The logs show that the attacker is using password spraying, not brute force in general, to try to gain access to the web server.
Reference = 1: Password spraying: An overview of password spraying attacks … – Norton, 2: Security: Credential Stuffing vs. Password
Spraying – Baeldung, 3: Brute Force Attack: A definition + 6 types to know | Norton, 4: What is a Pass-the-Hash Attack? – CrowdStrike, 5: What is a Brute Force Attack? | Definition, Types & How It Works – Fortinet
A user needs to complete training at https://comptiatraining.com. After manually entering the URL, the user sees that the accessed website is noticeably different from the standard company website.
Which of the following is the most likely explanation for the difference?
- A . Cross-site scripting
- B . Pretexting
- C . Typosquatting
- D . Vishing
C
Explanation:
Typosquatting (also known as URL hijacking) is a type of attack where cybercriminals register domain names similar to legitimate sites but with slight misspellings (e.g., comptiatraning.com instead of comptiatraining.com). Attackers use these fake sites to steal credentials or distribute malware. Since the user manually entered the URL and reached an unexpected website, this strongly indicates a typosquatting attack.
Reference: CompTIA Security+ SY0-701 Official Study Guide, Threats, Vulnerabilities, and Mitigations domain.
Employees in the research and development business unit receive extensive training to ensure they understand how to best protect company data.
Which of the following is the type of data these employees are most likely to use in day-to-day work activities?
- A . Encrypted
- B . Intellectual property
- C . Critical
- D . Data in transit
B
Explanation:
Intellectual property is a type of data that consists of ideas, inventions, designs, or other creative works that have commercial value and are protected by law. Employees in the research and development business unit are most likely to use intellectual property data in their day-to-day work activities, as they are involved in creating new products or services for the company. Intellectual property data needs to be protected from unauthorized use, disclosure, or theft, as it can give the company a competitive advantage in the market. Therefore, these employees receive extensive training to ensure they understand how to best protect this type of data.
Reference = CompTIA Security+ SY0-701 Certification Study Guide, page 90; Professor Messer’s CompTIA SY0-701 Security+ Training Course, video 1.2 – Security Concepts, 7:57 – 9:03.
An attacker posing as the Chief Executive Officer calls an employee and instructs the employee to buy gift cards.
Which of the following techniques is the attacker using?
- A . Smishing
- B . Disinformation
- C . Impersonating
- D . Whaling
D
Explanation:
Whaling is a type of phishing attack that targets high-profile individuals, such as executives, celebrities, or politicians. The attacker impersonates someone with authority or influence and tries to trick the victim into performing an action, such as transferring money, revealing sensitive information, or clicking on a malicious link. Whaling is also called CEO fraud or business email compromise2.
Reference: CompTIA Security+ Study Guide: Exam SY0-701, 9th Edition, Chapter 3, page 97.
An employee in the accounting department receives an email containing a demand for payment tot services performed by a vendor However, the vendor is not in the vendor management database.
Which of the following in this scenario an example of?
- A . Pretexting
- B . Impersonation
- C . Ransomware
- D . Invoice scam
D
Explanation:
The scenario describes an instance where an employee receives a fraudulent invoice from a vendor that is not recognized in the company’s vendor management system. This is a classic example of an invoice scam, where attackers attempt to trick organizations into making payments for fake or non-existent services. These scams often rely on social engineering tactics to bypass financial controls.
Reference = CompTIA Security+ SY0-701 study materials, particularly in the context of social engineering attacks and common scams.
A security engineer is working to address the growing risks that shadow IT services are introducing to the organization. The organization has taken a cloud-first approach end does not have an on-premises IT infrastructure.
Which of the following would best secure the organization?
- A . Upgrading to a next-generation firewall
- B . Deploying an appropriate in-line CASB solution
- C . Conducting user training on software policies
- D . Configuring double key encryption in SaaS platforms
B
Explanation:
A Cloud Access Security Broker (CASB) solution is the most suitable option for securing an organization that has adopted a cloud-first strategy and does not have an on-premises IT infrastructure. CASBs provide visibility and control over shadow IT services, enforce security policies, and protect data across cloud services.
Reference = CompTIA Security+ SY0-701 study materials, particularly in the domain of cloud security and managing risks associated with shadow IT.
Which of the following phases of the incident response process attempts to minimize disruption?
- A . Recovery
- B . Containment
- C . Preparation
- D . Analysis
B
Explanation:
Containment is the phase where an organization attempts to minimize the damage caused by a security incident. This may involve isolating affected systems, blocking malicious traffic, or temporarily shutting down compromised services to prevent further impact.
Recovery (A) focuses on restoring normal operations after an incident. Preparation (C) involves planning and readiness before an incident occurs. Analysis (D) involves investigating the root cause and assessing the damage.
Reference: CompTIA Security+ SY0-701 Official Study Guide, Security Operations domain.
A technician wants to improve the situational and environmental awareness of existing users as they transition from remote to in-office work.
Which of the following is the best option?
- A . Send out periodic security reminders.
- B . Update the content of new hire documentation.
- C . Modify the content of recurring training.
- D . Implement a phishing campaign
C
Explanation:
Recurring training is a type of security awareness training that is conducted periodically to refresh and update the knowledge and skills of the users. Recurring training can help improve the situational and environmental awareness of existing users as they transition from remote to in-office work, as it can cover the latest threats, best practices, and policies that are relevant to their work environment. Modifying the content of recurring training can ensure that the users are aware of the current security landscape and the expectations of their roles.
Reference = CompTIA Security+ Study Guide with over 500 Practice Test Questions: Exam SY0-701, 9th Edition, Chapter 5, page 232. CompTIA
Security+ (SY0-701) Certification Exam Objectives, Domain 5.1, page 18.
A company wants to improve the availability of its application with a solution that requires minimal effort in the event a server needs to be replaced or added.
Which of the following would be the best solution to meet these objectives?
- A . Load balancing
- B . Fault tolerance
- C . Proxy servers
- D . Replication
A
Explanation:
Detailed Load balancing improves application availability by distributing traffic across multiple servers. If one server fails, traffic is automatically routed to other available servers with minimal intervention.
Reference: CompTIA Security+ SY0-701 Study Guide, Domain 3: Security Architecture, Section: "High Availability Solutions".