
Cisco 300-710 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-710
- Exam Name: Securing Networks with Cisco Firepower (SNCF)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which Cisco FMC report gives the analyst information about the ports and protocols that are related to the configured sensitive network for analysis?
- A . Malware Report
- B . Host Report
- C . Firepower Report
- D . Network Report
Refer to the exhibit.
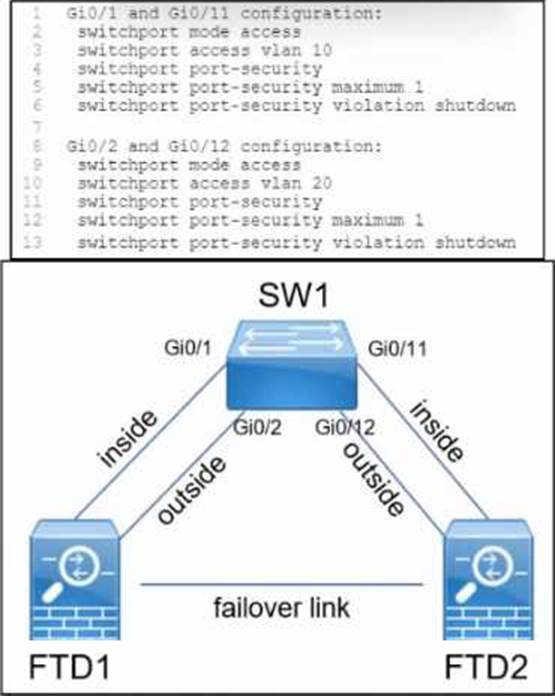
A company is deploying a pair of Cisco Secure Firewall Threat defense devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link.
What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?
- A . Disable port security on the switch interfaces connected to FTD1 and FTD2.
- B . Set maximum secured addresses to two on the switch interfaces on FTD1 and FTD2.
- C . Connect and configure a stateful link and thon deploy the changes.
- D . Configure the spanning-tree PortFasI feature on SW1 and FTD2
A network administrator needs to create a policy on Cisco Firepower to fast-path traffic to avoid
Layer 7 inspection. The rate at which traffic is inspected must be optimized.
What must be done to achieve this goal?
- A . Enable lhe FXOS for multi-instance.
- B . Configure a prefilter policy.
- C . Configure modular policy framework.
- D . Disable TCP inspection.
What is a behavior of a Cisco FMC database purge?
- A . User login and history data are removed from the database if the User Activity check box is selected.
- B . Data can be recovered from the device.
- C . The appropriate process is restarted.
- D . The specified data is removed from Cisco FMC and kept for two weeks.
What is the result of configuring an inline set to propagate link state?
- A . It causes all interfaces in the set to become active if one is active.
- B . It reduces the failover time between active and standby units.
- C . It allows interfaces to emulate a passive interface.
- D . It permits the monitoring of all inbound and outbound traffic through the device.
An engineer is troubleshooting application failures through a FTD deployment. While using the FMC CLI. it has been determined that the traffic in question is not matching the desired policy.
What should be done to correct this?
- A . Use the system support firewall-engine-debug command to determine which rules the traffic matching and modify the rule accordingly
- B . Use the system support application-identification-debug command to determine which rules the traffic matching and modify the rule accordingly
- C . Use the system support firewall-engine-dump-user-f density-data command to change the policy and allow the application through the firewall.
- D . Use the system support network-options command to fine tune the policy.
Which two conditions must be met to enable high availability between two Cisco FTD devices? (Choose two.)
- A . same flash memory size
- B . same NTP configuration
- C . same DHCP/PPoE configuration
- D . same host name
- E . same number of interfaces
A cisco Secure firewall Threat Defence device is configured in inline IPS mode to inspect all traffic that passes through the interfaces in the inline set.
Which setting in the inline set configuration must be connected to allow traffic to pass through uninterrupted when VDB updates are being applied?
- A . Propagate Link State
- B . Short Fall Open
- C . Strict TCP Enforcement
- D . Tap Mode
An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address.
How must the engineer deploy the device to meet this requirement?
- A . Deploy the device in routed mode and allow DHCP traffic in the access control policies.
- B . Deploy the device in routed made aid enable the DHCP Relay feature.
- C . Deploy the device in transparent mode and allow DHCP traffic in the access control policies
- D . Deploy the device in transparent mode and enable the DHCP Server feature.
A network security engineer must replace a faulty Cisco FTD device in a high availability pair.
Which action must be taken while replacing the faulty unit?
- A . Shut down the Cisco FMC before powering up the replacement unit.
- B . Ensure that the faulty Cisco FTD device remains registered to the Cisco FMC.
- C . Unregister the faulty Cisco FTD device from the Cisco FMC
- D . Shut down the active Cisco FTD device before powering up the replacement unit.