
Cisco 300-710 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-710
- Exam Name: Securing Networks with Cisco Firepower (SNCF)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which action should be taken after editing an object that is used inside an access control policy?
- A . Delete the existing object in use.
- B . Refresh the Cisco FMC GUI for the access control policy.
- C . Redeploy the updated configuration.
- D . Create another rule using a different object name.
Which protocol establishes network redundancy in a switched Firepower device deployment?
- A . STP
- B . HSRP
- C . GLBP
- D . VRRP
A network administrator is configuring a site-to-site IPsec VPN to a router sitting behind a Cisco FTD. The administrator has configured an access policy to allow traffic to this device on UDP 500, 4500, and ESP VPN traffic is not working.
Which action resolves this issue?
- A . Set the allow action in the access policy to trust.
- B . Enable IPsec inspection on the access policy.
- C . Modify the NAT policy to use the interface PAT.
- D . Change the access policy to allow all ports.
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface.
What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
- A . The destination MAC address is optional if a VLAN ID value is entered
- B . Only the UDP packet type is supported
- C . The output format option for the packet logs unavailable
- D . The VLAN ID and destination MAC address are optional
A mid-sized company is experiencing higher network bandwidth utilization due to a recent acquisition The network operations team is asked to scale up their one Cisco FTD appliance deployment to higher capacities due to the increased network bandwidth.
Which design option should be used to accomplish this goal?
- A . Deploy multiple Cisco FTD appliances in firewall clustering mode to increase performance.
- B . Deploy multiple Cisco FTD appliances using VPN load-balancing to scale performance.
- C . Deploy multiple Cisco FTD HA pairs to increase performance
- D . Deploy multiple Cisco FTD HA pairs in clustering mode to increase performance
What is the advantage of having Cisco Firepower devices send events to Cisco Threat Response via the security services exchange portal directly as opposed to using syslog?
- A . All types of Cisco Firepower devices are supported.
- B . An on-premises proxy server does not need to be set up and maintained.
- C . Cisco Firepower devices do not need to be connected to the Internet.
- D . Supports all devices that are running supported versions of Cisco Firepower.
Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session.
Which action must the engineer take to resolve the issue?
- A . Forward the captured data lo an FTP server
- B . Increase the amount of RAM allocated for the capture.
- C . Provide a file name to save the data.
- D . Ensure that the allocated memory is sufficient.
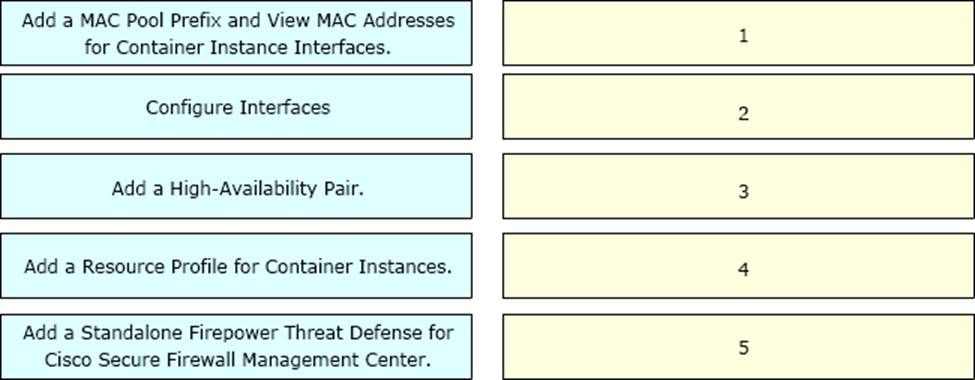
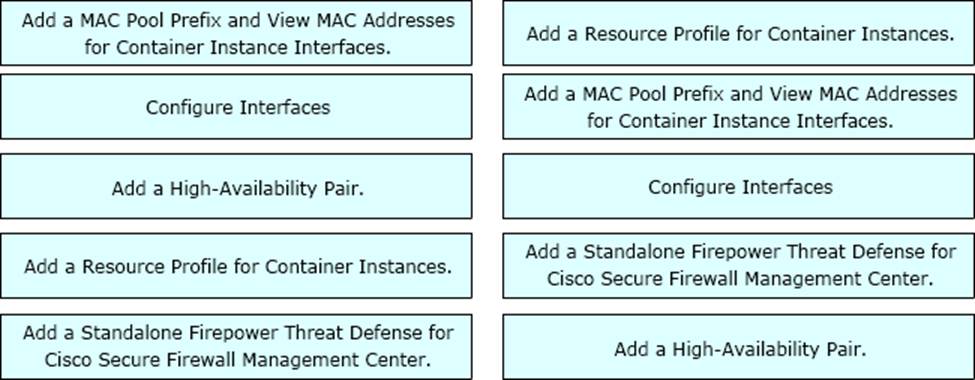
DRAG DROP
A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability.
Drag and drop me actions from the left into sequence on the right far this configuration.
After using Firepower for some time and learning about how it interacts with the network, an administrator is trying to correlate malicious activity with a user.
Which widget should be configured to provide this visibility on the Cisco Firepower dashboards?
- A . Custom Analysis
- B . Current Status
- C . Current Sessions
- D . Correlation Events
Which two packet captures does the FTD LINA engine support? (Choose two.)
- A . Layer 7 network ID
- B . source IP
- C . application ID
- D . dynamic firewall importing
- E . protocol