
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
An engineer creates a default static route on a router with a hop of 10.1.1.1. On inspection, the engineer finds the router has two VRFs, Red and Blue. The next hop is valid for both VRFs and exists in each assigned VRF.
Which configuration achieves connectivity?
- A . ip route vrf BLUE 0.0.0.0 255.255.255.255 10.1.1.1
ip route vrf RED 0.0.0.0 255.255.255.255 10.1.1.1 - B . ip route vrf Red 0.0.0.0 0.0.0.0 10.1.1.1
ip route vrf Blue 0.0.0.0 0.0.0.0 10.1.1.1 - C . ip route vrf 0.0.0.0 0.0.0.0 10.1.1.1
- D . ip route vrf Red 0.0.0.0 255.255.255.255 10.1.1.1
ip route vrf Blue 0.0.0.0 255.255.255.255 10.1.1.1
Refer to the exhibit.
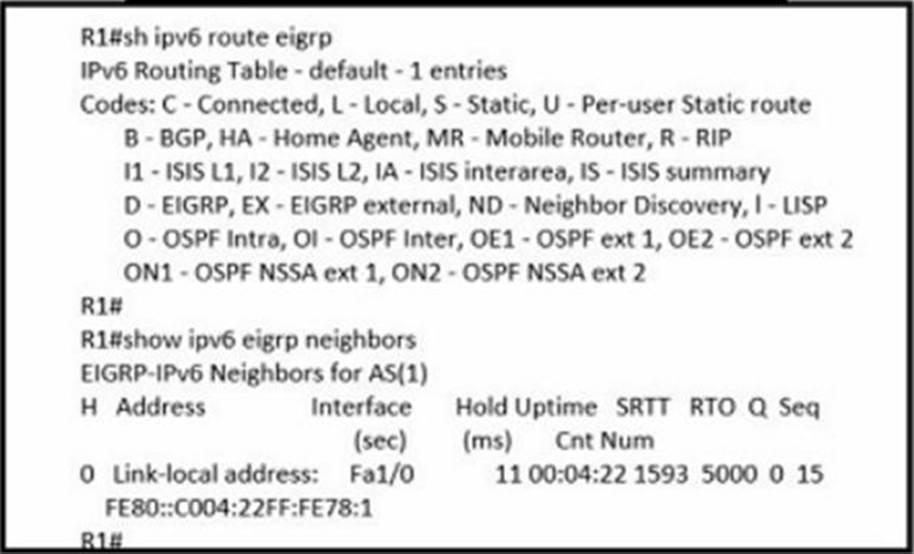
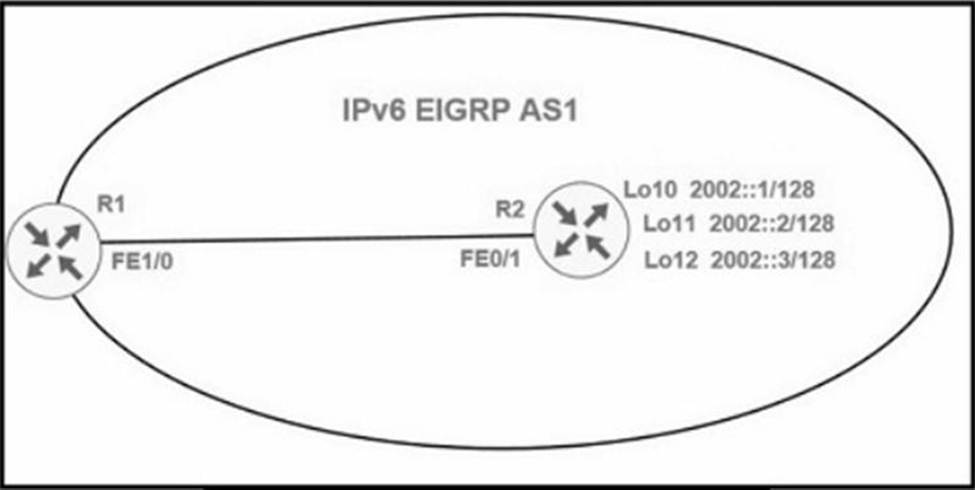
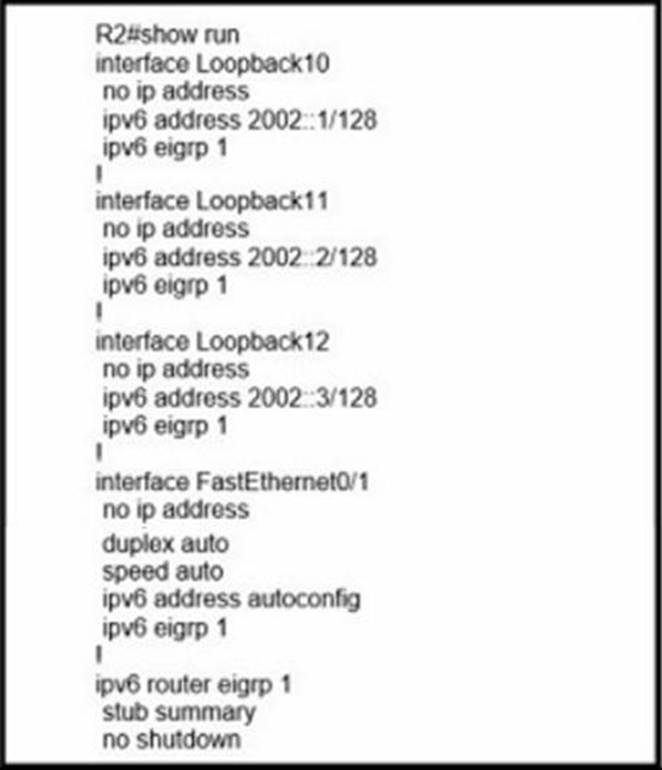
R1 cannot receive the R2 Interfaces with individual prefixes.
What must be reconfigured to advertise R2 Interfaces to R1?
- A . EIGRP process on R2 by removing the stub command Keyword summary
- B . interface FastEthernet0/1 on R2 with an EIGRP summary for all three loopback prefixes
- C . EIGRP process on R2 with the command stub summary receive-only
- D . EIGRP process on R2 with the command stub summary connected
Refer to the exhibit.
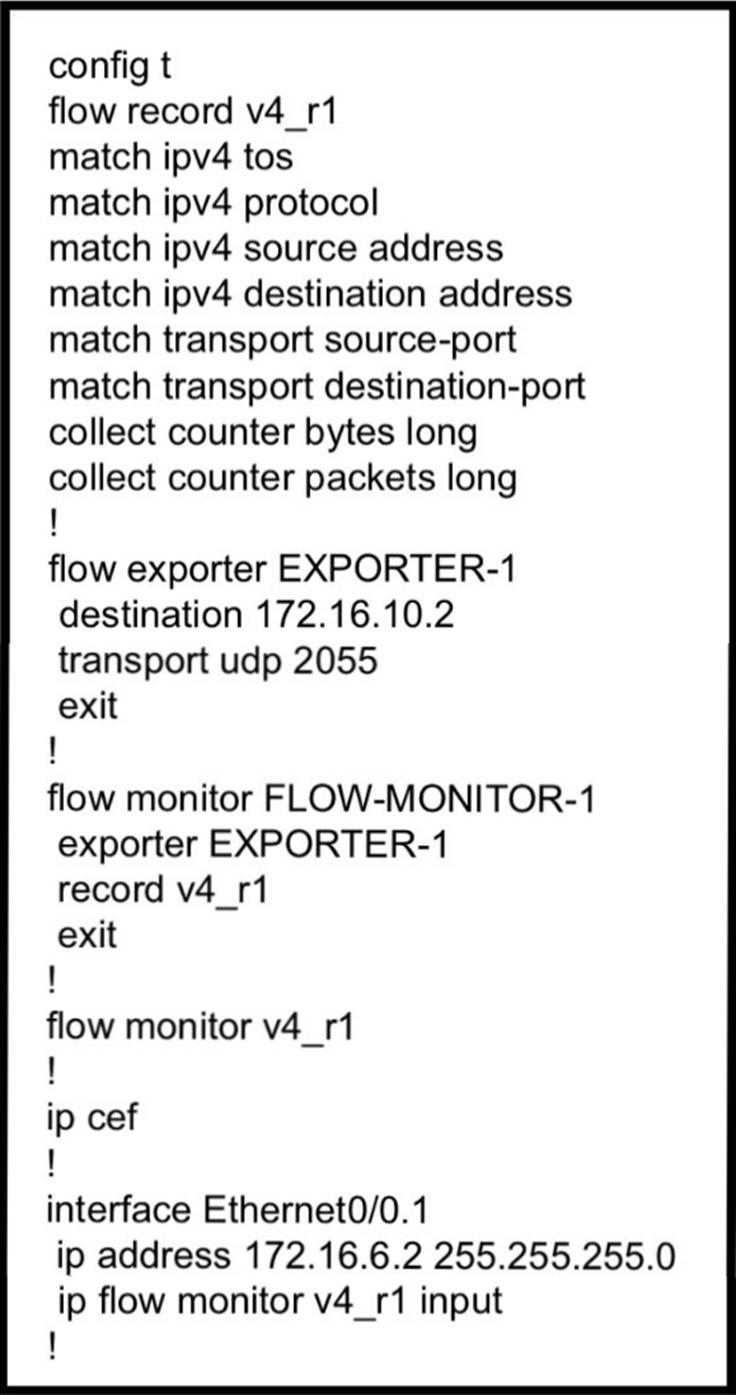
The remote server is failing to receive the NetFlow data.
Which action resolves the issue?
- A . Modify the flow transport command transport udp 2055 to move under flow monitor profile.
- B . Modify the interlace command to Ip flow monitor FLOW-MONITOR-1 Input.
- C . Modify the udp port under flow exporter profile to Ip transport udp 4739.
- D . Modify the flow record command record v4_r1 to move under flow exporter profile.
B
Explanation:
From the exhibit we see there are two flow monitors: the first one “FLOW-MONITOR-1” has been configured correctly but the second one “v4_r1” was left empty andinterface E0/0.1 is using it. So the remote server does not receive any NetFlow data.
What must a network architect consider for RTs when planning for a single customer full-mesh VPN m an MPLS Layer 3 network?
- A . RT must be globally unique within the same VPN
- B . RT must be globally identical within the same VPN
- C . RT values must be Afferent from the RD values in the same VPN
- D . Each RT value must be identical to an RD value within the same VPN.
What is the purpose of an OSPF sham-link?
- A . to allow intra-area routing when OSPF is used as the PE-CE connection protocol in an MPLS VPN network
- B . to correct OSPF backdoor routing when OSPF is used as the PE-CE connection protocol *i an MPLS VPN network
- C . to correct OSPF backdoor routing when OSPF is used as the PE-PE connection protocol m an MPLS VPN network
- D . to allow inter-area routing when OSPF is used as the PE-CE connection protocol in a MPLS VPN network
Refer to the exhibit.
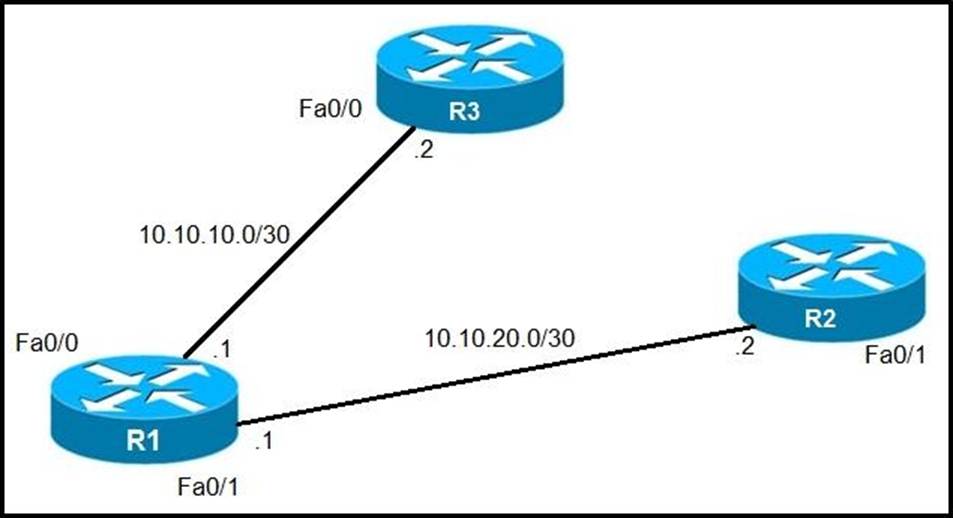
An IP SLA was configured on router R1 that allows the default route to be modified in the event that Fa0/0 loses reachability with the router R3 Fa0/0 interface. The route has changed to flow through router R2.
Which debug command is used to troubleshoot this issue?
- A . debug ip flow
- B . debug ip sla error
- C . debug ip routing
- D . debug ip packet
C
Explanation:
debug ip routing This command enables debugging messages related to the routing table.
Refer to the exhibit.
An IP SLA was configured on router R1 that allows the default route to be modified in the event that Fa0/0 loses reachability with the router R3 Fa0/0 interface. The route has changed to flow through router R2.
Which debug command is used to troubleshoot this issue?
- A . debug ip flow
- B . debug ip sla error
- C . debug ip routing
- D . debug ip packet
C
Explanation:
debug ip routing This command enables debugging messages related to the routing table.
Refer to the exhibit.
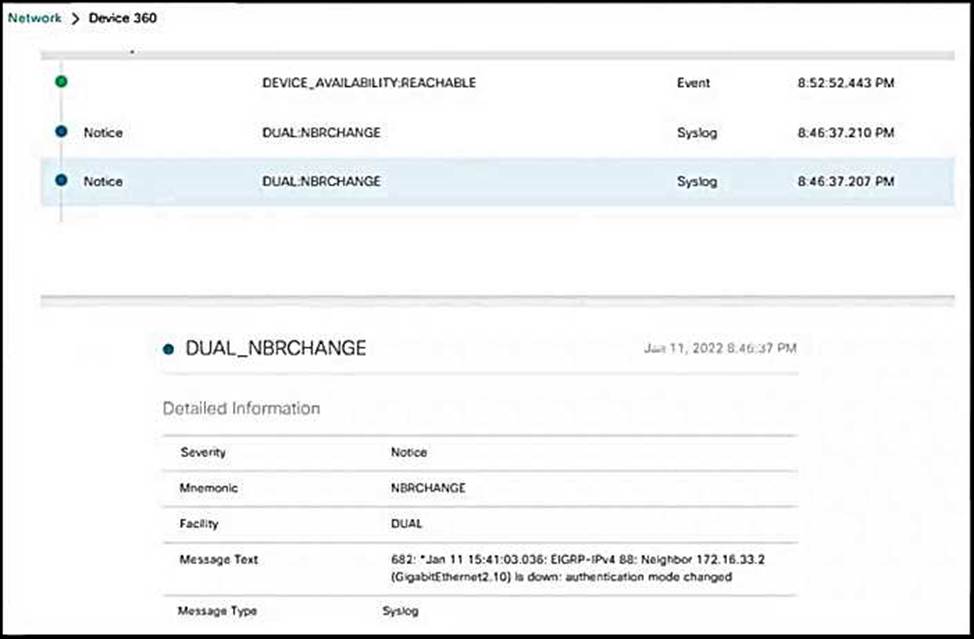
R1 test its directly connected EIGRP peer 172.16.33.2 (SW1).
Which configuration resolves the issue1?
- A . key chain EIGRP
key 1
key-string Cisco
!
interface Gigabit Ethernet 2
IP authentication mode elgrp 88 md5
IP authentication key-chain elgrp 88 EIGRP - B . key chain EIGRP
key1
key-string Cisco
!
interface Gigabit Ethernet 2.10
IP authentication mode eigrp 88 md5
IP authentication key-chain eigrp 88 Cisco - C . key chain EIGRP
key 1
key-string Cisco
!
interface Gigabit Ethernet 2.10
IP authentication mode elgrp 88 md5
IP authentication key-chain eigrp 88 EIGRP - D . key chain EIGRP
key1
key-string Cisco
!
interface Gigabit Ethernet 2
IP authentication mode eigrp 88 md5
IP authentication key-chain elgrp 88 Cisco
Refer to the exhibit.
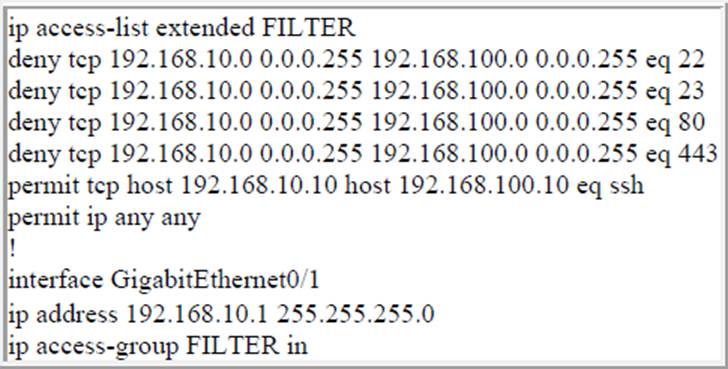
The ACL is placed on the inbound Gigabit 0/1 interface of the router. Host 192.168.10.10cannot SSH to host 192.168.100.10 even though the flow is permitted.
Which action resolves the issue without opening full access to this router?
- A . Move the SSH entry to the beginning of the ACL
- B . Temporarily move the permit ip any any line to the beginning of the ACL to see if the flow works
- C . Temporarily remove the ACL from the interface to see if the flow works
- D . Run the show access-list FILTER command to view if the SSH entry has any hit statistic associated with it
Refer to the exhibit.
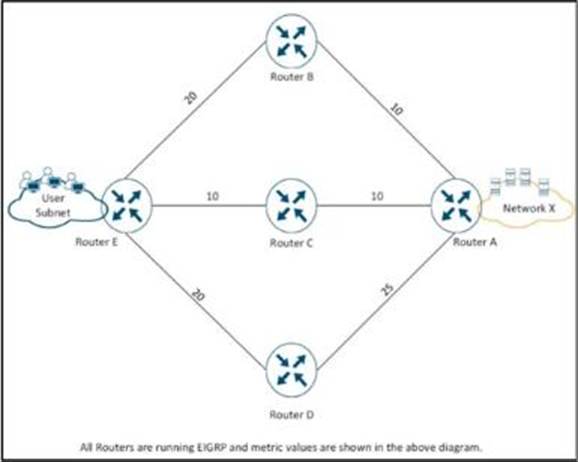
The IT manager received reports from users about slow application through network x.
Which action resolves the issue?
- A . Use the variance 2 command to enable load balancing.
- B . Increase the bandwidth from the service provider.
- C . Move the servers into the users subnet.
- D . Upgrade the IOS on router E.