
Check Point 156-315.81.20 Practice Exams
Last updated on Oct 23,2026- Exam Code: 156-315.81.20
- Exam Name: Check Point Certified Security Expert - R81.20
- Certification Provider: Check Point
- Latest update: Oct 23,2026
In which deployment is the security management server and Security Gateway installed on the same appliance?
- A . Standalone
- B . Remote
- C . Distributed
- D . Bridge Mode
A
Explanation:
In a Standalone deployment, a Check Point computer runs both the Security Gateway and Security Management Server products. This means that the same appliance performs both network security functions and security policy management functions. A Standalone deployment is suitable for small or branch offices that do not require a separate management server.
Reference: Check Point R81 Installation and Upgrade Guide, page 10
On R81.20 the IPS Blade is managed by:
- A . Threat Protection policy
- B . Anti-Bot Blade
- C . Threat Prevention policy
- D . Layers on Firewall policy
C
Explanation:
On R81.20 the IPS Blade is managed by the Threat Prevention policy. The Threat Prevention policy is
a unified policy that includes Anti-virus, IPS, Anti-bot, and Threat Emulation software blades. The IPS blade provides protection against network attacks and exploits by inspecting the traffic and blocking malicious packets. The IPS blade can be configured with different profiles and exceptions to suit different security needs.
Reference: R81 Threat Prevention Administration Guide, page 15.
Which two Identity Awareness daemons are used to support identity sharing?
- A . Policy Activation Point (PAP) and Policy Decision Point (PDP)
- B . Policy Manipulation Point (PMP) and Policy Activation Point (PAP)
- C . Policy Enforcement Point (PEP) and Policy Manipulation Point (PMP)
- D . Policy Decision Point (PDP) and Policy Enforcement Point (PEP)
D
Explanation:
The two Identity Awareness daemons that are used to support identity sharing are Policy Decision Point (PDP) and Policy Enforcement Point (PEP). PDP is a daemon that runs on Security Gateways that acquire identities from various sources, such as AD Query, Identity Agent, Captive Portal, etc.
PEP is a daemon that runs on Security Gateways that enforce the security policy based on identities received from PDPs. Identity sharing is a feature that allows PDPs to share identities with other PDPs or PEPs in different gateways or domains.
Reference: [Check Point R81 Identity Awareness Administration Guide]
Which options are given on features, when editing a Role on Gaia Platform?
- A . Read/Write, Read Only
- B . Read/Write, Read Only, None
- C . Read/Write, None
- D . Read Only, None
B
Explanation:
The options that are given on features, when editing a Role on Gaia Platform are Read/Write, Read Only, and None. These options determine the level of access that a user has to a specific feature or command in Gaia. If a user has Read/Write access to a feature, they can view and modify the settings of that feature. If a user has Read Only access to a feature, they can only view the settings of that feature, but not change them. If a user has None access to a feature, they cannot view or modify the settings of that feature.
The following command is used to verify the CPUSE version:
- A . HostName:0>show installer status build
- B . [Expert@HostName:0]#show installer status
- C . [Expert@HostName:0]#show installer status build
- D . HostName:0>show installer build
A
Explanation:
The correct command to verify the CPUSE (Check Point Update Service Engine) version is:
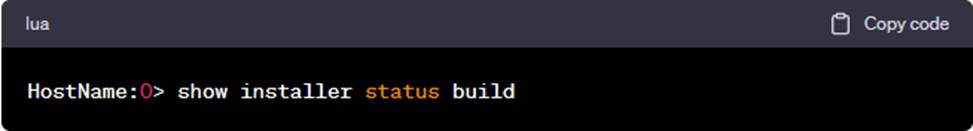
Option B is incorrect because it uses the "[Expert@HostName:0]#" prompt, which is typically used for expert mode commands, but the CPUSE version can be checked using the "show installer status build" command in standard mode.
Option C is incorrect because it uses the "[Expert@HostName:0]#" prompt, and while it includes the "build" parameter, it’s not the standard command to check the CPUSE version.
Option D is incorrect because it uses the "HostName:0>" prompt, but it lacks the "show" command and uses "build" instead of "status build."
Reference: Check Point Certified Security Expert R81 documentation
Bob has finished io setup provisioning a secondary security management server. Now he wants to check if the provisioning has been correct.
Which of the following Check Point command can be used to check if the security management server has been installed as a primary or a secondary security management server?
- A . cpprod_util MgmtlsPrimary
- B . cpprod_util FwlsSecondary
- C . cpprod_util MgmtlsSecondary
- D . cpprod_util FwlsPrimary
A
Explanation:
The cpprod_util command is a utility that provides information about the installed Check Point products and their versions. The cpprod_util MgmtIsPrimary option checks if the Security Management Server is installed as a primary or a secondary server in a High Availability cluster2. If the server is primary, the command returns “yes”. If the server is secondary, the command returns “no”. Therefore, Bob can use this command to verify the provisioning of the secondary Security Management Server.
Reference: 2: cpprod_util
The back-end database for Check Point Management uses:
- A . PostgreSQL
- B . MongoDB
- C . MySQL
- D . DBMS
B
Explanation:
Check Point Management uses MongoDB as its back-end database. MongoDB is a NoSQL database that offers high performance, high availability, and easy scalability, which are essential for managing the complex and dynamic nature of network security configurations and logs.
After the initial installation on Check Point appliance, you notice that the Management-interface and default gateway are incorrect.
Which commands could you use to set the IP to 192.168.80.200/24 and default gateway to 192.168.80.1.
- A . set interface Mgmt ipv4-address 192.168.80.200 mask-length 24set static-route default nexthop
gateway address 192.168.80.1 onsave config - B . set interface Mgmt ipv4-address 192.168.80.200 255.255.255.0add static-route 0.0.0.0. 0.0.0.0 gw 192.168.80.1 onsave config
- C . set interface Mgmt ipv4-address 192.168.80.200 255.255.255.0set static-route 0.0.0.0. 0.0.0.0 gw 192.168.80.1 onsave config
- D . set interface Mgmt ipv4-address 192.168.80.200 mask-length 24add static-route default nexthop gateway address 192.168.80.1 onsave config
A
Explanation:
To set the IP address and default gateway of the Management interface on a Check Point appliance, you can use the following commands:
set interface Mgmt ipv4-address 192.168.80.200 mask-length 24 – This command sets the IPv4 address of the Management interface to 192.168.80.200 and the subnet mask to 255.255.255.0 (24 bits).
set static-route default nexthop gateway address 192.168.80.1 on – This command sets the default gateway to 192.168.80.1 and enables the static route.
save config – This command saves the configuration changes to the appliance.
These commands are documented in the Check Point appliance initial installation guide, which you can find in the web search results.
The other options are incorrect because they use invalid syntax or parameters for the commands. For example, option B uses add static-route instead of set static-route, option C uses 0.0.0.0. instead of 0.0.0.0, and option D uses add static-route default instead of set static-route default.
When an encrypted packet is decrypted, where does this happen?
- A . Security policy
- B . Inbound chain
- C . Outbound chain
- D . Decryption is not supported
A
Explanation:
When an encrypted packet is received by a Check Point Security Gateway, it is decrypted according to the security policy. The security policy defines the rules and settings for encryption and decryption of traffic, such as the encryption algorithm, the encryption domain, the pre-shared secret or certificate, etc. The security policy is enforced by the Firewall kernel, which is responsible for decrypting the packets before passing them to the inbound chain for further inspection. The inbound chain consists of various inspection modules that apply security checks and actions on the decrypted packets. The outbound chain is the reverse process, where the packets are inspected and then encrypted according to the security policy before being sent out.
Reference: Check Point Firewall Security Solution, Check Point R81 Cyber Security Platform, Check Point VPN Administration Guide R81
The SmartEvent R81 Web application for real-time event monitoring is called:
- A . SmartView Monitor
- B . SmartEventWeb
- C . There is no Web application for SmartEvent
- D . SmartView
B
Explanation:
The SmartEvent R81 Web application for real-time event monitoring is called SmartEventWeb.
SmartEventWeb is a web-based interface that allows administrators to view and analyze security events from various sources, such as logs, reports, incidents, and indicators. SmartEventWeb provides dashboards, widgets, filters, and drill-down options to help administrators gain insights into their security posture. The other options are either incorrect or refer to different applications.