
Check Point 156-315.81.20 Practice Exams
Last updated on Oct 23,2026- Exam Code: 156-315.81.20
- Exam Name: Check Point Certified Security Expert - R81.20
- Certification Provider: Check Point
- Latest update: Oct 23,2026
What command verifies that the API server is responding?
- A . api stat
- B . api status
- C . show api_status
- D . app_get_status
B
Explanation:
The API server is a service that runs on the Security Management Server and enables external applications to communicate with the Check Point management database using REST APIs.
You can verify that the API server is responding by using the following command in Expert mode:
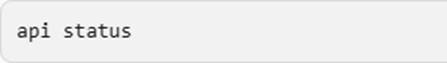
This command will display the current status of the API server, such as running, stopped, or initializing. It will also show the API version, port number, and SSL certificate information.
Reference: Check Point R81 REST API Reference Guide
What CLI utility runs connectivity tests from a Security Gateway to an AD domain controller?
- A . test_connectivity_ad Cd <domain>
- B . test_ldap_connectivity Cd <domain>
- C . test_ad_connectivity Cd <domain>
- D . ad_connectivity_test Cd <domain>
C
Explanation:
The CLI utility that runs connectivity tests from a Security Gateway to an AD domain controller is test_ad_connectivity -d <domain>. This command tests the connectivity between the gateway and the domain controller using LDAP, Kerberos, and WMI protocols. It also verifies the identity awareness configuration and shows the relevant logs3. The other options are not valid commands for testing AD connectivity.
Reference: 3: Check Point Software, Getting Started, Testing Active Directory Connectivity.
What are the available options for downloading Check Point hotfixes in Gala WebUI (CPUSE)?
- A . Manually, Scheduled, Automatic
- B . Manually, Automatic, Disabled
- C . Manually, Scheduled, Disabled
- D . Manually, Scheduled, Enabled
A
Explanation:
The available options for downloading Check Point hotfixes in Gaia WebUI (CPUSE) are Manually, Scheduled, and Automatic. These options can be configured in the CPUSE Settings tab of the Gaia Portal. The Manual option lets you download hotfixes manually from the Check Point Cloud or a local Deployment Agent when you need them. The Scheduled option lets you download hotfixes automatically at a specified time interval (daily, weekly, or monthly). The Automatic option lets you download hotfixes automatically as soon as they are available.
Reference: https://sc1.checkpoint.com/documents/R77/CP_R77_Gaia_AdminWebAdminGuide/ html_frameset.htm?topic=documents/R77/CP_R77_Gaia_AdminWebAdminGuide/112109
The WebUI offers several methods for downloading hotfixes via CPUSE except:
- A . Automatic
- B . Force override
- C . Manually
- D . Scheduled
B
Explanation:
The WebUI offers three methods for downloading hotfixes via CPUSE: Automatic, Manually, and Scheduled. Force override is not a valid method for downloading hotfixes. Force override is an option that can be used when installing a hotfix to override the compatibility check and force the installation of the hotfix.
Reference: CPUSE – Gaia Software Updates (including Gaia Software Updates Agent)
An administrator is creating an IPsec site-to-site VPN between his corporate office and branch office. Both offices are protected by Check Point Security Gateway managed by the same Security Management Server. While configuring the VPN community to specify the pre-shared secret the administrator found that the check box to enable pre-shared secret and cannot be enabled.
Why does it not allow him to specify the pre-shared secret?
- A . IPsec VPN blade should be enabled on both Security Gateway.
- B . Pre-shared can only be used while creating a VPN between a third party vendor and Check Point Security Gateway.
- C . Certificate based Authentication is the only authentication method available between two Security Gateway managed by the same SMS.
- D . The Security Gateways are pre-R75.40.
C
Explanation:
When two Security Gateways are managed by the same Security Management Server, they use certificate based authentication to establish a VPN tunnel. This is because the Security Management Server acts as an internal certificate authority (ICA) that can issue and revoke certificates for the Security Gateways. The Security Management Server also maintains a trust relationship with the Security Gateways, which is based on a one-time password (OTP) that is used to initialize secure internal communication (SIC). Therefore, there is no need to use a pre-shared secret for authentication between two Security Gateways managed by the same SMS.
Which of the following is NOT a method used by identity Awareness for acquiring identity?
- A . Remote Access
- B . Active Directory Query
- C . Cloud IdP (Identity Provider)
- D . RADIUS
Full synchronization between cluster members is handled by Firewall Kernel.
Which port is used for this?
- A . UDP port 265
- B . TCP port 265
- C . UDP port 256
- D . TCP port 256
D
Explanation:
Full synchronization between cluster members is handled by Firewall Kernel using TCP port 256 by default. Full synchronization occurs when a cluster member joins or rejoins the cluster and needs to receive the entire state table from another member.
Reference: [ClusterXL Administration Guide]
Fill in the blanks: Default port numbers for an LDAP server is ________________ for standard connections and SSL connections.
- A . 443,389
- B . 636; 8080
- C . 290; 3389
- D . 389; 636
D
Explanation:
LDAP (Lightweight Directory Access Protocol) operates over different ports, with each serving a specific purpose. Port 389 is the default port for unsecured LDAP connections or LDAP with StartTLS, which upgrades the connection to use TLS (Transport Layer Security) for encryption. On the other hand, port 636 is used for LDAP over SSL/TLS, often referred to as LDAPS (LDAP Secure), where communication is encrypted from the start of the connection1.
Reference: LDAP Ports Explained: Configuring Standard, StartTLS, and LDAPS Connections
Red Hat Directory Server documentation on changing LDAP and LDAPS port numbers
Oracle documentation on Directory Server and Directory Proxy Server LDAP and LDAPS Port Numbers ServerFault discussion on LDAP server authentication ports
Which one of the following is true about Capsule Connect?
- A . It is a full layer 3 VPN client
- B . It offers full enterprise mobility management
- C . It is supported only on iOS phones and Windows PCs
- D . It does not support all VPN authentication methods
A
Explanation:
Capsule Connect is a full layer 3 VPN client that provides secure and seamless remote access to corporate networks from iOS and Android devices. It supports all VPN authentication methods, such as certificates, passwords, tokens, and challenge-response. It also supports split tunneling and seamless roaming.
Reference: Capsule Connect Datasheet, Capsule Connect Administration Guide
True or False: In R81, more than one administrator can login to the Security Management Server with write permission at the same time.
- A . False, this feature has to be enabled in the Global Properties.
- B . True, every administrator works in a session that is independent of the other administrators.
- C . True, every administrator works on a different database that is independent of the other administrators.
- D . False, only one administrator can login with write permission.
B
Explanation:
In R81, more than one administrator can login to the Security Management Server with write permission at the same time. This feature is enabled by default and allows concurrent administration of the security policy. Every administrator works in a session that is independent of the other administrators. Changes made by one administrator are not visible to others until they are published. Administrators can also lock objects to prevent others from editing them until they are unlocked.
Reference: R81 Security Management Administration Guide, page 43.