
Check Point 156-315.81.20 Practice Exams
Last updated on Oct 22,2026- Exam Code: 156-315.81.20
- Exam Name: Check Point Certified Security Expert - R81.20
- Certification Provider: Check Point
- Latest update: Oct 22,2026
The installation of a package via SmartConsole CANNOT be applied on
- A . A single Security Gateway
- B . A full Security Cluster (All Cluster Members included)
- C . Multiple Security Gateways and/or Clusters
- D . R81.20 Security Management Server
How many images are included with Check Point TE appliance in Recommended Mode?
- A . 2(OS) images
- B . images are chosen by administrator during installation
- C . as many as licensed for
- D . the newest image
A
Explanation:
The Check Point TE appliance in Recommended Mode includes 2(OS) images. One image is used for running the appliance, and the other image is used for backup and recovery purposes. The images are not chosen by the administrator during installation, nor based on the license or the latest version.
Reference: [Check Point R81 Threat Emulation Administration Guide]
Check Point Support in many cases asks you for a configuration summary of your Check Point system.
This is also called:
- A . cpexport
- B . sysinfo
- C . cpsizeme
- D . cpinfo
D
Explanation:
Check Point Support in many cases asks you for a configuration summary of your Check Point system. This is also called cpinfo. Cpinfo is a utility that collects diagnostic data on a Check Point gateway, management server, or log server. It generates a file that contains information such as product version, license details, OS details, network configuration, installed hotfixes, status of Check Point processes, firewall tables, etc. This file can be used by Check Point Support to troubleshoot issues or analyze performance.
Reference: [Cpinfo Utility]
Advanced Security Checkups can be easily conducted within:
- A . Reports
- B . Advanced
- C . Checkups
- D . Views
- E . Summary
A
Explanation:
Advanced Security Checkups can be easily conducted within the Reports tab in the Logs & Monitor view in SmartConsole. The Reports tab allows you to generate and view various reports that provide insights into the security status and performance of your network. You can use predefined reports or create custom reports based on your needs. You can also schedule reports to run automatically and send them by email. Some of the predefined reports that can help you conduct advanced security checkups are:
Security Overview: This report provides a summary of the security posture of your network, including the number and severity of incidents, the top attacked hosts and services, the top attackers and attack methods, the top detected threats and vulnerabilities, etc.
Security Best Practices: This report evaluates your security configuration and policy against the Check Point best practices and provides recommendations for improvement. It covers areas such as firewall policy, NAT policy, VPN policy, identity awareness, threat prevention, etc.
Compliance Status: This report assesses your compliance level with various regulations and standards, such as PCI DSS, ISO 27001, NIST 800-53, etc. It shows the compliance score, the compliance status of each requirement, the compliance status of each gateway and blade, etc. Network Activity: This report shows the network activity and traffic patterns on your network, including the top sources and destinations of traffic, the top protocols and applications used, the top bandwidth consumers, etc.
System Health: This report monitors the health and performance of your management server and gateways, including the CPU utilization, memory usage, disk space, network interfaces, etc.
Reference: R81 Logging and Monitoring Administration Guide
Under which file is the proxy arp configuration stored?
- A . $FWDIR/state/proxy_arp.conf on the management server
- B . $FWDIR/conf/local.arp on the management server
- C . $FWDIR/state/_tmp/proxy.arp on the security gateway
- D . $FWDIR/conf/local.arp on the gateway
D
Explanation:
The proxy ARP configuration is stored under the following file:
D. $FWDIR/conf/local.arp on the gateway
This file, local.arp, contains the proxy ARP configuration for the Security Gateway. It is used to configure ARP (Address Resolution Protocol) settings for network communication.
Reference: Check Point Certified Security Expert R81 Study Guide, Check Point documentation on proxy ARP.
What is the Implicit Clean-up Rule?
- A . A setting is defined in the Global Properties for all policies.
- B . A setting that is configured per Policy Layer.
- C . Another name for the Clean-up Rule.
- D . Automatically created when the Clean-up Rule is defined.
C
Explanation:
The Implicit Clean-up Rule is another name for the Clean-up Rule, which is the last rule in every policy layer. The Clean-up Rule defines the default action for traffic that does not match any of the preceding rules in the layer. The default action is to drop the traffic and log it, but it can be changed by the administrator.
Reference: Training & Certification | Check Point Software, Check Point Resource Library
Fill in the blank: With the User Directory Software Blade, you can create user definitions on a(n)_____________ Server.
- A . SecurID
- B . NT domain
- C . LDAP
- D . SMTP
C
Explanation:
The User Directory Software Blade allows you to create user definitions on an LDAP server, such as Active Directory, and use them in your security policy. You can also integrate with other user authentication methods, such as SecurID, RADIUS, or TACACS+, but you cannot create user definitions on those servers.
The references are:
Check Point Certified Security Expert R81.20 (CCSE) Core Training, slide 13
Check Point R81 Quantum Security Gateway Guide, page 139
Check Point R81 Identity Awareness Administration Guide, page 9
Automatic affinity means that if SecureXL is running, the affinity for each interface is automatically
reset every
- A . 15 sec
- B . 60 sec
- C . 5 sec
- D . 30 sec
B
Explanation:
Automatic affinity means that if SecureXL is running, the affinity for each interface is automatically reset every 60 seconds based on the current traffic load. This ensures optimal performance and load balancing of SecureXL instances.
Reference: SecureXL Mechanism
Check Pont Central Deployment Tool (CDT) communicates with the Security Gateway / Cluster Members over Check Point SIC _______ .
- A . TCP Port 18190
- B . TCP Port 18209
- C . TCP Port 19009
- D . TCP Port 18191
D
Explanation:
Check Point Central Deployment Tool (CDT) communicates with the Security Gateway / Cluster Members over Check Point SIC using TCP port 18191 by default. CDT is a tool that allows you to perform simultaneous configuration changes on multiple gateways or clusters using predefined commands or scripts.
Reference: Check Point Central Deployment Tool (CDT)
You find one of your cluster gateways showing “Down” when you run the “cphaprob stat” command. You then run the “clusterXL_admin up” on the down member but unfortunately the member continues to show down.
What command do you run to determine the cause?
- A . cphaprob Cf register
- B . cphaprob Cd Cs report
- C . cpstat Cf all
- D . cphaprob Ca list
D
Explanation:
To determine the cause of a cluster gateway showing "Down" despite running "clusterXL_admin up" on the down member, you can run the following command:
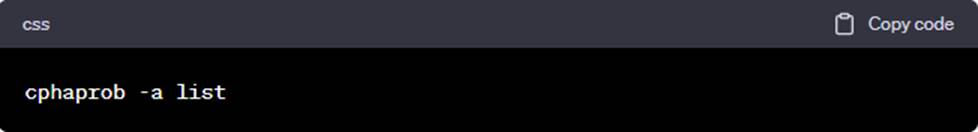
This command will provide a list of cluster members along with their statuses and can help diagnose the issue with the down member.
Reference: Check Point documentation or training materials related to High Availability and ClusterXL.