
Check Point 156-215.81.20 Practice Exams
Last updated on Oct 23,2026- Exam Code: 156-215.81.20
- Exam Name: Check Point Certified Security Administrator R81.20
- Certification Provider: Check Point
- Latest update: Oct 23,2026
From SecureXL perspective, what are the tree paths of traffic flow:
- A . Initial Path; Medium Path; Accelerated Path
- B . Layer Path; Blade Path; Rule Path
- C . Firewall Path; Accept Path; Drop Path
- D . Firewall Path; Accelerated Path; Medium Path
D
Explanation:
The correct answer is D because from SecureXL perspective, the three paths of traffic flow are Firewall Path, Accelerated Path, and Medium Path3. The Firewall Path is used when SecureXL is disabled or traffic is not eligible for acceleration3. The Accelerated Path is used when SecureXL handles the entire connection and bypasses the Firewall kernel3. The Medium Path is used when SecureXL handles part of the connection and forwards packets to the Firewall kernel for further inspection3. The other options are not valid paths of traffic flow from SecureXL perspective3.
Reference: Check Point R81 Performance Tuning Administration Guide
Which two of these Check Point Protocols are used by?
- A . ELA and CPD
- B . FWD and LEA
- C . FWD and CPLOG
- D . ELA and CPLOG
B
Explanation:
The two Check Point Protocols that are used by are FWD and LEA567. FWD is the Firewall Daemon that handles communication between different Check Point components, such as Security Management Server, Security Gateway, SmartConsole, etc. LEA is the Log Export API that allows external applications to retrieve logs from the Security Gateway or Security Management Server. Therefore, the correct answer is B. FWD and LEA.
Reference: Border Gateway Protocol – Check Point Software, Check Point IPS Datasheet, List of valid protocols for services? – Check Point CheckMates
Gaia includes Check Point Upgrade Service Engine (CPUSE), which can directly receive updates for what components?
- A . The Security Gateway (SG) and Security Management Server (SMS) software and the CPUSE engine.
- B . Licensed Check Point products for the Gala operating system and the Gaia operating system itself.
- C . The CPUSE engine and the Gaia operating system.
- D . The Gaia operating system only.
B
Explanation:
Gaia includes Check Point Upgrade Service Engine (CPUSE), which can directly receive updates for licensed Check Point products for the Gaia operating system and the Gaia operating system itself. CPUSE is an advanced tool that automates software updates and upgrades on Gaia platforms. It can download and install packages such as hotfixes, Jumbo Hotfix Accumulators, minor versions, major versions, and OS updates.
Reference: [CPUSE – Gaia Software Updates (including Gaia Software Updates Agent)], [Check Point R81]
When connected to the Check Point R80 Management Server using the SmartConsole the first administrator to connect has a lock on:
- A . Only the objects being modified in the Management Database and other administrators can connect to make changes using a special session as long as they all connect from the same LAN network.
- B . The entire Management Database and other administrators can connect to make changes only if the first administrator switches to Read-only.
- C . The entire Management Database and all sessions and other administrators can connect only as Read-only.
- D . Only the objects being modified in his session of the Management Database and other administrators can connect to make changes using different sessions.
D
Explanation:
The answer is D because in R80 and above, the first administrator to connect to the Management Server using SmartConsole gets a lock on only the objects being modified in his session of the Management Database. Other administrators can connect to make changes using different sessions, but they cannot modify the same objects as the first administrator until he publishes his changes. This is called concurrent administration and it allows multiple administrators to work on the same policy package simultaneously12
Reference: Check Point R80.10 Concurrent Administration, Check Point R80.40 Security Management Administration Guide
Which one of the following is a way that the objects can be manipulated using the new API integration in R80 Management?
- A . Microsoft Publisher
- B . JSON
- C . Microsoft Word
- D . RC4 Encryption
B
Explanation:
The way that the objects can be manipulated using the new API integration in R80 Management is JSON. JSON (JavaScript Object Notation) is a lightweight data-interchange format that is easy for humans and machines to read and write. The R80 Management API uses JSON as the primary data format for requests and responses. Therefore, the correct answer is B. JSON.
Which policy type is used to enforce bandwidth and traffic control rules?
- A . Access Control
- B . Threat Emulation
- C . Threat Prevention
- D . QoS
D
Explanation:
The policy type that is used to enforce bandwidth and traffic control rules is QoS. QoS stands for Quality of Service and is a software blade that allows administrators to prioritize network traffic according to various criteria such as source, destination, service, application, user, etc. QoS can also limit the bandwidth consumption of certain traffic types or guarantee a minimum bandwidth for critical applications.
Reference: [Check Point R81 QoS Administration Guide]
You have created a rule at the top of your Rule Base to permit Guest Wireless access to the Internet. However, when guest users attempt to reach the Internet, they are not seeing the splash page to accept your Terms of Service, and cannot access the Internet.
How can you fix this?
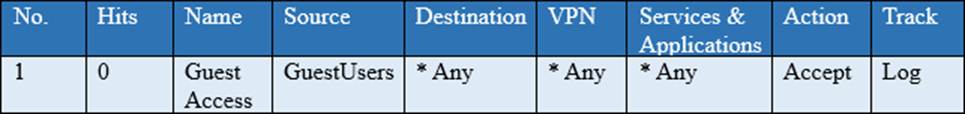
- A . Right click Accept in the rule, select “More”, and then check “Enable Identity Captive Portal”
- B . On the firewall object, Legacy Authentication screen, check “Enable Identity Captive Portal”
- C . In the Captive Portal screen of Global Properties, check “Enable Identity Captive Portal”
- D . On the Security Management Server object, check the box “Identity Logging”
A
Explanation:
Identity Captive Portal is a Check Point Identity Awareness web portal, to which users connect with their web browser to log in and authenticate, when using Browser-Based Authentication2. To enable Identity Captive Portal for a specific rule, you need to right click Accept in the rule, select “More”, and then check “Enable Identity Captive Portal”3.
Reference: Identity Awareness Administration Guide R80, Identity awareness with captive portal in Checkpoint R80
Name the utility that is used to block activities that appear to be suspicious.
- A . Penalty Box
- B . Drop Rule in the rulebase
- C . Suspicious Activity Monitoring (SAM)
- D . Stealth rule
C
Explanation:
Suspicious Activity Monitoring (SAM) is the utility that is used to block activities that appear to be suspicious. SAM allows administrators to block connections from specific IP addresses or network objects for a specified period of time3. Penalty Box is a feature of SAM that automatically blocks connections from sources that generate too many log entries. Drop Rule in the rulebase is a firewall action that discards packets that match certain criteria. Stealth rule is a firewall rule that prevents direct access to the Security Gateway from external sources.
Fill in the blank RADIUS Accounting gets_____data from requests generated by the accounting client
- A . Location
- B . Payload
- C . Destination
- D . Identity
D
Explanation:
RADIUS Accounting gets identity data from requests generated by the accounting client. RADIUS Accounting is a feature that allows tracking and measuring resource usage of network services by users. The accounting client, which is usually a network access server (NAS), sends accounting requests to a RADIUS server with information about user sessions, such as start and stop times, bytes transmitted and received, IP addresses, etc. The RADIUS server records this information in a database for billing, auditing, or reporting purposes. One of the mandatory attributes that the accounting client must include in every accounting request is the User-Name attribute, which identifies the user who is accessing the network service.
When defining group-based access in an LDAP environment with Identity Awareness, what is the BEST object type to represent an LDAP group in a Security Policy?
- A . Access Role
- B . User Group
- C . SmartDirectory Group
- D . Group Template
A
Explanation:
The BEST object type to represent an LDAP group in a Security Policy is an Access Role. An Access Role object defines a set of users, machines, or networks that can access a resource or service1, p. 27. An Access Role object can include LDAP groups as one of its components2, p. 10.
Reference: Check Point CCSA – R81: Practice Test & Explanation, Check Point Identity Awareness Administration Guide R81