
PECB ISO-IEC-27001 Lead Auditor Practice Exams
Last updated on Oct 21,2026- Exam Code: ISO-IEC-27001 Lead Auditor
- Exam Name: PECB Certified ISO/IEC 27001 Lead Auditor exam
- Certification Provider: PECB
- Latest update: Oct 21,2026
You are an experience ISMS audit team leader carrying out a third-party certification audit of an organization specialising in the secure disposal of confidential documents and removable media. Both documents and media are shredded in military grade devices which make it impossible to reconstruct the original.
The audit has gone well and you are just about to start to write the audit report, 30 minutes before the closing meeting. At this point one of the organization’s employees knocks on your door and asks if they can speak to you. They tell you that when things get busy her manager tells her to use a lower grade industrial shredder instead as the organisation has more of these and they operate faster. You were not informed about the existence or use of these machines by the auditee.
Select three options for how you should respond to this information.
- A . Advise the individual managing the audit programme of any recommendation by you to conduct a further auditprior to certification
- B . Cancel the production of the audit report and instead review the organization’s contracts with its clients to determine whether they have permitted the use of lower grade machines
- C . Consider the need for a subsequent audit within 4 weeks based on the additional information that has come to light
- D . Do nothing. All audits are based on a sample and the sample you took did not include a planned review of the lower grade machines
- E . Extend the certification audit duration to create additional time to audit the use of the lower grade machines
- F . Raise a nonconformity against 8.1 Operational Planning and Control as the organization has not been open about its processes
- G . Verify with the auditee that lower grade machines are used in certain circumstances
ACG
Explanation:
According to ISO/IEC 27001:2022 clause 8.1, the organization must plan, implement and control the processes needed to meet the information security requirements, and to implement the actions determined in clause 6.1. The organization must also ensure that the outsourced processes are controlled or influenced. According to control A.5.24, the organization must establish and maintain an information security incident management process that includes reporting information security events and weaknesses. Therefore, the use of lower grade machines for the secure disposal of confidential documents and media could pose a significant information security risk and a potential breach of contract with the clients.
The auditor should respond to this information by:
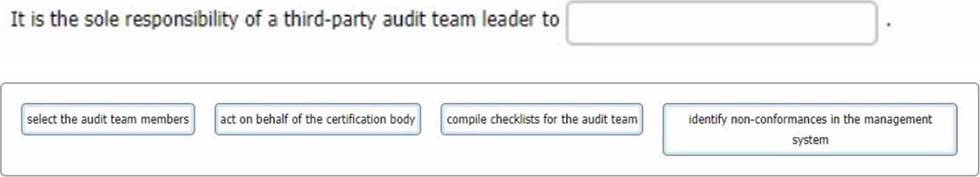
DRAG DROP
Select the words that best complete the sentence:
To complete the sentence with the best word(s), click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Explanation:
A third-party audit team leader is a person who leads an audit team that conducts audits on behalf of an external organization, such as a certification body, that provides certification or accreditation services to other organizations12.
One of the main responsibilities of a third-party audit team leader is to act on behalf of the certification body, which means to represent its interests, policies, and procedures during the audit process12.
Acting on behalf of the certification body involves communicating with the audit client and the auditee, planning and conducting the audit, reporting and evaluating the audit results, and making recommendations for certification or accreditation decisions12.
Acting on behalf of the certification body also requires maintaining professional integrity, impartiality, confidentiality, and competence throughout the audit process12.
Reference: =
ISO 19011:2022 Guidelines for auditing management systems
ISO/IEC 17021-1:2022 Conformity assessment ― Requirements for bodies providing audit and certification of management systems ― Part 1: Requirements
Which two of the following phrases are ‘objectives’ in relation to a first-party audit?
- A . Apply international standards
- B . Prepare the audit report for the certification body
- C . Confirm the scope of the management system is accurate
- D . Complete the audit on time
- E . Apply Regulatory requirements
- F . Update the management policy
CF
Explanation:
A first-party audit is an internal audit conducted by the organization itself or by an external party on its behalf. The objectives of a first-party audit are to: 12
Confirm the scope of the management system is accurate, i.e., it covers all the processes, activities, locations, and functions that are relevant to the information security objectives and requirements of the organization.
Update the management policy, i.e., review and revise the policy statement, roles and responsibilities, and objectives and targets of the information security management system (ISMS) based on the audit findings and feedback.
The other phrases are not objectives of a first-party audit, but rather:
Apply international standards: This is a requirement for the ISMS, not an objective of the audit. The ISMS must conform to the ISO/IEC 27001 standard and any other applicable standards or regulations12
Prepare the audit report for the certification body: This is an activity of a third-party audit, not a first-party audit. A third-party audit is an external audit conducted by an independent certification body to verify the conformity and effectiveness of the ISMS and to issue a certificate of compliance12 Complete the audit on time: This is a performance indicator, not an objective of the audit. The audit should be completed within the planned time frame and budget, but this is not the primary purpose of the audit12
Apply regulatory requirements: This is also a requirement for the ISMS, not an objective of the audit. The ISMS must comply with the legal and contractual obligations of the organization regarding information security12
Reference: 1: ISO/IEC 27001:2022 Lead Auditor (Information Security Management Systems) Course by CQI and IRCA Certified Training 1 2: ISO/IEC 27001 Lead Auditor Training Course by PECB 2
You ask the IT Manager why the organisation still uses the mobile app while personal data encryption and pseudonymisation tests failed. Also, whether the Service Manager is authorised to approve the test.
The IT Manager explains the test results should be approved by him according to the software security management procedure. The reason why the encryption and pseudonymisation functions failed is that these functions heavily slowed down the system and service performance. An extra 150% of resources are needed to cover this. The Service Manager agreed that access control is good enough and acceptable. That’s why the Service Manager signed the approval. You are preparing the audit findings. Select the correct option.
- A . There is a nonconformity (NC). The organisation and developer do not perform acceptance tests. (Relevant to clause 8.1, control A.8.29)
- B . There is a nonconformity (NC). The Service Manager does not comply with the software security management procedure. (Relevant to clause 8.1, control A.8.30)
- C . There is a nonconformity (NC). The organisation and developer perform security tests that fail. (Relevant to clause 8.1, control A.8.29)
- D . There is NO nonconformity (NC). The Service Manager makes a good decision to continue the service. (Relevant to clause 8.1, control A.8.30)
B
Explanation:
According to ISO 27001:2022 Annex A Control 8.30, the organisation shall ensure that externally provided processes, products or services that are relevant to the information security management system are controlled. This includes developing and entering into licensing agreements that cover code ownership and intellectual property rights, and implementing appropriate contractual requirements related to secure design and coding in accordance with Annex A 8.25 and 8.2912
In this case, the organisation and the developer have performed security tests that failed, which indicates that the secure design and coding requirements of Annex A 8.29 were not met. The IT Manager explains that the encryption and pseudonymisation functions failed because they slowed down the system and service performance, and that an extra 150% of resources are needed to cover this. However, this does not justify the acceptance of the test results by the Service Manager, who is not authorised to approve the test according to the software security management procedure. The Service Manager should have consulted with the IT Manager, who is the owner of the process, and followed the procedure for handling nonconformities and corrective actions. The Service Manager’s decision to continue the service based on access control alone exposes the organisation to the risk of compromising the confidentiality, integrity, and availability of personal data processed by the mobile app. Therefore, there is a nonconformity (NC) with clause 8.1, control A.8.30.
Reference: 1: ISO/IEC 27001:2022 Lead Auditor (Information Security Management Systems) Course by CQI and IRCA Certified Training 1 2: ISO/IEC 27001 Lead Auditor Training Course by PECB 2
Which situation presented below represents a threat?
- A . HackX uses and distributes pirated software
- B . The information security training was provided to only the IT team members of the organization
- C . Hackers compromised the administrator’s account by cracking the password
C
Explanation:
A threat in information security is any circumstance or event with the potential to cause harm to an information system through unauthorized access, destruction, disclosure, modification of data, and/or denial of service. The situation where hackers compromise an administrator’s account by cracking the password represents a direct threat to the security of the information system.
Reference: = This explanation is based on general information security principles and the typical content covered in ISMS ISO/IEC 27001 Lead Auditor training and certification programs. It aligns with the knowledge expected of a professional with an ISO/IEC 27001 Lead Auditor certification
During an audit, the audit team leader reached timely conclusions based on logical reasoning and analysis.
What professional behaviour was displayed by the audit team leader?
- A . Decisive
- B . Open minded
- C . Ethical
- D . Perceptive
A
Explanation:
According to the PECB Candidate Handbook for ISO/IEC 27001 Lead Auditor, one of the professional behaviours expected from an audit team leader is to be decisive, which means to “reach timely conclusions based on logical reasoning and analysis” (page 8). Being open minded, ethical, and perceptive are also desirable qualities for an audit team leader, but they do not match the description given in the question.
Reference: PECB Candidate Handbook for ISO/IEC 27001 Lead Auditor, page 8.
Which one of the following conclusions in the audit report is not required by the certification body when deciding to grant certification?
- A . The corrections taken by the organisation related to major nonconformities have been accepted.
- B . The organisation fully complies with all legal and other requirements applicable to the Information Security Management System.
- C . The plans to address corrective actions related to minor nonconformities have been accepted
- D . The scope of certification has been fulfilled
B
Explanation:
The conclusion in the audit report that is not required by the certification body when deciding to grant certification is that the organisation fully complies with all legal and other requirements applicable to the ISMS. This is because the certification body does not have the authority or the responsibility to verify the legal compliance of the organisation, as this is outside the scope of ISO/IEC 27001:2022. The certification body only evaluates the conformity of the organisation’s ISMS with the requirements of the standard, which include the establishment of a process to identify and evaluate the legal and other requirements that are relevant to the ISMS. The organisation is responsible for ensuring its own legal compliance and for providing evidence of such compliance to the certification body if requested.
Reference: = ISO/IEC 27001:2022, clause 6.1.3; ISO/IEC 27006:2022, clause 9.2.2.4; PECB Candidate Handbook ISO 27001 Lead Auditor, page 29.
Which of the options below presents a minor nonconformity?
- A . The risk assessment methodology prevents evaluation of information security risks
- B . The contract of the company with its supplier does not have the appropriate document version control
- C . The backup of data is performed once a month, while the company’s procedure requires daily backups
C
Explanation:
This is a minor nonconformity. The backup frequency not adhering to the company’s procedure of daily backups but occurring once a month represents a deviation from established processes, yet it might not immediately impact the effectiveness of the information security management system.
Reference: ISO/IEC 27001:2013, Clause A.12.3 (Backup)
After completing Stage 1 and in preparation for a Stage 2 initial certification audit, the auditee informs the audit team leader that they wish to extend the audit scope to include two additional sites that have recently been acquired by the organisation.
Considering this information, what action would you expect the audit team leader to take?
- A . Increase the length of the Stage 2 audit to include the extra sites
- B . Obtain information about the additional sites to inform the certification body
- C . Arrange to complete a remote Stage 1 audit of the two sites using a video conferencing platform
- D . Inform the auditee that the request can be accepted but a full Stage 1 audit must be repeated
B
Explanation:
According to ISO/IEC 17021-1, which specifies the requirements for bodies providing audit and certification of management systems, a certification body should establish criteria for determining audit time and audit team composition based on factors such as the scope of certification, size and complexity of the organization, risks associated with its activities, etc2. Therefore, if an auditee requests to extend the audit scope to include two additional sites after completing Stage 1 of an initial certification audit, the audit team leader should obtain information about the additional sites to inform the certification body, so that they can review and approve the change in scope and adjust the audit time and audit team accordingly2. The other options are not appropriate actions for the audit team leader to take in this situation. For example, increasing the length of the Stage 2 audit to include the extra sites without informing the certification body may violate their procedures and policies; arranging to complete a remote Stage 1 audit of the two sites using a video conferencing platform may not be feasible or effective depending on the nature and location of the sites; and informing the auditee that the request can be accepted but a full Stage 1 audit must be repeated may not be necessary or reasonable if there are no significant changes in the auditee’s ISMS since Stage 12.
Reference: ISO/IEC 17021-1:2015 – Conformity assessment C Requirements for bodies providing audit and certification of management systems C Part 1: Requirements
Scenario 2: Knight is an electronics company from Northern California, US that develops video game consoles. Knight has more than 300 employees worldwide. On the fifth anniversary of their establishment, they have decided to deliver the G-Console, a new generation video game console aimed for worldwide markets. G-Console is considered to be the ultimate media machine of 2021 which will give the best gaming experience to players. The console pack will include a pair of VR headset, two games, and other gifts.
Over the years, the company has developed a good reputation by showing integrity, honesty, and respect toward their customers. This good reputation is one of the reasons why most passionate gamers aim to have Knight’s G-console as soon as it is released in the market. Besides being a very customer-oriented company, Knight also gained wide recognition within the gaming industry because of the developing quality. Their prices are a bit higher than the reasonable standards allow.
Nonetheless, that is not considered an issue for most loyal customers of Knight, as their quality is top-notch.
Being one of the top video game console developers in the world, Knight is also often the center of attention for malicious activities. The company has had an operational ISMS for over a year. The ISMS scope includes all departments of Knight, except Finance and HR departments.
Recently, a number of Knight’s files containing proprietary information were leaked by hackers. Knight’s incident response team (IRT) immediately started to analyze every part of the system and the details of the incident.
The IRT’s first suspicion was that Knight’s employees used weak passwords and consequently were easily cracked by hackers who gained unauthorized access to their accounts. However, after carefully investigating the incident, the IRT determined that hackers accessed accounts by capturing the file transfer protocol (FTP) traffic.
FTP is a network protocol for transferring files between accounts. It uses clear text passwords for authentication.
Following the impact of this information security incident and with IRT’s suggestion, Knight decided to replace the FTP with Secure Shell (SSH) protocol, so anyone capturing the traffic can only see encrypted data.
Following these changes, Knight conducted a risk assessment to verify that the implementation of controls had minimized the risk of similar incidents. The results of the process were approved by the ISMS project manager who claimed that the level of risk after the implementation of new controls was in accordance with the company’s risk acceptance levels.
Based on this scenario, answer the following question:
Which risk treatment option has Knight used in replacing FTP with SSH? Refer to scenario 2.
- A . Risk retention
- B . Risk avoidance
- C . Risk modification
C
Explanation:
Risk modification involves implementing controls to reduce the likelihood or impact of a risk. By replacing FTP with SSH, Knight has modified the risk associated with the transfer of files by ensuring that the data is encrypted, thereby reducing the likelihood of unauthorized access through traffic capturing1.
Reference: = This answer is based on the standard risk treatment options provided in ISO/IEC 27001, which include avoiding, modifying, sharing, or retaining risks as part of the risk management process