
Splunk SPLK-1005 Practice Exams
Last updated on Oct 06,2026- Exam Code: SPLK-1005
- Exam Name: Splunk Cloud Certified Admin
- Certification Provider: Splunk
- Latest update: Oct 06,2026
What is the correct syntax to monitor /apache/too/logo, /apache/bor/logs, and /apache/bar/l/logo?
A)
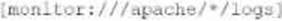
B)
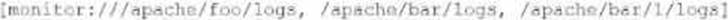
C)
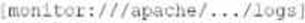
D)
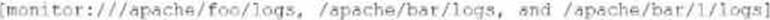
- A . Option A
- B . Option B
- C . Option C
- D . Option D
When adding a directory monitor and specifying a sourcetype explicitly, it applies to all files in the directory and subdirectories.
If automatic sourcetyping is used, a user can selectively override it in which file on the forwarder?
- A . transforms.conf
- B . props.conf
- C . inputs.conf
- D . outputs.cont
Which of the following is a valid stanza in props. conf?
- A . [sourcetype::linux_secure]
- B . [host=nyc25]
- C . [host::nyc*]
- D . [host:nyc*]
Which of the following would always require raising a support ticket?
- A . Capacity or configuration changes in Splunk Cloud.
- B . Search does not return expected results in Splunk Cloud.
- C . A user is unable to log into Splunk Cloud.
- D . Data is not indexed in Splunk Cloud.
What is the recommended approach to collect data from network devices?
- A . TCP/UDP Feed > Heavy Forwarder > Intermediate Forwarder > Splunk Cloud
- B . TCP/UDP Feed > Syslog Server with Universal Forwarder > Splunk Cloud
- C . TCP/UDP Feed > Universal Forwarder > Intermediate Forwarder > Splunk Cloud
- D . TCP/UDP Feed > Intermediate Forwarder > Heavy Forwarder > Splunk Cloud
A log file is being ingested into Splunk, and a few events have no date stamp.
How would Splunk first try to determine the missing date of the events?
- A . Splunk will take the date of a previous event within the log file.
- B . Splunk will use the current system time of the Indexer for the date.
- C . Splunk will use the date of when the file monitor was created.
- D . Splunk will take the date from the file modification time.
Due to internal security policies, a Splunk Cloud administrator cannot send data directly to Splunk Cloud from certain data sources. Additional parsing and API-based data sources also need to be sent to Splunk Cloud.
What forwarder type should the Splunk Cloud administrator use to satisfy these requirements within their environment?
- A . Syslog-ng server with a universal forwarder
- B . Light forwarder as an intermediate forwarder
- C . Heavy forwarder as an intermediate forwarder
- D . Universal forwarder as an intermediate forwarder
The following Apache access log is being ingested into Splunk via a monitor input:
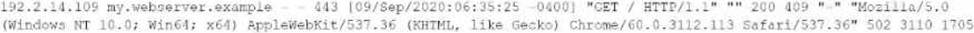
How does Splunk determine the time zone for this event?
- A . The value of the TZ attribute in props. cont for the a :ces3_ccwbined sourcetype.
- B . The value of the TZ attribute in props, conf for the my.webserver.example host.
- C . The time zone of the Heavy/Intermediate Forwarder with the monitor input.
- D . The time zone indicator in the raw event data.
A customer wants to mask unstructured data before sending it to Splunk Cloud. Where should SEBCMD be configured for this?
- A . props. conf on a Splunk Cloud search head,
- B . props.conf on a Heavy Forwarder.
- C . transforms, cent on a Splunk Cloud indexer.
- D . props. conf- on a Universal Forwarder.
What Splunk command will allow an administrator to view the runtime configuration instructions for a monitored file in Inputs. cont on the forwarders?
- A . ./splunk _internal call /services/data/input.3/filemonitor
- B . ./splunk show config inputs.conf
- C . ./splunk _internal rest /services/data/inputs/monitor
- D . ./splunk show config inputs