
Splunk SPLK-1002 Practice Exams
Last updated on Oct 06,2026- Exam Code: SPLK-1002
- Exam Name: Splunk Core Certified Power User
- Certification Provider: Splunk
- Latest update: Oct 06,2026
Two separate results tables are being combined using the join command.
The outer table has the following values:
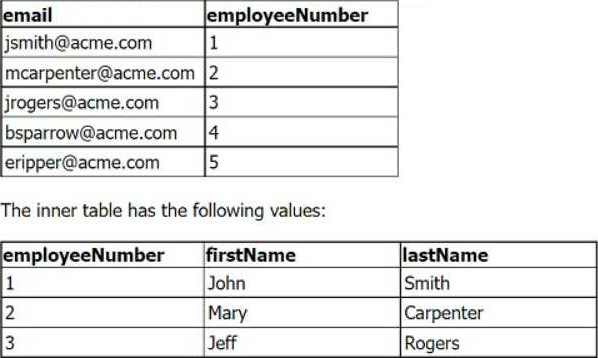
The line of SPL used to join the tables is: join employeeNumber type=outer
How many rows are returned in the new table?
- A . Three
- B . Eight
- C . Five
- D . Zero
Which of the following knowledge objects can reference field aliases?
- A . Calculated fields, lookups, event types, and tags.
- B . Calculated fields and tags only.
- C . Calculated fields and event types only.
- D . Calculated fields, lookups, event types, and extracted fields.
Which of the following statements describes field aliases?
- A . Field alias names replace the original field name.
- B . Field aliases can be used in lookup file definitions.
- C . Field aliases only normalize data across sources and sourcetypes.
- D . Field alias names are not case sensitive when used as part of a search.
This function of the stats command allows you to identify the number of values a field has.
- A . max
- B . distinct_count
- C . fields
- D . count
When using the transaction command, what does the argument maxspan do?
- A . Sets the maximum total time between events in a transaction.
- B . Sets the maximum length of all events within a transaction.
- C . Sets the maximum total time between the earliest and latest events in a transaction.
- D . Sets the maximum length that any single event can reach to be included in the transaction.
Given the following eval statement:
…| eval fieldl – if(isnotnull(fieldl),fieldl,0), field2 = if(isnull<field2>, "NO-VALUE", fieid2) Which of the following is the equivalent using f ilinull?
- A . There is no equivalent expression using f ilinull
- B . … t filinull values=(0,"NO-VALUE") fields=(fieldl,field2)
- C . … I filinull value=0 fieldl I fillnull fields
- D . … I fillnull fieldl I filinull value="NO-VALUE" field2
A data model consists of which three types of datasets?
- A . Constraint, field, value.
- B . Events, searches, transactions.
- C . Field extraction, regex, delimited.
- D . Transaction, session ID, metadata.
In most large Splunk environments, what is the most efficient command that can be used to group events by fields/
- A . join
- B . stats
- C . streamstats
- D . transaction
The stats command will create a _____________ by default.
- A . Table
- B . Report
- C . Pie chart
Which of the following commands connects an additional table of data directly to the right side of the existing table?
- A . subsearch
- B . update
- C . appendcols
- D . append