
Paloalto Networks NetSec-Generalist Practice Exams
Last updated on Oct 22,2026- Exam Code: NetSec-Generalist
- Exam Name: Palo Alto Networks Network Security Generalist
- Certification Provider: Paloalto Networks
- Latest update: Oct 22,2026
Which two components of a Security policy, when configured, allow third-party contractors access to internal applications outside business hours? (Choose two.)
- A . User-ID
- B . Schedule
- C . Service
- D . App-ID
A company uses Prisma Access to provide secure connectivity for mobile users to access its corporate-sanctioned Google Workspace and wants to block access to all unsanctioned Google Workspace environments.
What would an administrator configure in the snippet to achieve this goal?
- A . Dynamic Address Groups
- B . Tenant restrictions
- C . Dynamic User Groups
- D . URL category
How are content updates downloaded and installed for Cloud NGFWs?
- A . Through the management console
- B . Through Panorama
- C . Automatically
- D . From the Customer Support Portal
Which step is necessary to ensure an organization is using the inline cloud analysis features in its Advanced Threat Prevention subscription?
- A . Configure Advanced Threat Prevention profiles with default settings and only focus on high-risk traffic to avoid affecting network performance.
- B . Enable SSL decryption in Security policies to inspect and analyze encrypted traffic for threats.
- C . Update or create a new anti-spyware security profile and enable the appropriate local deep – learning models.
- D . Disable anti-spyware to avoid performance impacts and rely solely on external threat intelligence.
At a minimum, which action must be taken to ensure traffic coming from outside an organization to the DMZ can access the DMZ zone for a company using private IP address space?
- A . Configure static NAT for all incoming traffic.
- B . Create NAT policies on post-NAT addresses for all traffic destined for DMZ.
- C . Configure NAT policies on the pre-NAT addresses and post-NAT zone.
- D . Create policies only for pre-NAT addresses and any destination zone.
An IT security administrator is maintaining connectivity and security between on-premises infrastructure, private cloud, and public cloud environments in Strata Cloud Manager (SCM).
Which set of practices must be implemented to effectively manage certificates and ensure secure communication across these segmented environments?
- A . Use a centralized certificate management solution. Regularly renew and update certificates.
Employ strong encryption protocols. - B . Use self-signed certificates for all environments. Renew certificates manually once a year.
Avoid automating certificate management to maintain control. - C . Rely on the cloud provider’s default certificates.
Avoid renewing certificates to reduce overhead and complexity. Manage certificate deployment manually. - D . Implement different certificate authorities (CAs) for each environment. Use default certificate settings.
Renew certificates only when they expire to reduce overhead and complexity.
Refer to the exhibit.
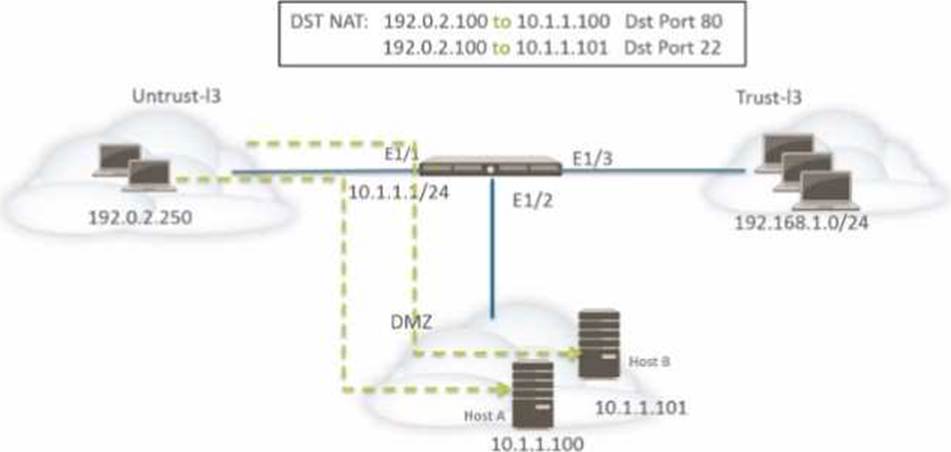
A network administrator is using DNAT to map two servers to one public IP address. Traffic will be directed to a specific server based on the application, where Host A (10.1.1.100) receives HTTP traffic and Host B (10.1.1.101) receives SSH traffic.
Which two sets of Security policy rules will accomplish this configuration? (Choose two.)
- A . Source: Untrust (Any) Destination: Untrust Application(s): web-browsing Action: allow
- B . Source: Untrust (Any) Destination: Trust Application(s): web-browsing, ssh Action: allow
- C . Source: Untrust (Any) Destination: DMZ Application(s): web-browsing Action: allow
- D . Source: Untrust (Any) Destination: DMZ Application(s): ssh Action: allow
Which Cloud-Delivered Security Services (CDSS) solution is required to configure and enable Advanced DNS Security?
- A . Advanced WildFire
- B . Enterprise SaaS Security
- C . Advanced Threat Prevention
- D . Advanced URL Filtering
Why would an enterprise architect use a Zero Trust Network Access (ZTNA) connector instead of a service connection for private application access?
- A . It controls traffic from the mobile endpoint to any of the organization’s internal resources.
- B . It functions as the attachment point for IPSec-based connections to remote site or branch networks.
- C . It supports traffic sourced from on-premises or public cloud-based resources to mobile users and remote networks.
- D . It automatically discovers private applications and suggests Security policy rules for them.
Which functionality does an NGFW use to determine whether new session setups are legitimate or illegitimate?
- A . SYN flood protection
- B . SYN bit
- C . Random Early Detection (RED)
- D . SYN cookies