
Palo Alto Networks PCNSE Practice Exams
Last updated on Oct 21,2026- Exam Code: PCNSE
- Exam Name: Palo Alto Networks Certified Network Security Engineer Exam
- Certification Provider: Palo Alto Networks
- Latest update: Oct 21,2026
A network administrator configured a site-to-site VPN tunnel where the peer device will act as initiator None of the peer addresses are known
What can the administrator configure to establish the VPN connection?
- A . Set up certificate authentication.
- B . Use the Dynamic IP address type.
- C . Enable Passive Mode
- D . Configure the peer address as an FQDN.
A network engineer has discovered that asymmetric routing is causing a Palo Alto Networks firewall to drop traffic. The network architecture cannot be changed to correct this.
Which two actions can be taken on the firewall to allow the dropped traffic permanently? (Choose two.)
- A . Navigate to Network > Zone Protection Click Add
Select Packet Based Attack Protection > TCP/IP Drop Set "Reject Non-syn-TCP" to No Set "Asymmetric Path" to Bypass - B . > set session tcp-reject-non-syn no
- C . Navigate to Network > Zone Protection Click Add
Select Packet Based Attack Protection > TCP/IP Drop Set "Reject Non-syn-TCP" to Global Set "Asymmetric Path" to Global - D . # set deviceconfig setting session tcp-reject-non-syn no
A security engineer needs firewall management access on a trusted interface.
Which three settings are required on an SSL/TLS Service Profile to provide secure Web UI authentication? (Choose three.)
- A . Minimum TLS version
- B . Certificate
- C . Encryption Algorithm
- D . Maximum TLS version
- E . Authentication Algorithm
After importing a pre-configured firewall configuration to Panorama, what step is required to ensure a commit/push is successful without duplicating local configurations?
- A . Ensure Force Template Values is checked when pushing configuration.
- B . Push the Template first, then push Device Group to the newly managed firewall.
- C . Perform the Export or push Device Config Bundle to the newly managed firewall.
- D . Push the Device Group first, then push Template to the newly managed firewall
A firewall engineer creates a new App-ID report under Monitor > Reports > Application Reports > New Applications to monitor new applications on the network and better assess any Security policy updates the engineer might want to make.
How does the firewall identify the New App-ID characteristic?
- A . It matches to the New App-IDs downloaded in the last 90 days.
- B . It matches to the New App-IDs in the most recently installed content releases.
- C . It matches to the New App-IDs downloaded in the last 30 days.
- D . It matches to the New App-IDs installed since the last time the firewall was rebooted.
An engineer is configuring a template in Panorama which will contain settings that need to be applied to all firewalls in production.
Which three parts of a template an engineer can configure? (Choose three.)
- A . NTP Server Address
- B . Antivirus Profile
- C . Authentication Profile
- D . Service Route Configuration
- E . Dynamic Address Groups
Which two statements correctly describe Session 380280? (Choose two.)
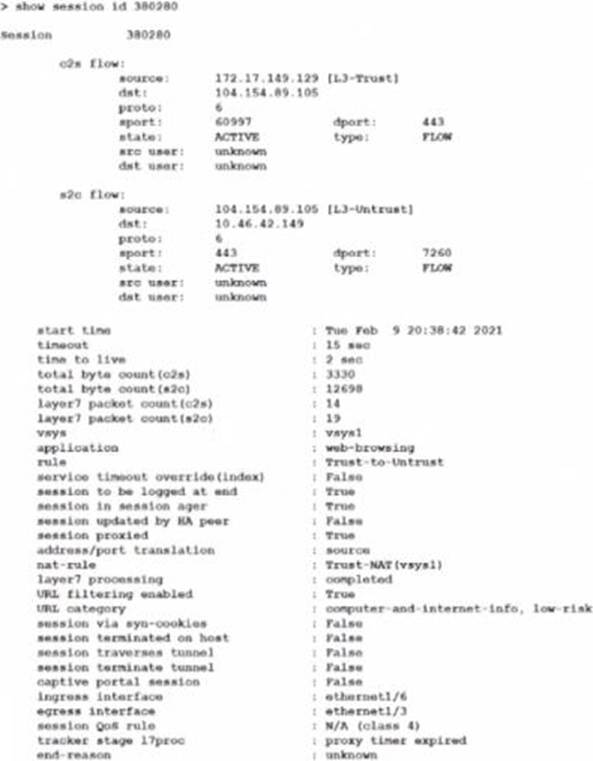
- A . The session went through SSL decryption processing.
- B . The session has ended with the end-reason unknown.
- C . The application has been identified as web-browsing.
- D . The session did not go through SSL decryption processing.
Which three actions can Panorama perform when deploying PAN-OS images to its managed devices? (Choose three.)
- A . upload-onlys
- B . install and reboot
- C . upload and install
- D . upload and install and reboot
- E . verify and install
An engineer is monitoring an active/active high availability (HA) firewall pair.
Which HA firewall state describes the firewall that is experiencing a failure of a monitored path?
- A . Initial
- B . Tentative
- C . Passive
- D . Active-secondary
A network security administrator wants to inspect HTTPS traffic from users as it egresses through a firewall to the Internet/Untrust zone from trusted network zones.
The security admin wishes to ensure that if users are presented with invalid or untrusted security
certificates, the user will see an untrusted certificate warning.
What is the best choice for an SSL Forward Untrust certificate?
- A . A web server certificate signed by the organization’s PKI
- B . A self-signed certificate generated on the firewall
- C . A subordinate Certificate Authority certificate signed by the organization’s PKI
- D . A web server certificate signed by an external Certificate Authority