
Palo Alto Networks PCNSA Practice Exams
Last updated on Oct 22,2026- Exam Code: PCNSA
- Exam Name: Palo Alto Networks Certified Network Security Administrator
- Certification Provider: Palo Alto Networks
- Latest update: Oct 22,2026
Which data-plane processor layer of the graphic shown provides uniform matching for spyware and vulnerability exploits on a Palo Alto Networks Firewall?
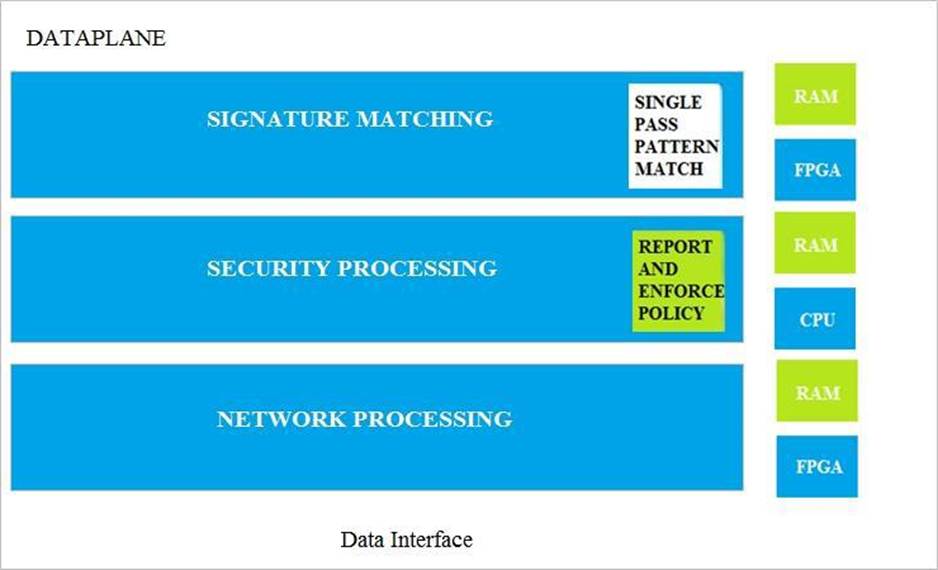
- A . Signature Matching
- B . Network Processing
- C . Security Processing
- D . Security Matching
By default, which action is assigned to the intrazone-default rule?
- A . Reset-client
- B . Reset-server
- C . Deny
- D . Allow
What is the purpose of the automated commit recovery feature?
- A . It reverts the Panorama configuration.
- B . It reverts the Panorama configuration.
- C . It reverts the firewall configuration if the firewall recognizes a loss of connectivity to Panorama after the change.
- D . It generates a config log after the Panorama configuration successfully reverts to the last running configuration.
What are two valid selections within an Antivirus profile? (Choose two.)
- A . deny
- B . drop
- C . default
- D . block-ip
All users from the internal zone must be allowed only HTTP access to a server in the DMZ zone.
Complete the empty field in the Security policy using an application object to permit only this type of access.
Source Zone: Internal
Destination Zone: DMZ Zone
Application: _________
Service: application-default
Action: allow
- A . Application = "any"
- B . Application = "web-browsing"
- C . Application = "ssl"
- D . Application = "http"
In which threat profile object would you configure the DNS Security service?
- A . Anti-Spyware
- B . URL Filtering
- C . Antivirus
- D . WildFire
A server-admin in the USERS-zone requires SSH-access to all possible servers in all current and future Public Cloud environments. All other required connections have already been enabled between the USERS-and the OUTSIDE-zone.
What configuration-changes should the Firewall-admin make?
- A . Create a custom-service-object called SERVICE-SSH for destination-port-TCP-22. Create a security-rule between zone USERS and OUTSIDE to allow traffic from any source IP-address to any destination IP-address for SERVICE-SSH
- B . Create a security-rule that allows traffic from zone USERS to OUTSIDE to allow traffic from any source IP-address to any destination IP-address for application SSH
- C . In addition to option a, a custom-service-object called SERVICE-SSH-RETURN that contains source-port-TCP-22 should be created. A second security-rule is required that allows traffic from zone OUTSIDE to USERS for SERVICE-SSH-RETURN for any source-IP-address to any destination-Ip-address
- D . In addition to option c, an additional rule from zone OUTSIDE to USERS for application SSH from any source-IP-address to any destination-IP-address is required to allow the return-traffic from the SSH-servers to reach the server-admin
Which five Zero Trust concepts does a Palo Alto Networks firewall apply to achieve an integrated approach to prevent threats? (Choose five.)
- A . User identification
- B . Filtration protection
- C . Vulnerability protection
- D . Antivirus
- E . Application identification
- F . Anti-spyware