
Palo Alto Networks PCNSA Practice Exams
Last updated on Oct 23,2026- Exam Code: PCNSA
- Exam Name: Palo Alto Networks Certified Network Security Administrator
- Certification Provider: Palo Alto Networks
- Latest update: Oct 23,2026
A network administrator created an intrazone Security policy rule on the firewall. The source zones were set to IT. Finance, and HR.
Which two types of traffic will the rule apply to? (Choose two)
- A . traffic between zone IT and zone Finance
- B . traffic between zone Finance and zone HR
- C . traffic within zone IT
- D . traffic within zone HR
Given the network diagram, which two statements are true about traffic between the User and Server networks? (Choose two.)
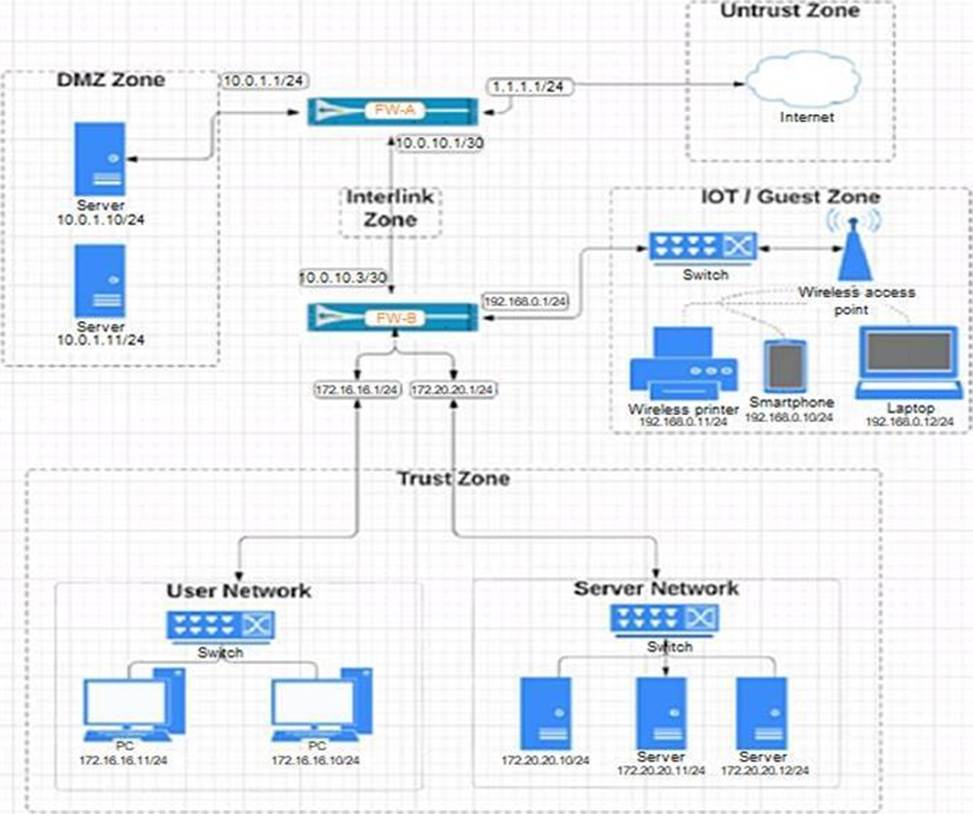
- A . Traffic is permitted through the default Intrazone "allow" rule.
- B . Traffic restrictions are not possible because the networks are in the same zone.
- C . Traffic is permitted through the default Interzone "allow" rule.
- D . Traffic restrictions are possible by modifying Intrazone rules.
Which administrative management services can be configured to access a management interface?
- A . HTTP, CLI, SNMP, HTTPS
- B . HTTPS, SSH, telnet, SNMP
- C . SSH, telnet, HTTP, HTTPS
- D . HTTPS, HTTP, CLI, API
Which Palo Alto networks security operating platform service protects cloud-based application such as Dropbox and salesforce by monitoring permissions and shared and scanning files for Sensitive information?
- A . Prisma SaaS
- B . AutoFocus
- C . Panorama
- D . GlobalProtect
Which Palo Alto networks security operating platform service protects cloud-based application such as Dropbox and salesforce by monitoring permissions and shared and scanning files for Sensitive information?
- A . Prisma SaaS
- B . AutoFocus
- C . Panorama
- D . GlobalProtect
Which Palo Alto networks security operating platform service protects cloud-based application such as Dropbox and salesforce by monitoring permissions and shared and scanning files for Sensitive information?
- A . Prisma SaaS
- B . AutoFocus
- C . Panorama
- D . GlobalProtect
Which component is a building block in a Security policy rule?
- A . decryption profile
- B . destination interface
- C . timeout (min)
- D . application
Which type of profile must be applied to the Security policy rule to protect against buffer overflows, illegal code execution, and other attempts to exploit system flaws?
- A . URL filtering
- B . vulnerability protection
- C . file blocking
- D . anti-spyware
Given the topology, which zone type should zone A and zone B to be configured with?
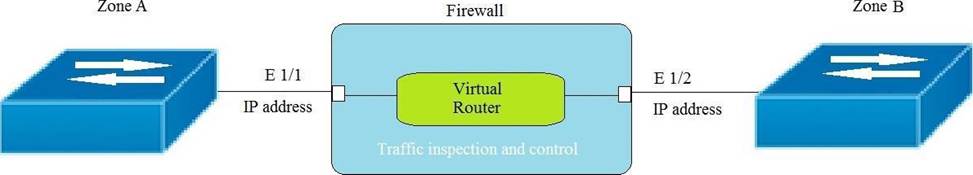
- A . Layer3
- B . Tap
- C . Layer2
- D . Virtual Wire
You receive notification about a new malware that infects hosts. An infection results in the infected host attempting to contact a command-and-control server.
Which Security Profile when applied to outbound Security policy rules detects and prevents this threat from establishing a command-and-control connection?
- A . Antivirus Profile
- B . Data Filtering Profile
- C . Vulnerability Protection Profile
- D . Anti-Spyware Profile