
Microsoft SC-300 Practice Exams
Last updated on Nov 16,2026- Exam Code: SC-300
- Exam Name: Microsoft Identity and Access Administrator
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
DRAG DROP
Your network contains an Active Directory forest named contoso.com that is linked to an Azure Active Directory (Azure AD) tenant named contoso.com by using Azure AD Connect.
Attire AD Connect is installed on a server named Server 1.
You deploy a new server named Server? that runs Windows Server 2019.
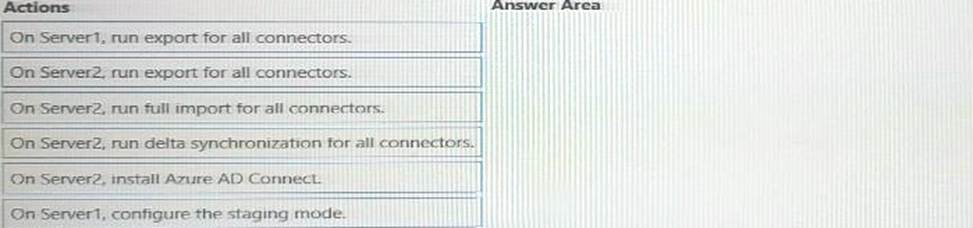
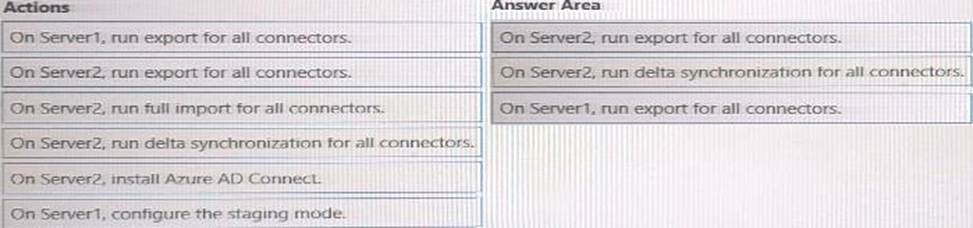
You need to implement a failover server for Azure AD Connect. The solution must minimize how long it takes to fail over if Server1 fails.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
HOTSPOT
You have a Microsoft 365 tenant that contains a group named Group1 as shown in the Group1 exhibit. (Click the Group1 tab.)
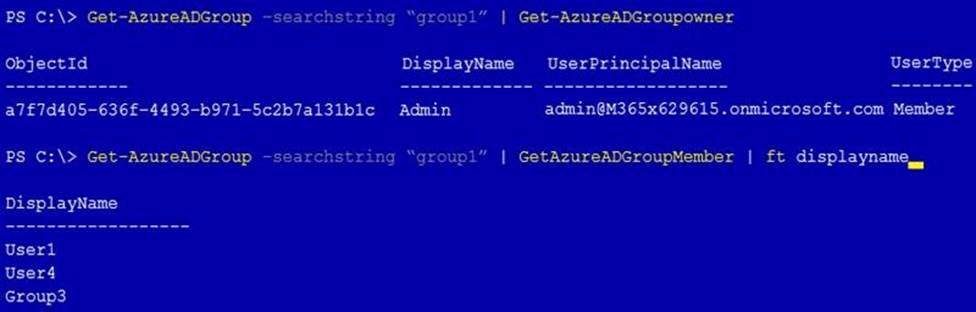
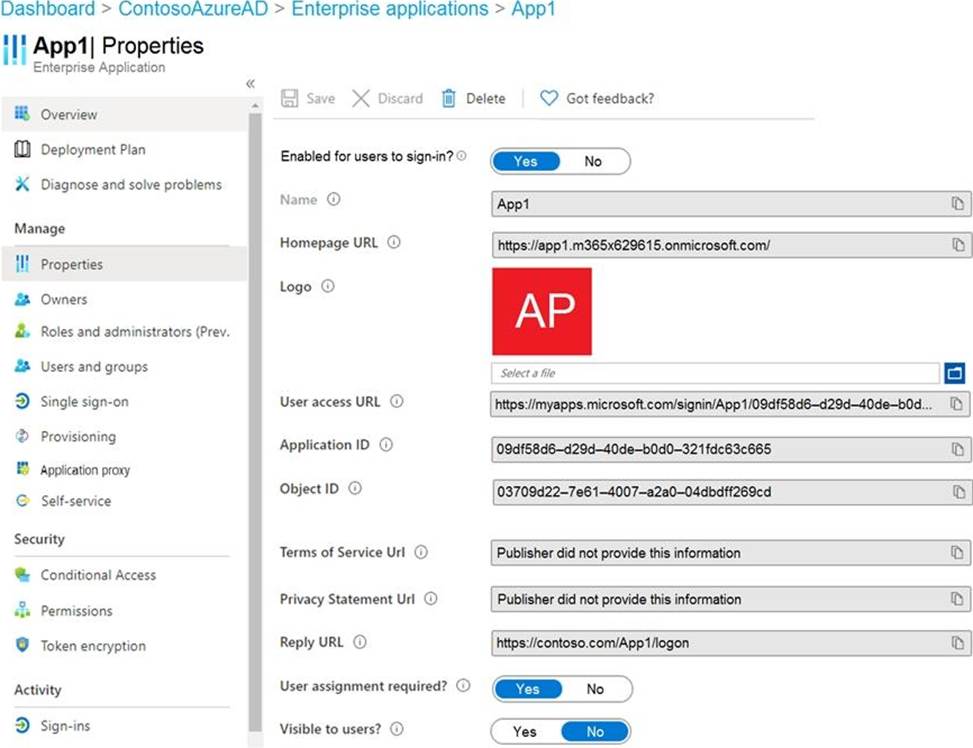
You create an enterprise application named App1 as shown in the App1 Properties exhibit. (Click the App1 Properties tab.)
You configure self-service for App1 as shown in the App1 Self-service exhibit. (Click the App1 Self-service tab.)
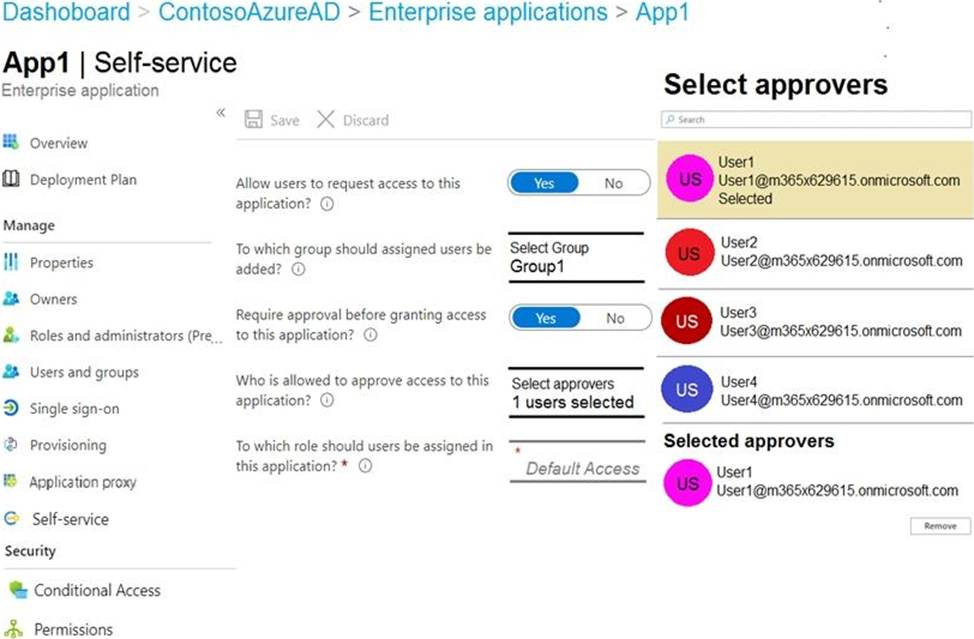
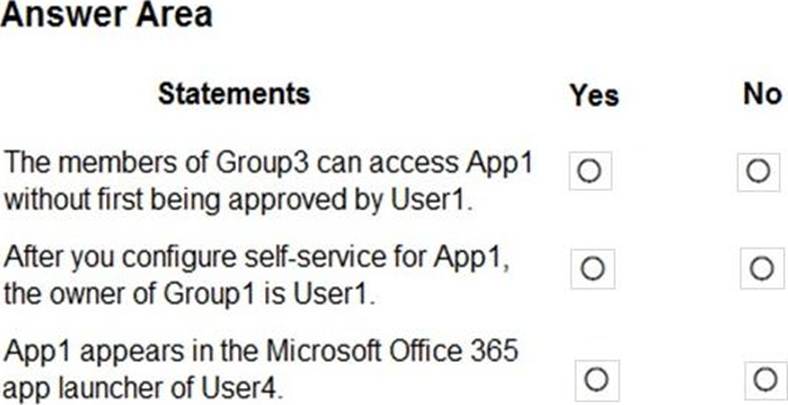
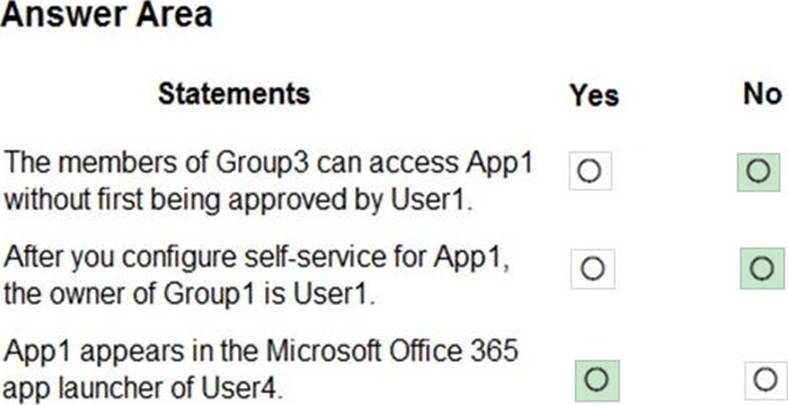
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
HOTSPOT
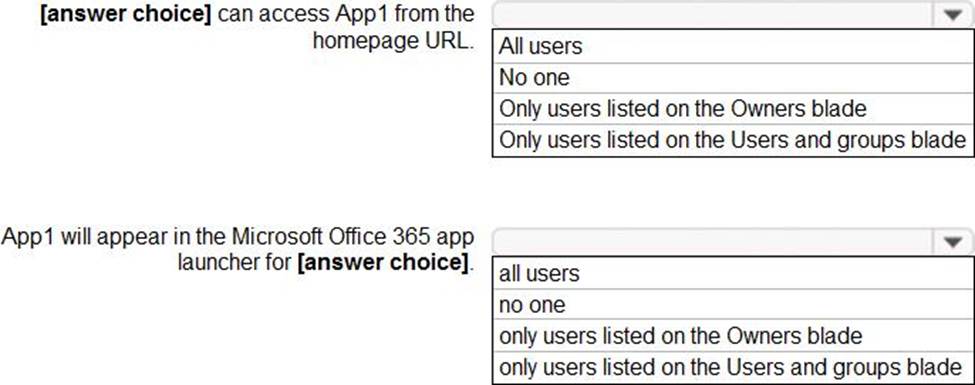
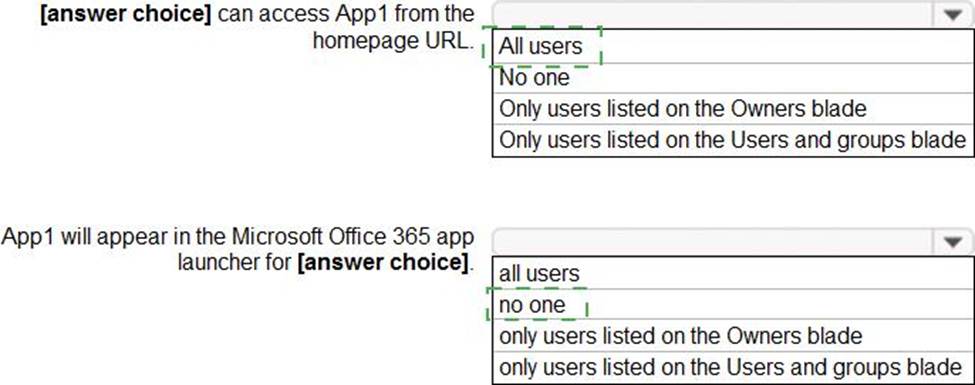
You have a custom cloud app named App1 that is registered in Azure Active Directory (Azure AD).
App1 is configured as shown in the following exhibit.
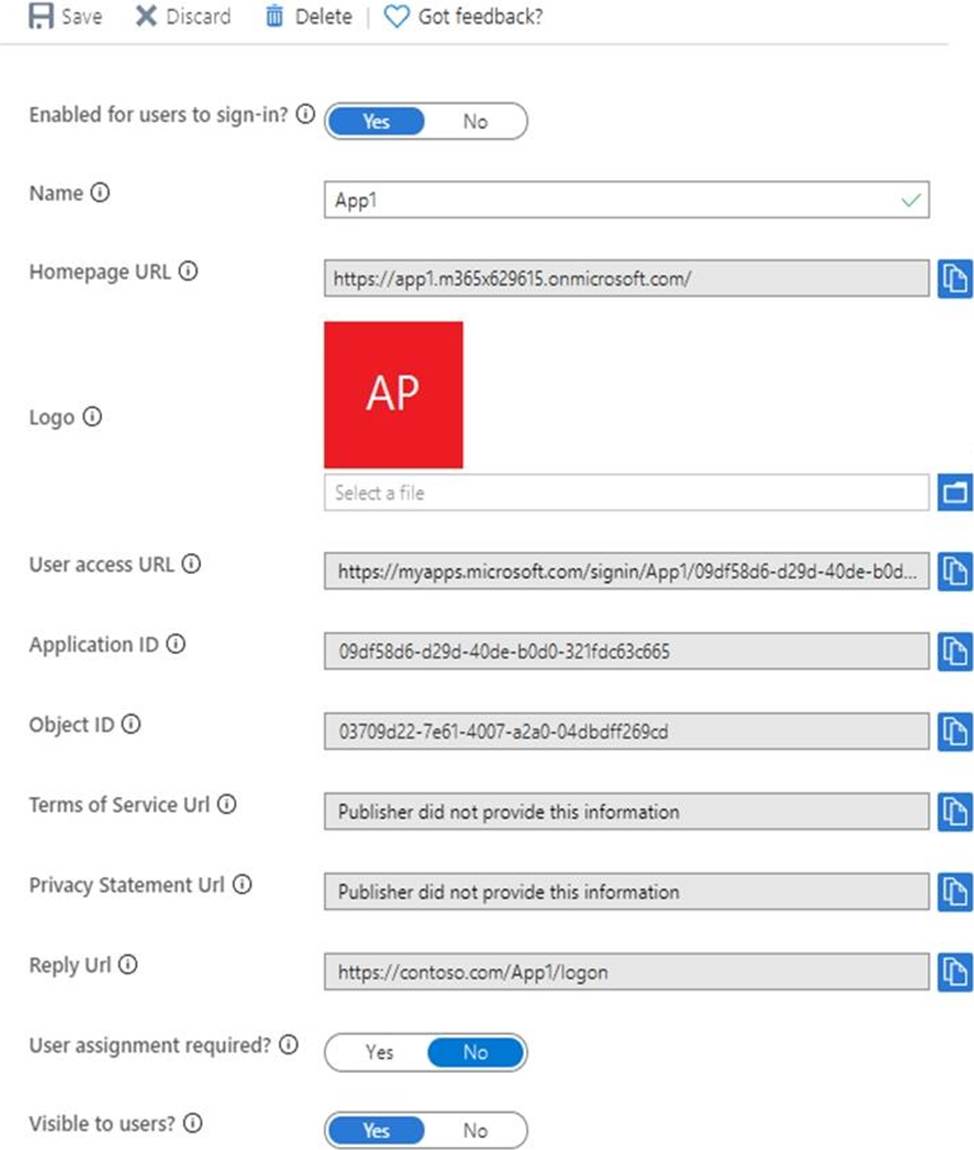
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.
You need to resolve the issue of I-.Group1.
What should you do first?
- A . Recreate the IT-Group 1 group.
- B . Change Membership type of IT-Group1 to Dynamic Device
- C . Add an owner to IT_Group1.
- D . Change Membership type of IT-Group1 to Dynamic User
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant that syncs to an Active Directory forest.
You discover that when a user account is disabled in Active Directory, the disabled user can still authenticate to Azure AD for up to 30 minutes.
You need to ensure that when a user account is disabled in Active Directory, the user account is immediately prevented from authenticating to Azure AD.
Solution: You configure password writeback.
Does this meet the goal?
- A . Yes
- B . No