Microsoft MS-102 Practice Exams
Last updated on Nov 16,2026- Exam Code: MS-102
- Exam Name: Microsoft 365 Administrator
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
You have a Microsoft 365 E5 subscription.
You need to identify which users accessed Microsoft Office 365 from anonymous IP addresses during the last seven days.
What should you do?
- A . From the Cloud App Security admin center, select Users and accounts.
- B . From the Microsoft 365 security center, view the Threat tracker.
- C . From the Microsoft 365 admin center, view the Security & compliance report.
- D . From the Azure Active Directory admin center, view the Risky sign-ins report.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a computer that runs Windows 10.
You need to verify which version of Windows 10 is installed.
Solution: From Device Manager, you view the computer properties.
Does this meet the goal?
- A . Yes
- B . No
HOTSPOT
Your company uses Microsoft Defender for Endpoint.
The devices onboarded to Microsoft Defender for Endpoint are shown in the following table.
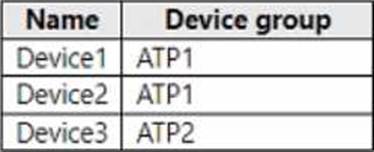
The alerts visible in the Microsoft Defender for Endpoint alerts queue are shown in the following table.
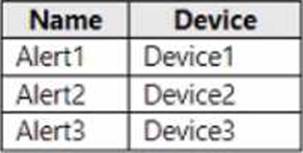
You create a suppression rule that has the following settings:
• Triggering IOC: Any IOC
• Action: Hide alert
• Suppression scope: Alerts on ATP1 device group
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.
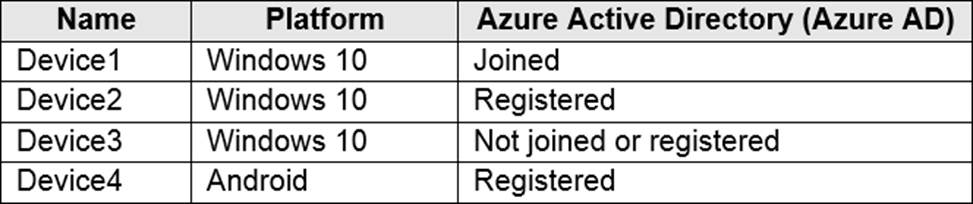
You plan to review device startup performance issues by using Endpoint analytics.
Which devices can you monitor by using Endpoint analytics?
- A . Device1 only
- B . Device1 and Device2 only
- C . Device1, Device2, and Device3 only
- D . Device1, Device2, and Device4 only
- E . Device1, Device2, Device3, and Device4
HOTSPOT
You have a Microsoft 365 E5 tenant
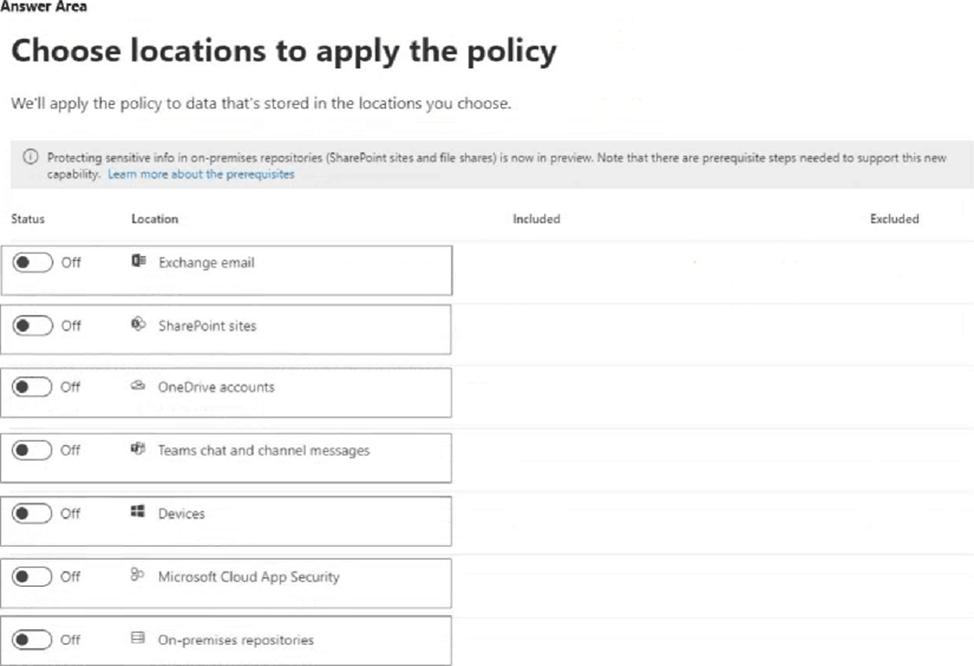
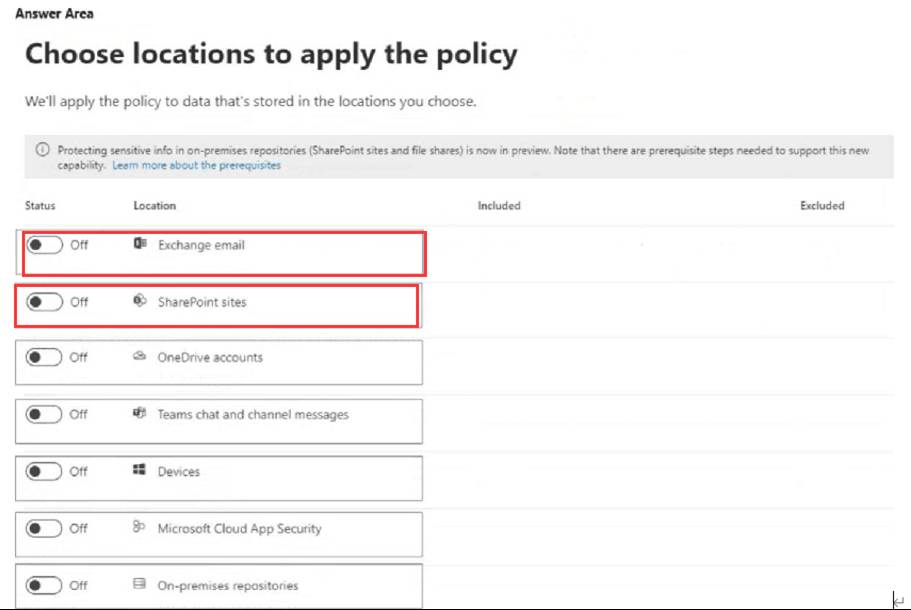
You create a data toss prevention (DLP) policy to prevent users from using Microsoft Teams to share internal documents with external users.
To which two locations should you apply the policy? To answer, select the appropriate locations in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that contains the domains shown in the following exhibit.
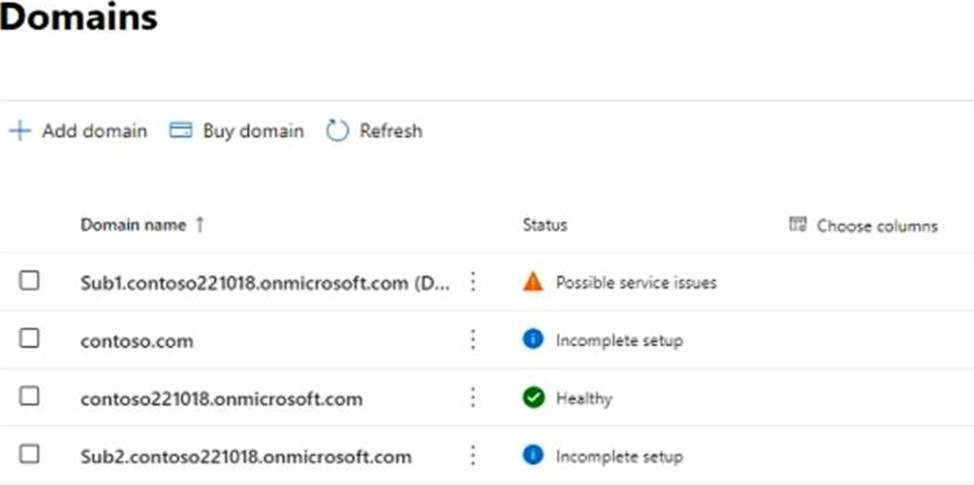
Which domain name suffixes can you use when you create users?
- A . only Sub1.contoso221018.onmicrosoft.com
- B . onlycontoso.com and Sub2.contoso221018.onmicrosoft.com
- C . onlvcontoso221018.onmicrosoft.com, Sub.contoso221018.onmicrosoft.com, and Sub2.contoso221018.onmicrosoft.com
- D . all the domains in the subscription
HOTSPOT
You have a Microsoft 365 E5 tenant that contains 100 Windows 10 devices.
You plan to attack surface reduction (ASR) rules for the Windows 10 devices.
You configure the ASR rules in audit mode and collect audit data in a Log Analytics workspace.
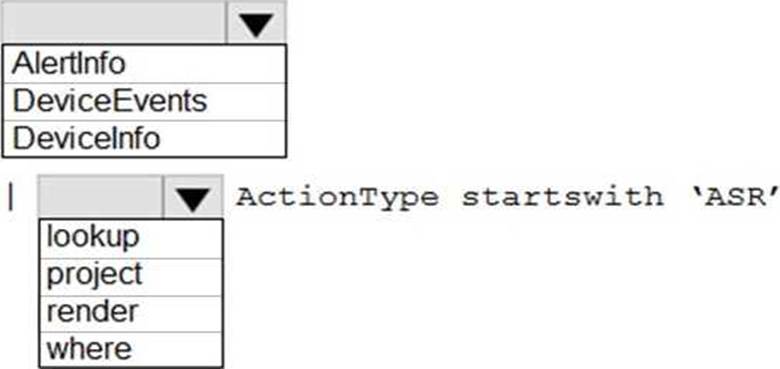
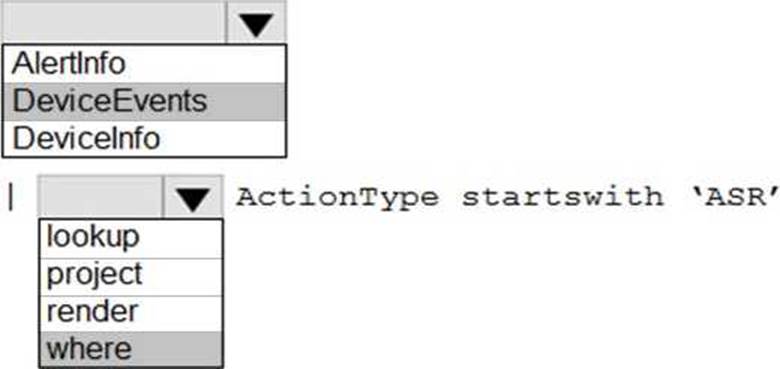
You need to find the ASR rules that match the activities on the devices.
How should you complete the Kusto query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
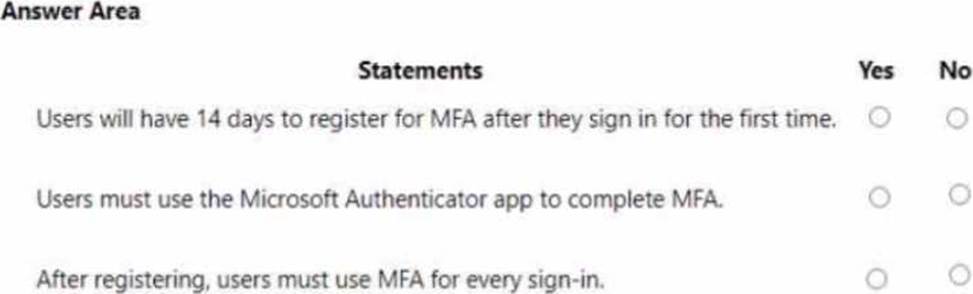
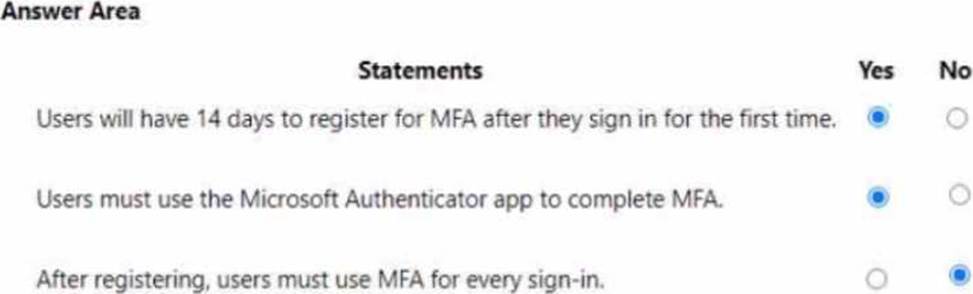
You are evaluating the use of multi-factor authentication (MFA).
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 E5 subscription that has published sensitivity labels shown in the following exhibit.
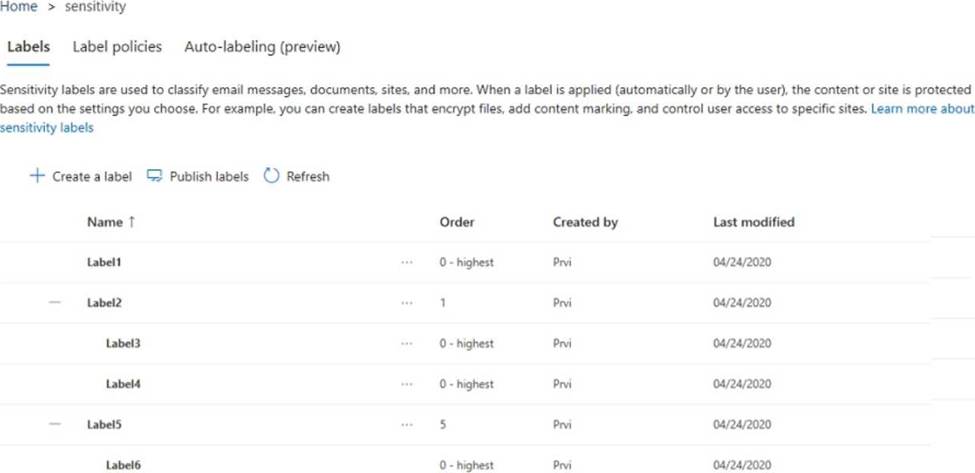
Which labels can users apply to content?
- A . Label1, Label2, and Label5 only
- B . Label3. Label4, and Label6 only
- C . Label1, Label3, Labe2, and Label6 only
- D . Label1, Label2, Label3, Label4, Label5. and Label6
HOTSPOT
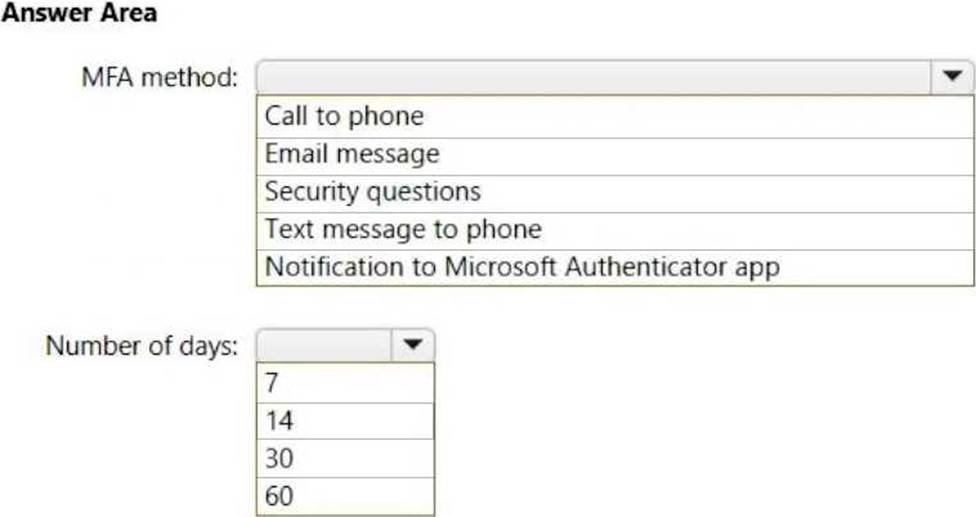
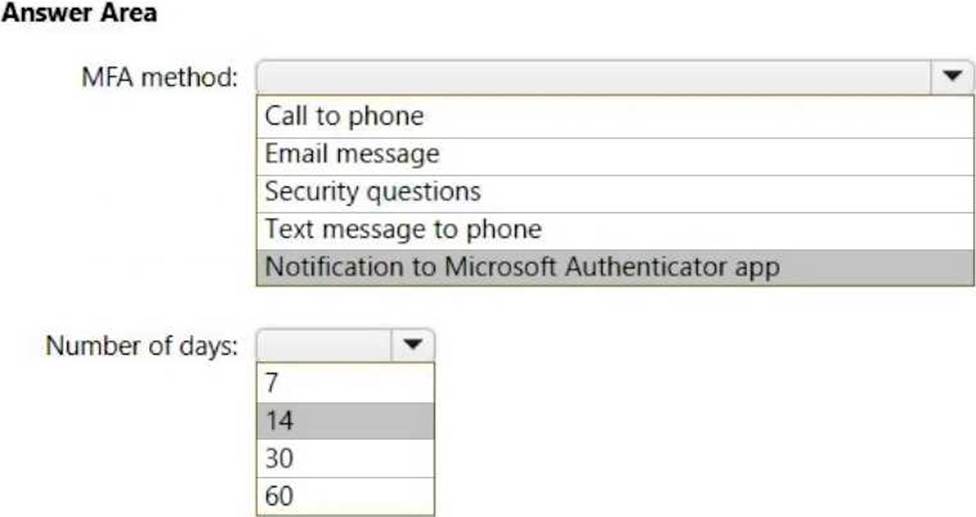
You have a new Microsoft 365 E5 tenant.
Enable Security defaults is set to Yes.
A user signs in to the tenant for the first time.
Which multi-factor authentication (MFA) method can the user use, and how many days does the user have to register for MFA? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.