
Microsoft MS-102 Practice Exams
Last updated on Nov 16,2026- Exam Code: MS-102
- Exam Name: Microsoft 365 Administrator
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
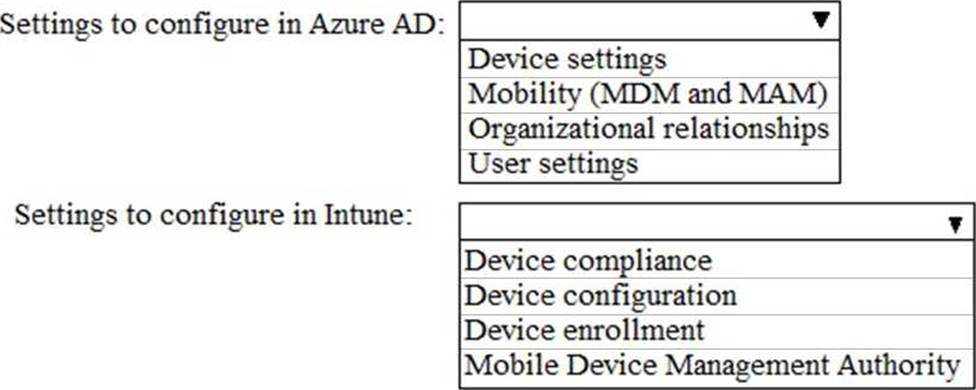
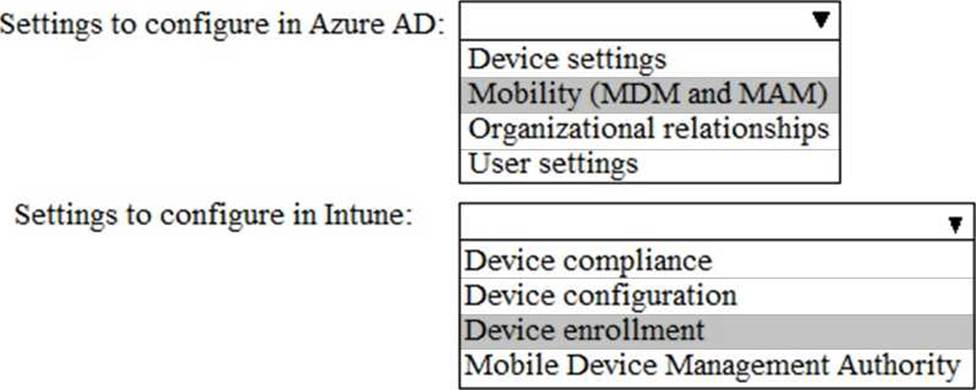
HOTSPOT
You need to meet the Intune requirements for the Windows 10 devices.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 E5 tenant that contains a user named User1.
You plan to implement insider risk management.
You need to ensure that User1 can perform the following tasks:
– Review alerts.
– Manage cases.
– Create notice templates.
– Review user emails by using Content explorer.
The solution must use the principle of least privilege.
To which role group should you add User1?
- A . Insider Risk Management
- B . Insider Risk Management Analysts
- C . Insider Risk Management Investigators
- D . Insider Risk Management Admin
You have a Microsoft 365 E5 tenant.
You need to evaluate compliance with European Union privacy regulations for customer data.
What should you do in the Microsoft 365 compliance center?
- A . Create a Data Subject Request (DSR)
- B . Create a data loss prevention (DLP) policy for General Data Protection Regulation (GDPR) data
- C . Create an assessment based on the EU GDPR assessment template
- D . Create an assessment based on the Data Protection Baseline assessment template
DRAG DROP
You have a Microsoft 365 subscription.
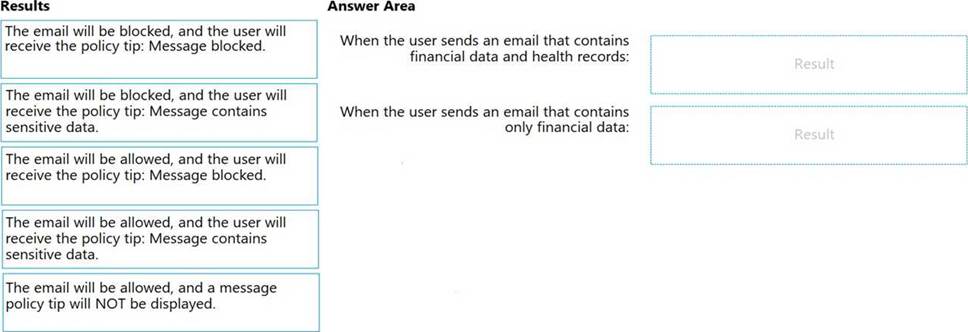
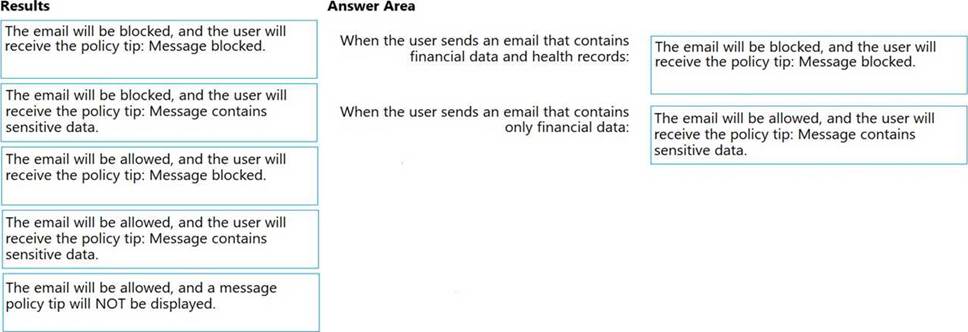
In the Exchange admin center, you have a data loss prevention (DLP) policy named Policy1 that has the following configurations:
– Block emails that contain financial data.
– Display the following policy tip text: Message blocked.
From the Security & Compliance admin center, you create a DLP policy named Policy2 that has the following configurations:
– Use the following location: Exchange email.
– Display the following policy tip text: Message contains sensitive data.
When a user sends an email, notify the user if the email contains health records.
What is the result of the DLP policies when the user sends an email? To answer, drag the appropriate results to the correct scenarios. Each result may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.
HOTSPOT
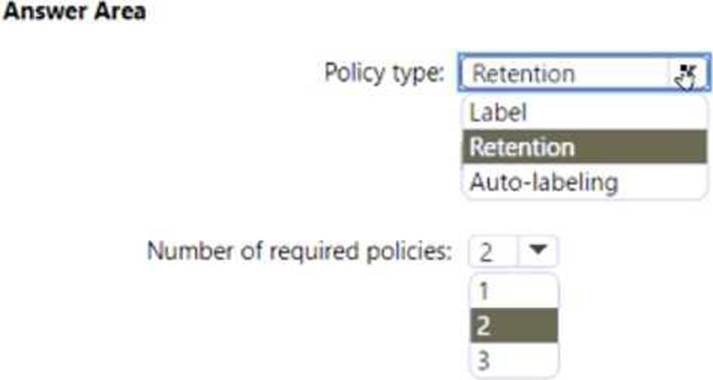
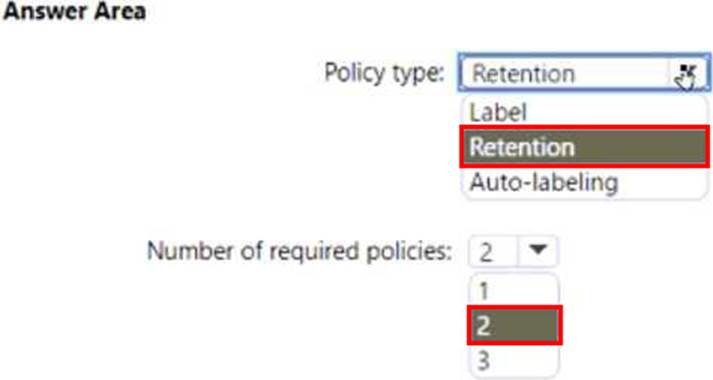
You need to configure the information governance settings to meet the technical requirements.
Which type of policy should you configure, and how many policies should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
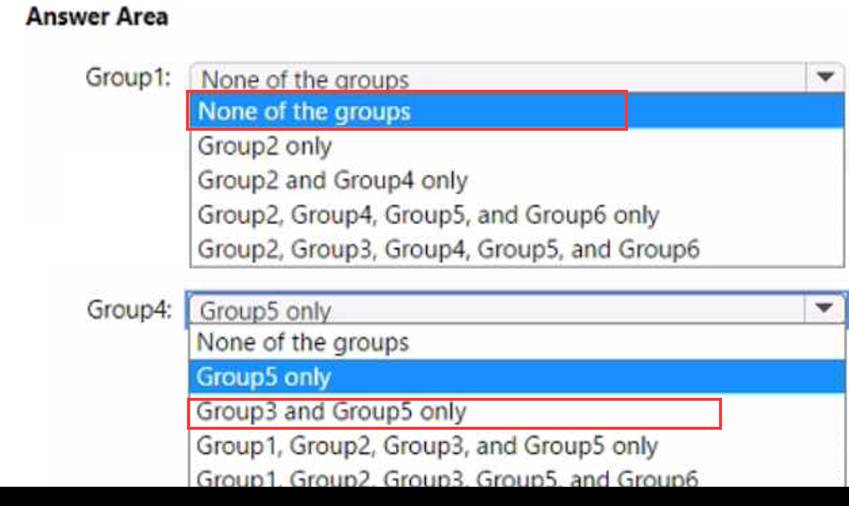
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.
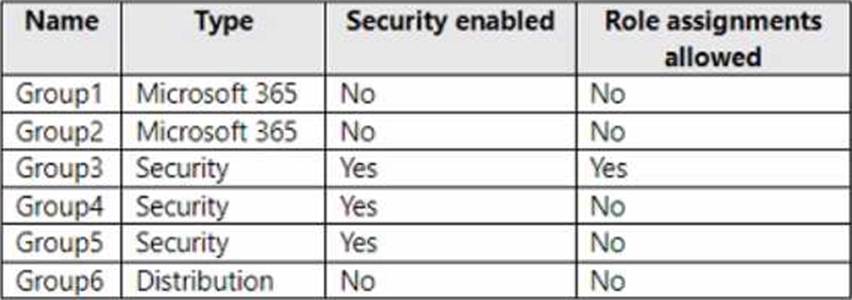
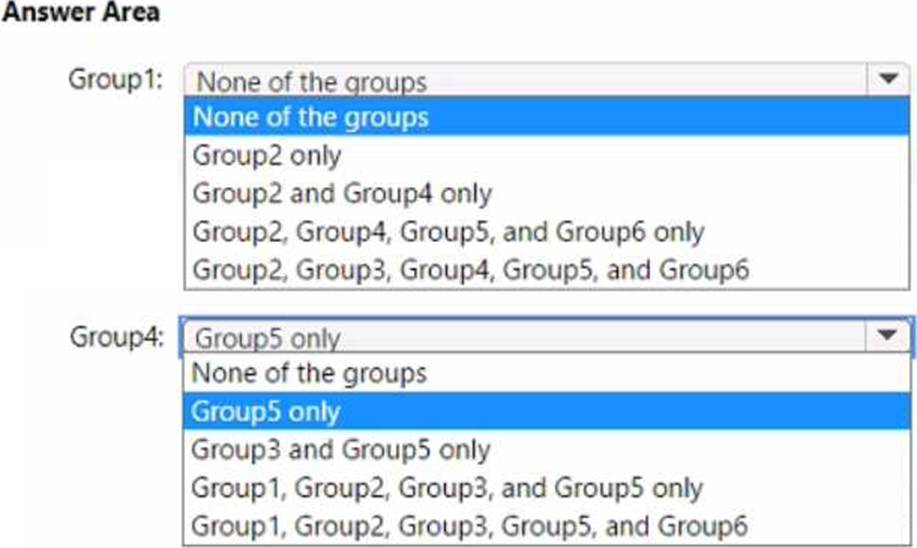
Which groups can be members of Group1 and Group4? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
Your network contains an Active Directory domain.
You deploy an Azure AD tenant.
Another administrator configures the domain to synchronize to Azure AD.
You discover that 10 user accounts in an organizational unit (OU) are NOT synchronized to Azure AD.
All the other user accounts synchronized successfully.
You review Azure AD Connect Health and discover that all the user account synchronizations completed successfully.
You need to ensure that the 10 user accounts are synchronized to Azure AD.
Solution: From Azure AD Connect, you modify the filtering settings.
Does this meet the goal?
- A . Yes
- B . No
You have a Microsoft 365 E5 subscription.
You need to create Conditional Access policies to meet the following requirements:
All users must use multi-factor authentication (MFA) when they sign in from outside the corporate network.
Users must only be able to sign in from outside the corporate network if the sign-in originates from a compliant device.
All users must be blocked from signing in from outside the United States and Canada.
Only users in the R&D department must be blocked from signing in from both Android and iOS devices.
Only users in the finance department must be able to sign in to an Azure AD enterprise application named App1. All other users must be blocked from signing in to App1.
What is the minimum number of Conditional Access policies you should create?
- A . 3
- B . 4
- C . 5
- D . 6
- E . 7
- F . 8
You need to ensure that User1 can enroll the devices to meet the technical requirements.
What should you do?
- A . From the Azure Active Directory admin center, assign User1 the Cloud device administrator rote.
- B . From the Azure Active Directory admin center, configure the Maximum number of devices per user setting.
- C . From the Intune admin center, add User1 as a device enrollment manager.
- D . From the Intune admin center, configure the Enrollment restrictions.
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Cloud Apps.
You need to be notified when a single user downloads more than 50 files during any 60-second period.
What should you configure?
- A . a session policy
- B . a file policy
- C . an activity policy
- D . an anomaly detection policy