
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
HOTSPOT
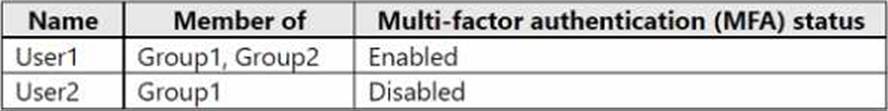
You have a Microsoft Entra tenant that contains the users shown in the following table.
You create and enforce a Microsoft Entra Identity Protection sign-in risk policy that has the following settings:
• Assignments: Include Group1, exclude Group2
• Conditions: Sign-in risk level: Low and above
• Access: Allow access, Require multi-factor authentication
You need to identify what occurs when the users sign in to Microsoft Entra ID.
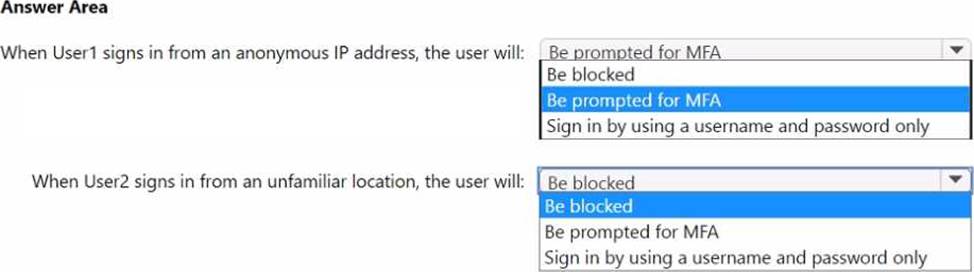
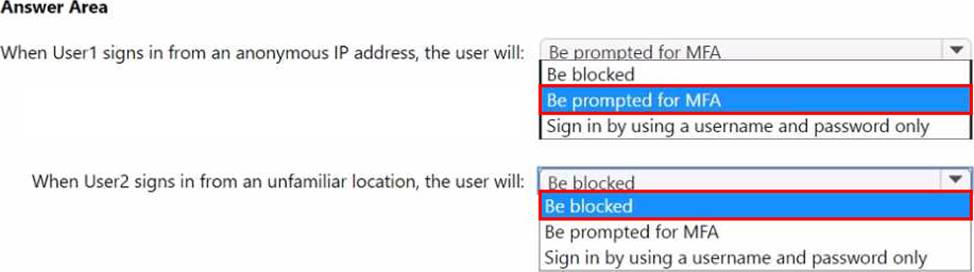
What should you identify for each user? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription.
You plan to map an online infrastructure and perform vulnerability scanning for the following:
• ASNs
• Hostnames
• IP addresses
• SSL certificates What should you use?
- A . Microsoft Defender for Cloud
- B . Microsoft Defender for Identity
- C . Microsoft Defender for Endpoint
- D . Microsoft Defender External Attack Surface Management (Defender EASM)
You have an Azure subscription that uses Microsoft Sentinel.
You need to create a Microsoft Sentinel notebook that will use the Guided Investigation – Anomaly Lookup template.
What should you create first?
- A . an analytics rule
- B . a Log Analytics workspace
- C . an Azure Machine Learning workspace
- D . a hunting query