
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
You have an Azure subscription that contains a user named Adminl1 and a virtual machine named VM1. VM1 runs Windows Server 2019 and was deployed by using an Azure Resource Manager template. VM1 is the member of a backend pool of a public Azure Basic Load Balancer.
Admin1 reports that VM1 is listed as Unsupported on the Just in time VM access blade of Azure Security Center.
You need to ensure that Admin1 can enable just in time (JIT) VM access for VM1.
What should you do?
- A . Create and configure an additional public IP address for VM 1.
- B . Replace the Basic Load Balancer with an Azure Standard Load Balancer.
- C . Assign an Azure Active Directory Premium Plan 1 license to Admin1.
- D . Create and configure a network security group (NSG).
You have been tasked with configuring an access review, which you plan to assigned to a new
collection of reviews. You also have to make sure that the reviews can be reviewed by resource owners.
You start by creating an access review program and an access review control.
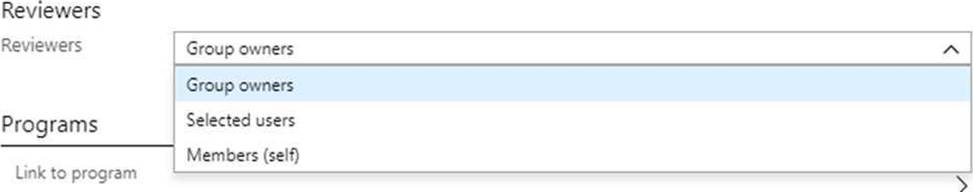
You now need to configure the Reviewers.
Which of the following should you set Reviewers to?
- A . Selected users.
- B . Members (Self).
- C . Group Owners.
- D . Anyone.
Lab Task
Task 6
You need to configure a Microsoft SQL server named Web3l 330471 only to accept connections from the Subnet0 subnet on the VNET01 virtual network.
You have an Azure subscription that contains an instance of Azure Firewall Standard named AzFWL
You need to identify whether you can use the following features with AzFW1:
• TLS inspection
• Threat intelligence
• The network intrusion detection and prevention systems (IDPS)
What can you use?
- A . TLS inspection only
- B . threat intelligence only
- C . TLS inspection and the IDPS only
- D . threat intelligence and the IDPS only
- E . TLS inspection, threat intelligence, and the IDPS
You have an Azure subscription that contains an instance of Azure Firewall Standard named AzFWL
You need to identify whether you can use the following features with AzFW1:
• TLS inspection
• Threat intelligence
• The network intrusion detection and prevention systems (IDPS)
What can you use?
- A . TLS inspection only
- B . threat intelligence only
- C . TLS inspection and the IDPS only
- D . threat intelligence and the IDPS only
- E . TLS inspection, threat intelligence, and the IDPS
You have an Azure subscription name Sub1 that contains an Azure Policy definition named Policy1.
Policy1 has the following settings:
– Definition location: Tenant Root Group
– Category: Monitoring
You need to ensure that resources that are noncompliant with Policy1 are listed in the Azure Security Center dashboard.
What should you do first?
- A . Change the Category of Policy1 to Security Center.
- B . Add Policy1 to a custom initiative.
- C . Change the Definition location of Policy1 to Sub1.
- D . Assign Policy1 to Sub1.
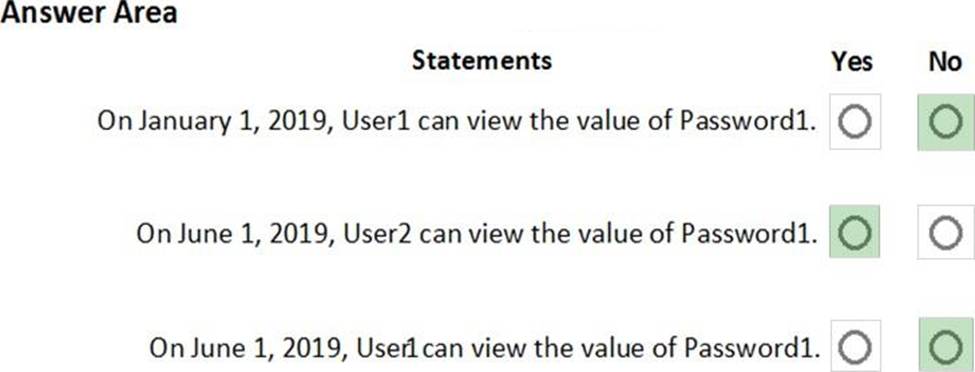
HOTSPOT
You have an Azure subscription that contains the resources shown in the following table.
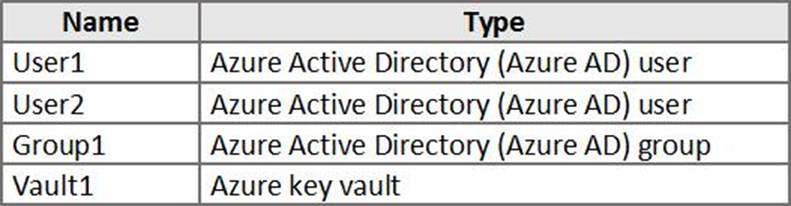
User1 is a member of Group1. Group1 and User2 are assigned the Key Vault Contributor role for Vault1.
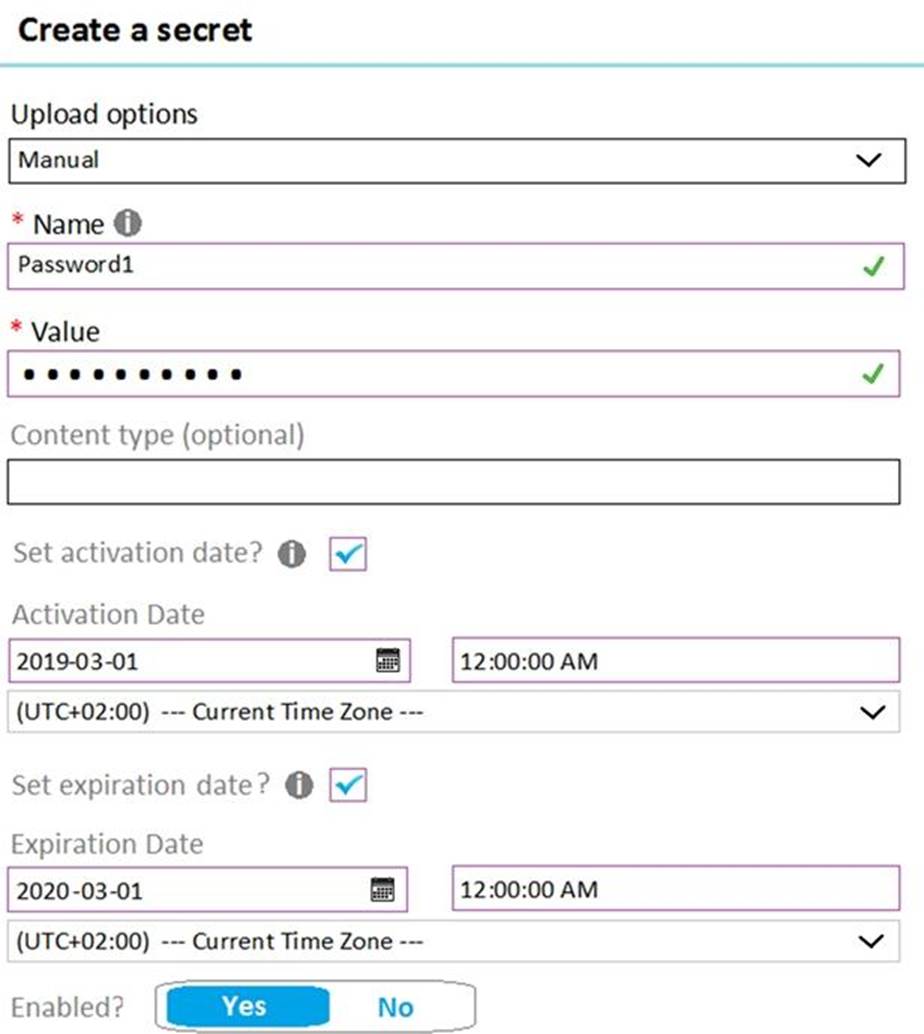
On January 1, 2019, you create a secret in Vault1.
The secret is configured as shown in the exhibit. (Click the Exhibit tab.)
User2 is assigned an access policy to Vault1.
The policy has the following configurations:
✑ Key Management Operations: Get, List, and Restore
✑ Cryptographic Operations: Decrypt and Unwrap Key
✑ Secret Management Operations: Get, List, and Restore
Group1 is assigned an access to Vault1.
The policy has the following configurations:
✑ Key Management Operations: Get and Recover
✑ Secret Management Operations: List, Backup, and Recover
For each of the following statements, select Yes if the statement is true. Otherwise, select No. 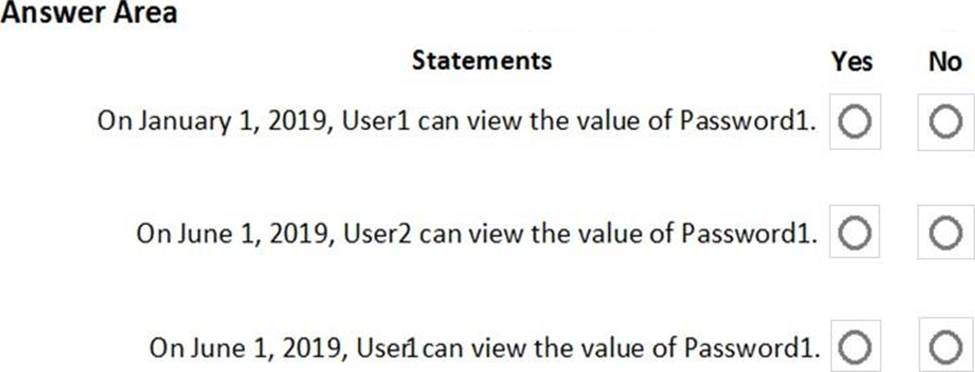
HOTSPOT
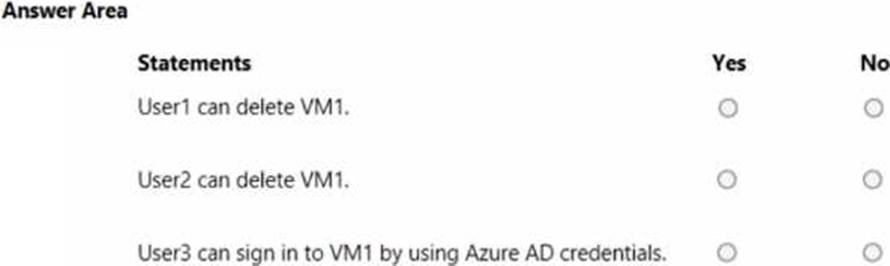
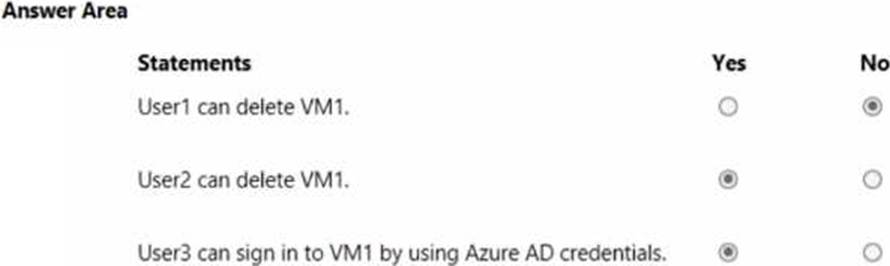
You have an Azure subscription that contains a resource group named RG1. RG1 contains a virtual machine named VM1 that uses Azure Active Directory (Azure AD) authentication.
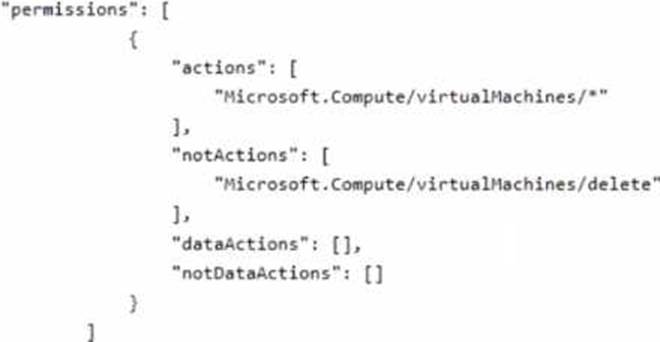
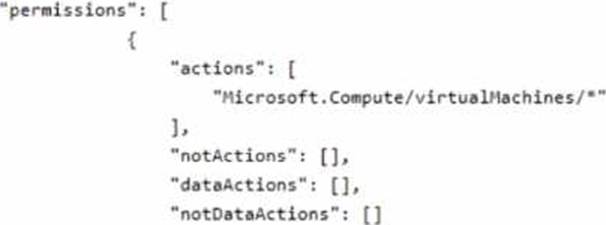
You have two custom Azure roles named Role1 and Role2 that are scoped to RG1.
The permissions for Role1 are shown in the following JSON code.
The permissions for Role2 are shown in the following JSON code.
You assign the roles to the users shown in the following table.
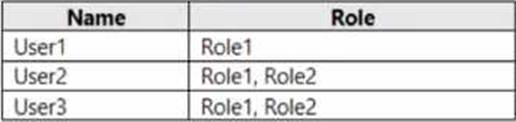
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Which Azure feature should be used to manage hybrid identities?
- A . Azure Active Directory B2C
- B . Azure Active Directory Connect
- C . Azure Information Protection
- D . Azure Key Vault
You have an Azure subscription that contains an Azure Data Lake Storage Gen2 account named storage1. You deploy an Azure Synapse Analytics workspace named synapsews1 to a managed virtual network. You need to enable access from synapsews1 to storage1.
What should you configure?
- A . a virtual network gateway
- B . a network security group (NSG)
- C . a private endpoint
- D . peering