
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
HOTSPOT
Your network contains an on-premises Active Directory domain named adatum.com that syncs to Azure Active Directory (Azure AD).
The Azure AD tenant contains the users shown in the following table.
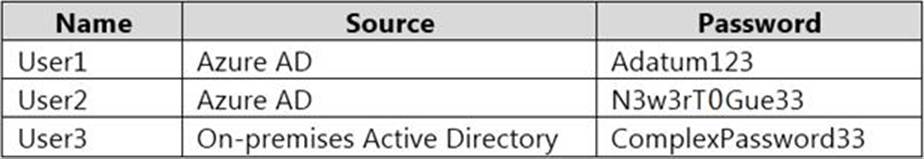
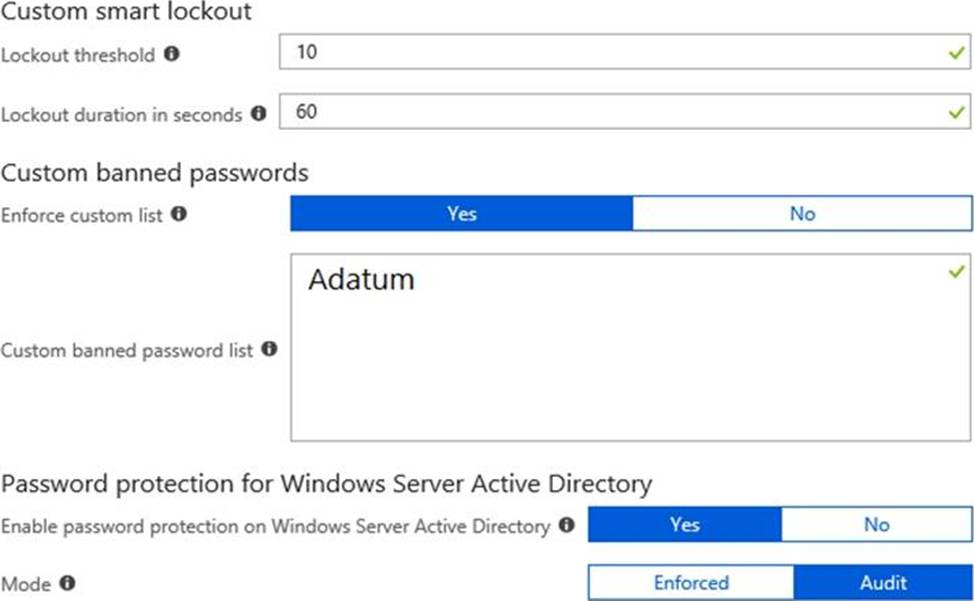
You configure the Authentication methods C Password Protection settings for adatum.com as shown in the following exhibit.
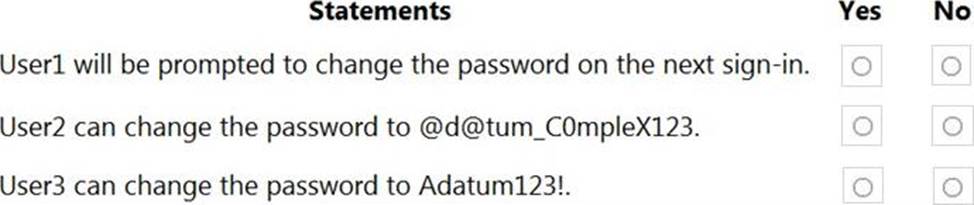
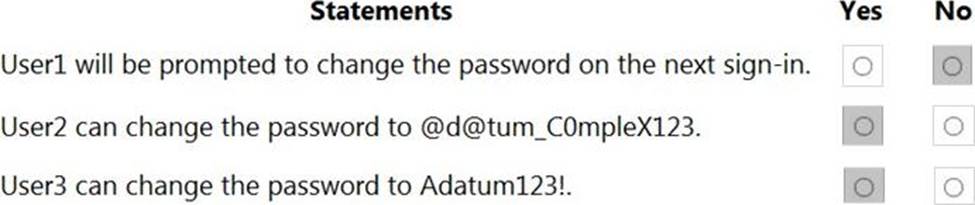
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: User1 [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 5
You need to ensure that only devices connected to a 131-107.0.0/16 subnet can access data in the rg1lod28681041 Azure Storage account.
HOTSPOT
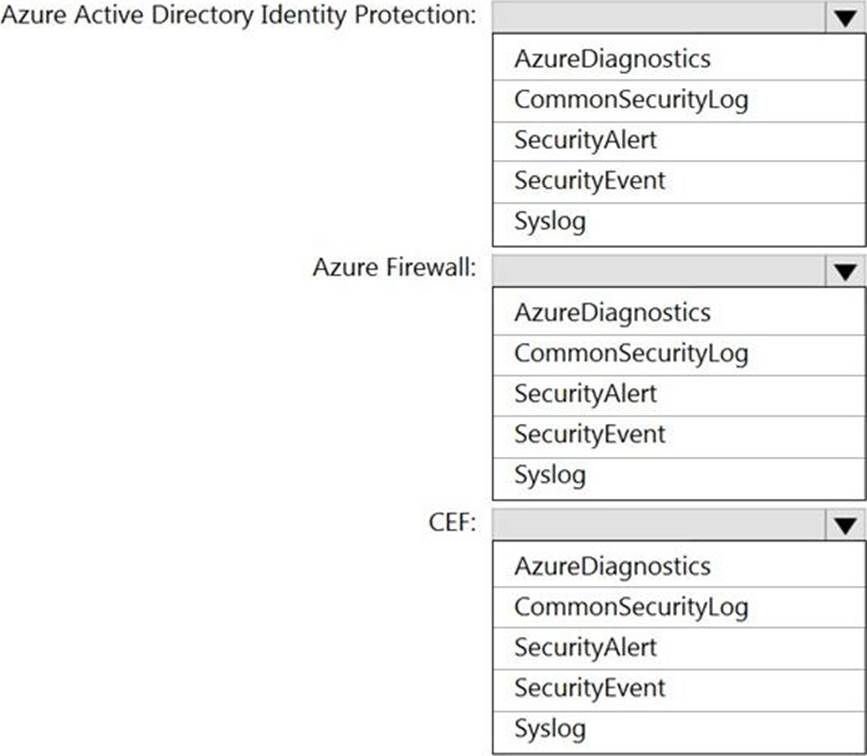
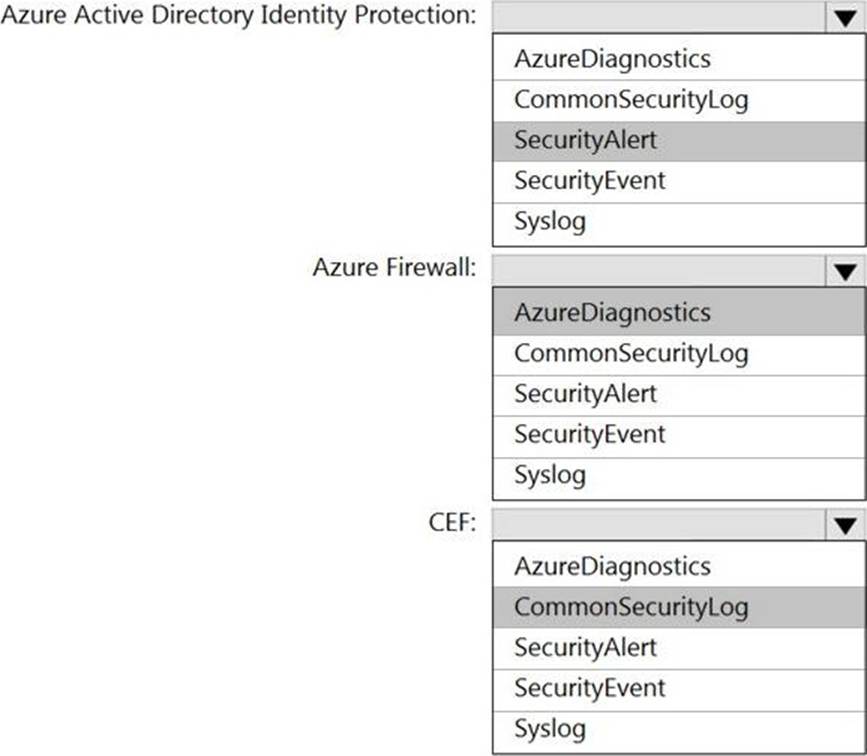
You have an Azure Sentinel workspace that has the following data connectors:
– Azure Active Directory Identity Protection
– Common Event Format (CEF)
– Azure Firewall
You need to ensure that data is being ingested from each connector.
From the Logs query window, which table should you query for each connector? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
You have an Azure Sentinel workspace that has the following data connectors:
– Azure Active Directory Identity Protection
– Common Event Format (CEF)
– Azure Firewall
You need to ensure that data is being ingested from each connector.
From the Logs query window, which table should you query for each connector? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains an Azure App Service app named App1, an Azure container instance named AC1. and a storage account named storage1. AC1 hosts an app named App2.
Users send requests to App1 by using a URL of https:/app1.contoso.com/echo/resource-cache? param1 =sample. App1 calls App2. which retrieves data from storage1.
You need to ensure that a security alert will be generated when connections are detected from anomalous IP addresses.
Which Microsoft Defender for Cloud service should you use?
- A . Microsoft Defender for App Service
- B . Microsoft Defender for APIs
- C . Microsoft Defender for Storage
- D . Microsoft Defender for Containers
You have an Azure subscription that contains the users shown in the following table.
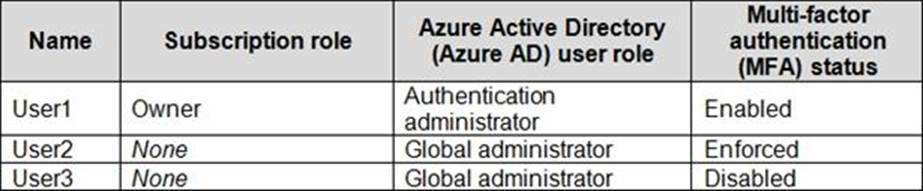
Which users can enable Azure AD Privileged Identity Management (PIM)?
- A . User2 and User3 only
- B . User1 and User2 only
- C . User2 only
- D . User1 only
HOTSPOT
You have an Azure subscription that contains the resources shown in the following table.
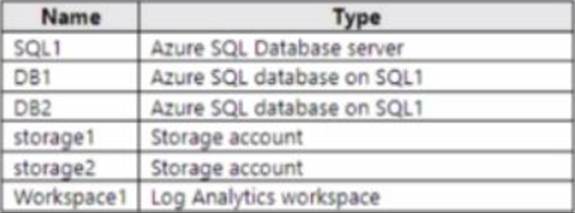
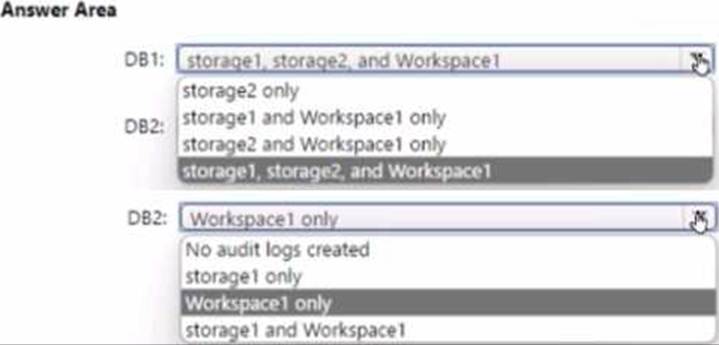
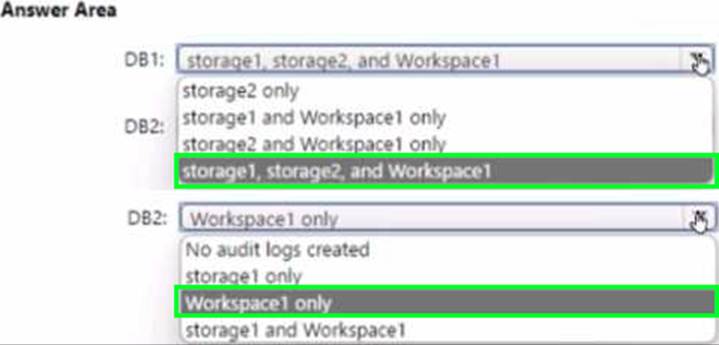
SQL1 has the following configurations:
• Auditing: Enabled
• Audit log destination: storage1, Workspace1 DB1 has the following configurations:
• Auditing: Enabled
• Audit log destination: storage2
DB2 has auditing disabled.
Where are the audit logs for DB1 and DB2 stored? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
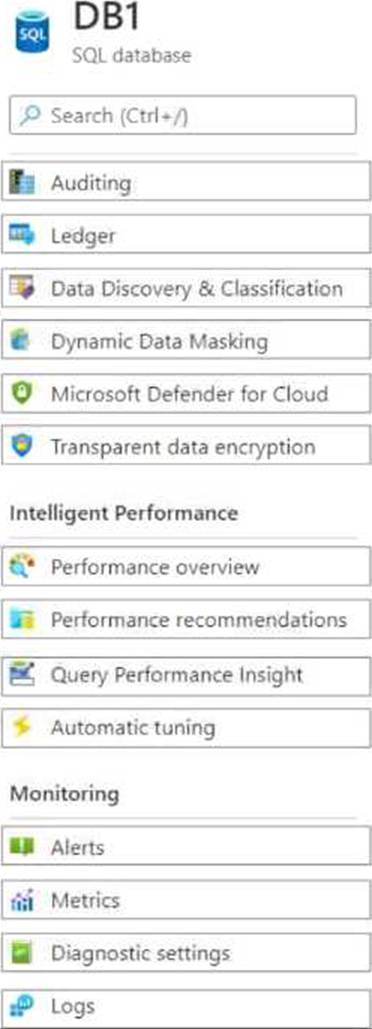
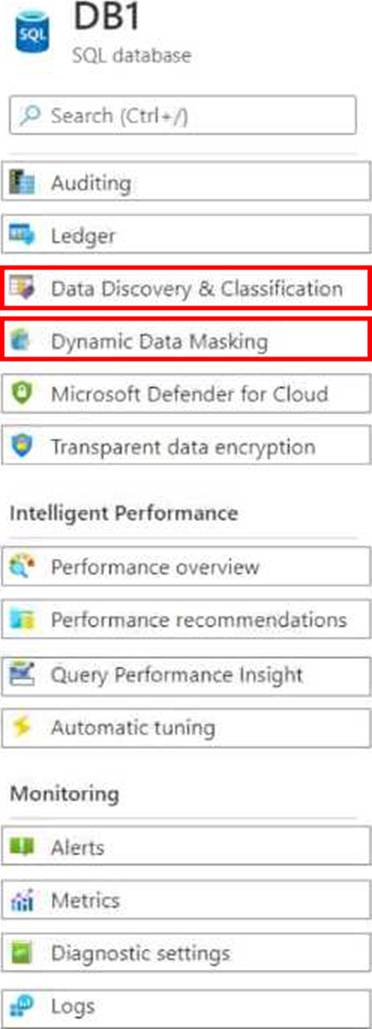
You have an Azure SQL database named DB1 that contains a table named Table.
You need to configure DB1 to meet the following requirements;
• Sensitive data in Table1 must be identified automatically.
• Only the first character and last character of the sensitive data must be displayed in query results.
Which two features should you configure? To answer, select the features in the answer area. NOTE: Each correct selection is worth one point.
Your company has an Azure subscription named Sub1 that is associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
The company develops an application named App1. App1 is registered in Azure AD.
You need to ensure that App1 can access secrets in Azure Key Vault on behalf of the application users.
What should you configure?
- A . an application permission without admin consent
- B . a delegated permission without admin consent
- C . a delegated permission that requires admin consent
- D . an application permission that requires admin consent
You have an Azure subscription named Sub1. Sub1 contains a virtual network named VNet1 that contains one subnet named Subnet1.
Subnet1 contains an Azure virtual machine named VM1 that runs Ubuntu Server 20.04.
You create a service endpoint for Microsoft. Storage in Subnet1.
You need to ensure that when you deploy Docker containers to VM1, the containers can access Azure Storage resources by using the service endpoint.
What should you do on VM1 before you deploy the container?
- A . Create an application security group and a network security group (NSG).
- B . Install the container network interface (CNI) plug-in.
- C . Edit the docker-compose.ym1 file.